

DidierStevensSuite
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
digital-forensicseducationhash-analysis+6
2.6k
didierstevens/didierstevenssuiteCollection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
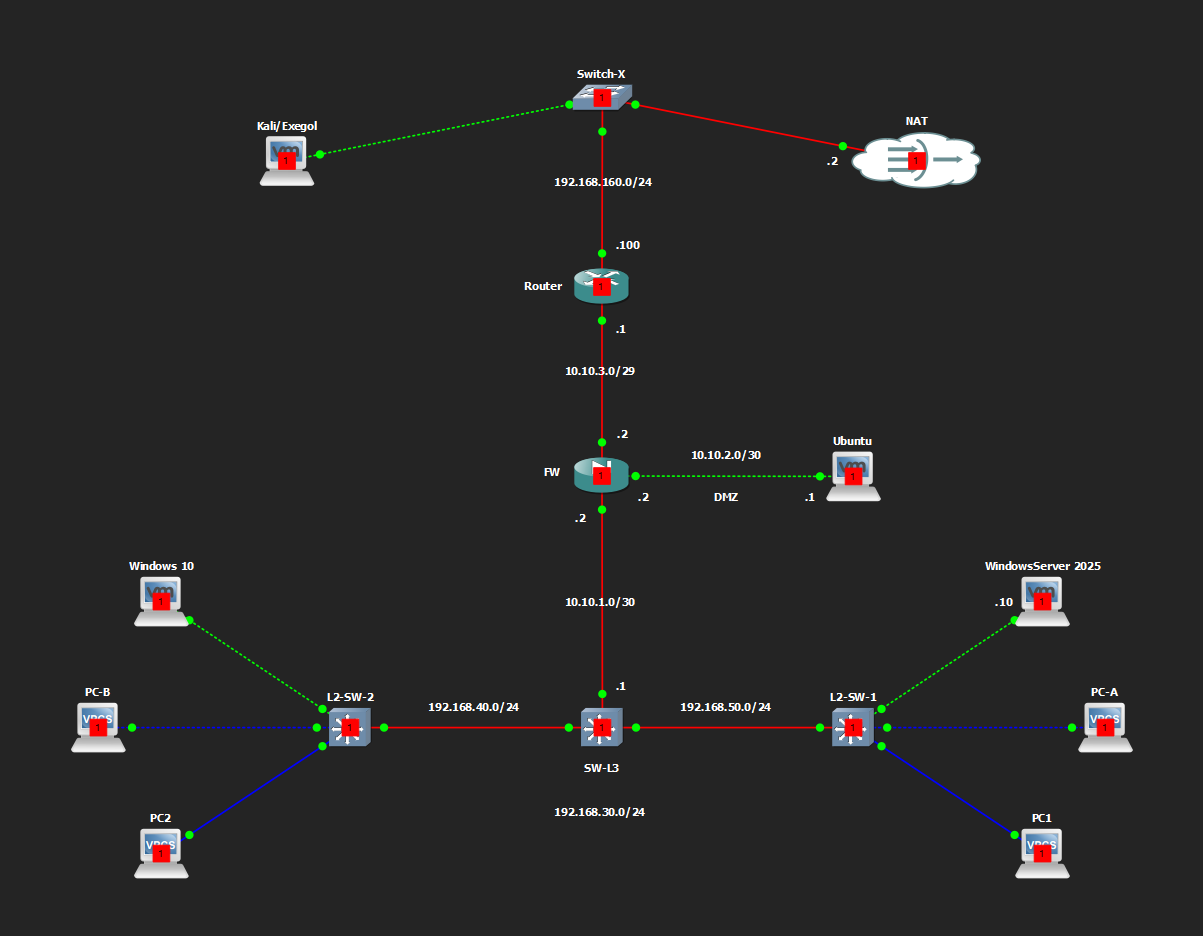 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
 tandasat/hello-vt-rp
A simple hypervisor demonstrating the use of the Intel VT-rp (redirect protection) technology.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 praetorian-inc/capability-sdk
Shared Go SDK defining a standard capability interface for security scanners, with multi-format finding output (terminal, JSON, NDJSON, Markdown,…
 bara-almustafa/cve-2026-34990-poc
CVE-2026-34990 — CUPS <= 2.4.16 Local Privilege Escalation
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…