
vphone-cli
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
exploitationfirmware-analysisios-security+3
16.4k
lakr233/vphone-cliBoot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
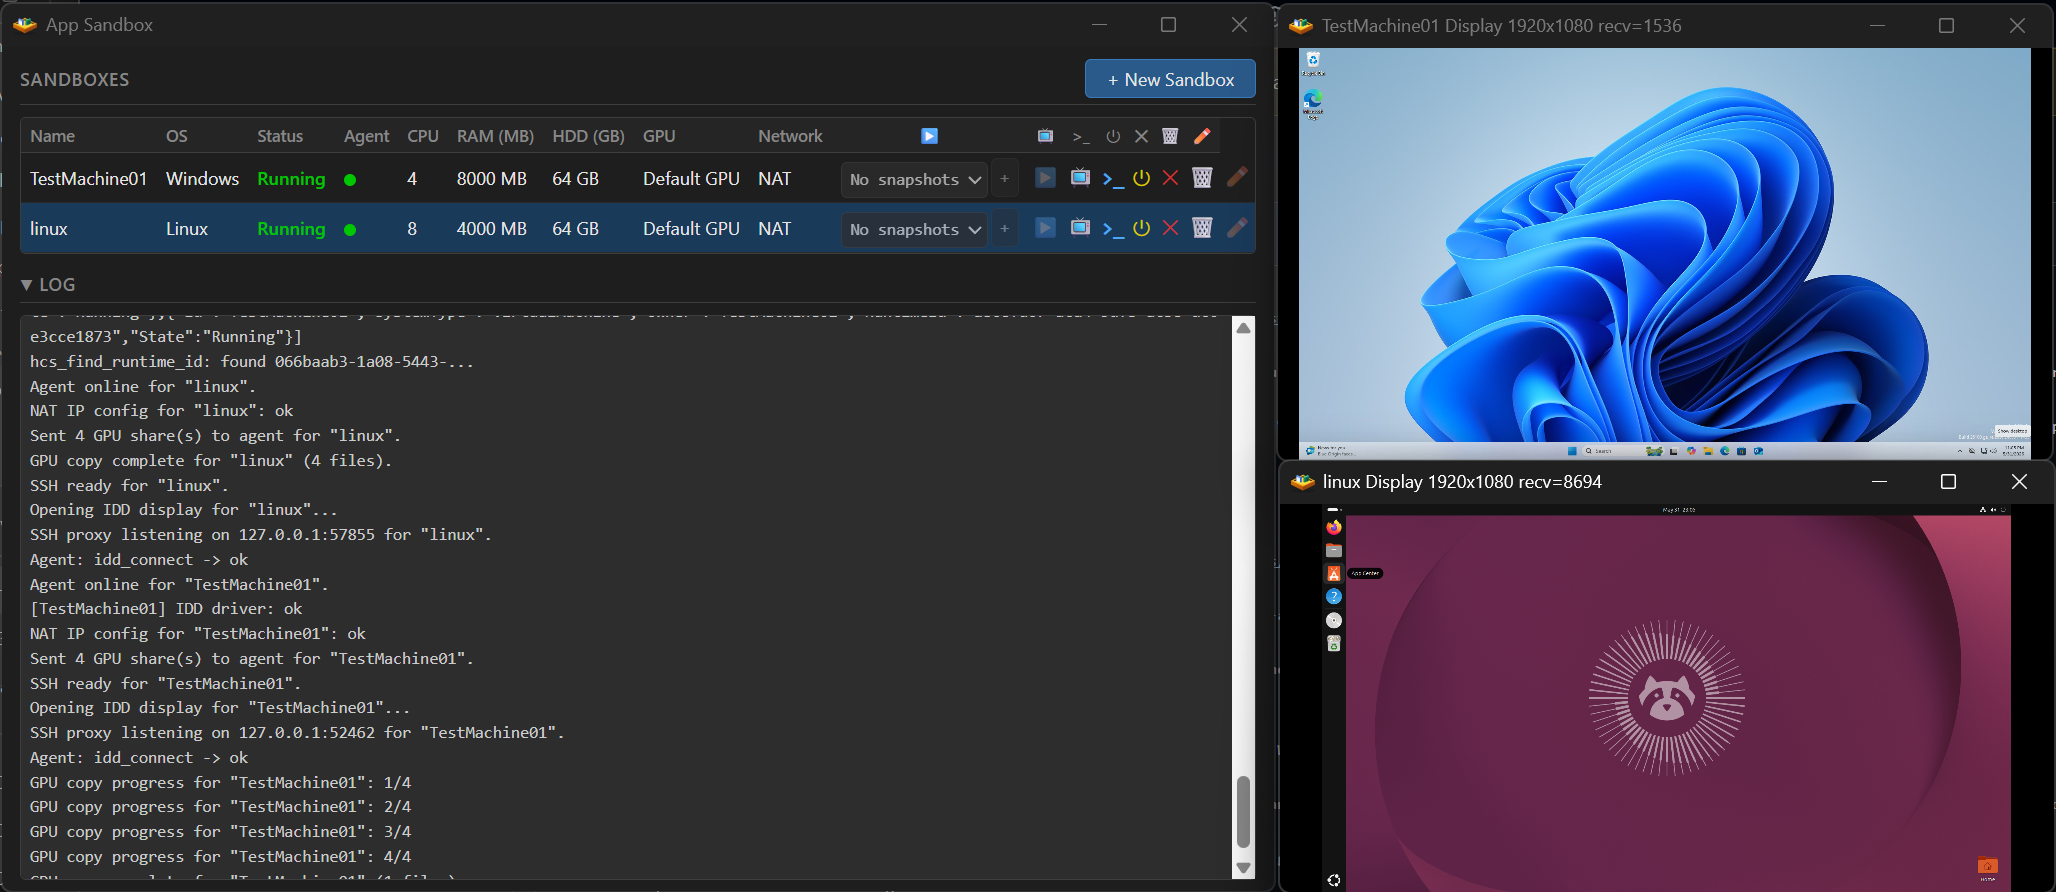 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 atiilla/cve-2026-2441_poc
Proof-of-concept exploit for CVE-2026-2441, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 hassham1/cve-2026-12227-visualcomposer-lfi-poc
Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…