

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
40
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
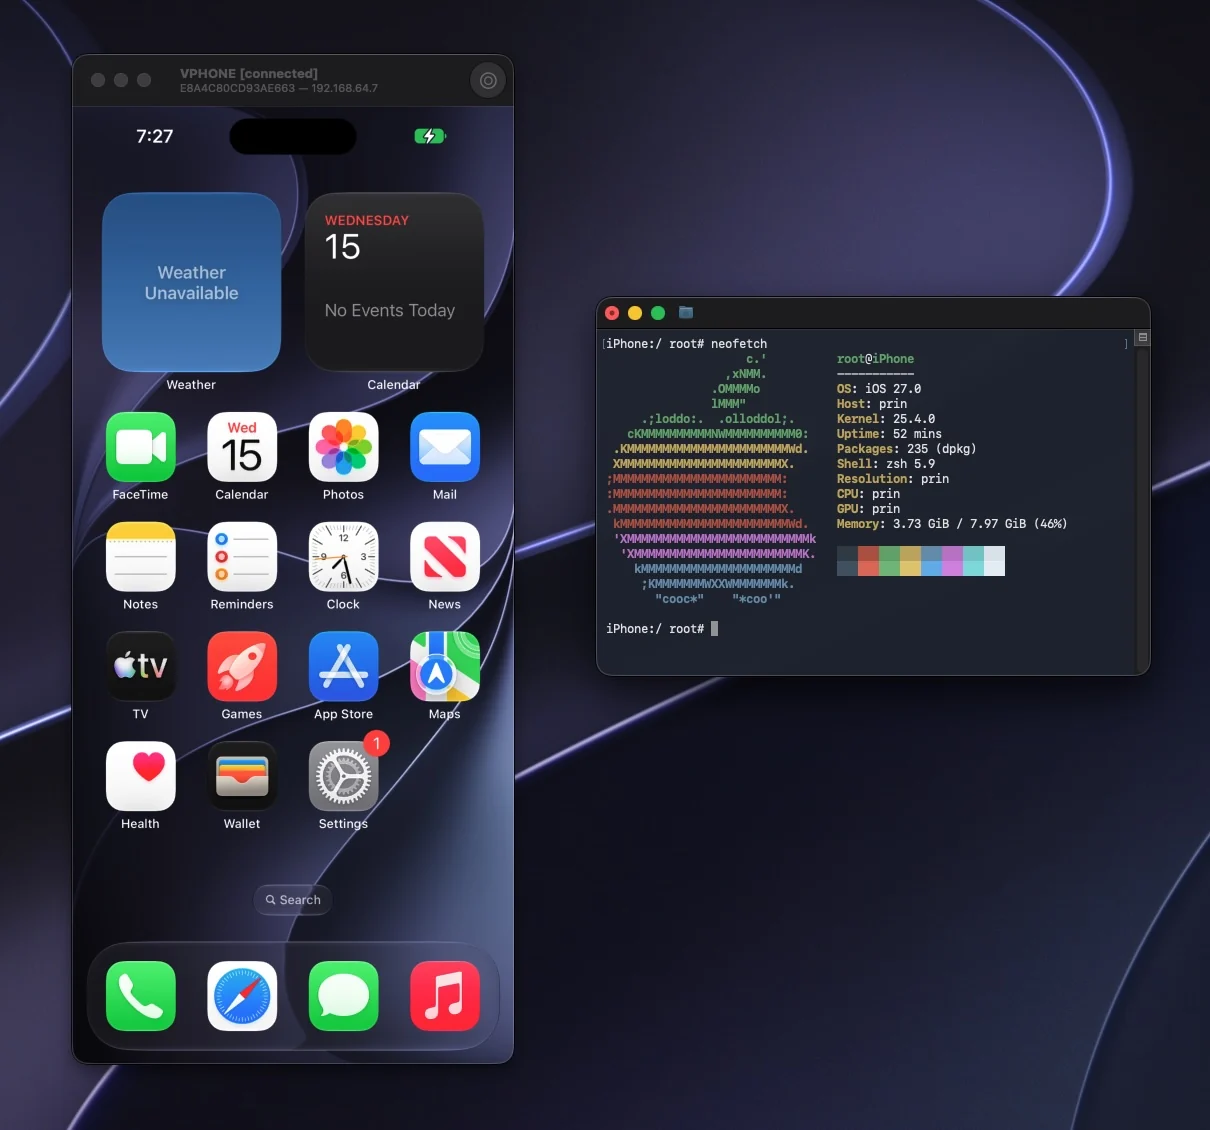 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 bmax121/apatch
The patching of Android kernel and Android system
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
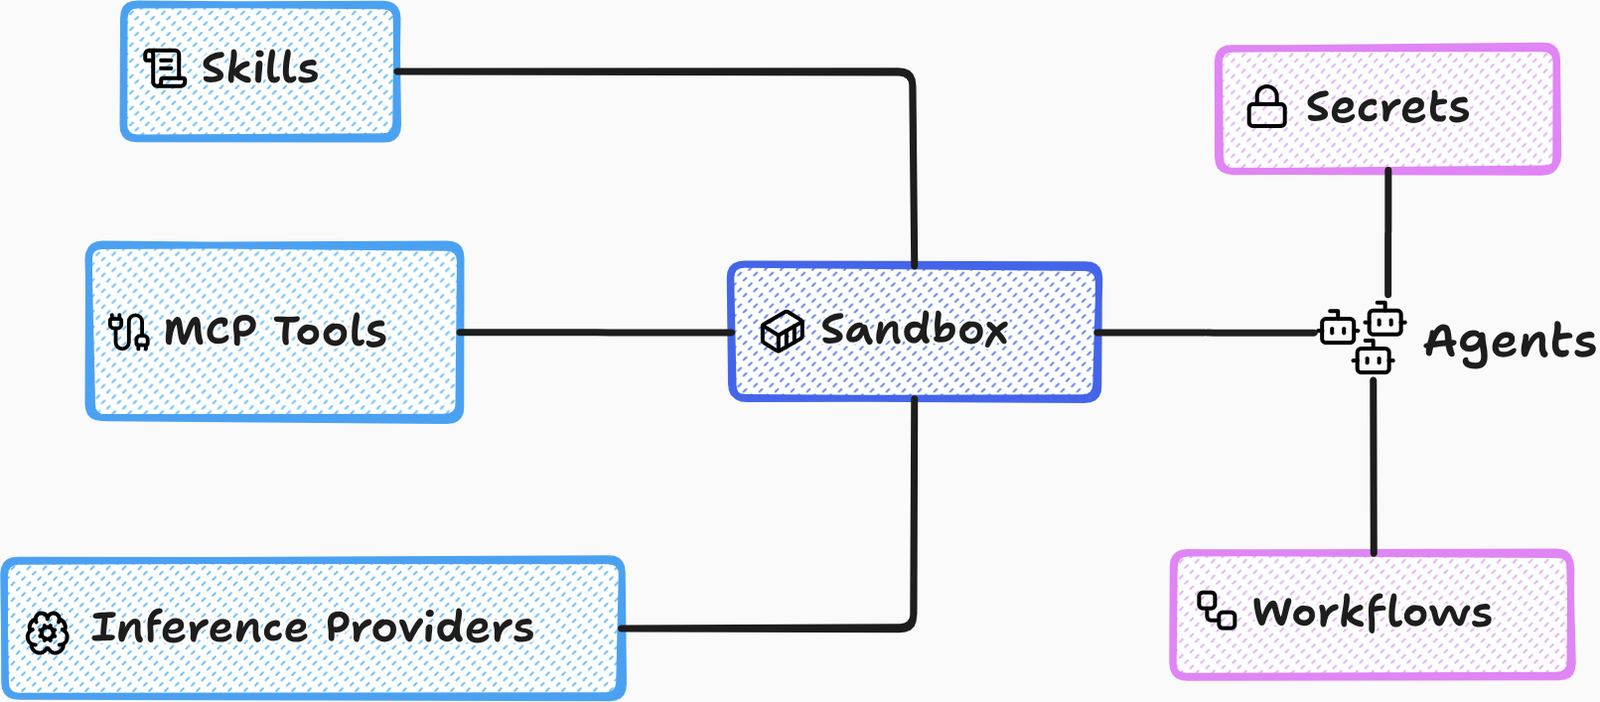 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 netblue30/firejail
Linux namespaces and seccomp-bpf sandbox
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 synacktiv/mofos
Virtual machines manipulation framework
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.