

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.3k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
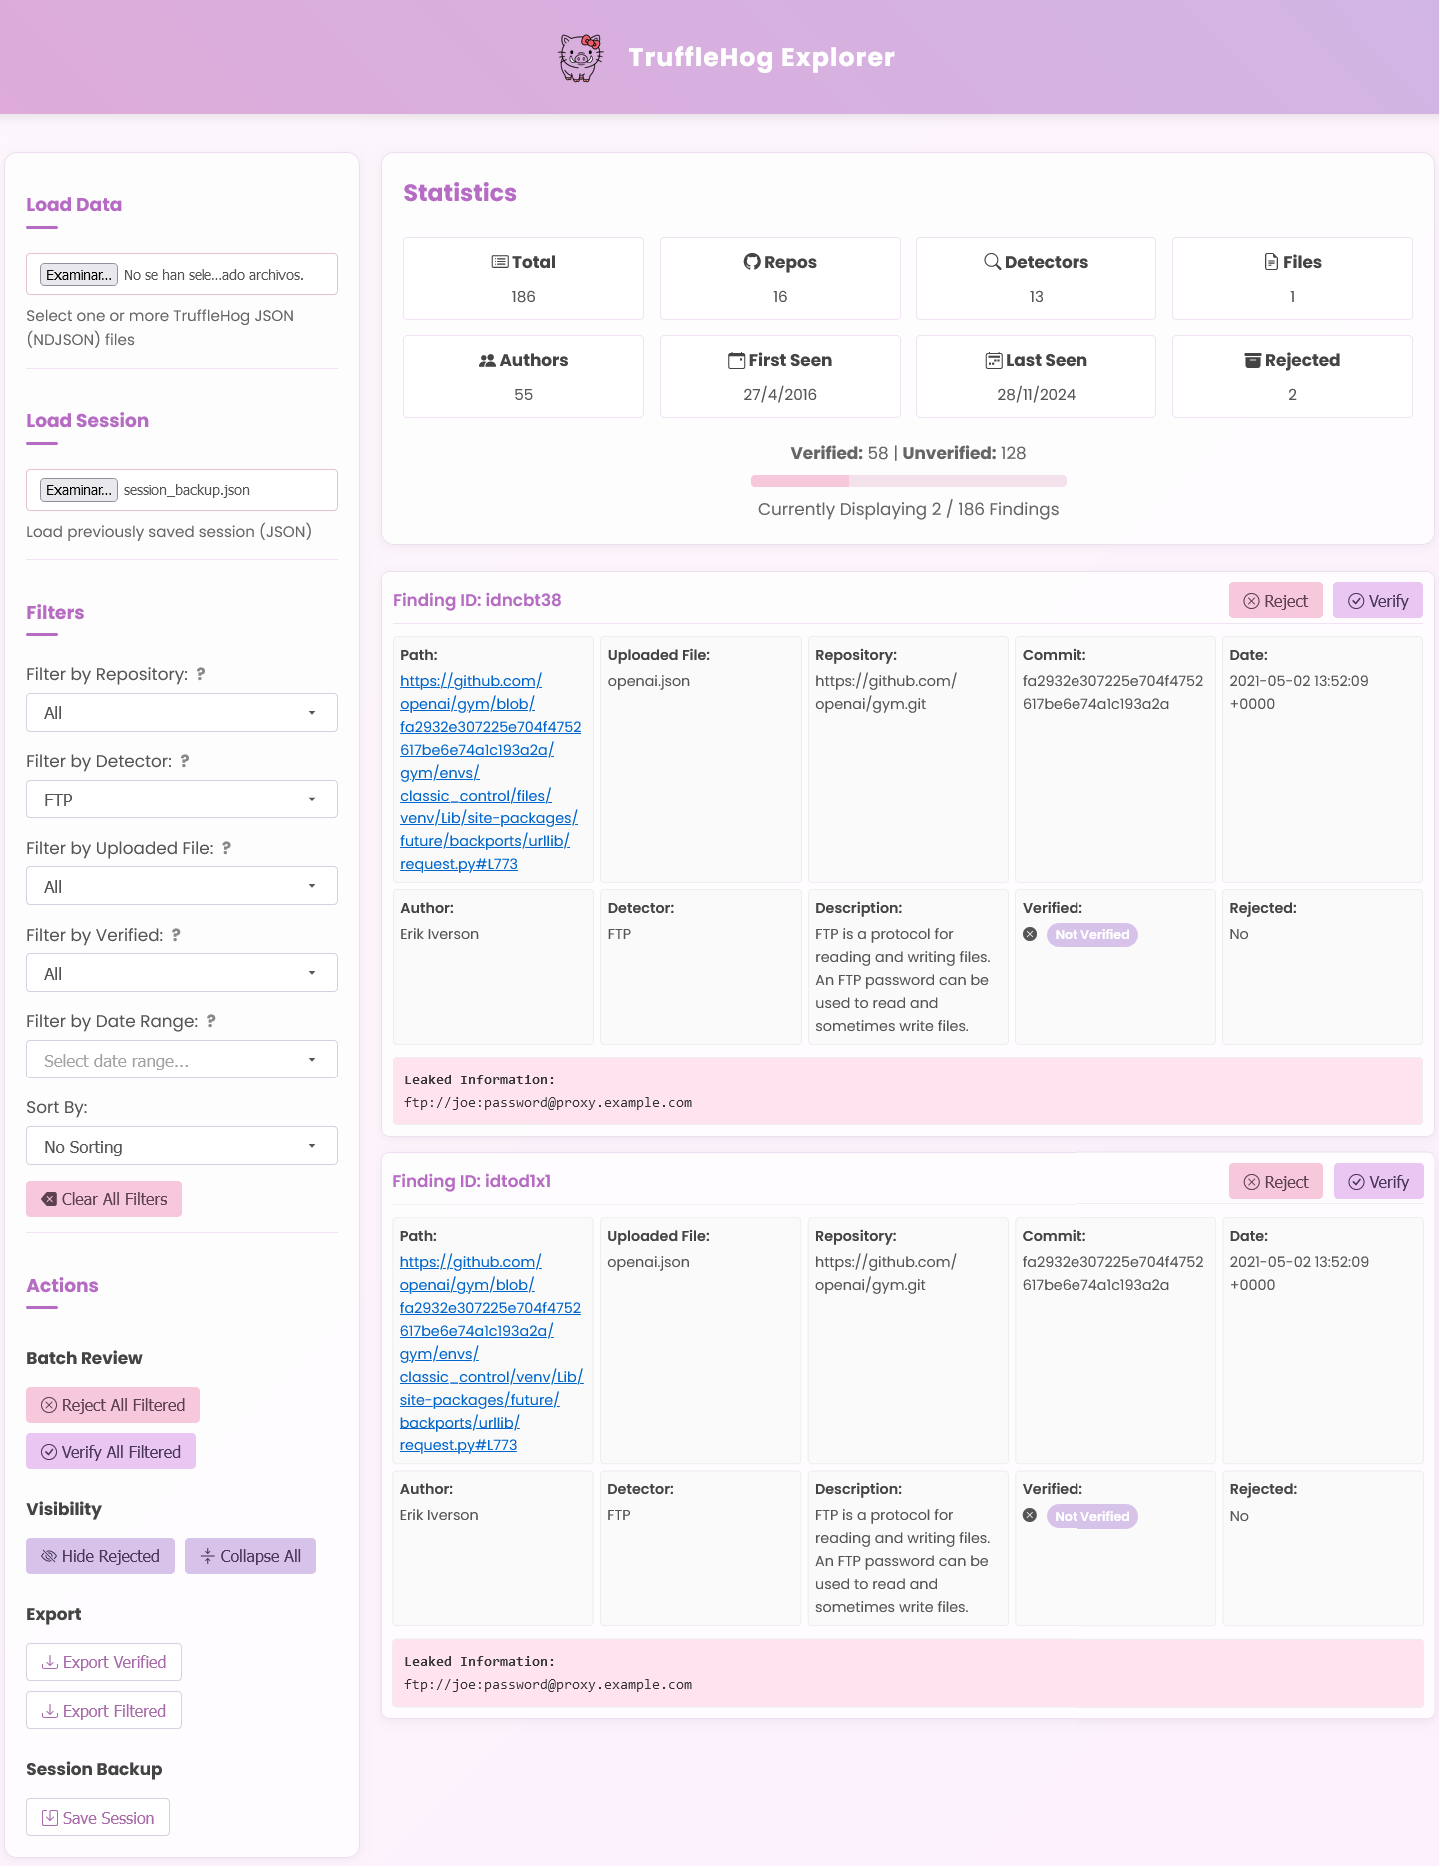 gonzosint/trufflehog-explorer
Web-based dashboard to visualize, filter, and analyze secrets discovered by TruffleHog, with batch verification, export, and session management for…
 arpsyndicate/kenzer
automated web assets enumeration & scanning [DEPRECATED]
 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 edoardottt/cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
 h33tlit/jbin-website-secret-scraper
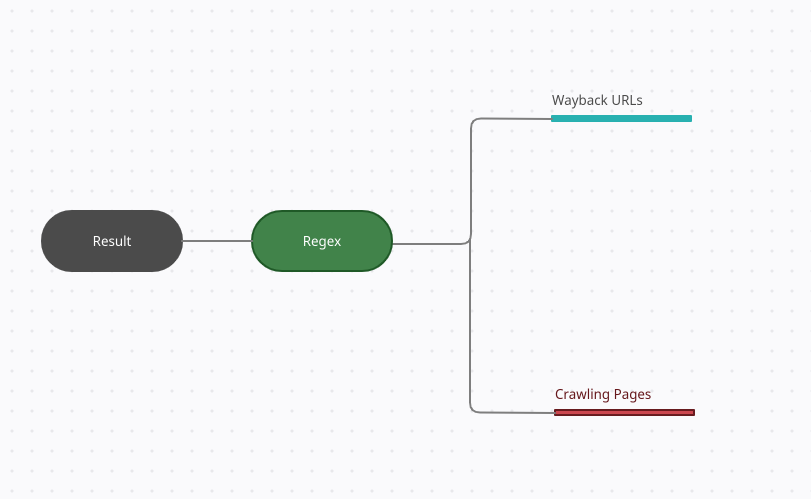
Jbin will gather all the URLs from the website and then it will try to expose the secret data from them such as API keys, API secrets, API tokens and…
 sohelyousef/js-secret-hunter
Automated Python scanner to detect hardcoded secrets (Private Keys, API Tokens) in client-side JavaScript files.
 s0md3v/photon
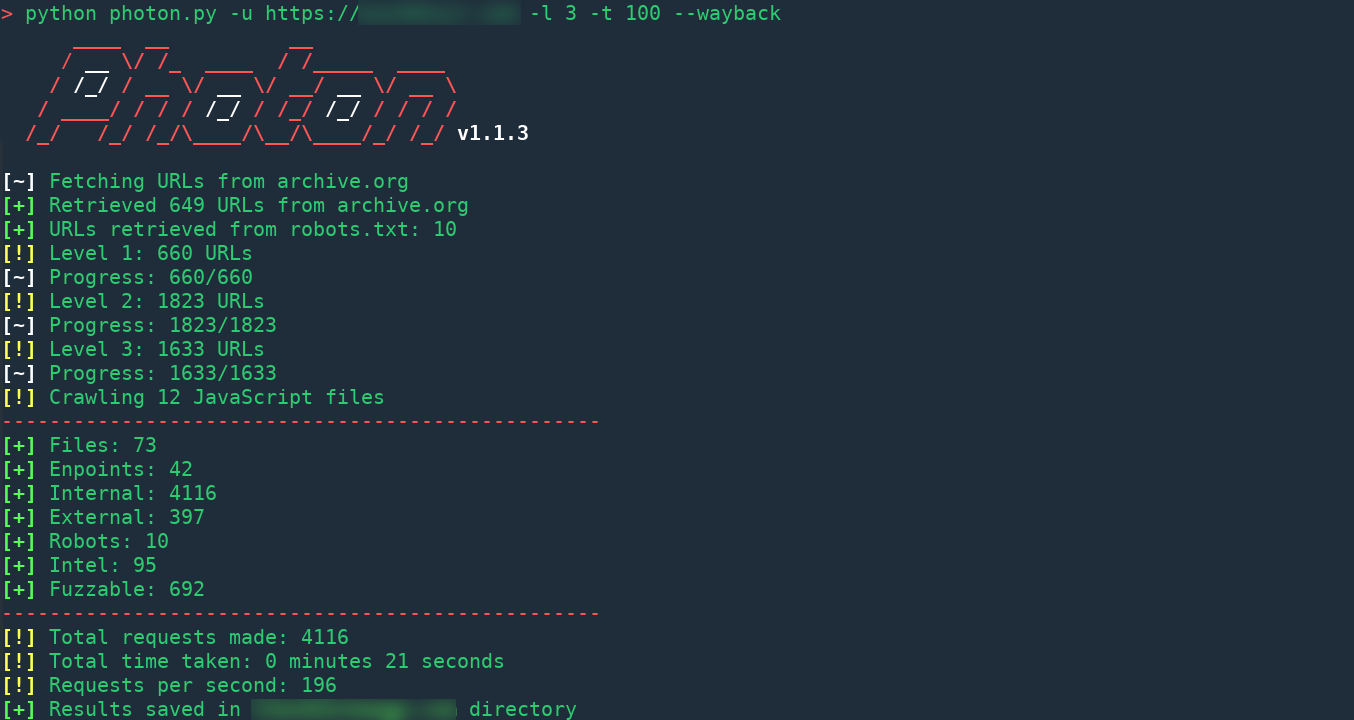
Incredibly fast crawler designed for OSINT.
 xnl-h4ck3r/xnlinkfinder
A python tool used to discover endpoints, potential parameters, a target specific wordlist for a given target and secrets
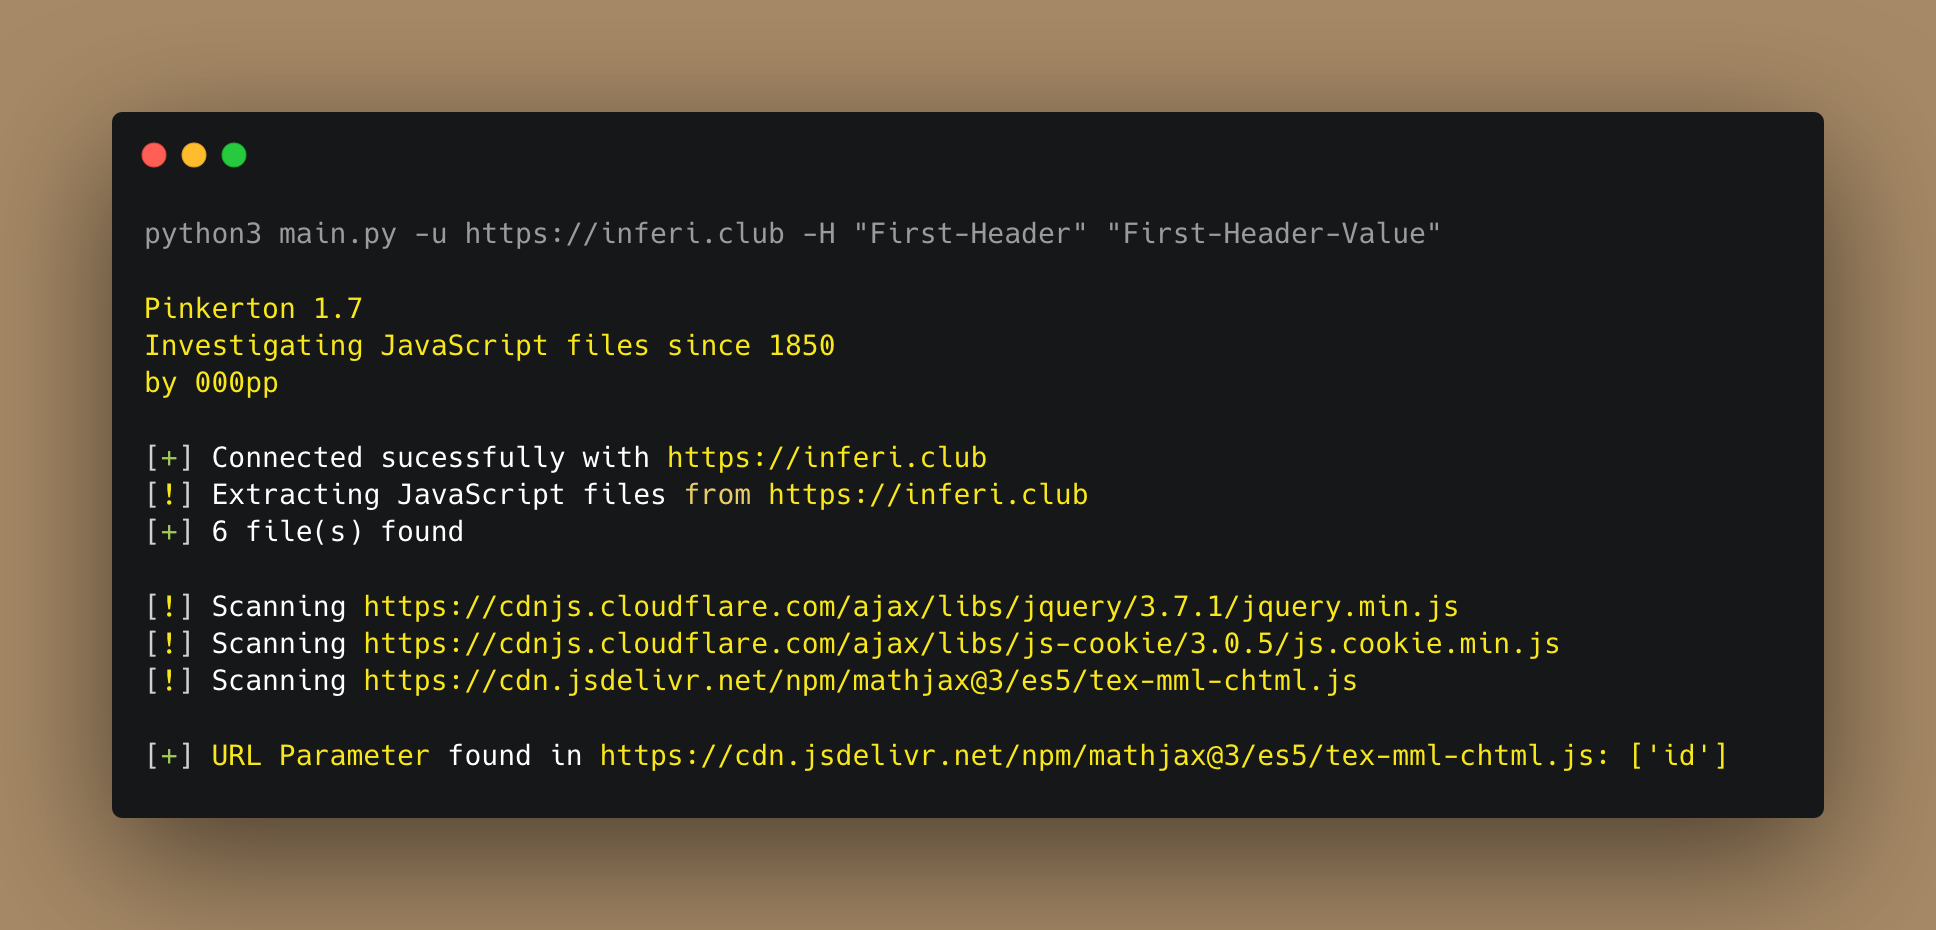 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
 redhuntlabs/httploot
An automated tool which can simultaneously crawl, fill forms, trigger error/debug pages and "loot" secrets out of the client-facing code of sites.
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.