
airgap
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
ai-securitycontainer-securitydefensive-tools+3
xtuc/airgapSecurity for the modern age of AI: defend against bad AI agents and malicious npm packages
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
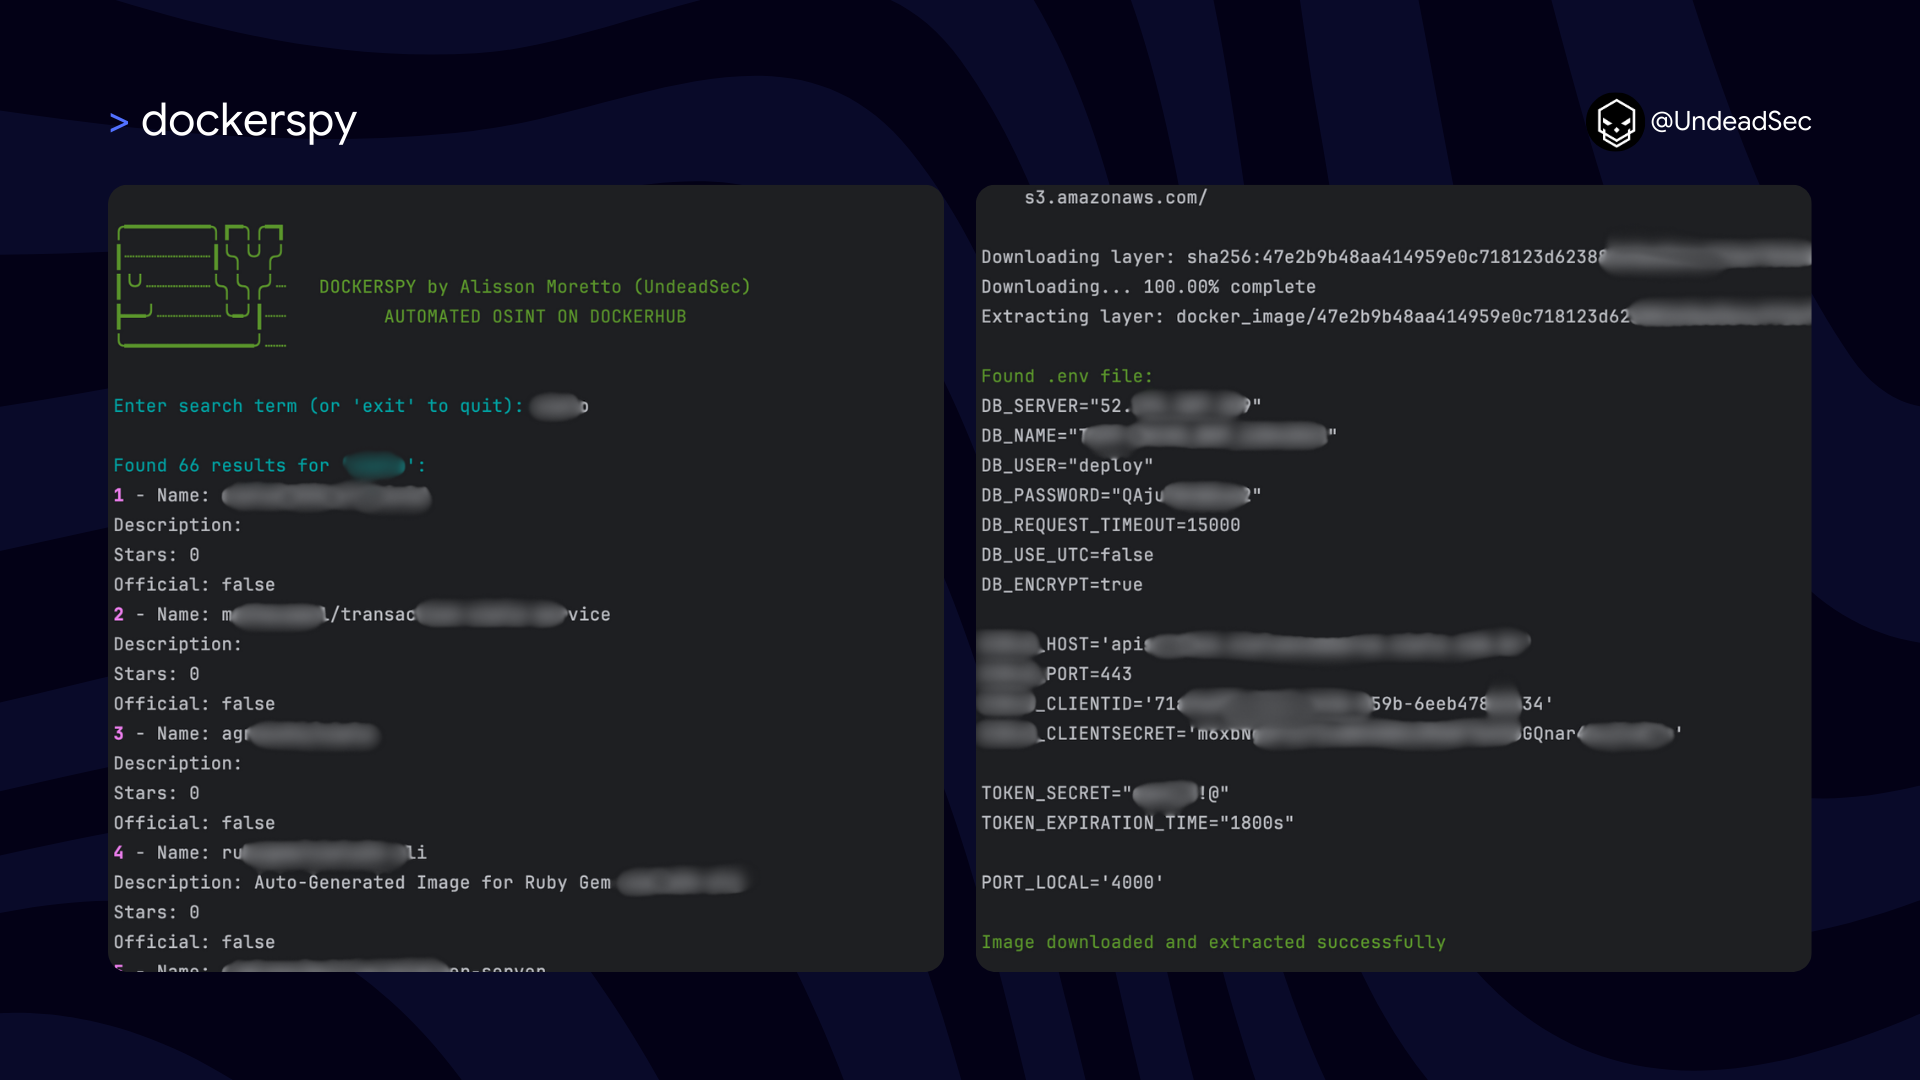 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning

 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 mhaggis/package-inferno
A Public Package Scanner for The Community