
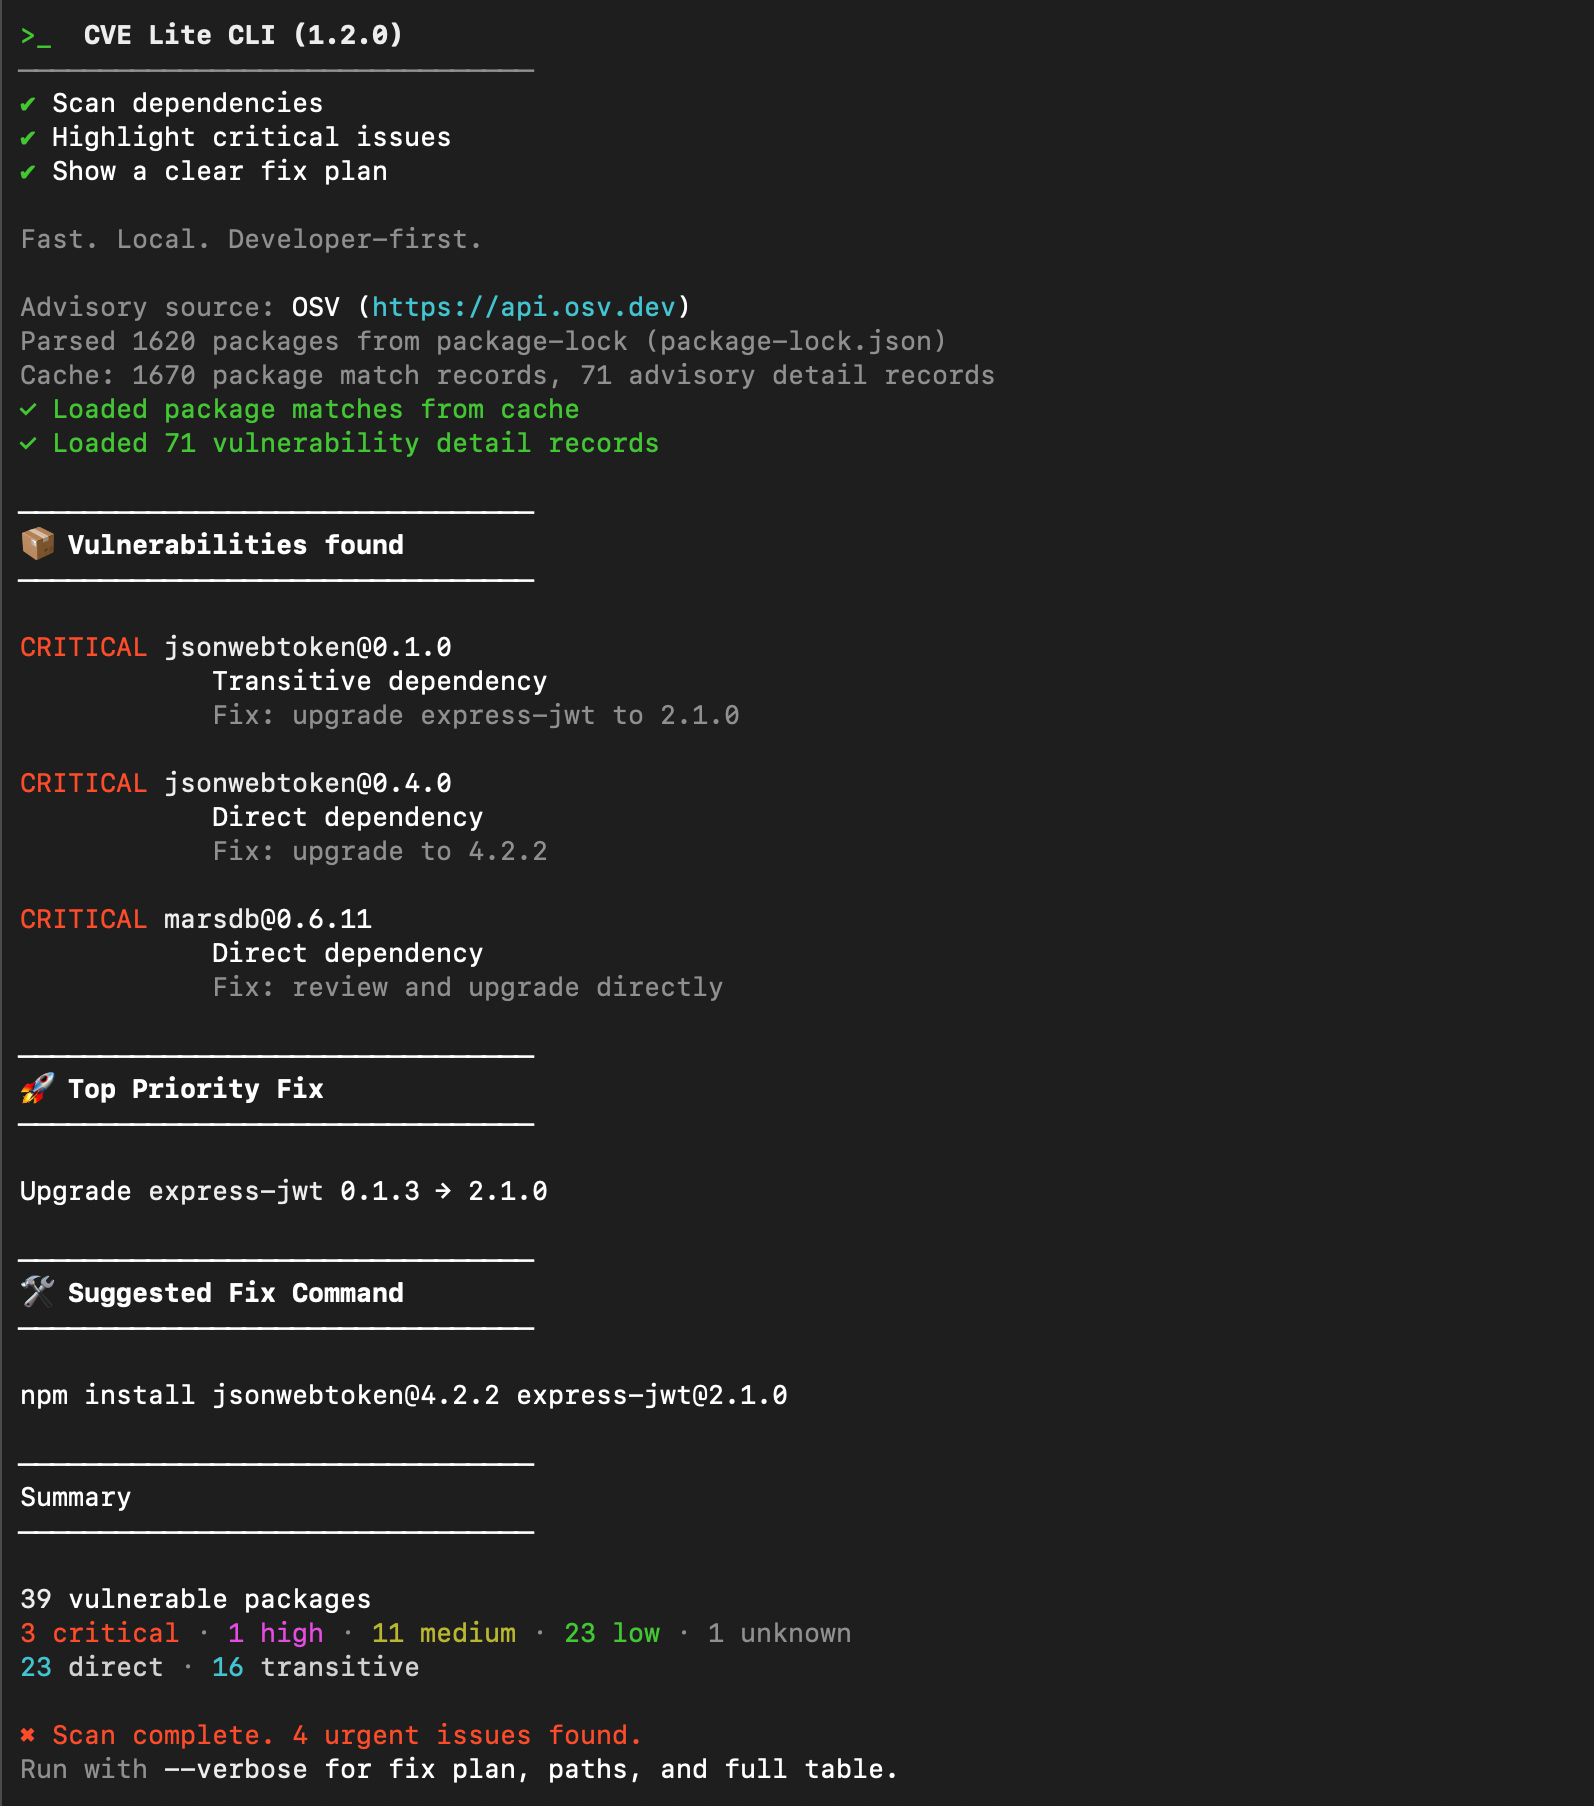
cve-lite-cli
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
code-analysiscurated-resourcesdevsecops+5
758
owasp/cve-lite-cliFast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
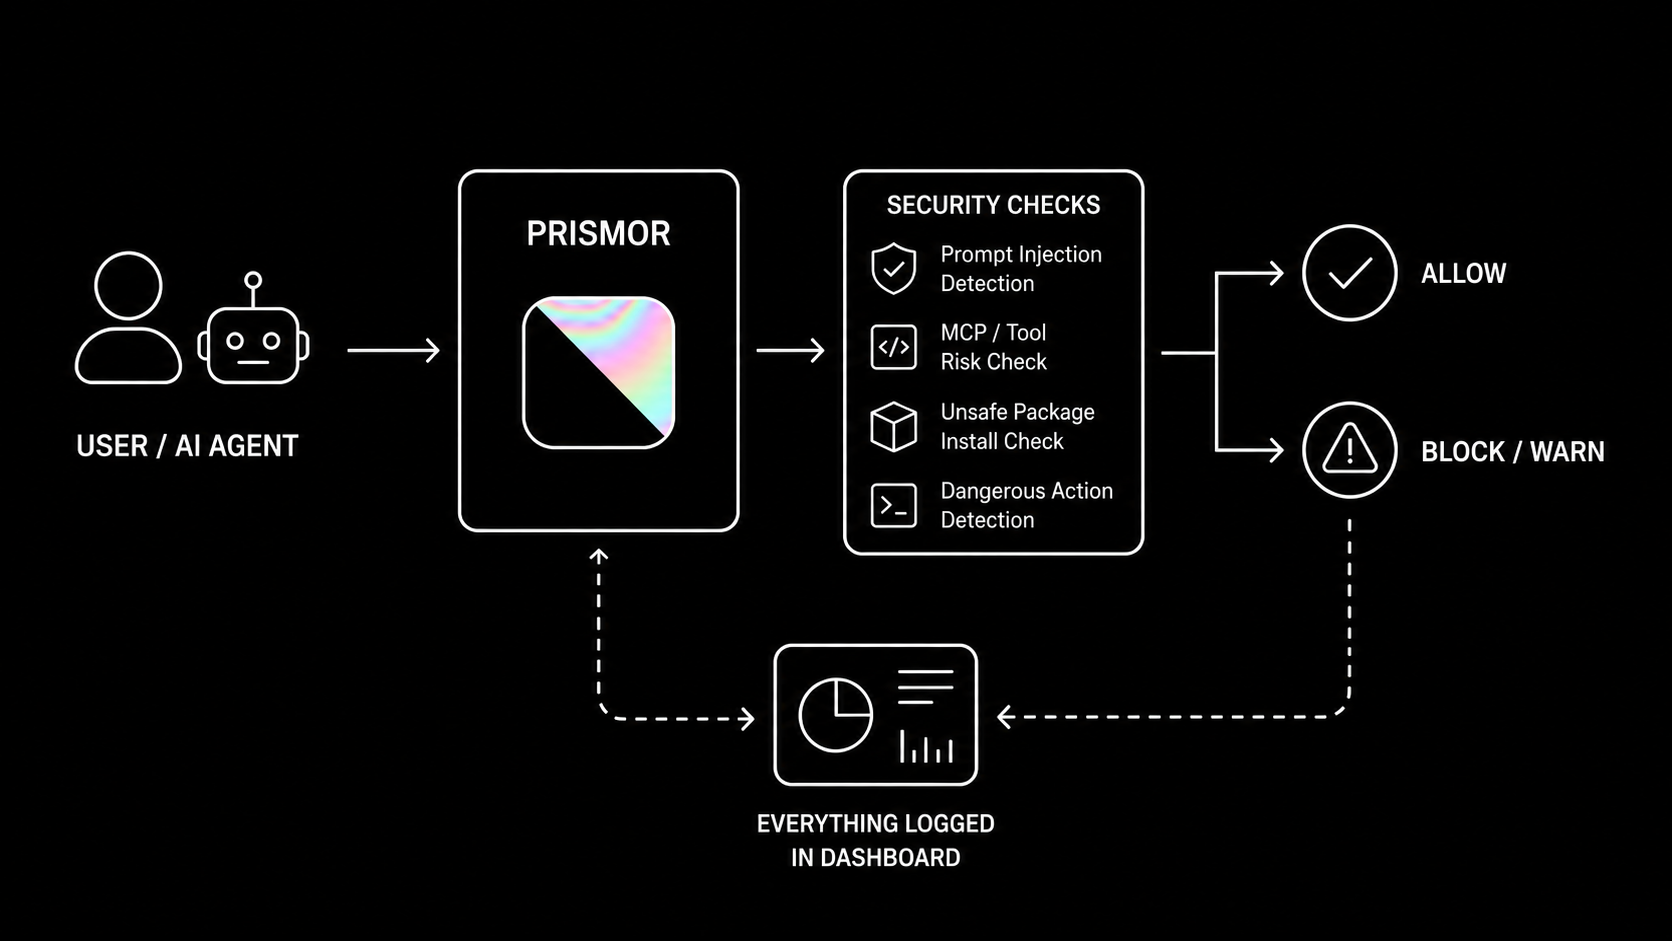 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 semonte/sisu
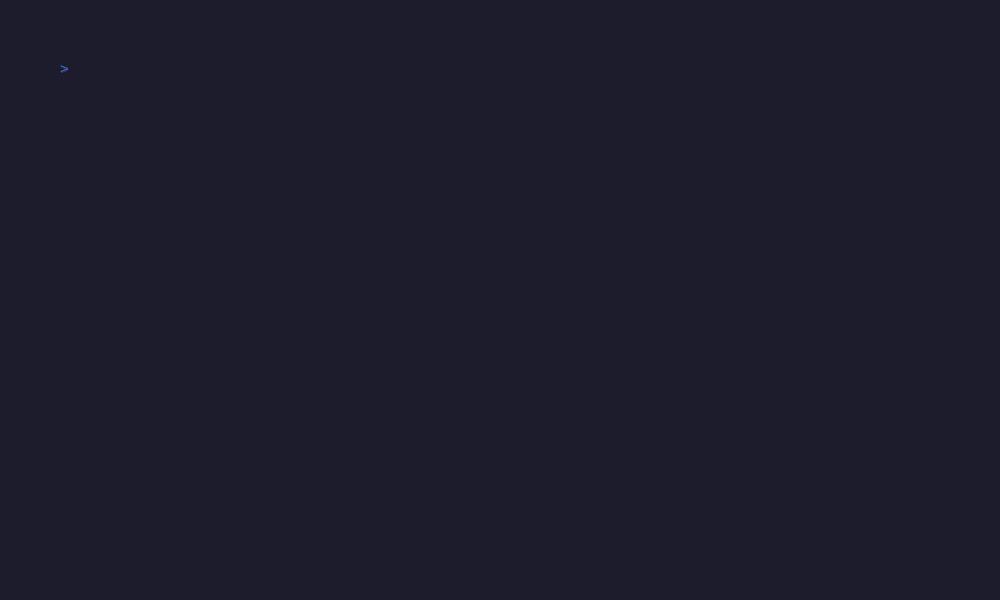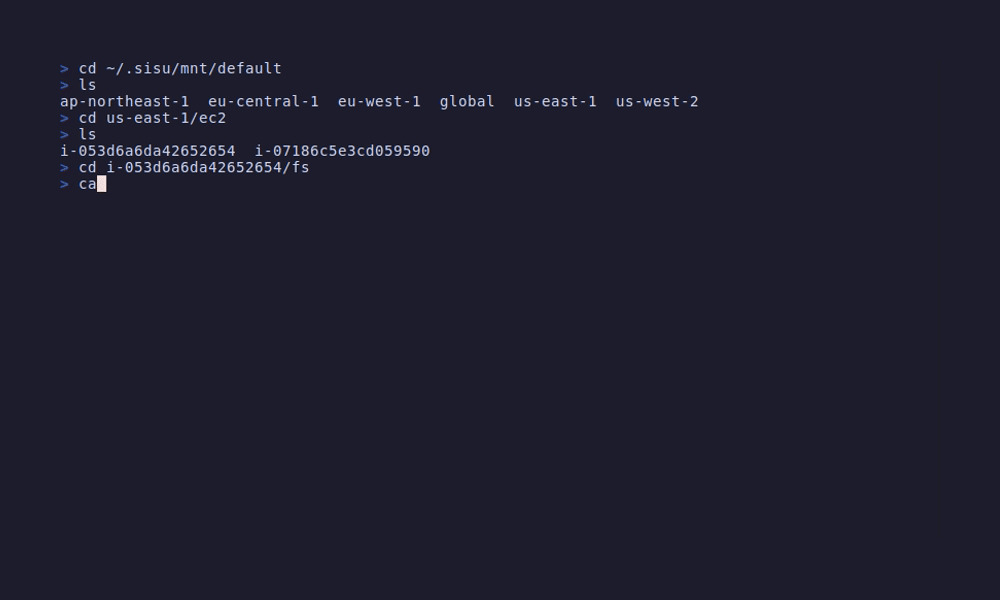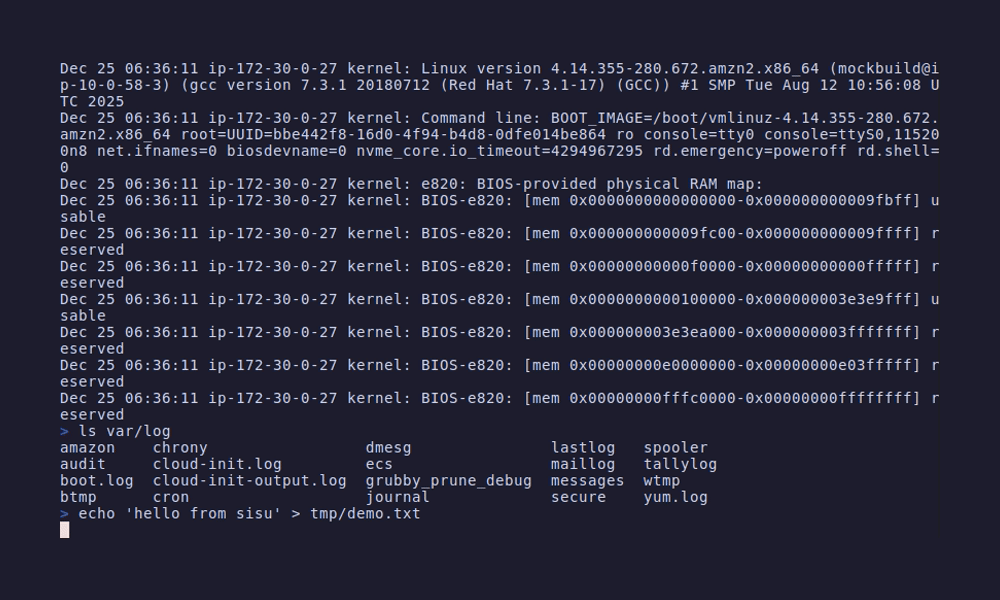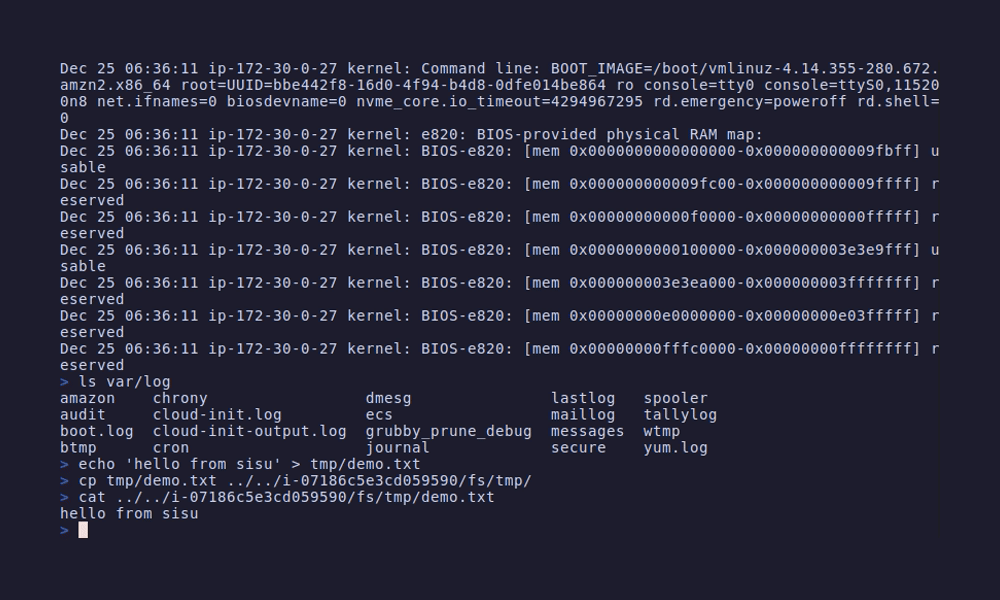
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
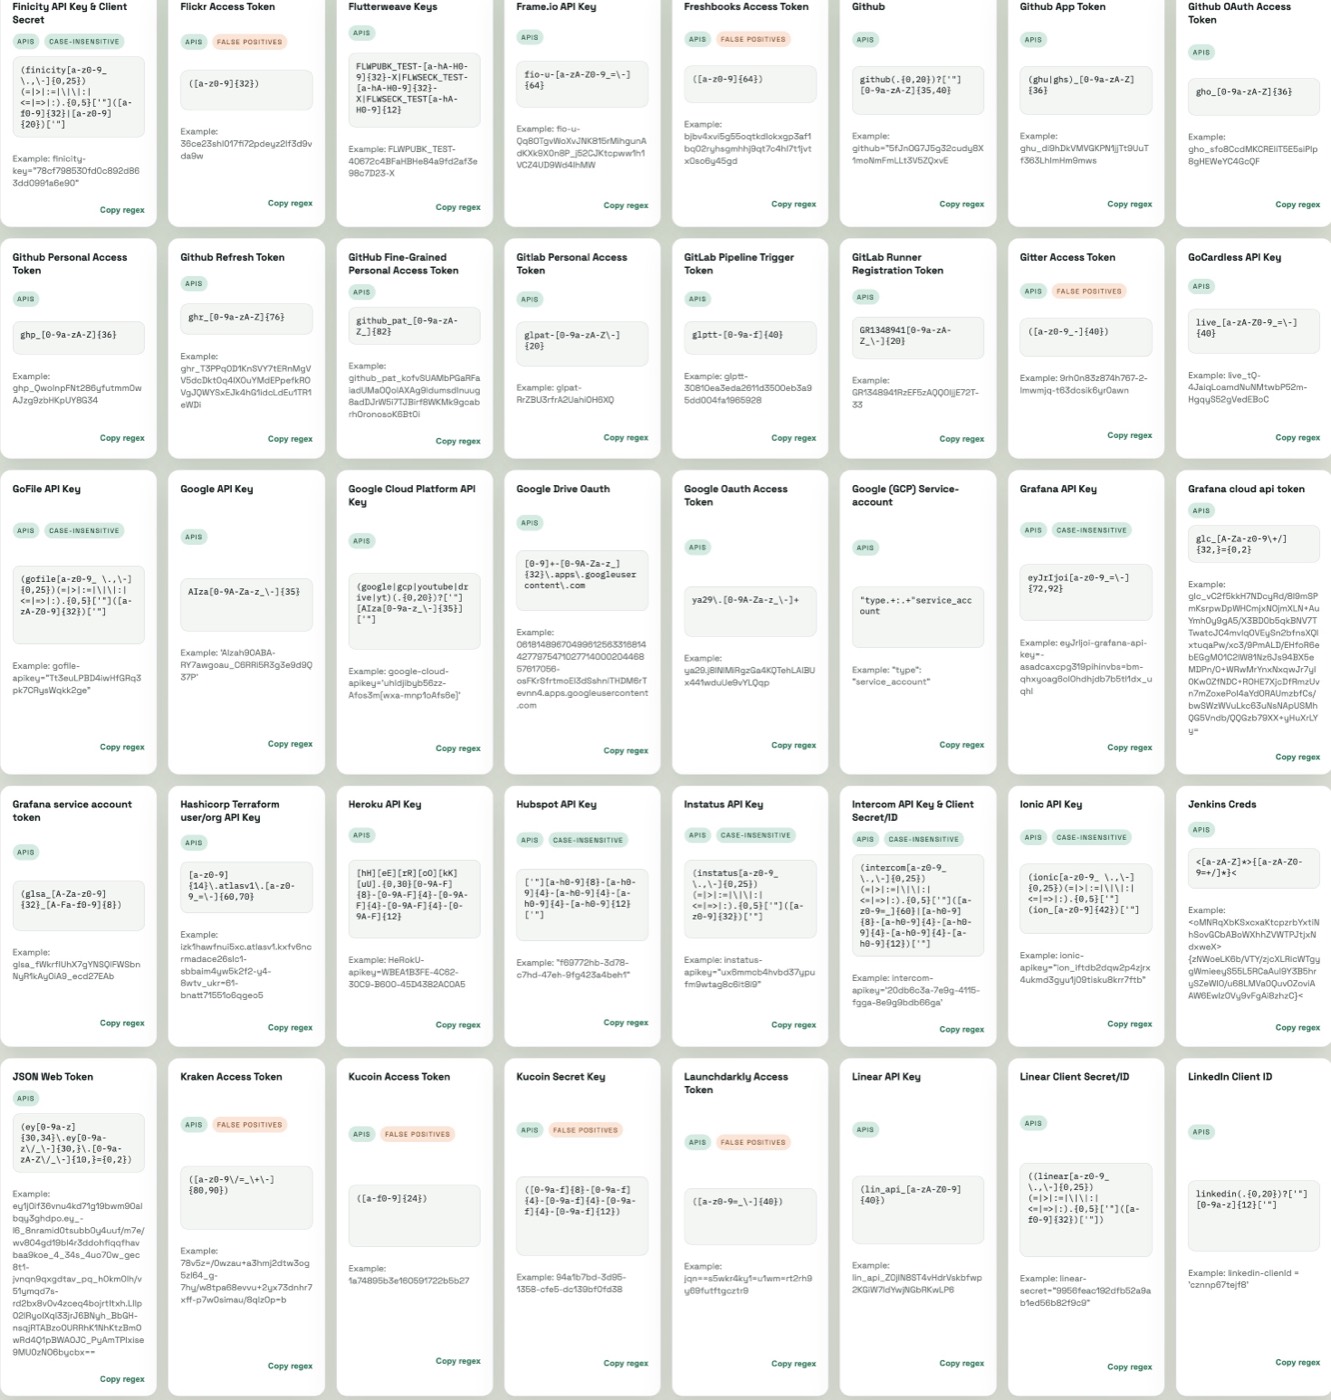 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.

 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
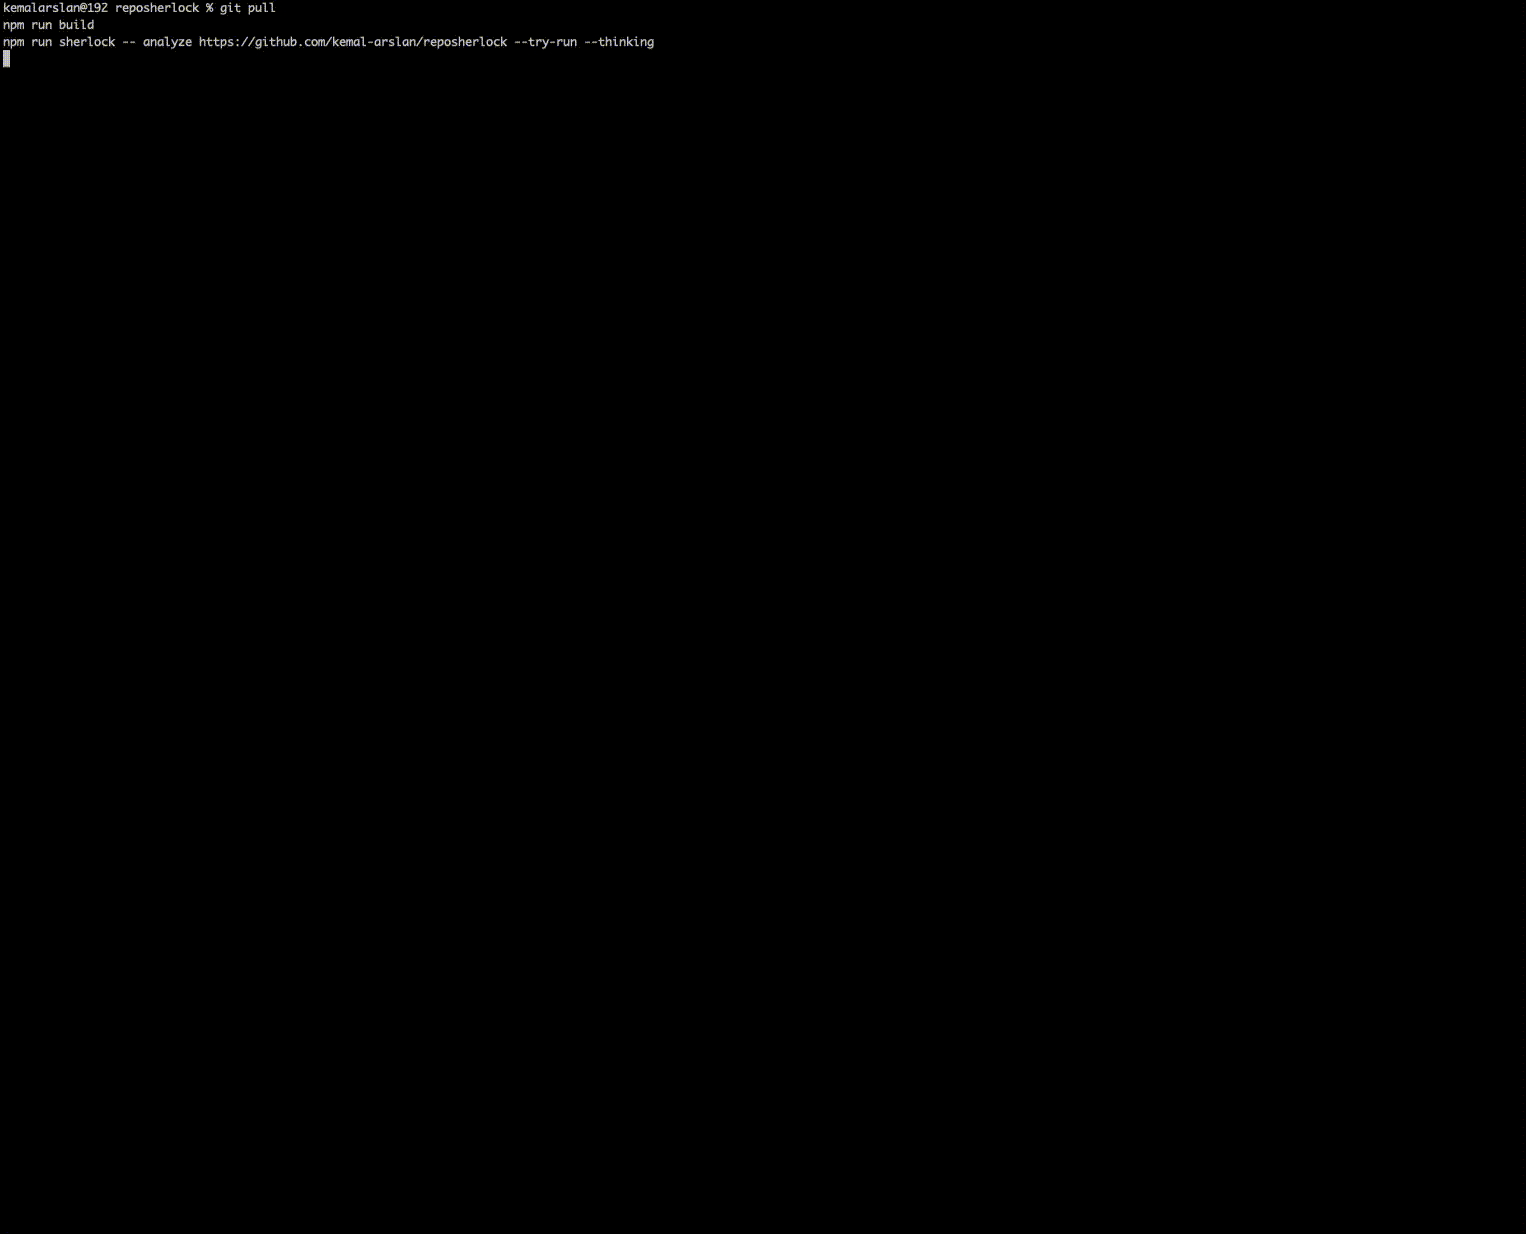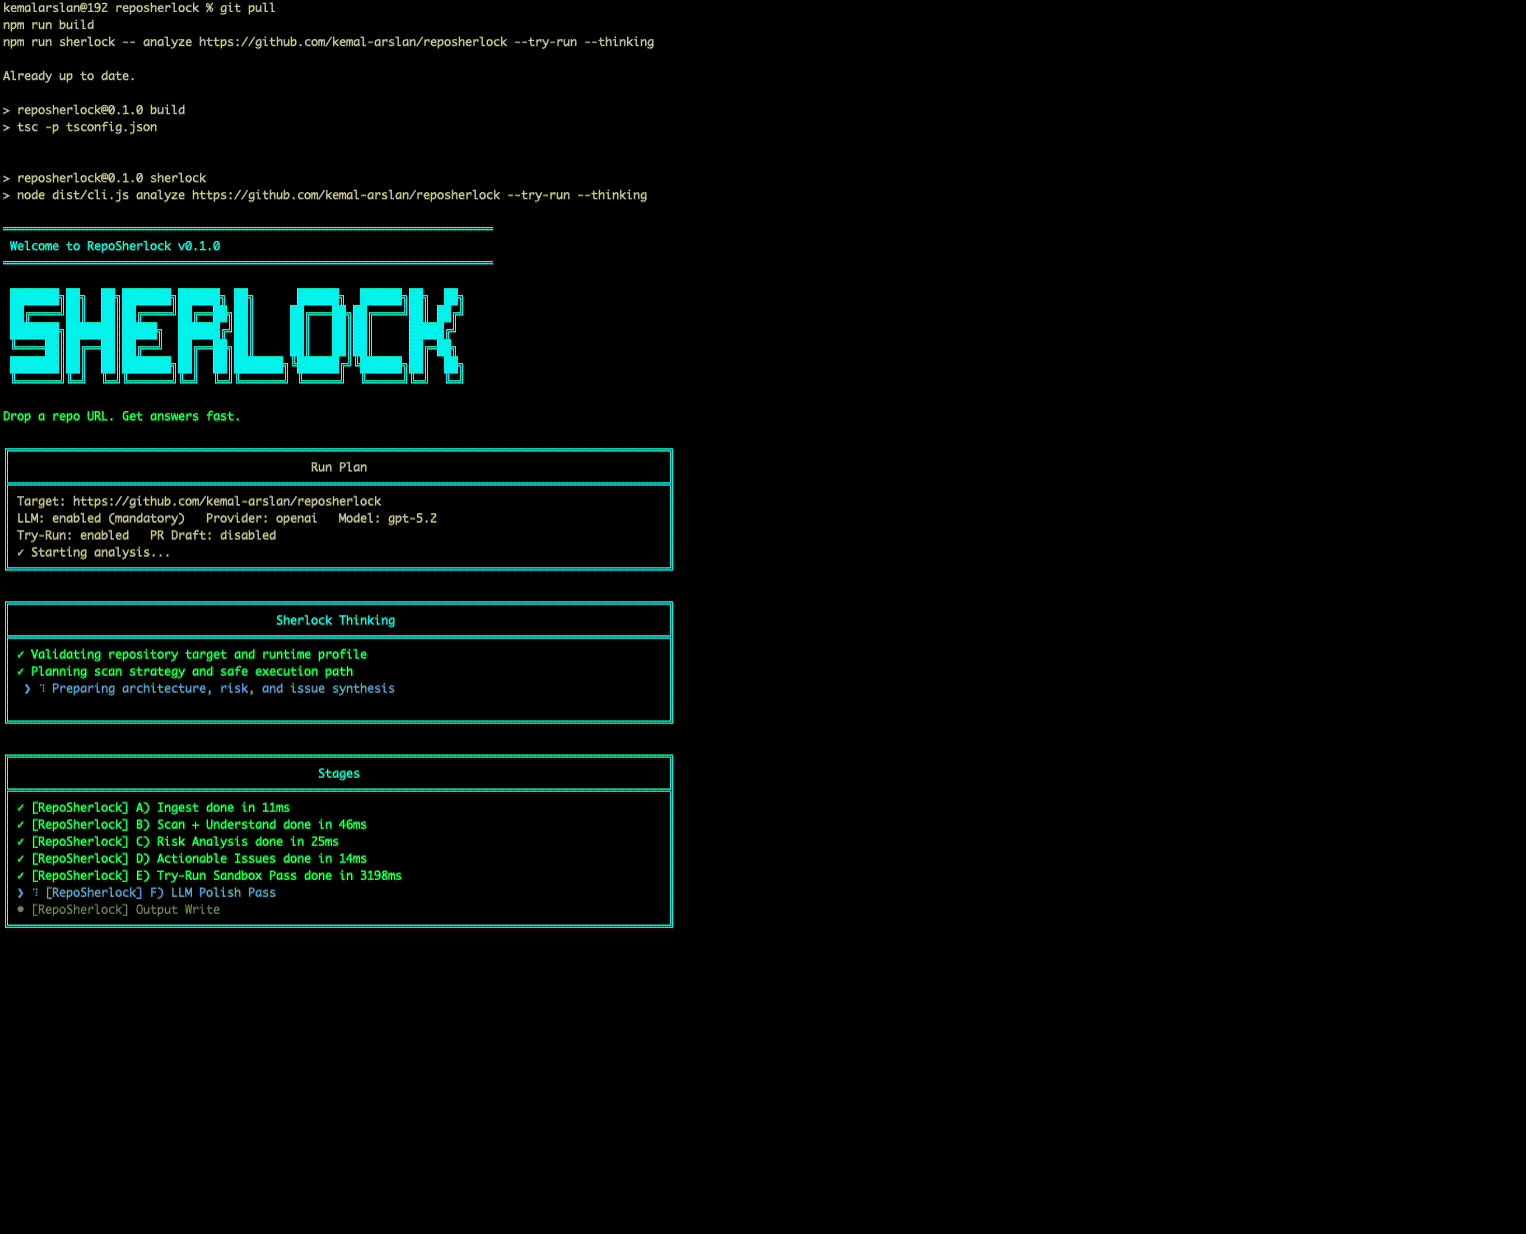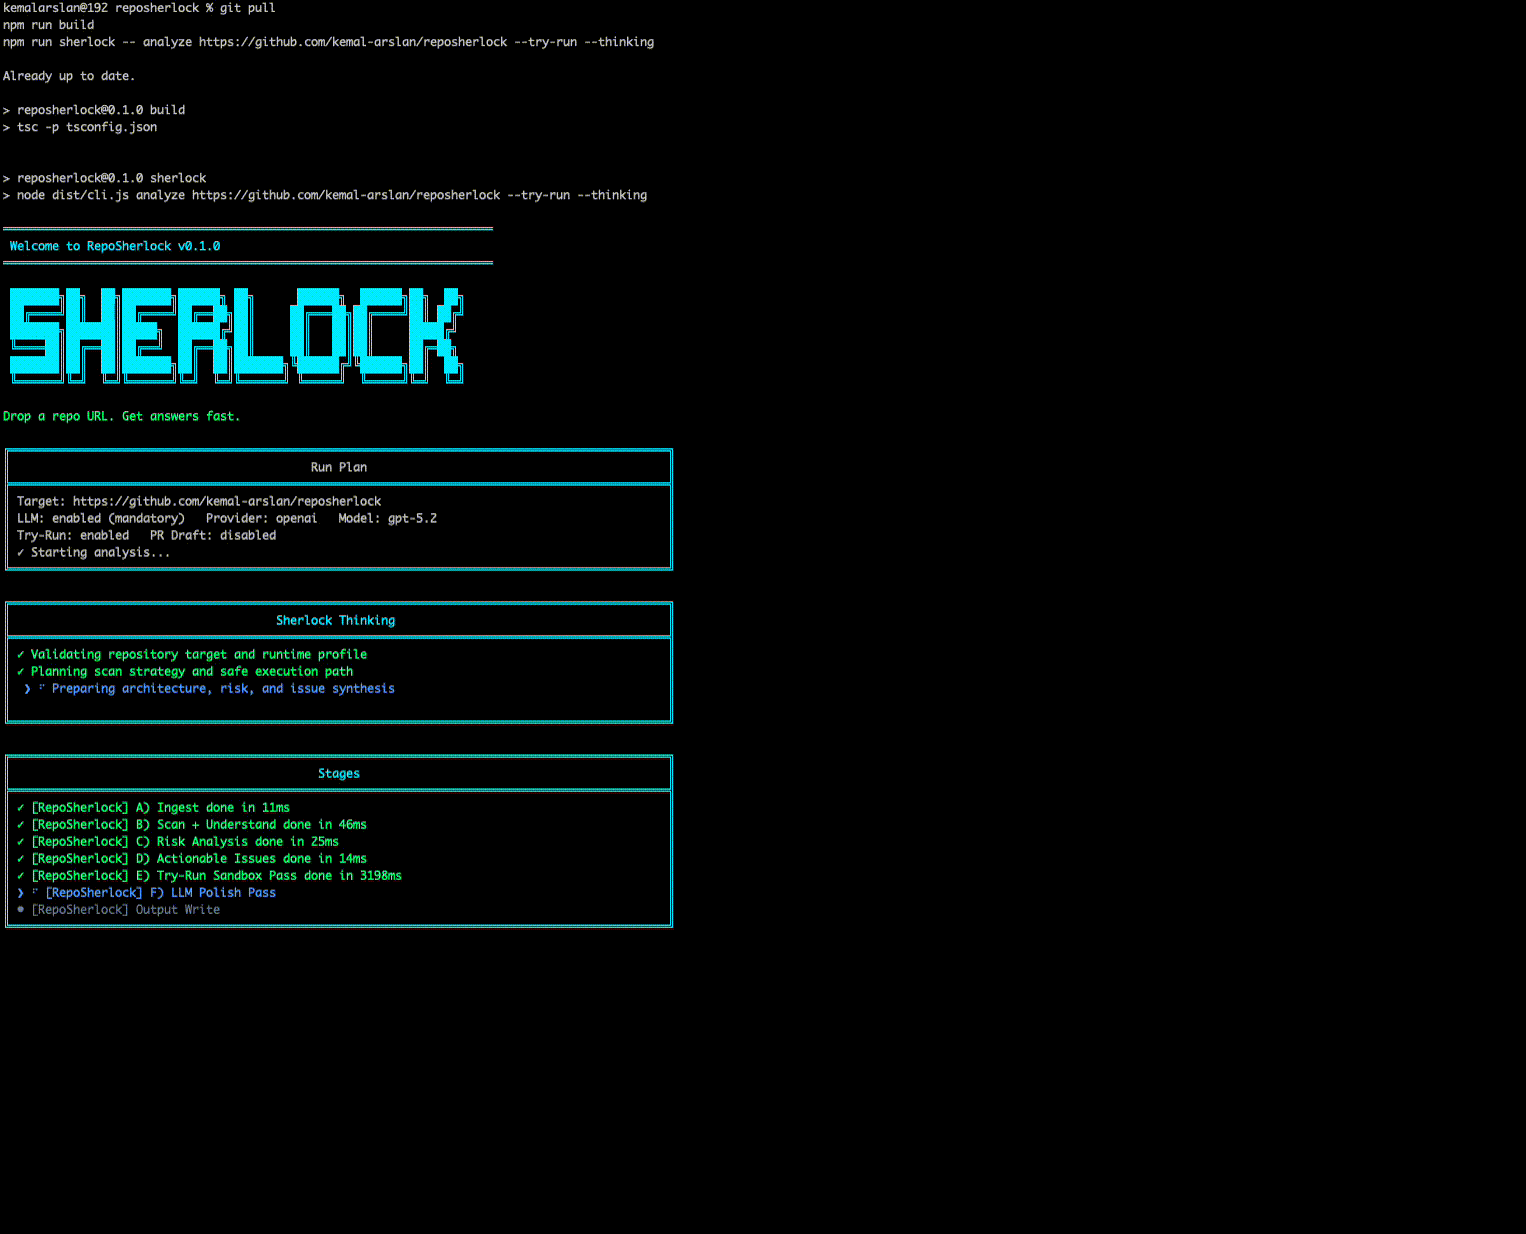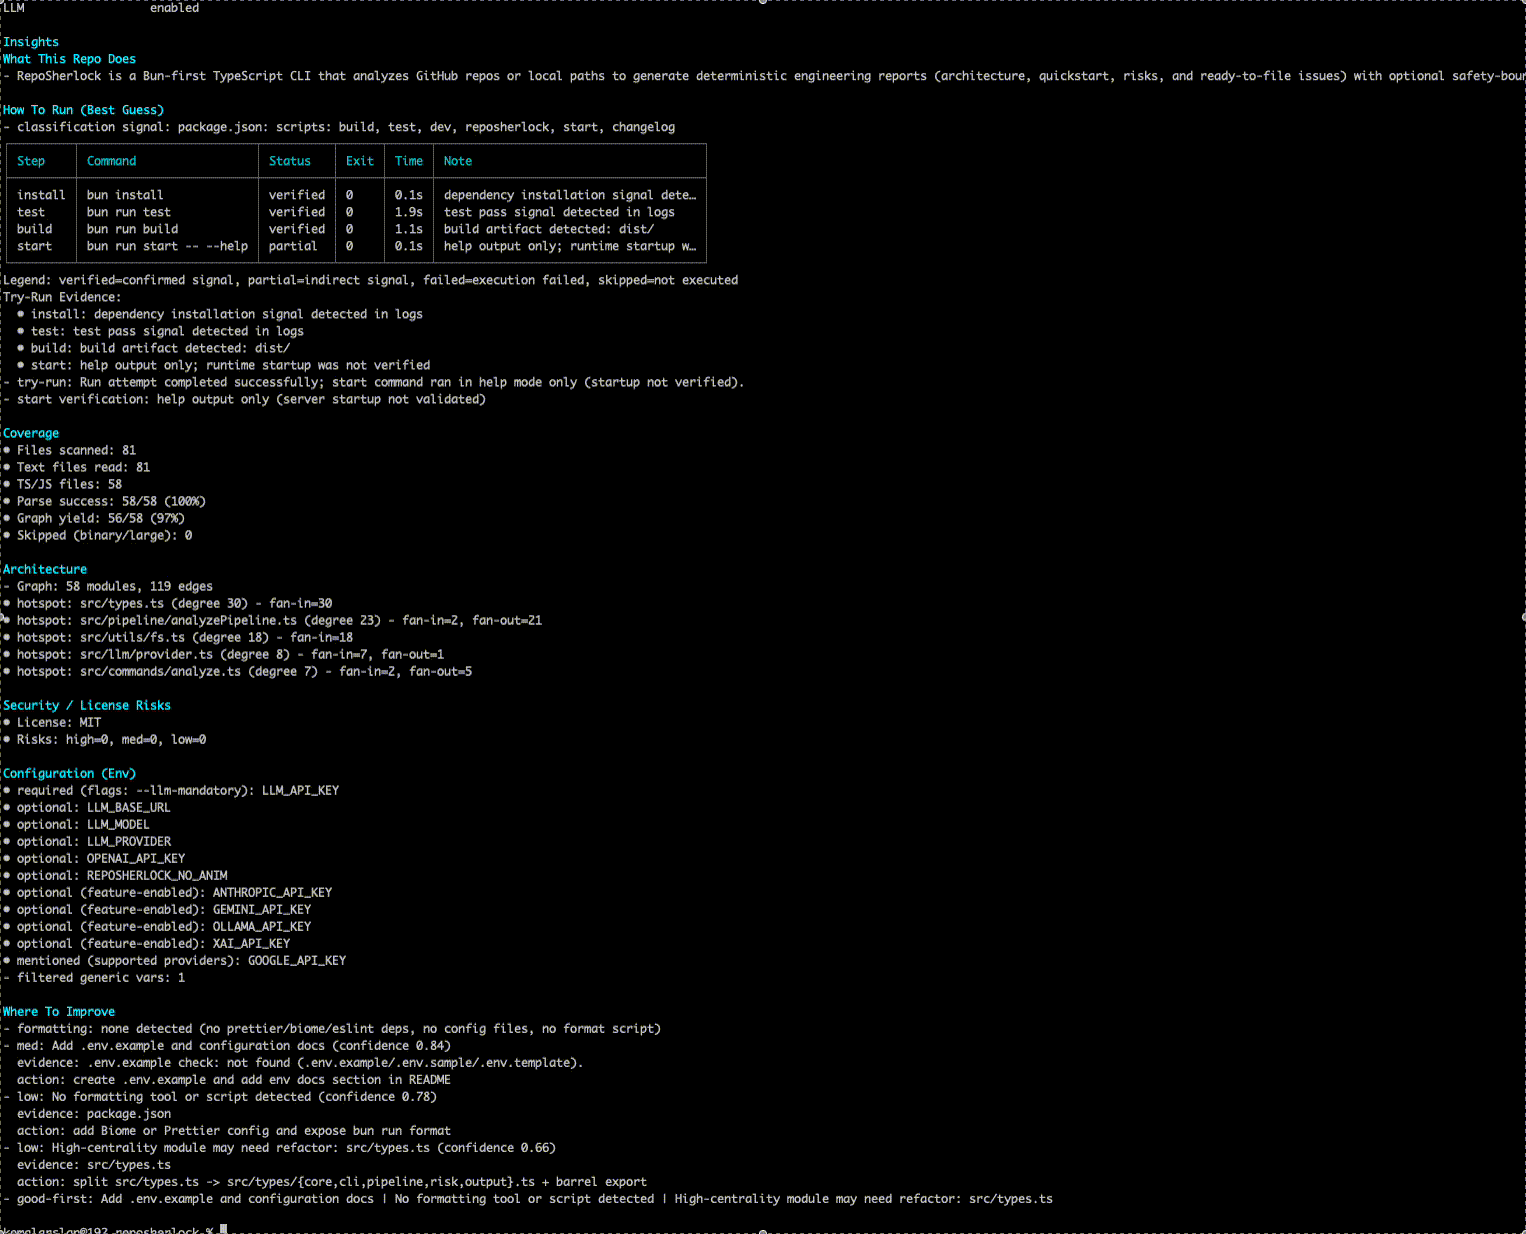 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
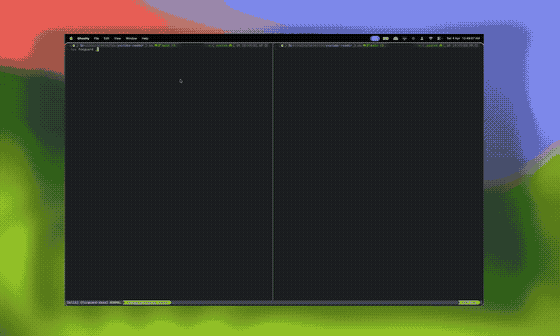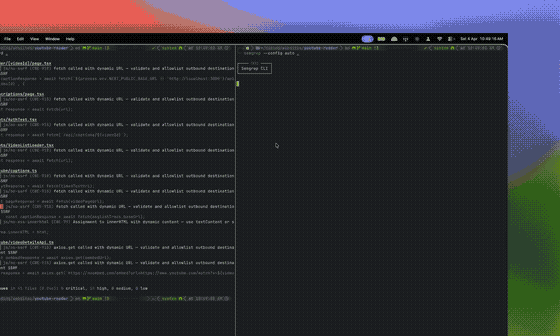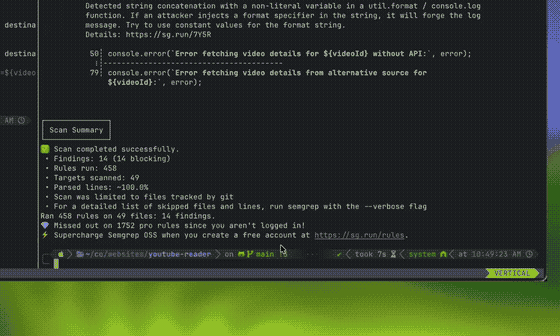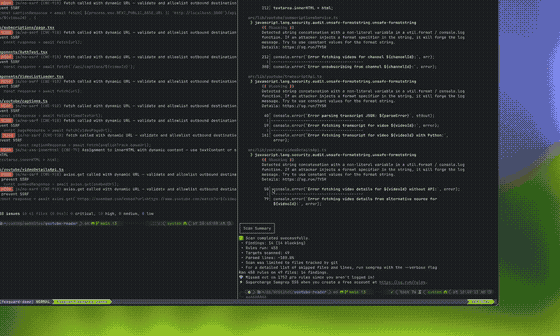 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 kontext-security/kontext-cli
Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.
 mhaggis/package-inferno
A Public Package Scanner for The Community
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…