
KubiScan
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
authentication-authorizationcloud-securityconfiguration-auditing+8
cyberark/kubiscanA tool to scan Kubernetes cluster for risky permissions
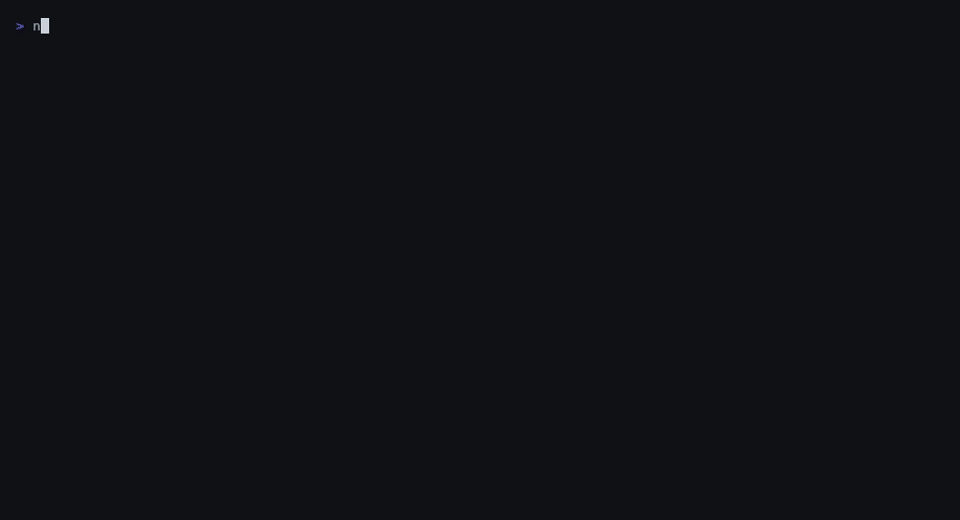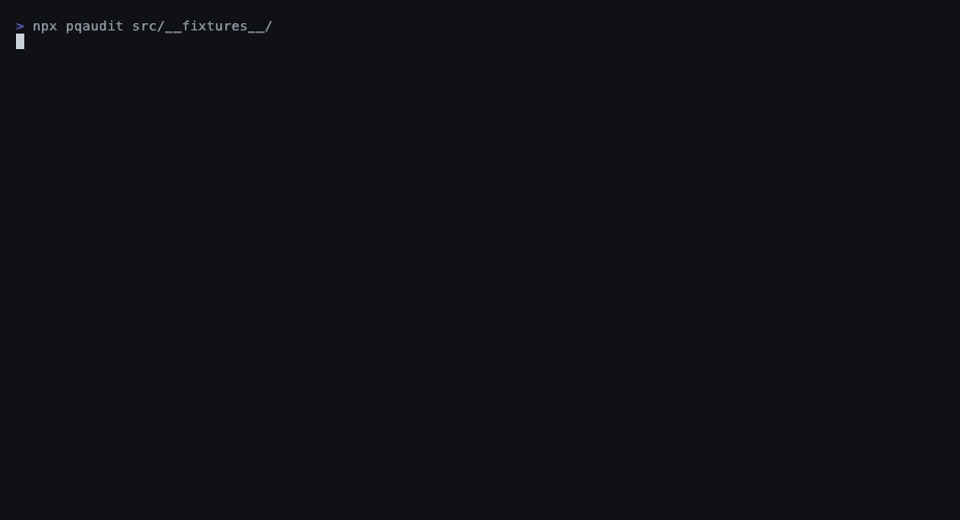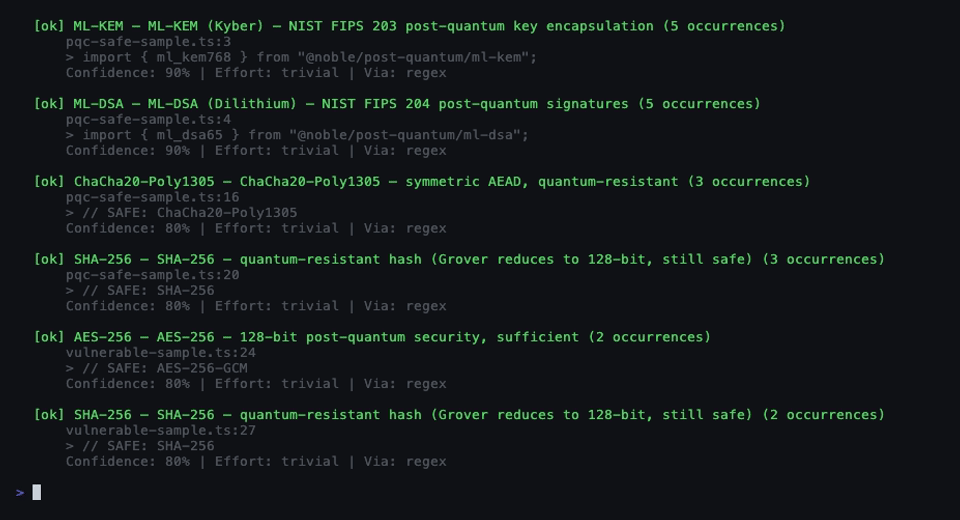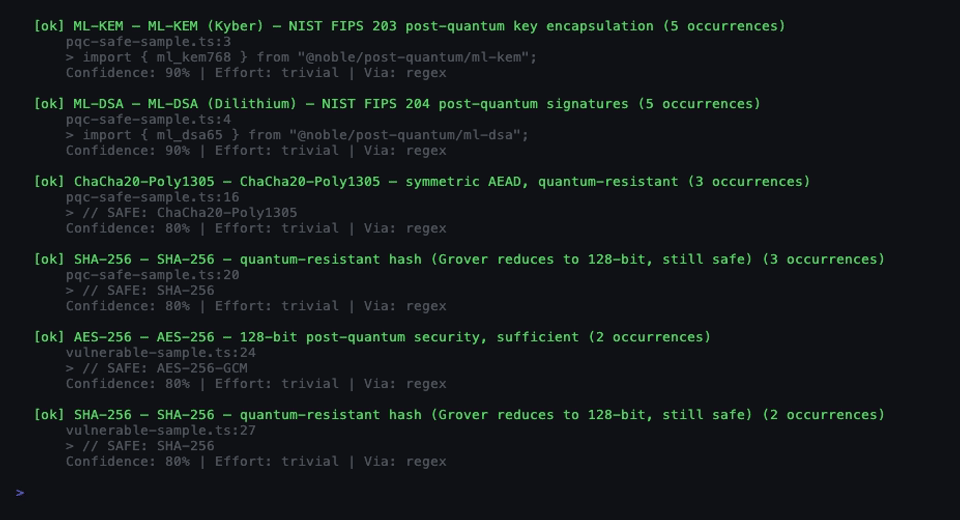 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 unkl4b/gitminer
Tool for advanced mining for content on Github
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
 ghostpack/deeppass
Hunting for passwords with deep learning
 talkaboutcybersecurity/gitmonitor
One way to continuously monitor sensitive information that could be exposed on Github
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
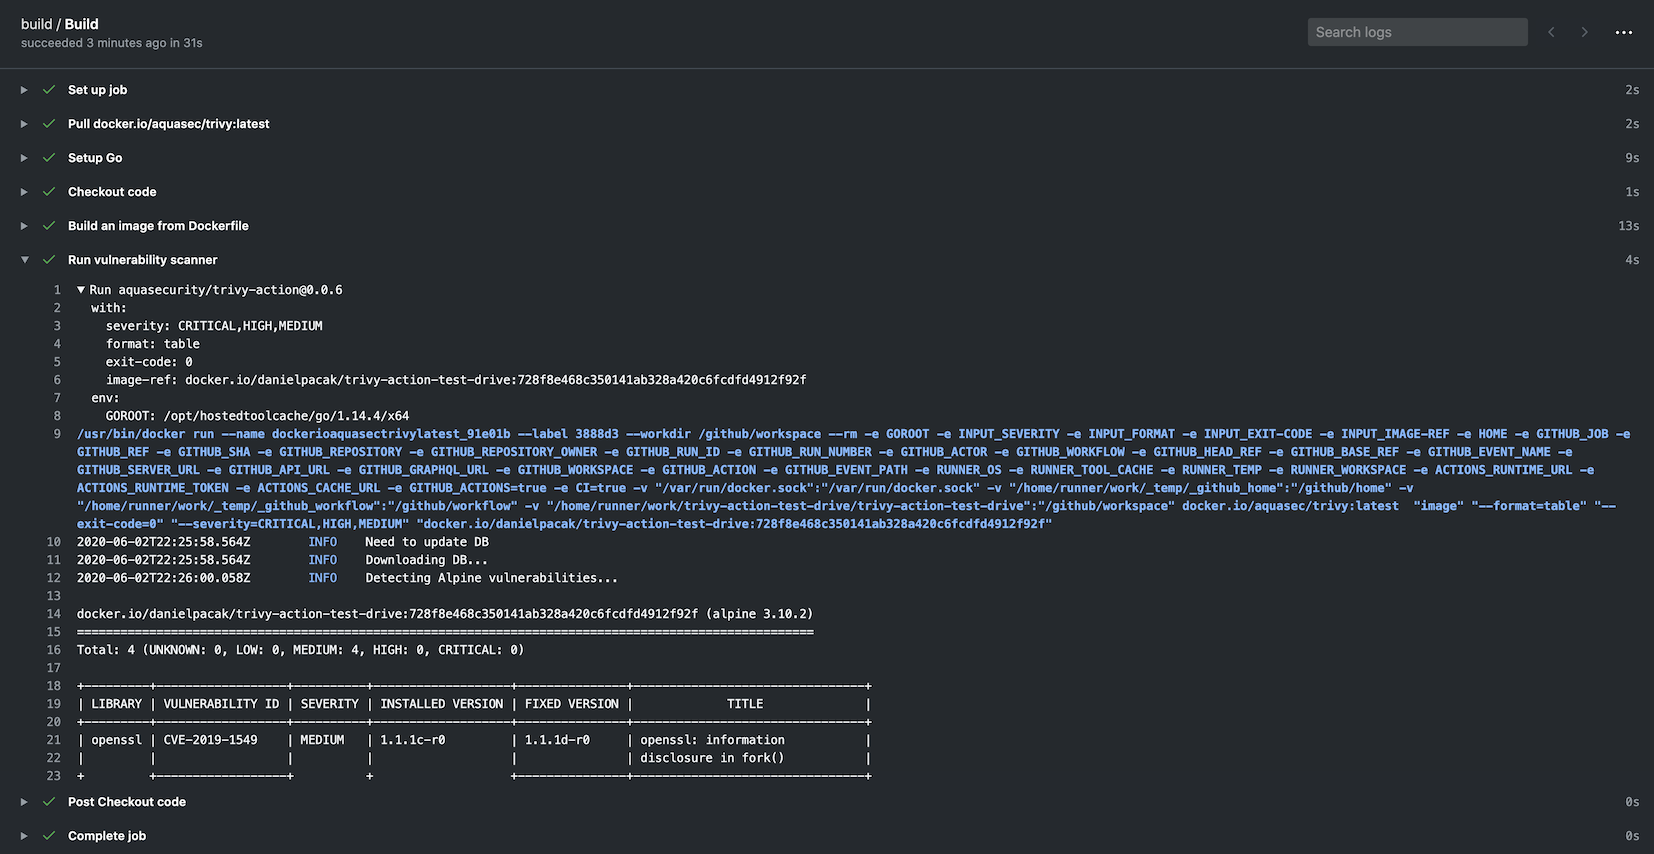 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
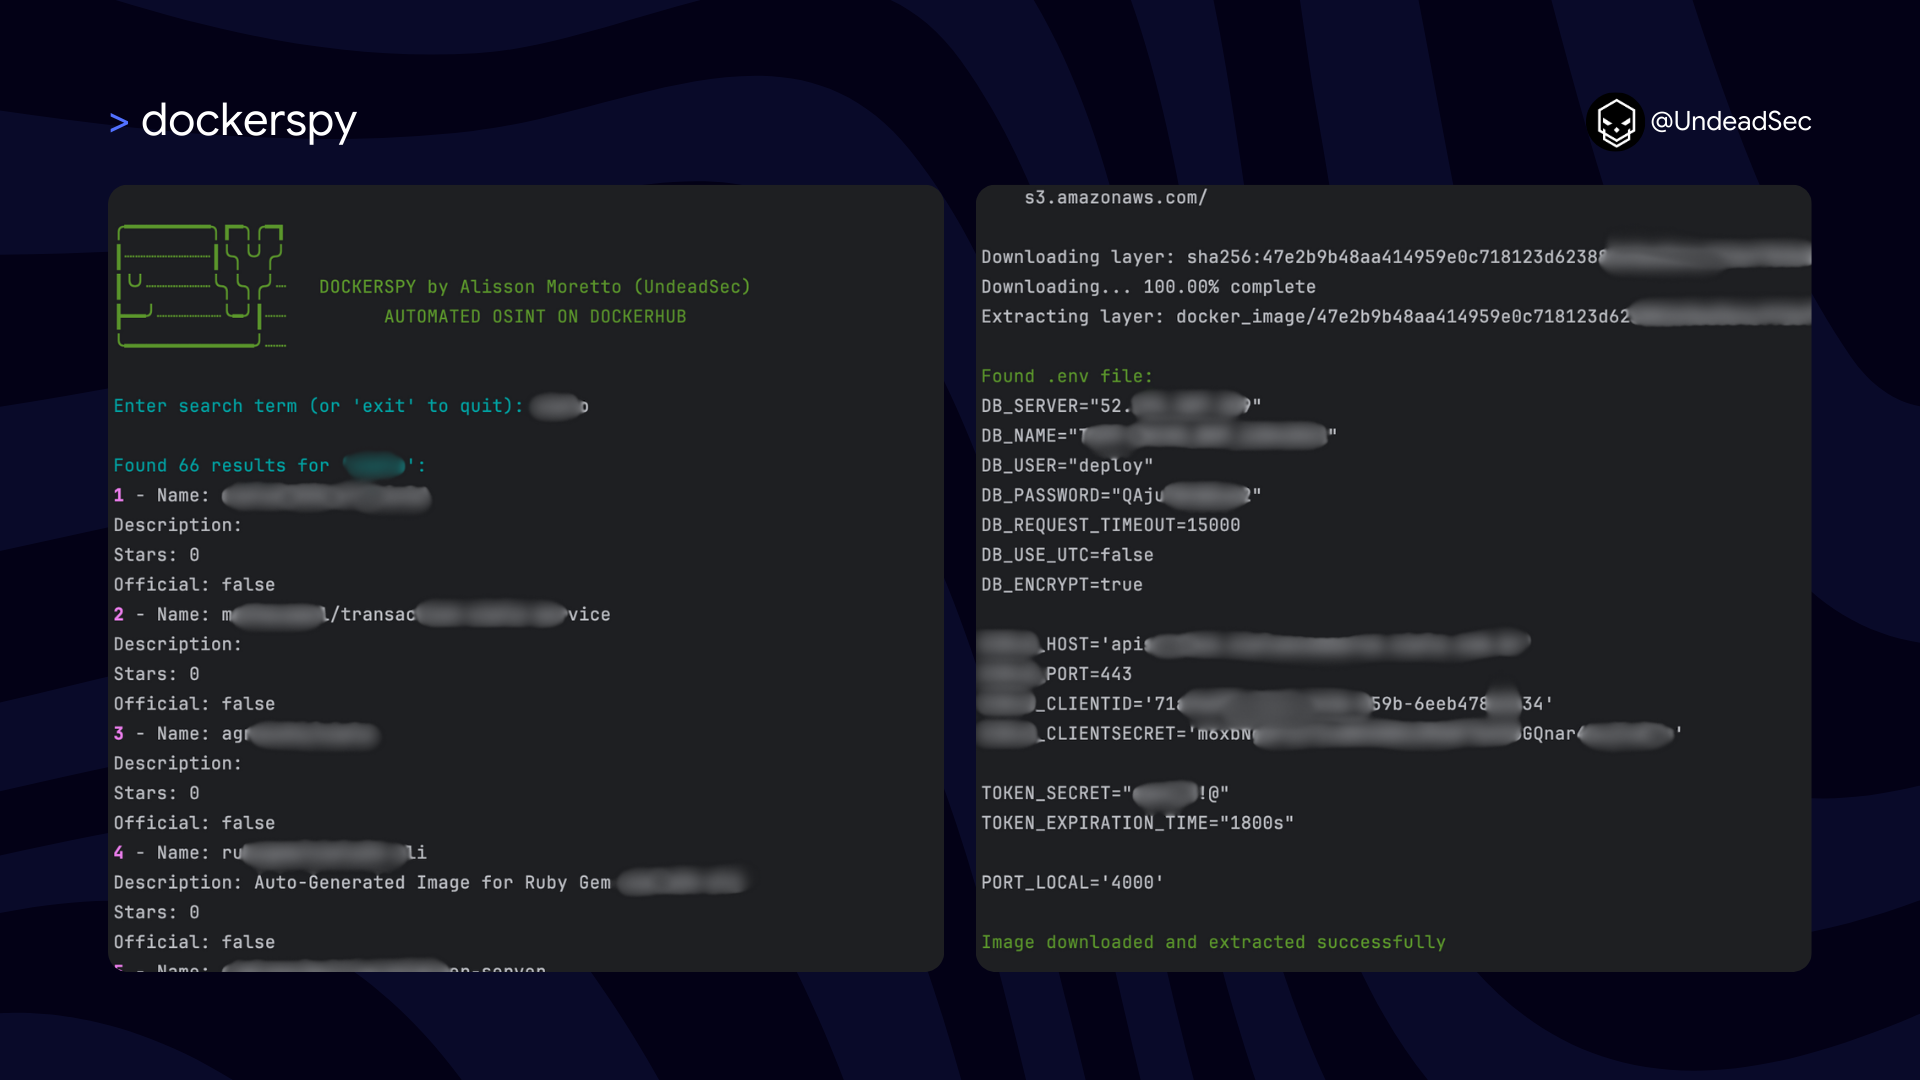 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 santhreal/keyhog
Open-source secret scanner in Rust
 randomrobbiebf/chart-down
Extracts all the chart lists from ChartMuseum