

Archived
gokart
 praetorian-inc/gokart
A static analysis tool for securing Go code
code-analysisdevsecopsmisconfiguration+3
2.2k
 getsops/sops
Simple and flexible tool for managing secrets
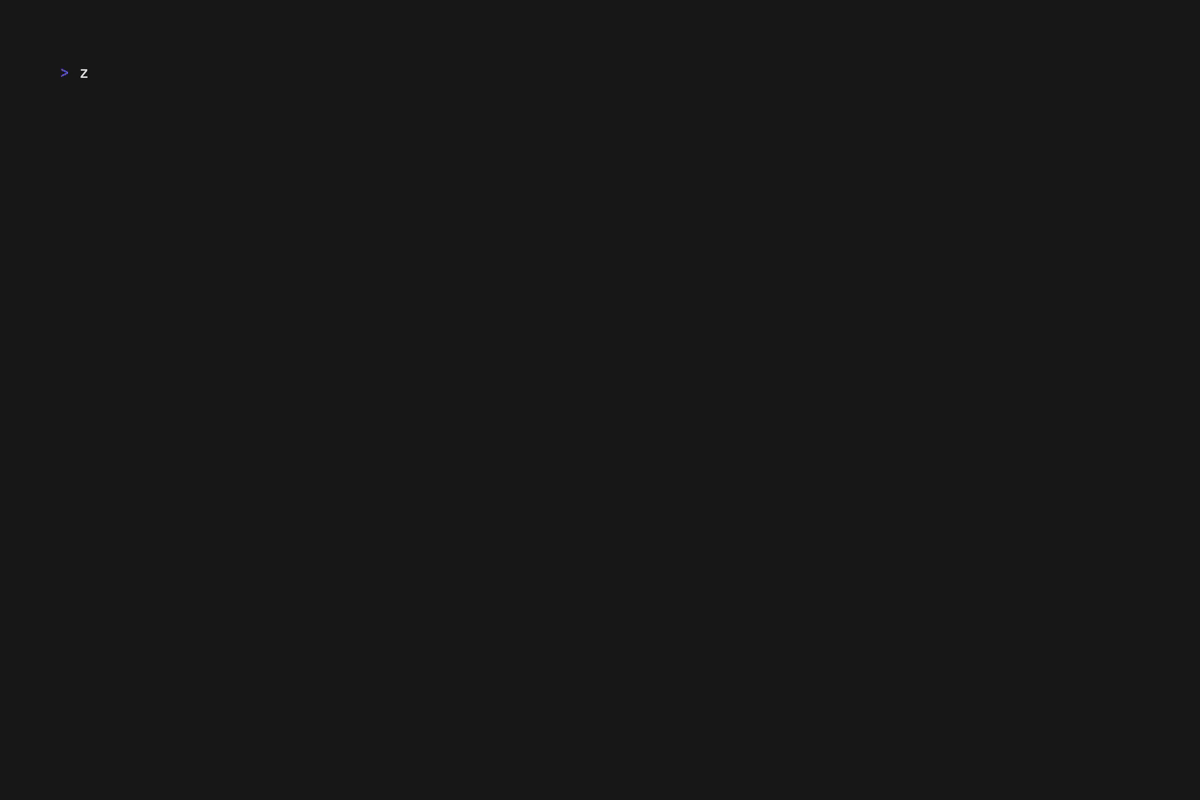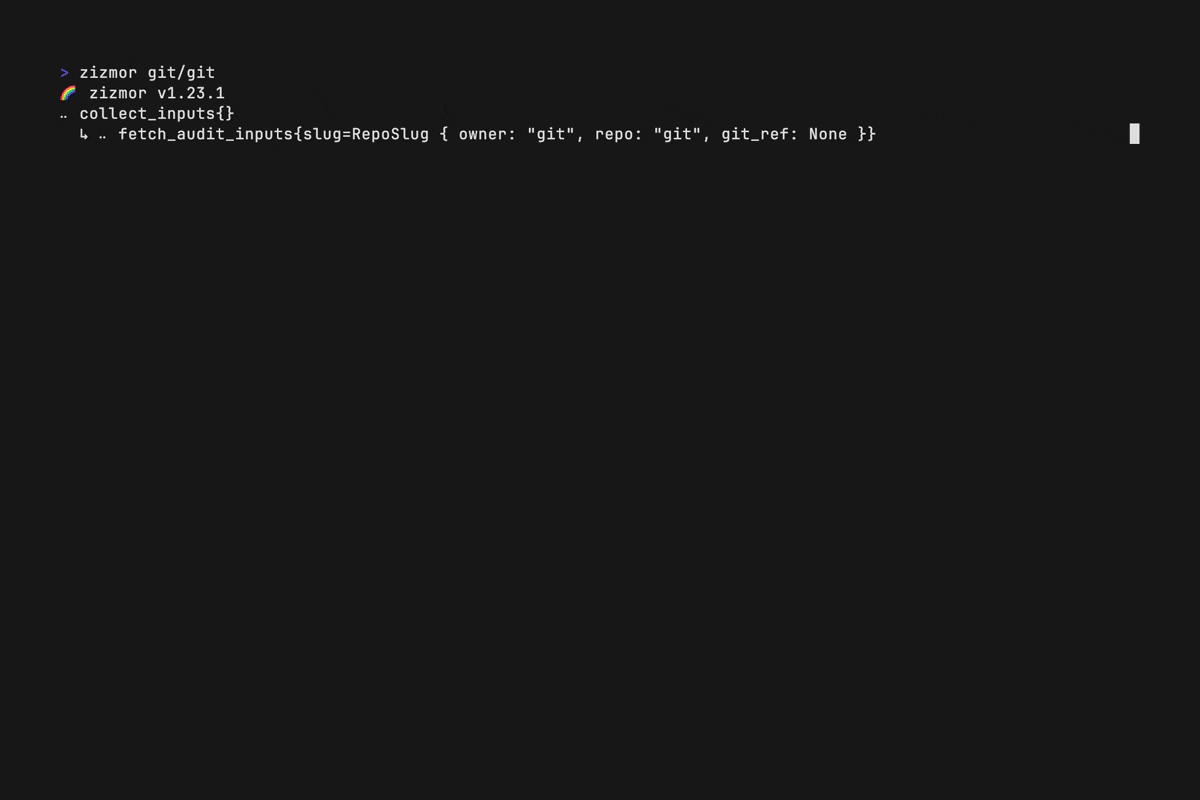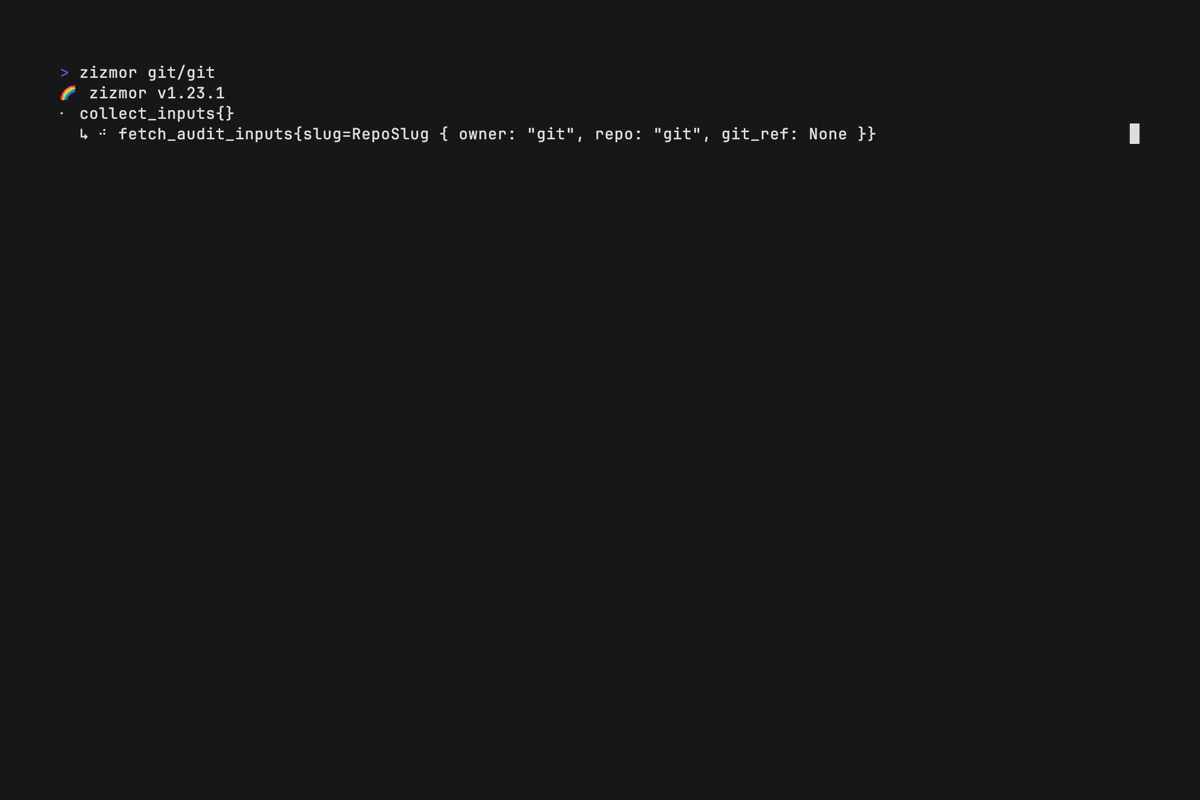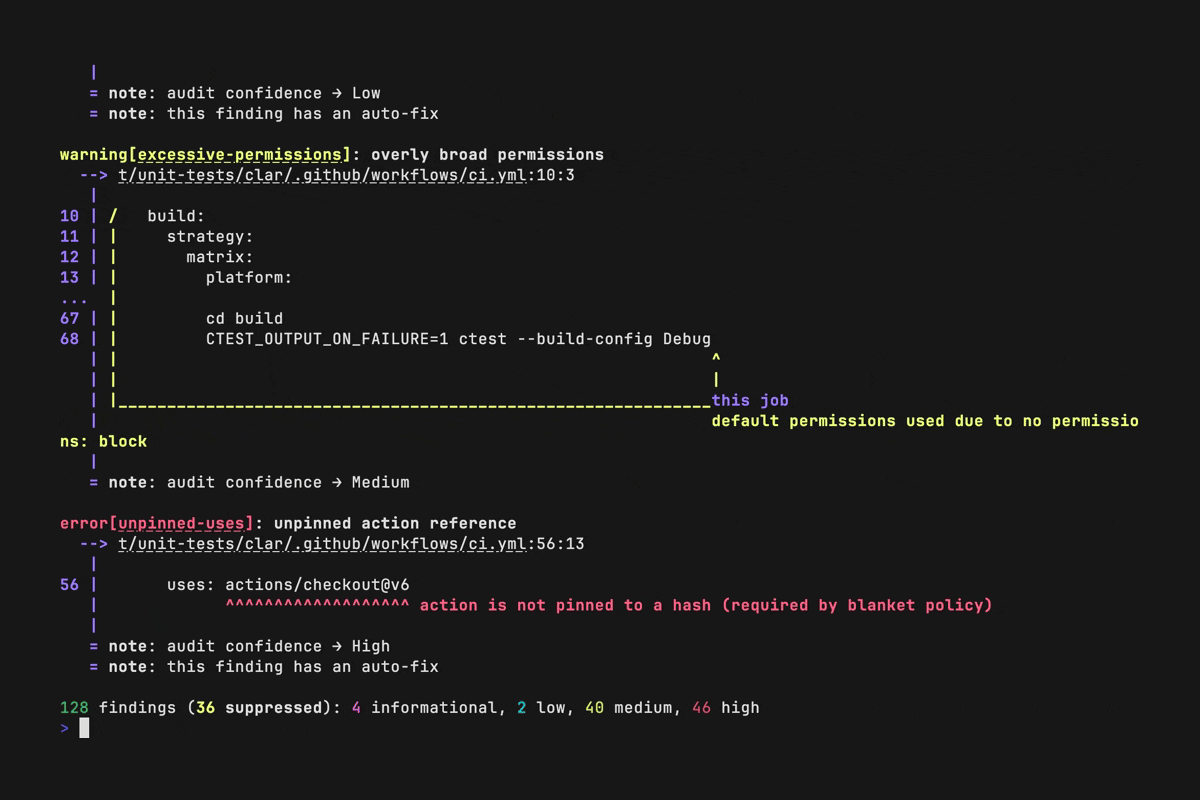 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
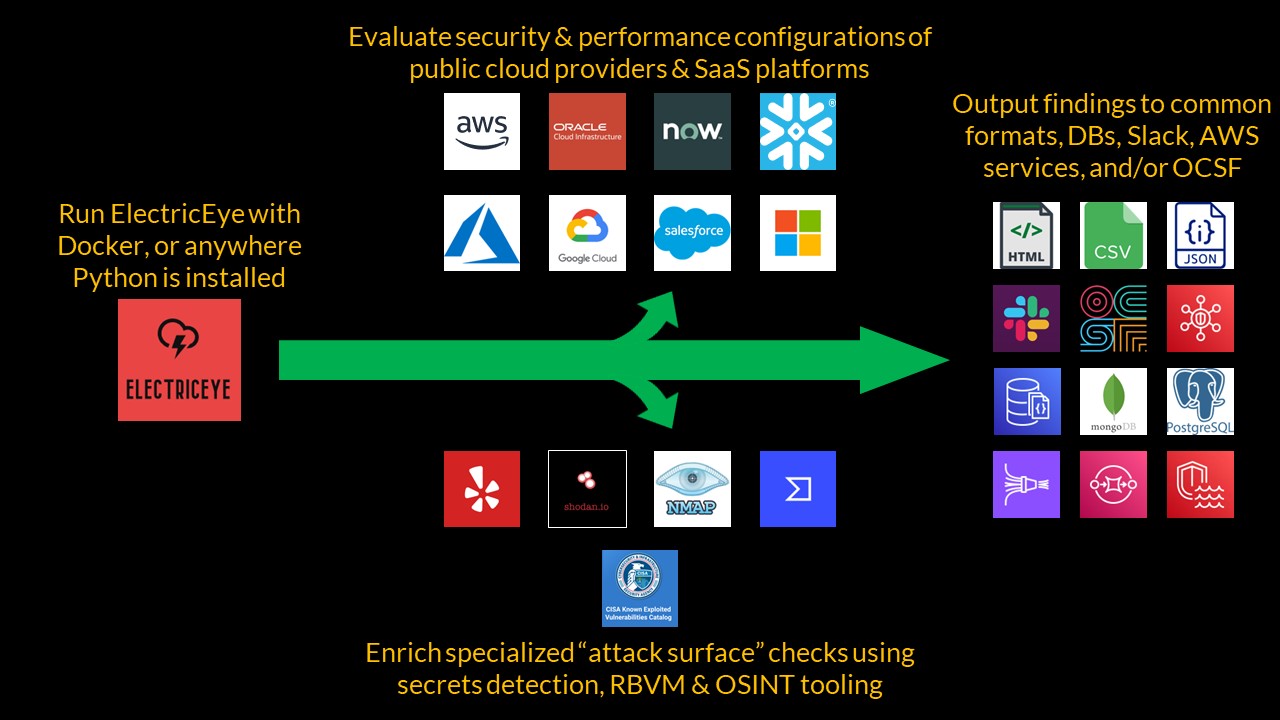 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
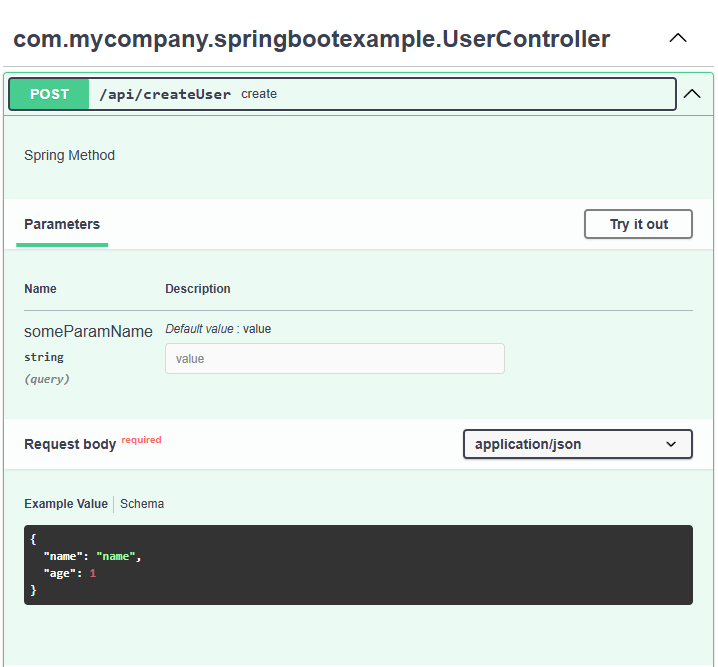 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 reposaur/reposaur
Open source compliance tool for development platforms.
 disruptops/cred_scanner
A simple file-based scanner to look for potential AWS access and secret keys in files
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 anchore/grype
A vulnerability scanner for container images and filesystems
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool