

SecretSifter
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
ai-securityapi-securitydefensive-tools+7
8
owasp/secretsifterOWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 sepehrdaddev/zap-scripts
Zed Attack Proxy Scripts for finding CVEs and Secrets.
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 r3curs1v3-pr0xy/vajra
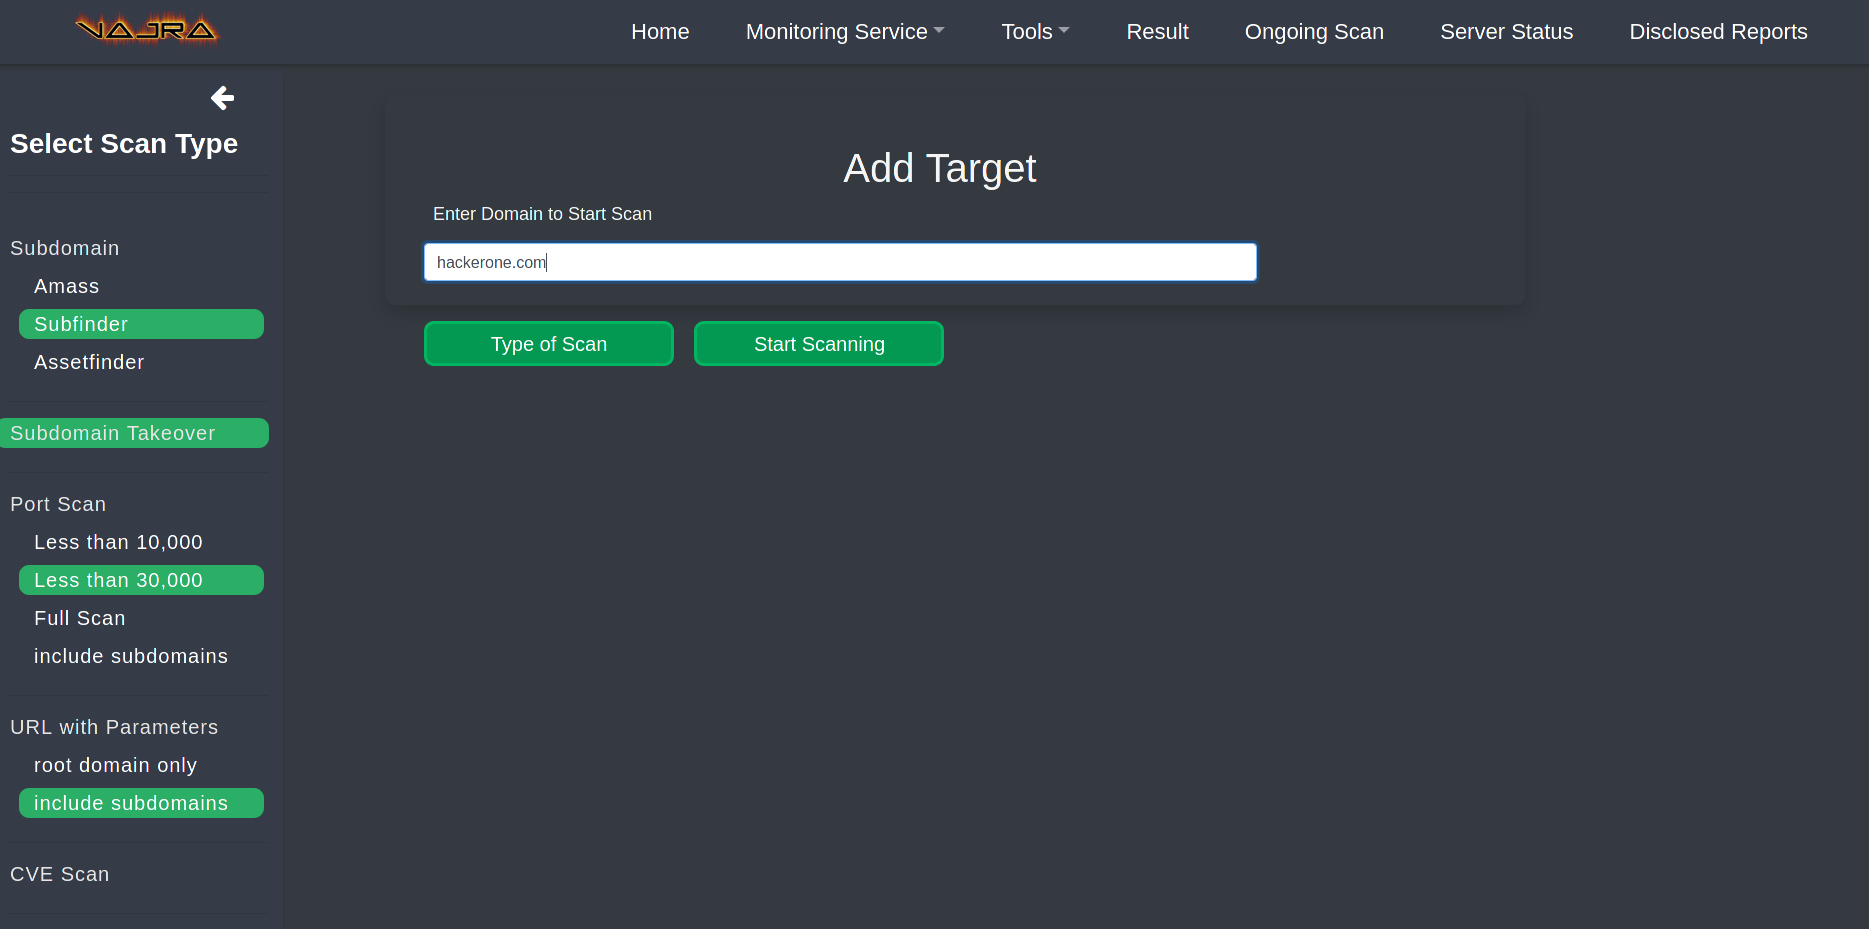
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 blacklanternsecurity/badsecrets
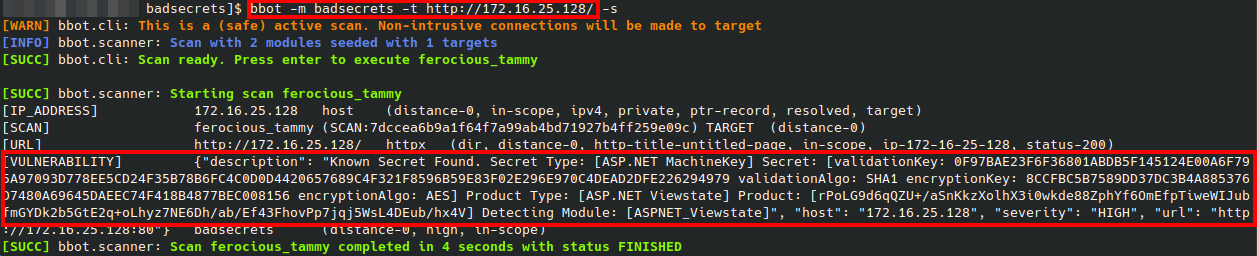
A library for detecting known secrets across many web frameworks
 irsdl/crapsecrets
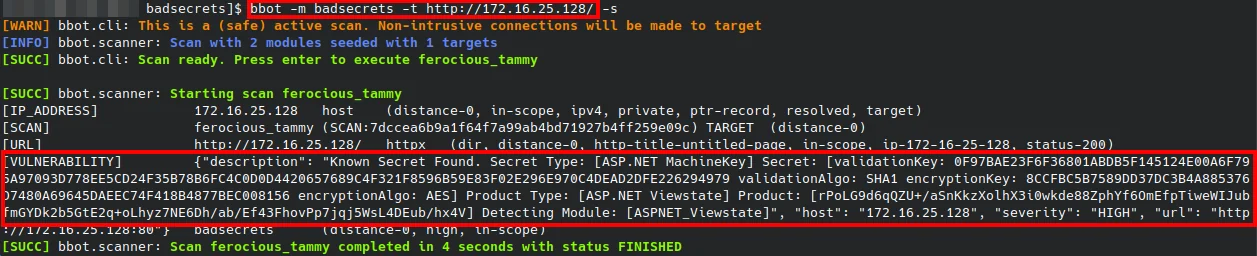
A library for detecting known secrets across many web frameworks
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
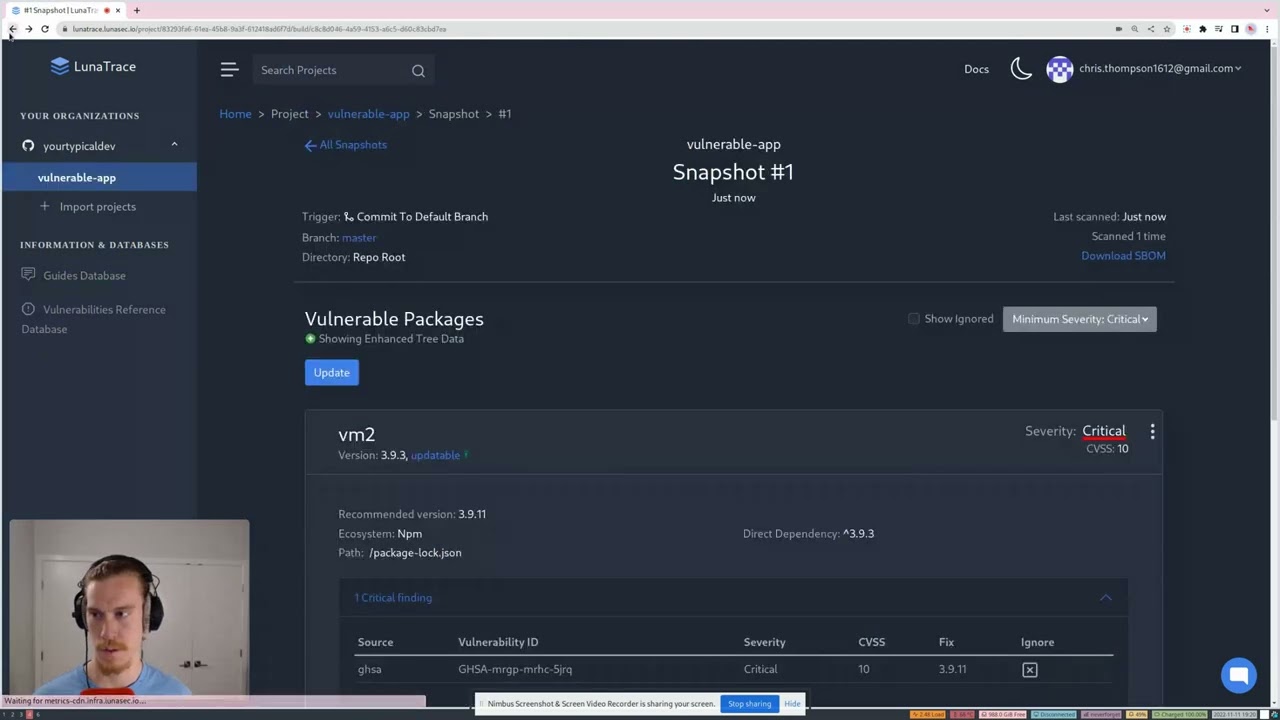 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
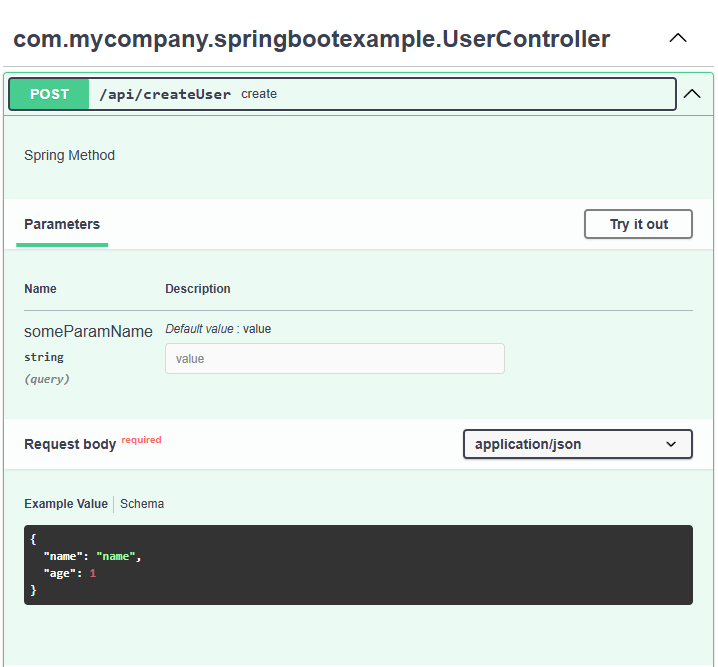 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…