CVE-2025-14847_Expolit

Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…

Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…

A tool to scan Kubernetes cluster for risky permissions

Pillage filesystems for sensitive information with Go 🔍

CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…

"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…

「🔑」A tool used to hunt down API key leaks in JS files and pages

Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

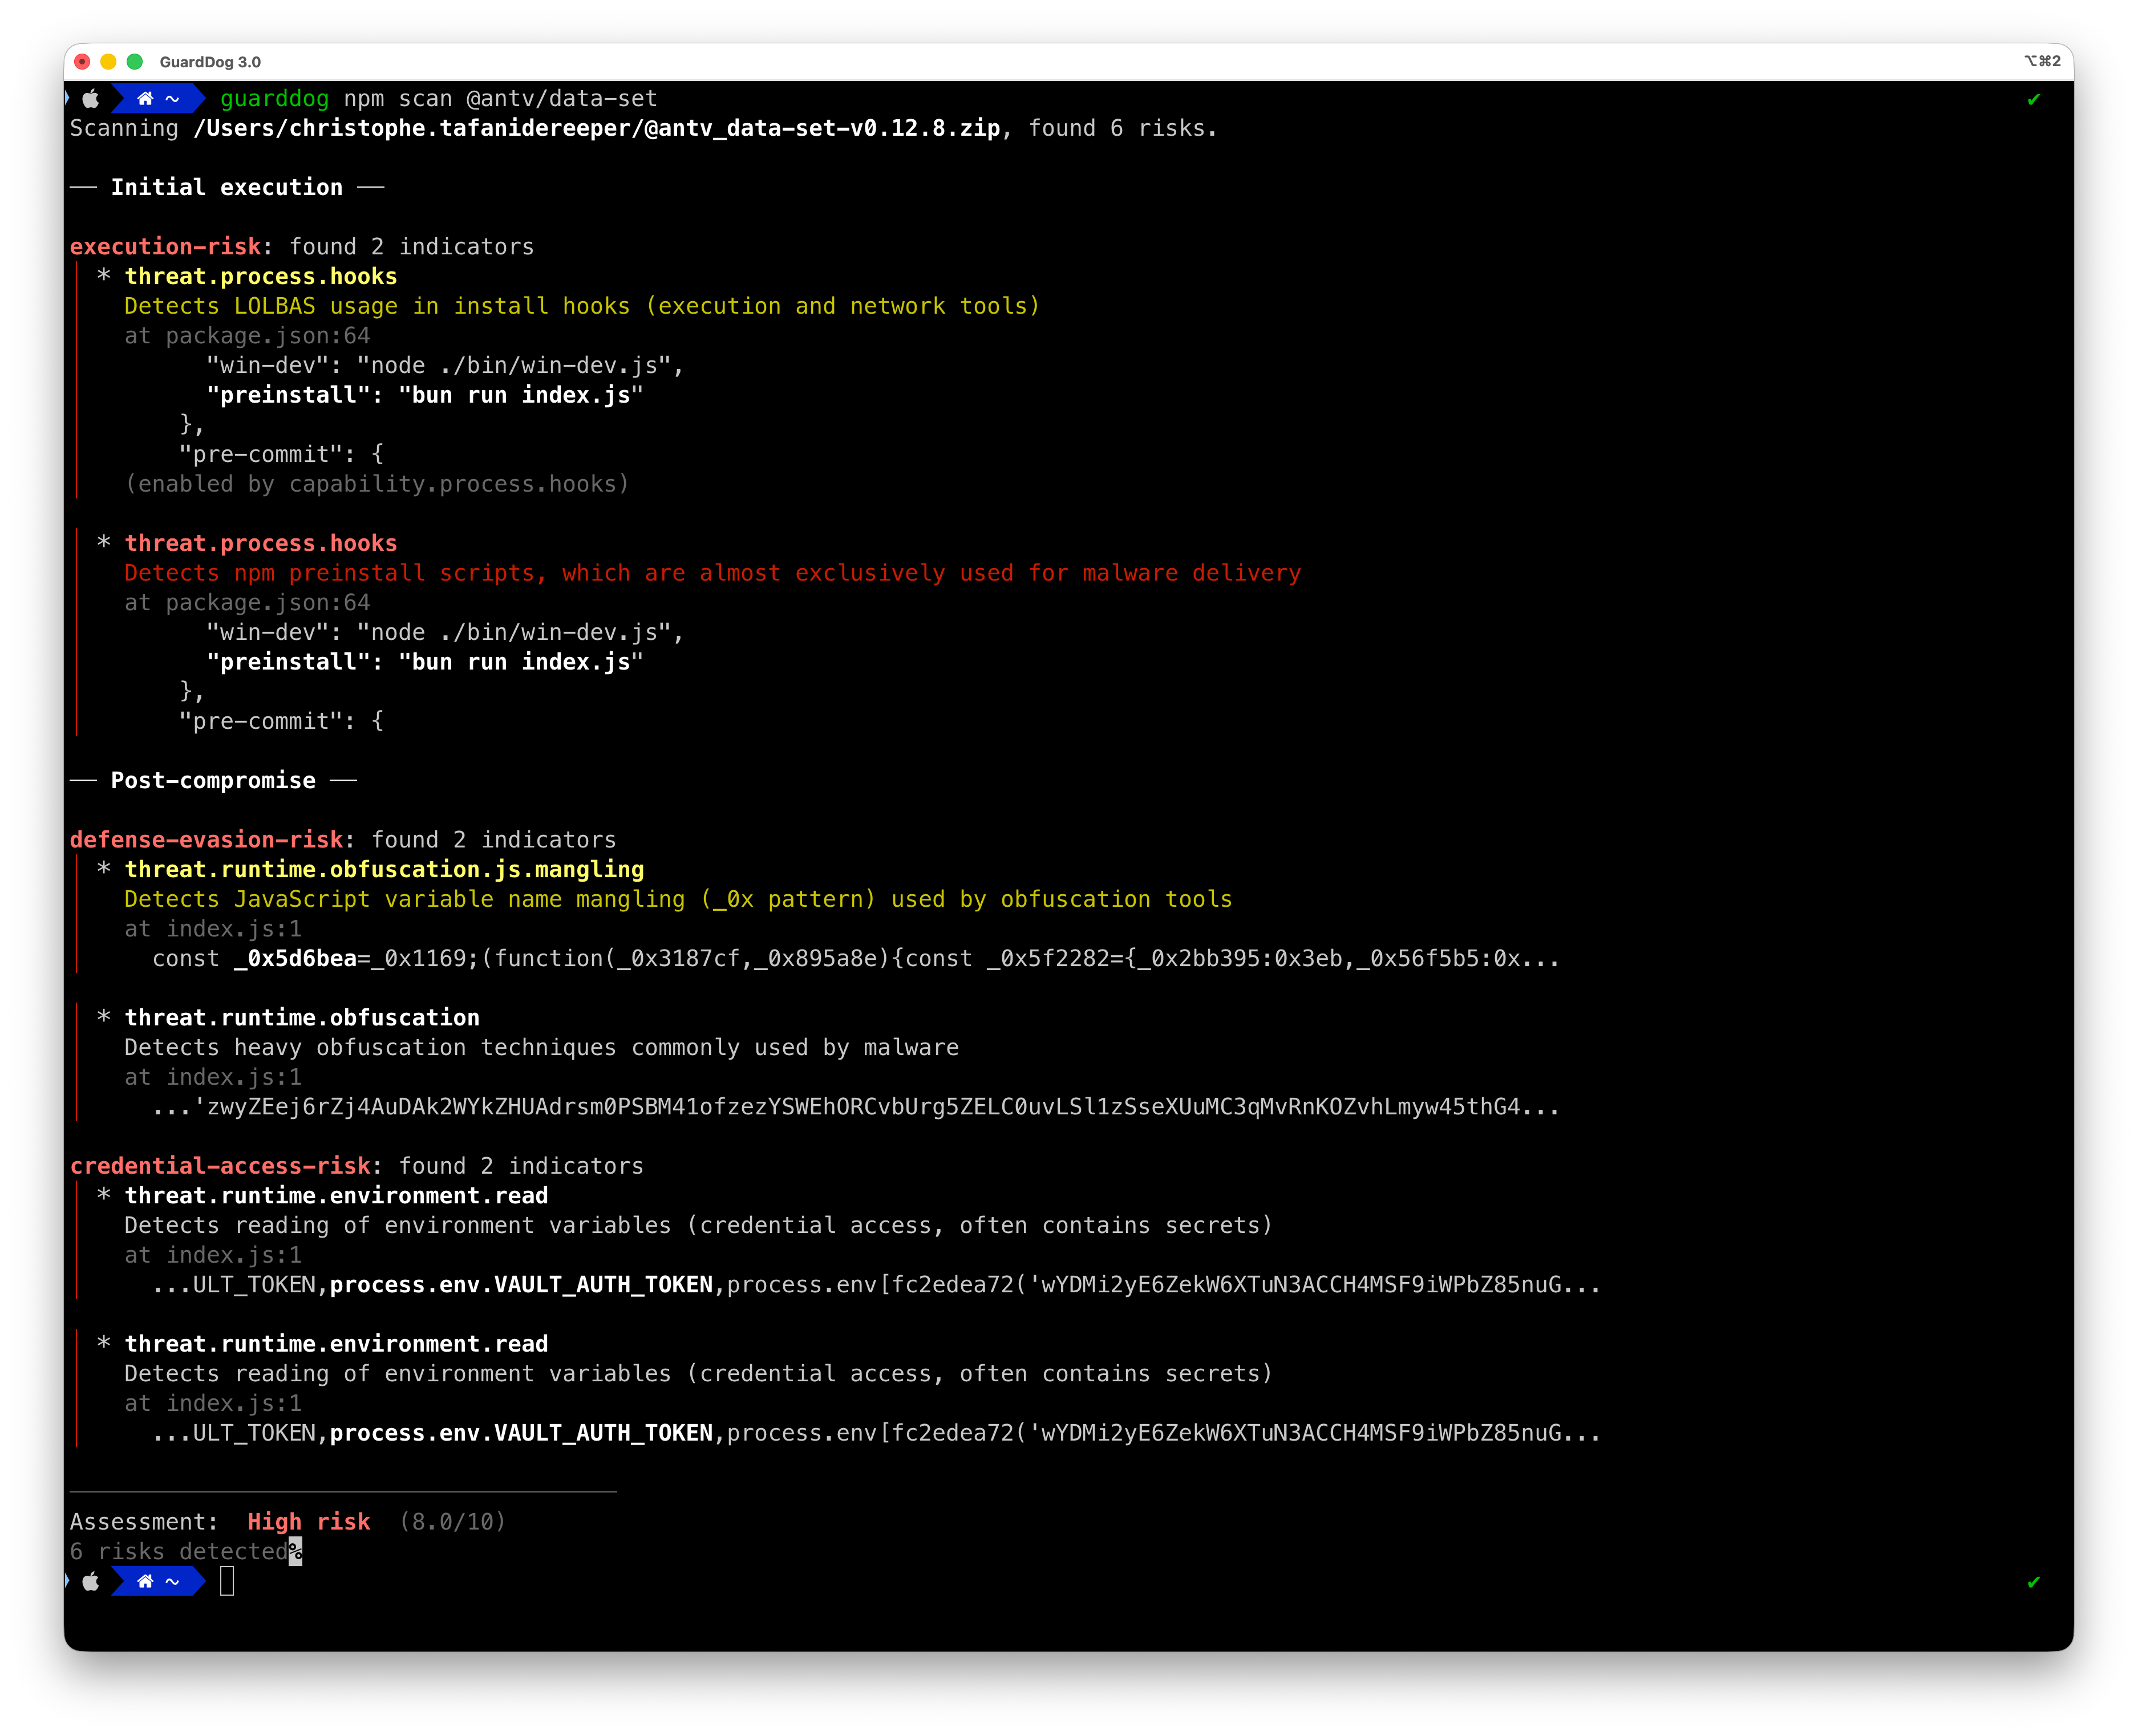
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

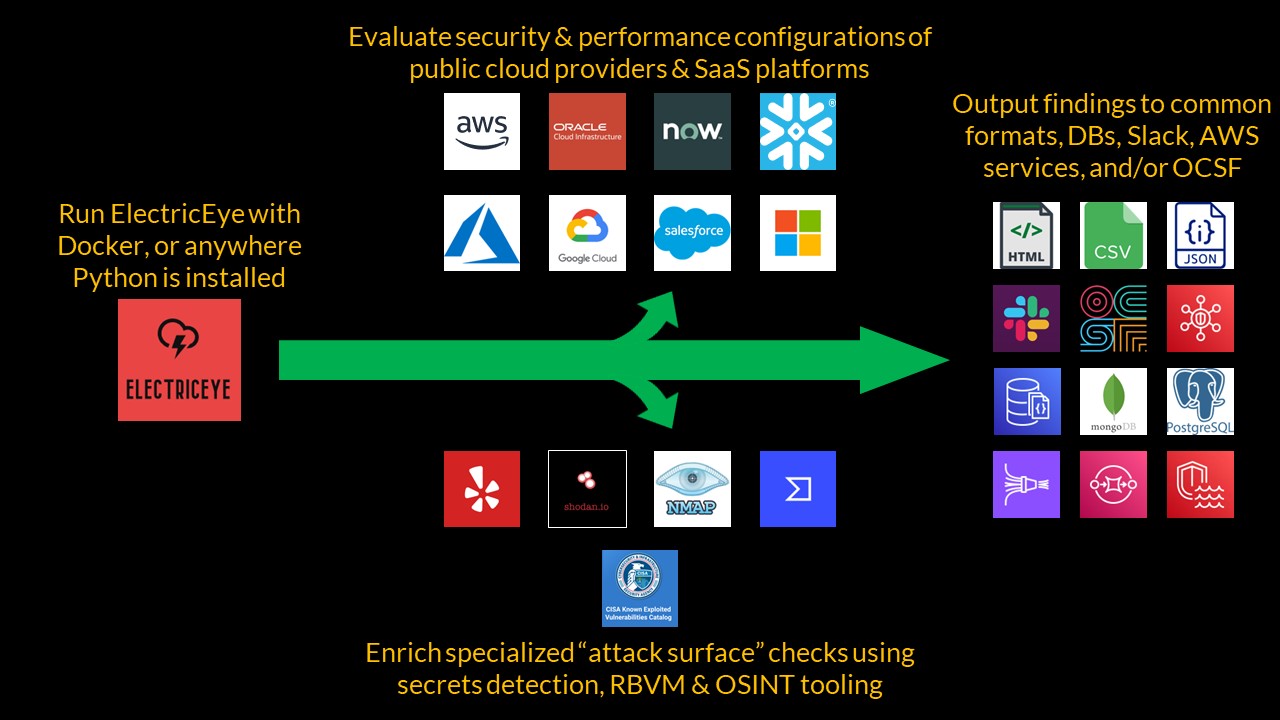
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…

Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…

Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…

A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.