
depx
 projectdiscovery/depx
Malicious package & supply-chain intelligence
devsecopssecret-detectionsupply-chain-security+2
projectdiscovery/depxMalicious package & supply-chain intelligence
 ghostpack/deeppass
Hunting for passwords with deep learning
 boringtools/git-alerts
Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 shubhamshubhankar/dumpthegit
Scans public GitHub repositories for accidentally uploaded sensitive data like credentials, secret keys, and tokens using a personal access token.
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
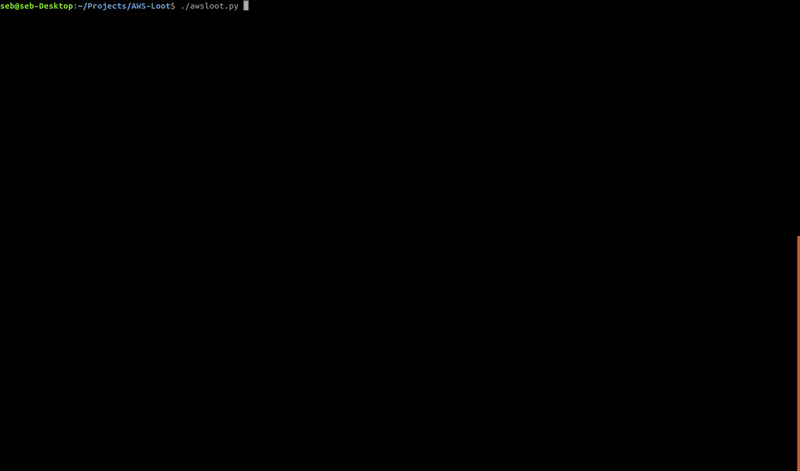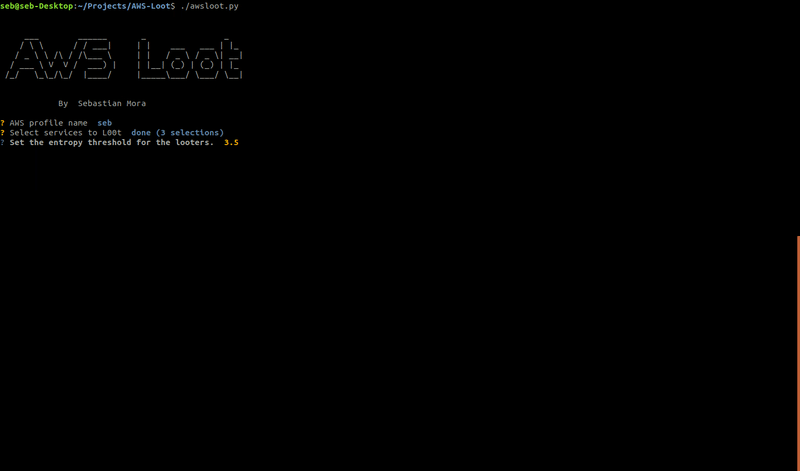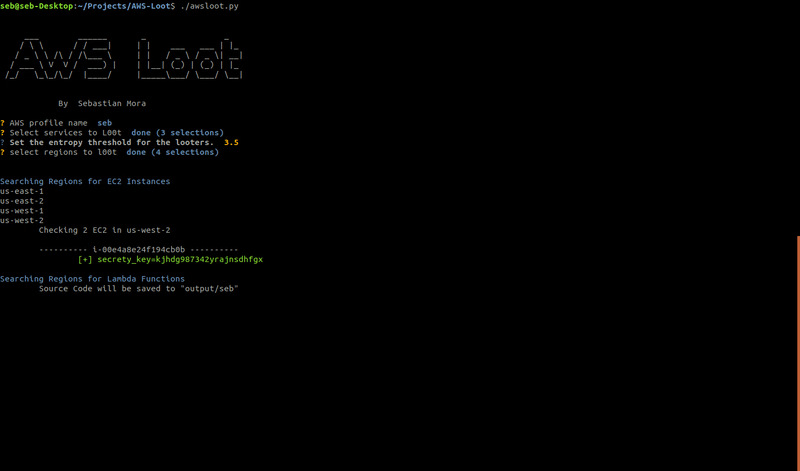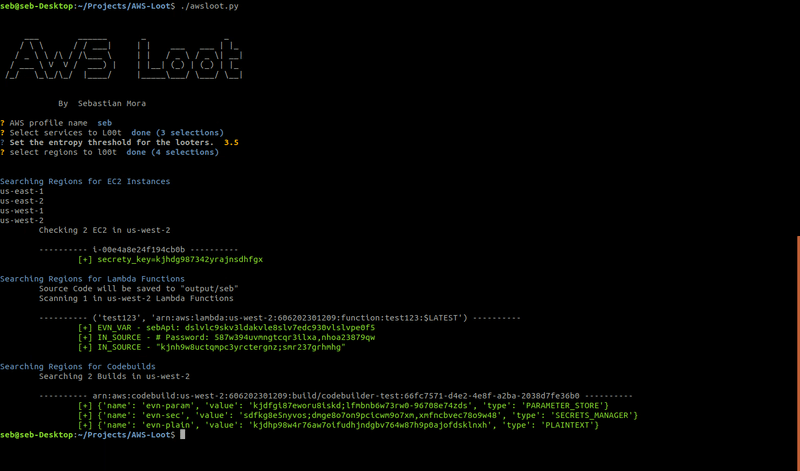 sebastian-mora/aws-loot
Enumerates AWS environments for secrets by scanning EC2 userdata, Lambda environment variables and source code, and CodeBuild instances for…
 liodeus/swaggerhole
A python3 script searching for secret on swaggerhub
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.
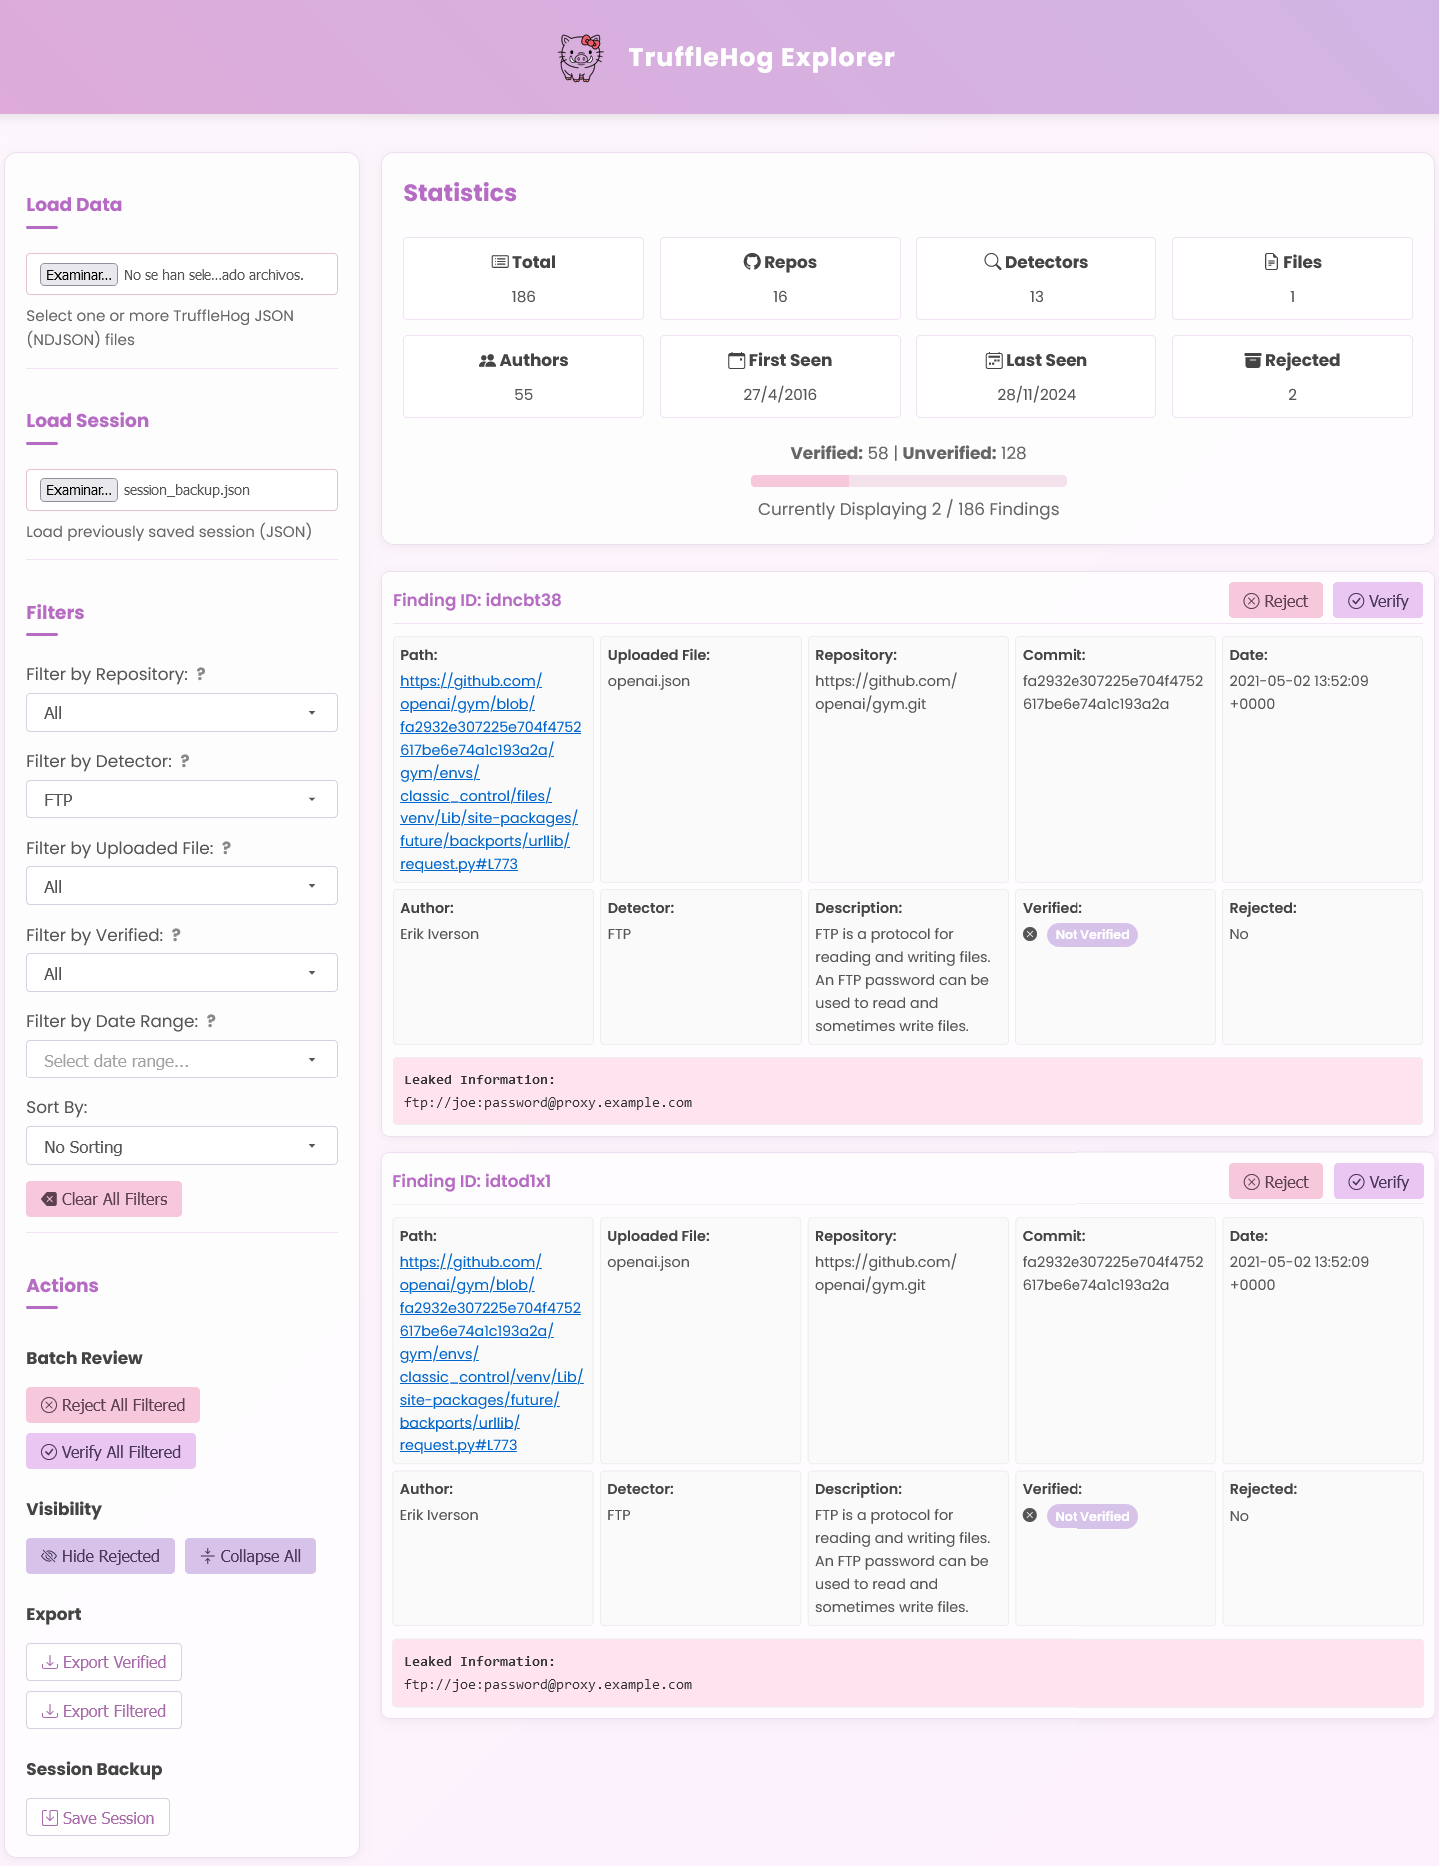 gonzosint/trufflehog-explorer
Web-based dashboard to visualize, filter, and analyze secrets discovered by TruffleHog, with batch verification, export, and session management for…
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation