
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 dracondev/dracon-utilities
Invisible infrastructure for Dracon developer workspaces: git sync, system guard, and warden encryption utilities.
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
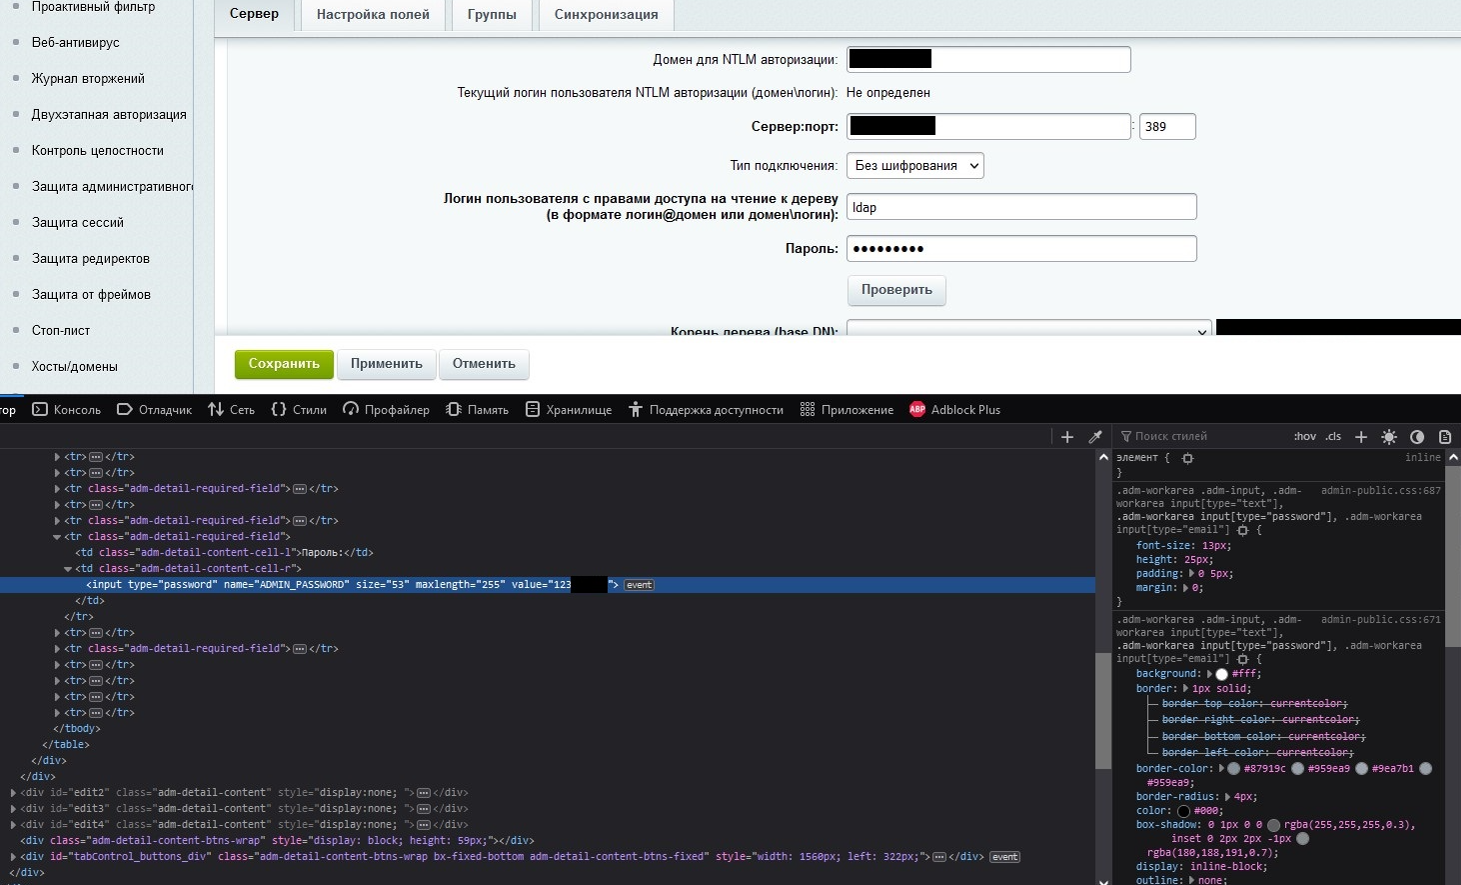 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.
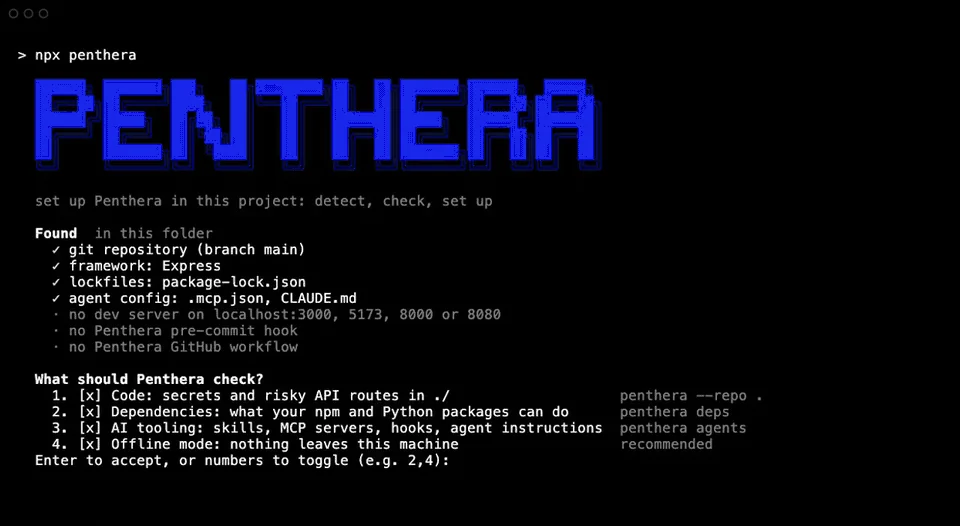 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 dani-garcia/vaultwarden
Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs