
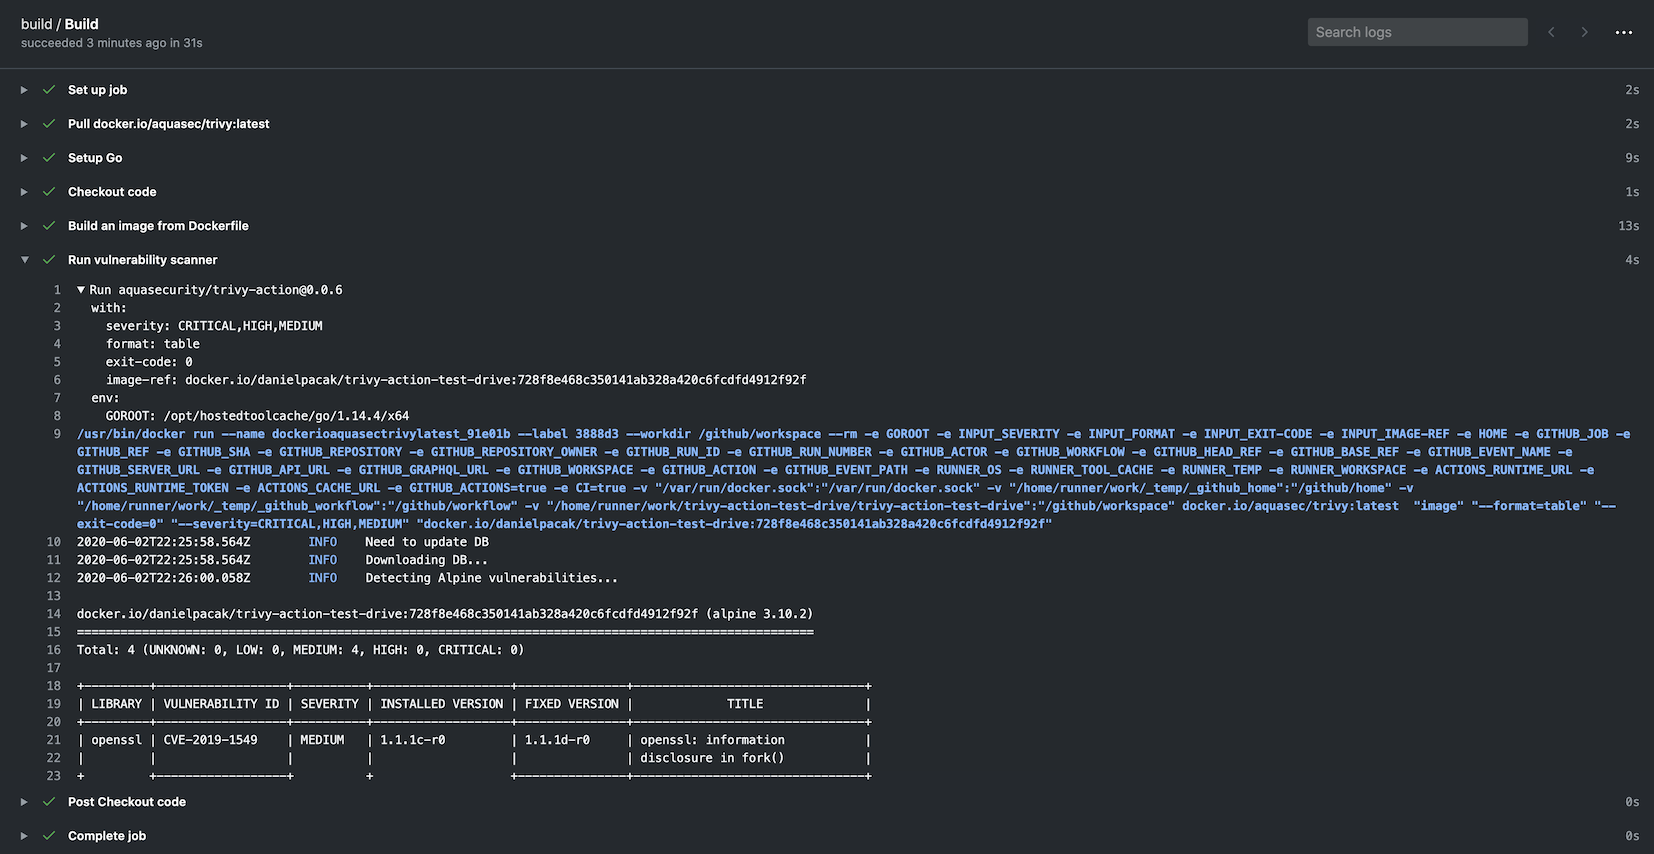
trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.4k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
 sepehrdaddev/zap-scripts
Zed Attack Proxy Scripts for finding CVEs and Secrets.
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
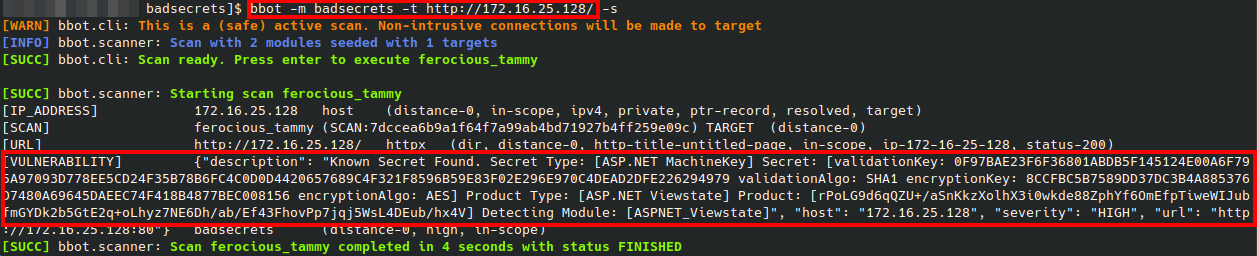 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
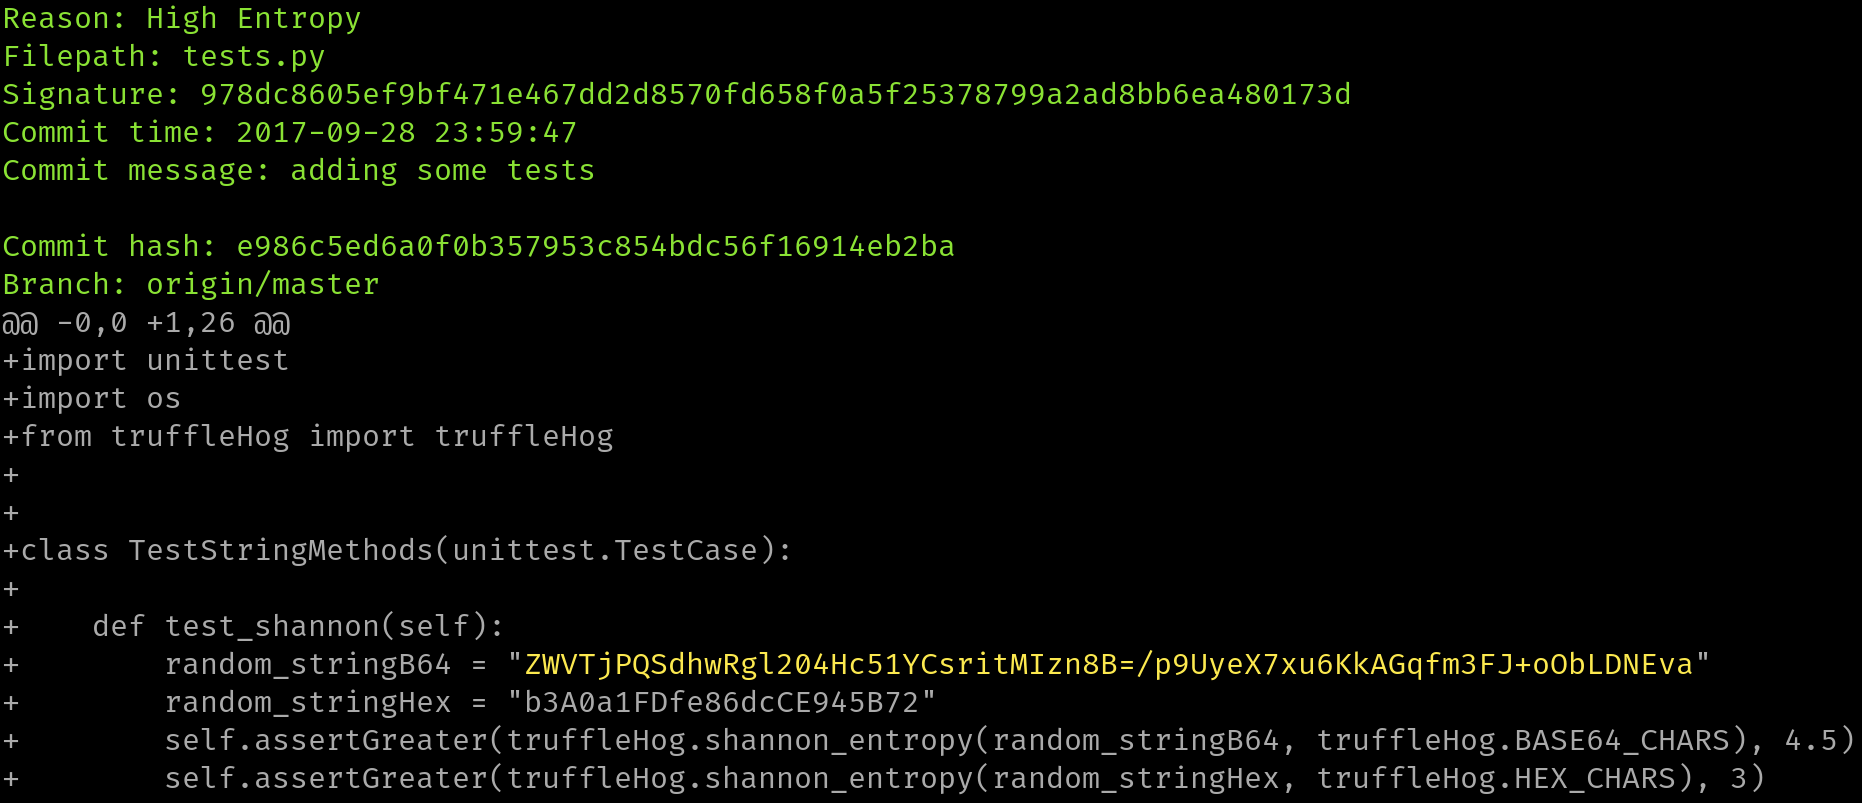 godaddy/tartufo
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
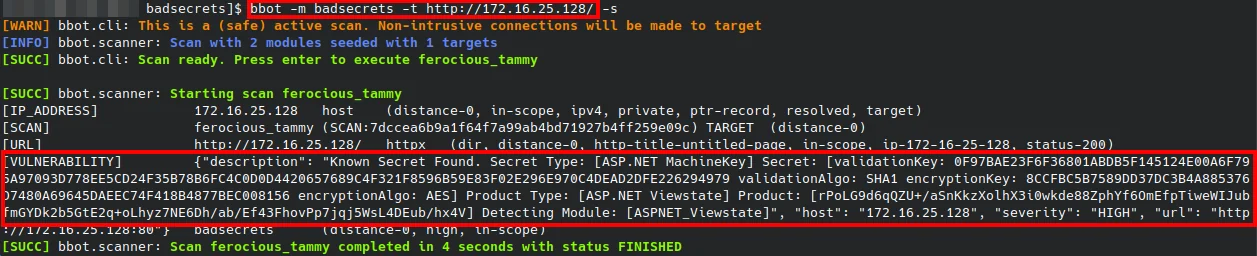 irsdl/crapsecrets
A library for detecting known secrets across many web frameworks
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 ustayready/mavd
Mobile Application Vulnerability Detection