
 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 davidcarliez/cover
Keep private data, internal infrastructure and secrets out of cloud coding agents without breaking your workflow.
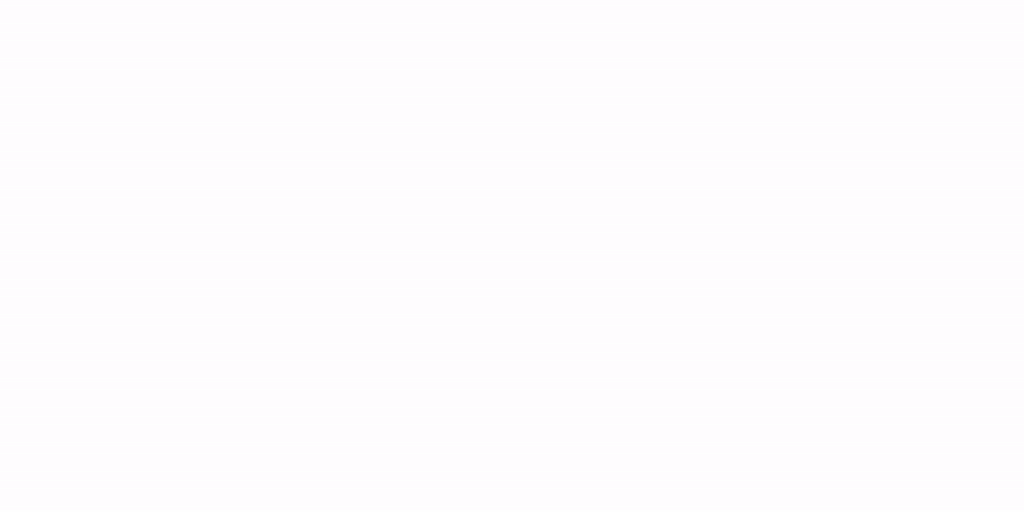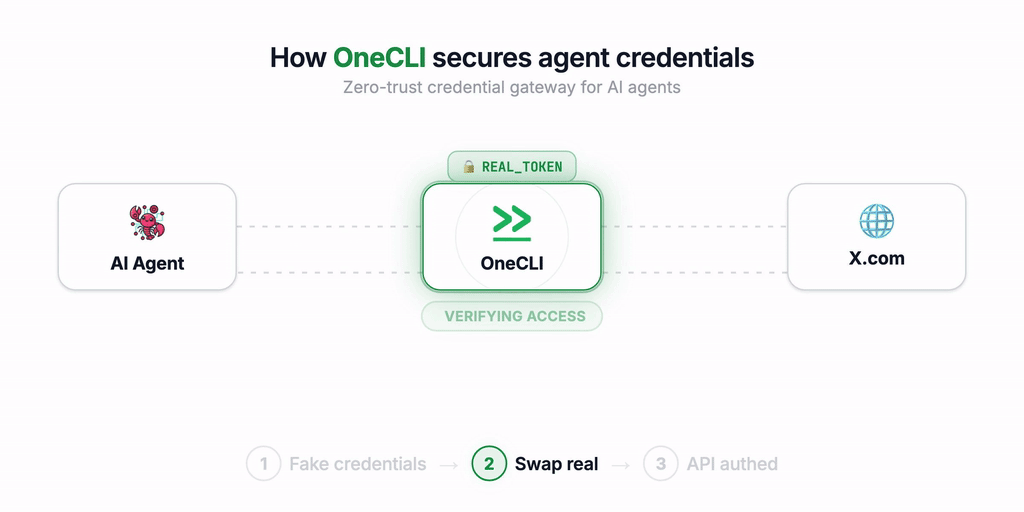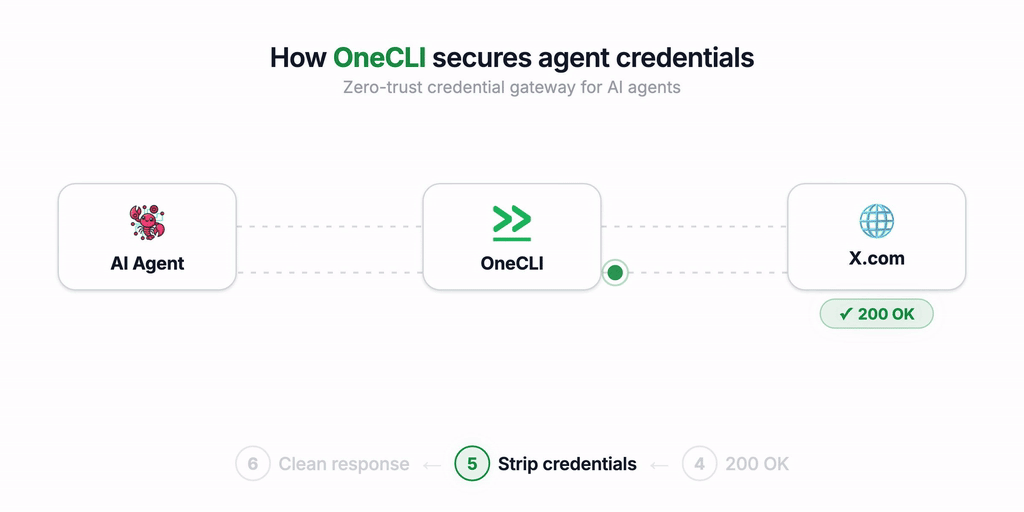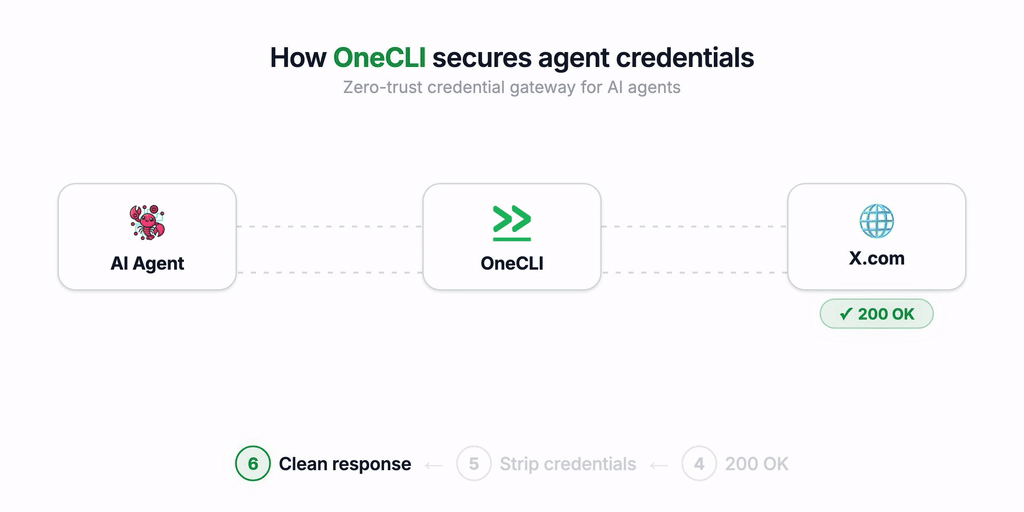 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 sushank05/mcp-doorman
A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
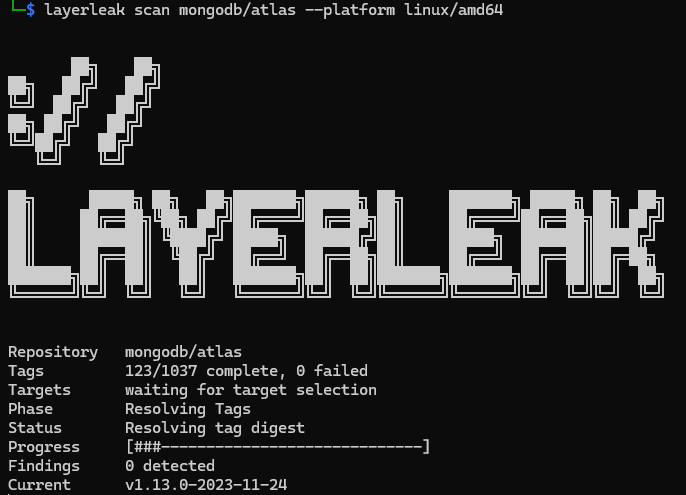 brumbelow/layerleak
layerleak the Docker Hub Secret Scanner