

ShipProof
 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
cloud-securitycode-analysisconfiguration-auditing+6
divyanshukumar0014/shipproofSOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…

 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 cybertix-pvt-ltd/one-liner-collections
This Repositories contains list of One Liners with Descriptions and Installation requirements
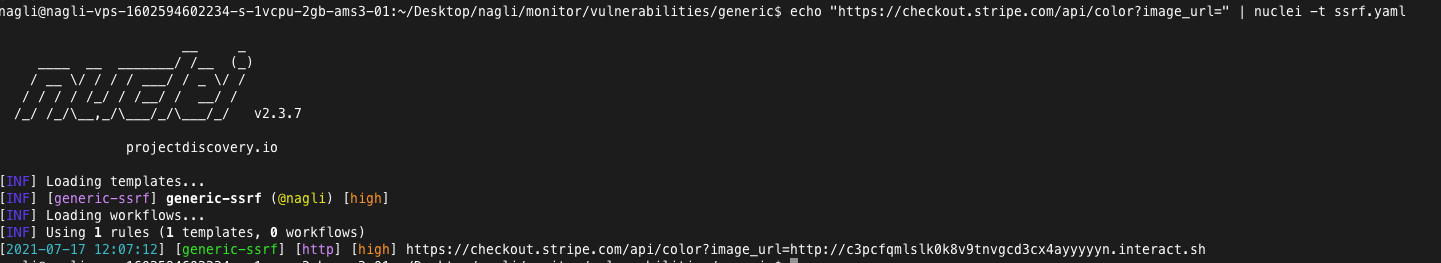 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
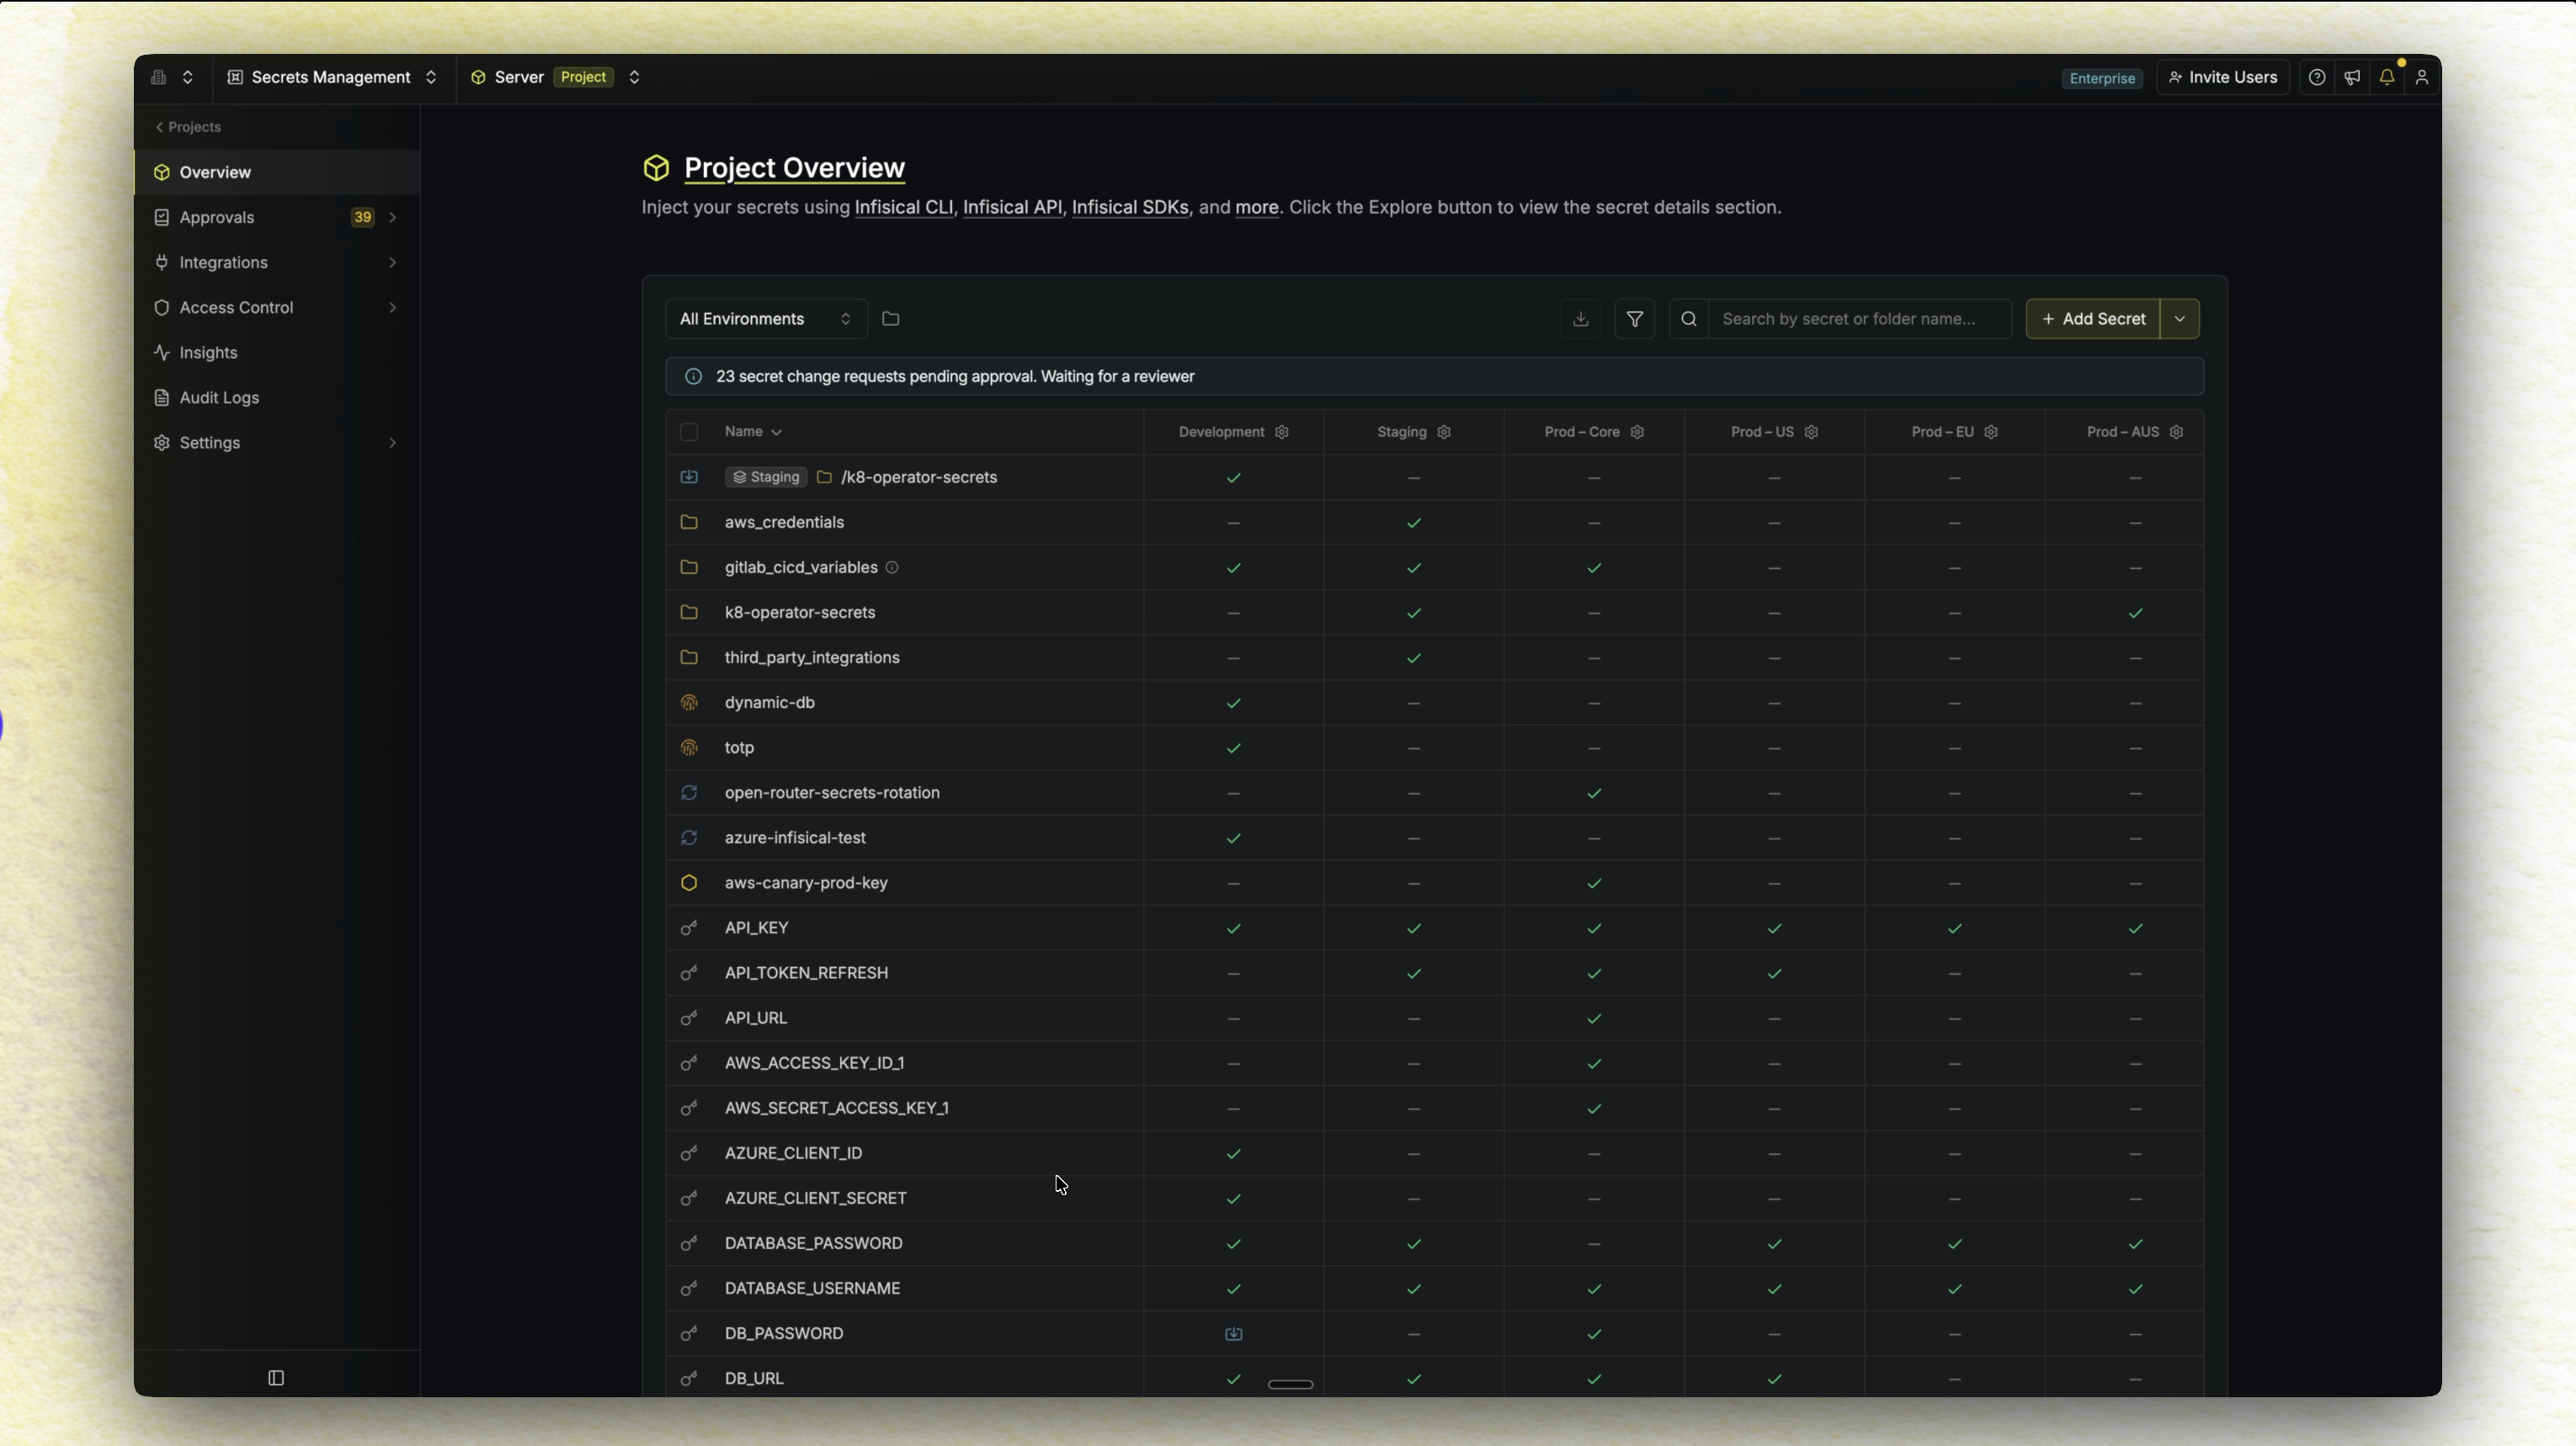 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
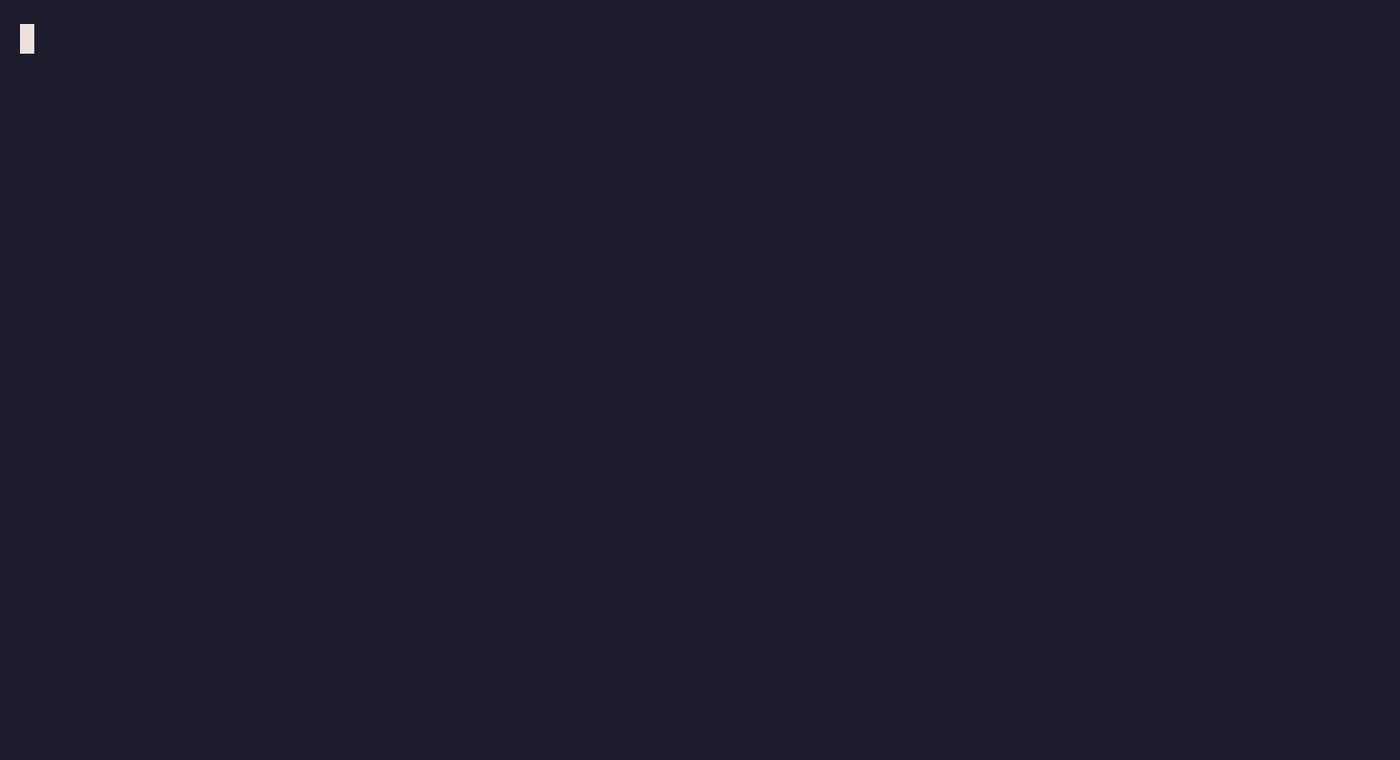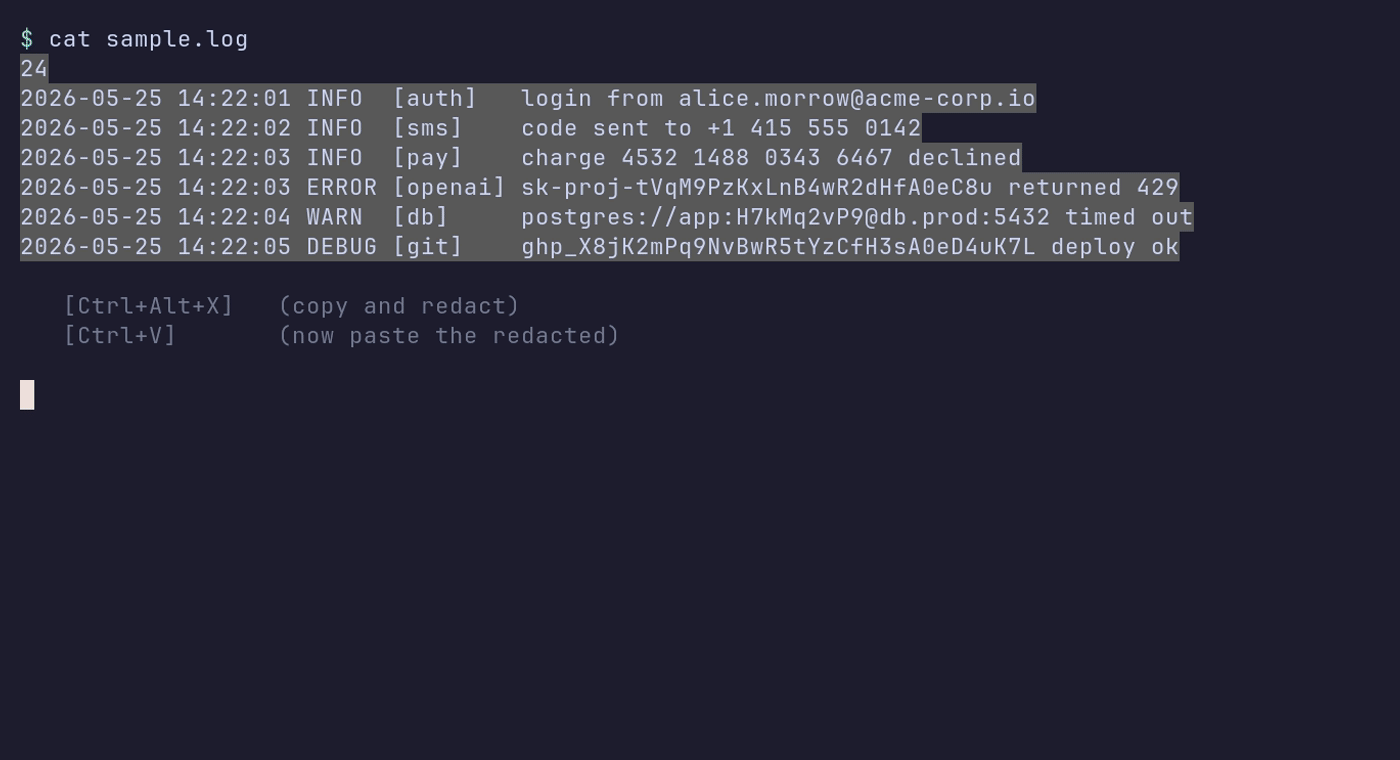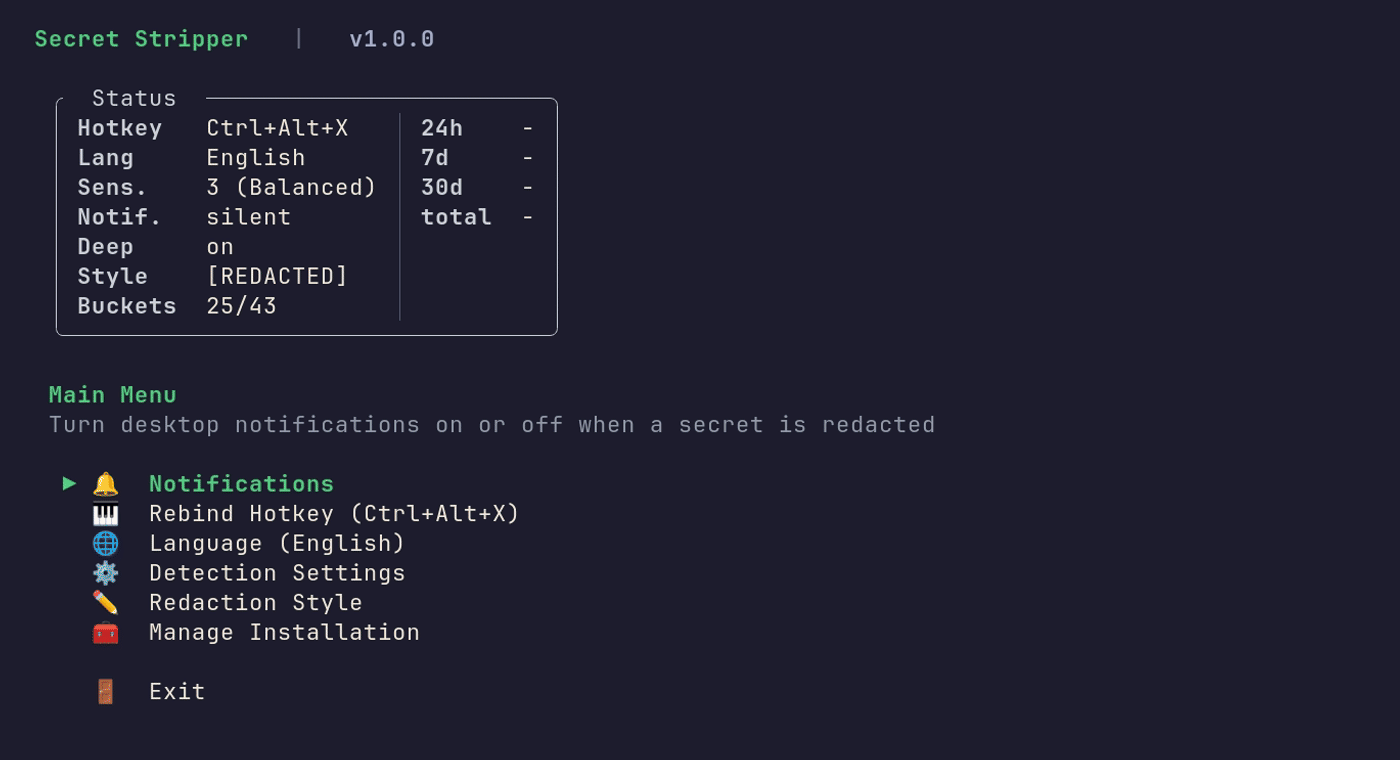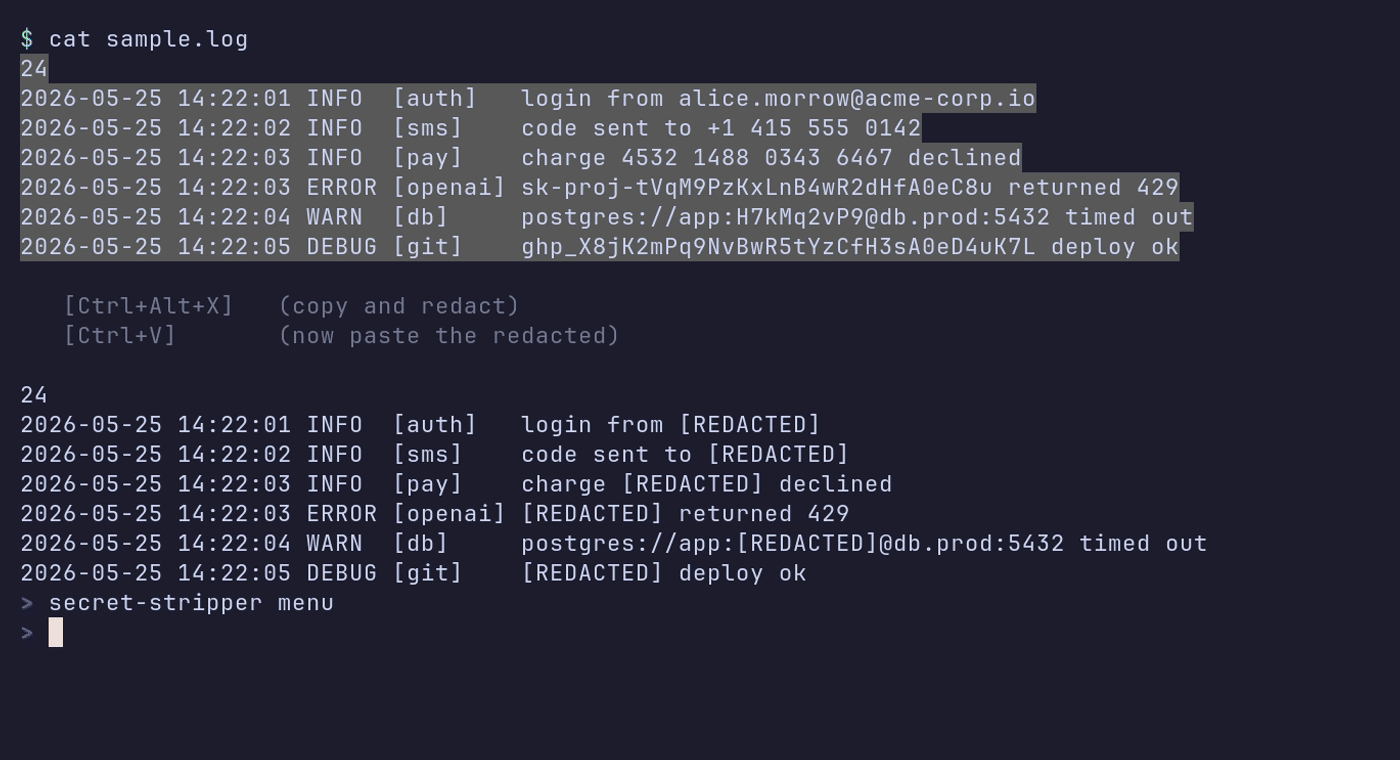 kalix127/secret-stripper
Paste a redacted copy of your clipboard with one hotkey. Hides API keys, tokens, passwords and PII (900+ patterns) before they reach AI chats,…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 agentguard-ai/tealtiger
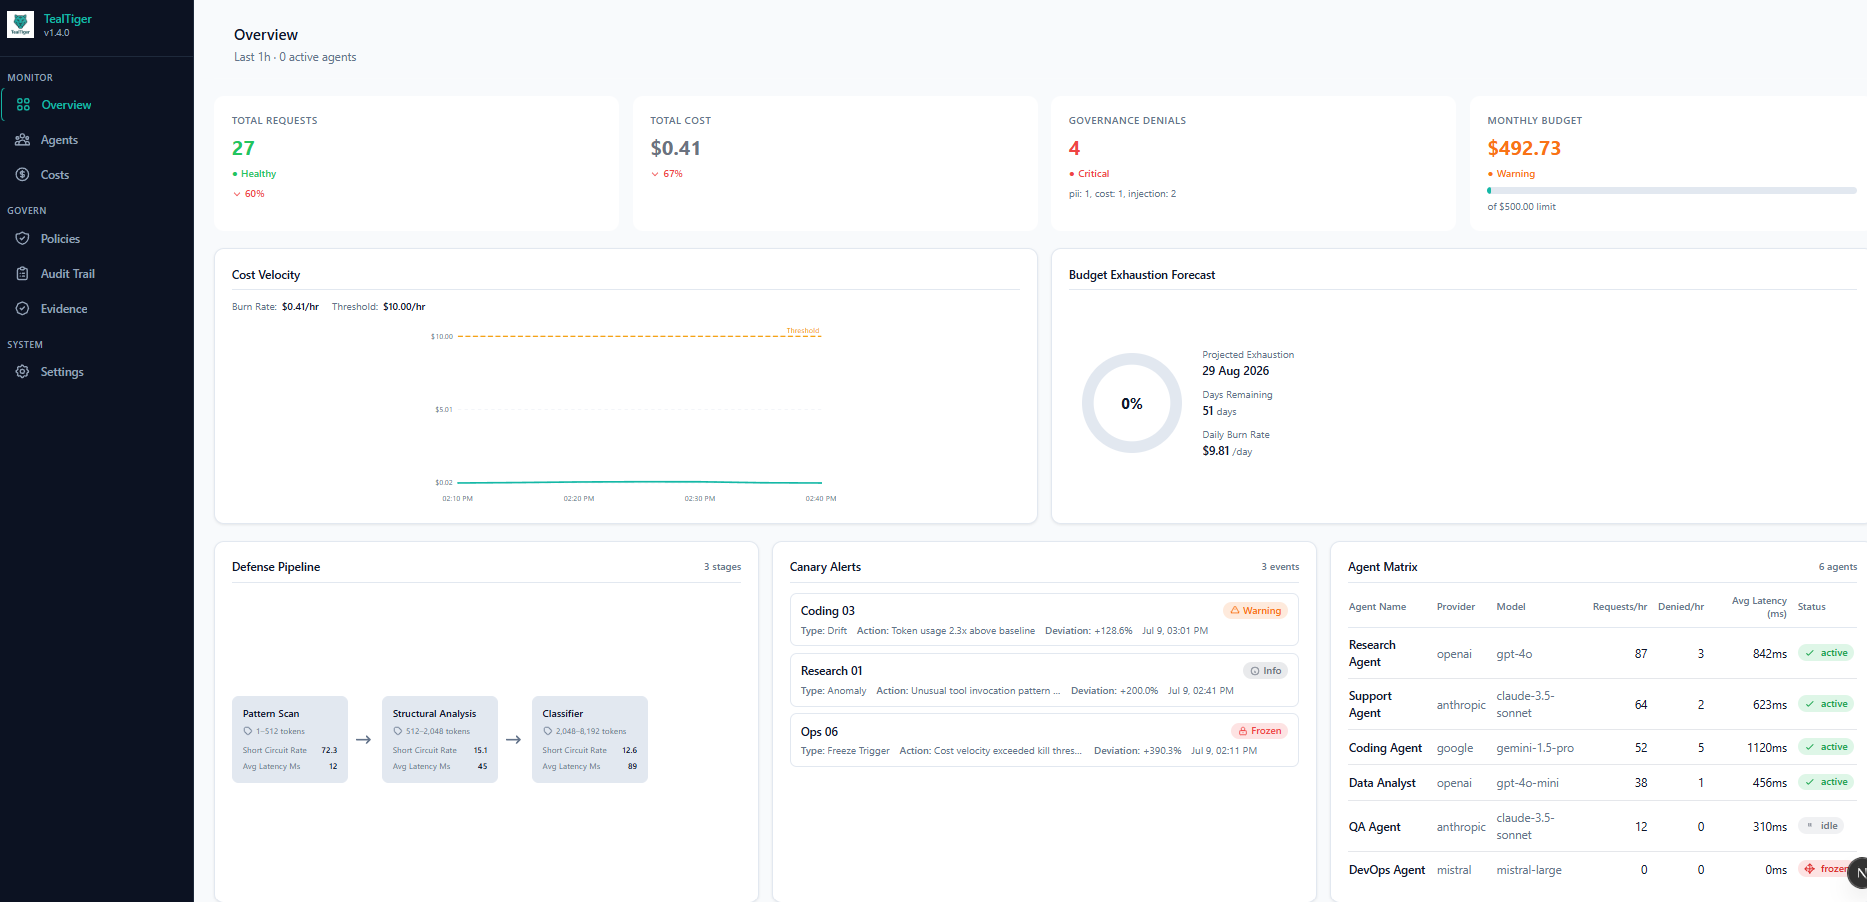
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 talkaboutcybersecurity/gitmonitor
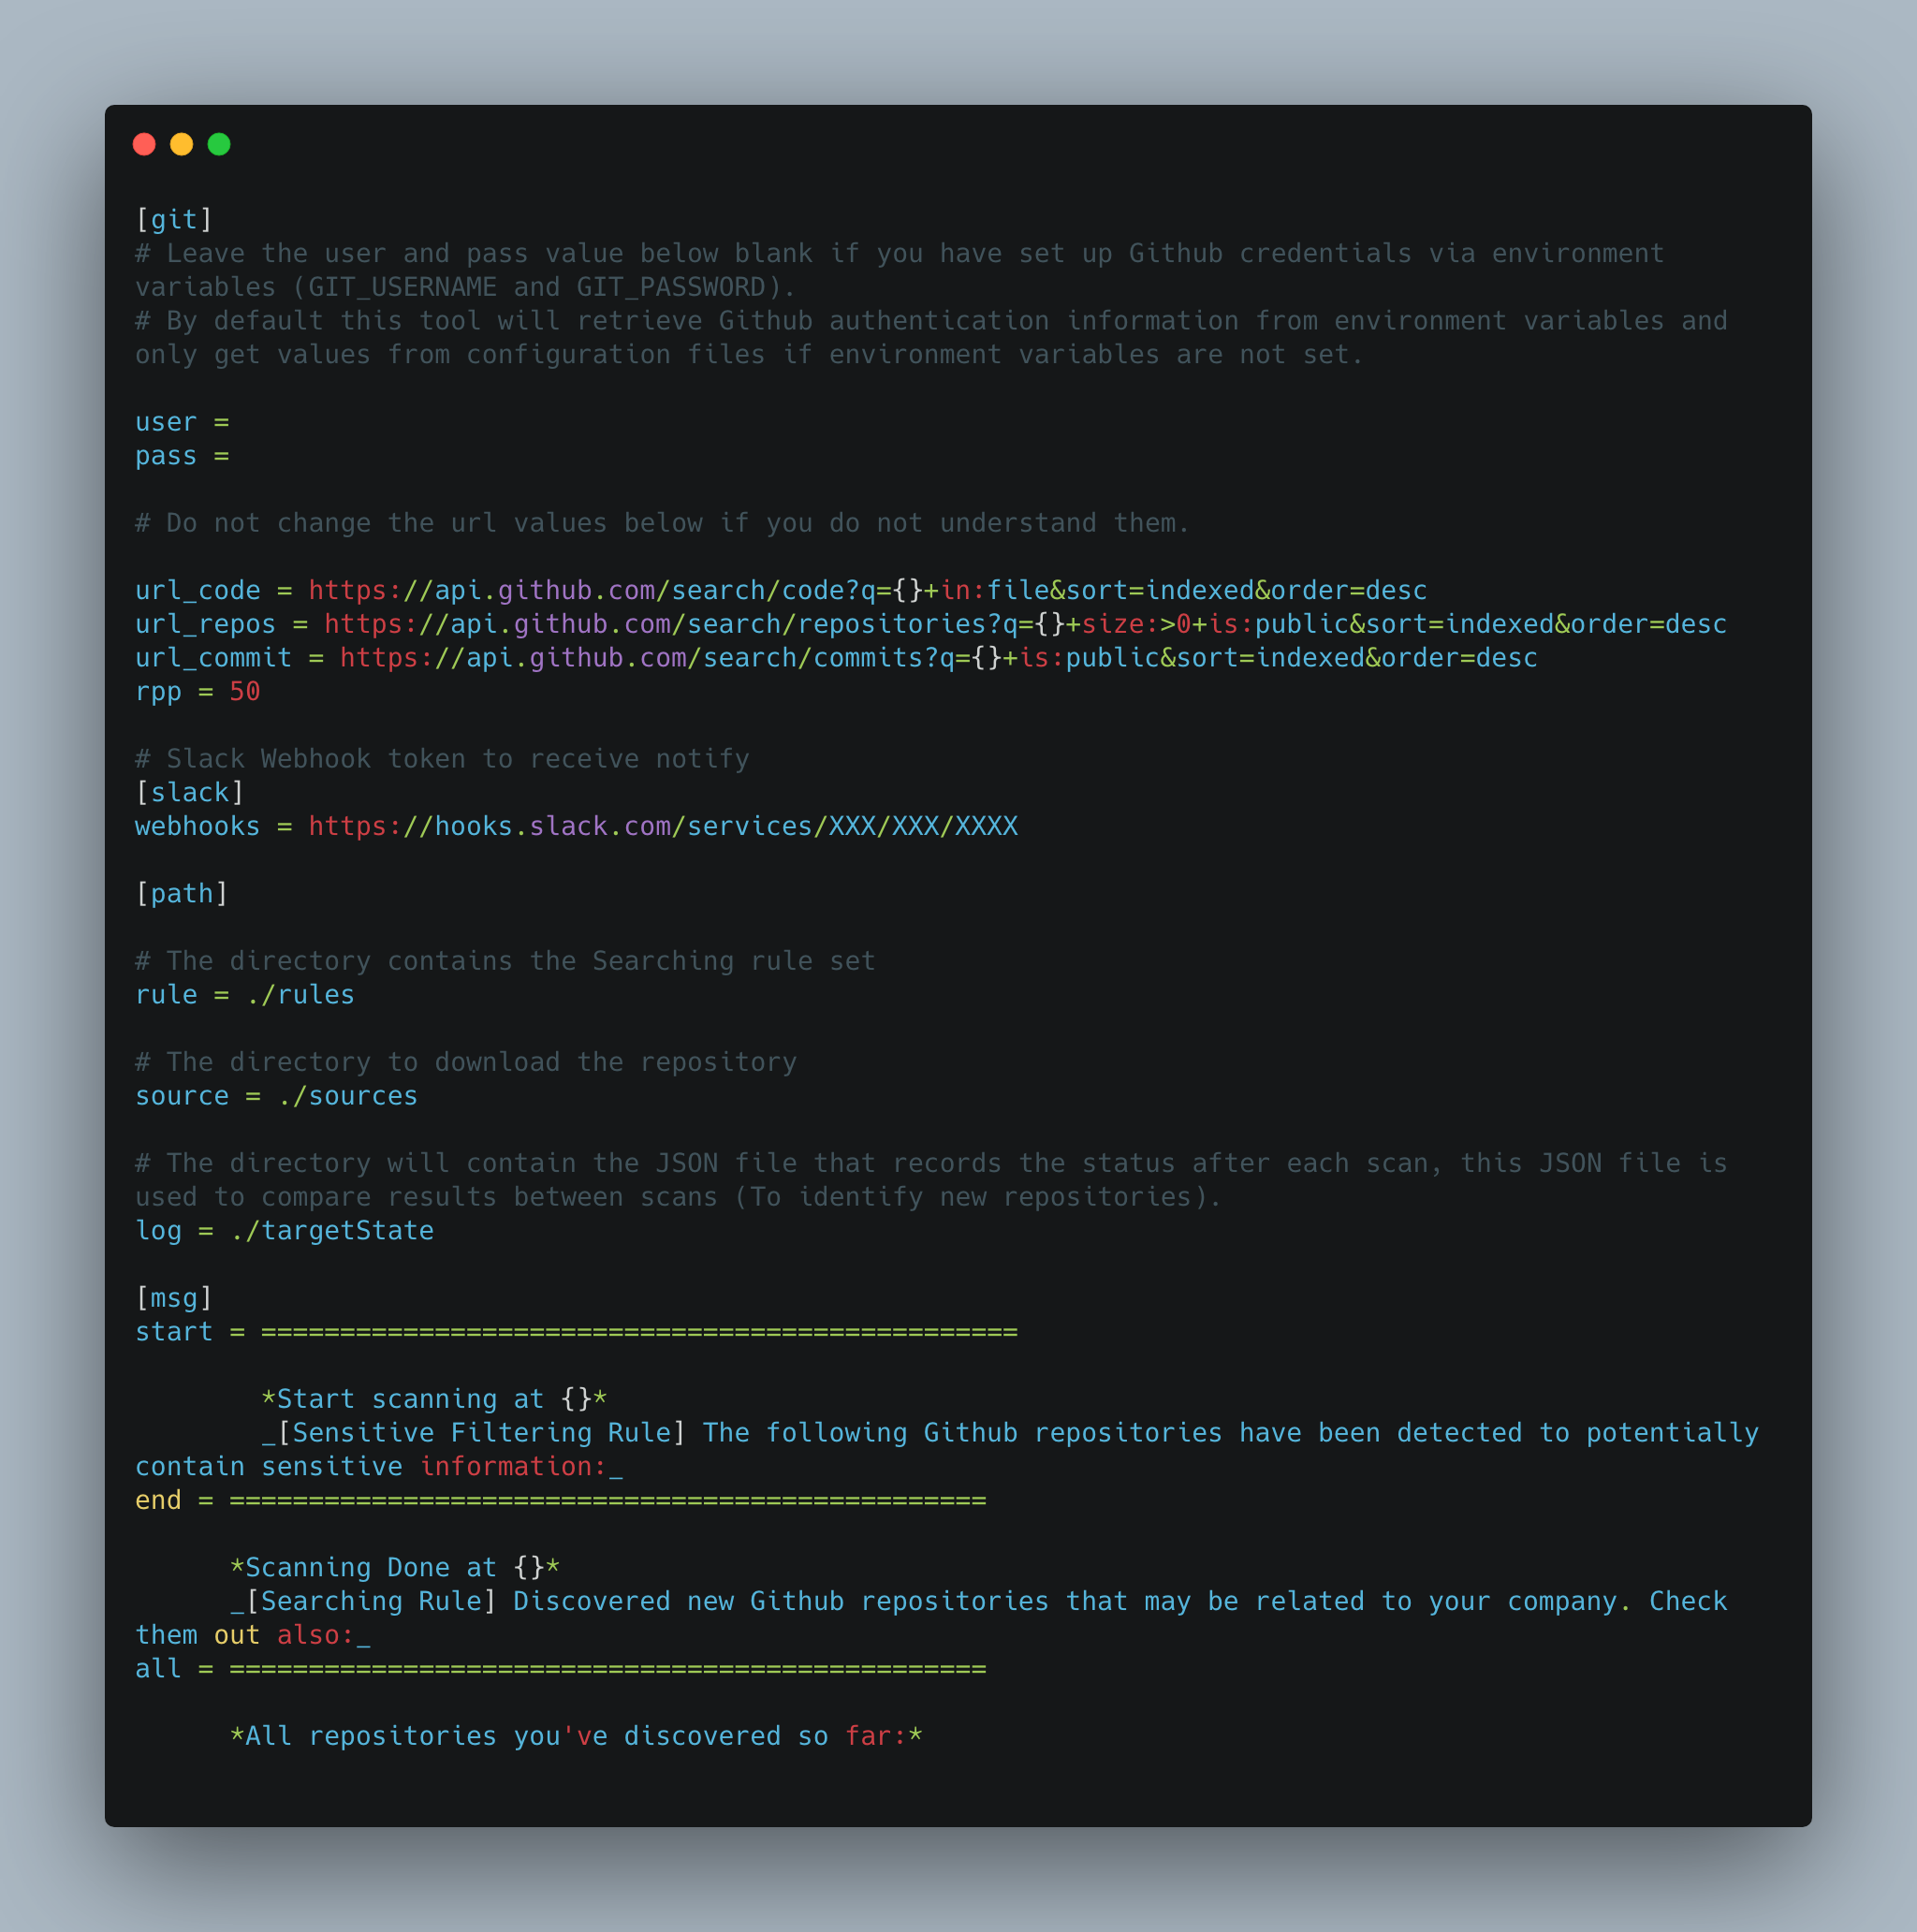
One way to continuously monitor sensitive information that could be exposed on Github
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.