Llama-Stack-0.4.0rc3-local-CVE-2026-25211

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment

Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…

Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

Automated Python scanner to detect hardcoded secrets (Private Keys, API Tokens) in client-side JavaScript files.

Check rclone config files for insecure passwords

Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.

Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…

GitHub Action that scans ML model files for malicious code and security vulnerabilities

Transparent file encryption in git

Hunt for AI coding artifacts containing secrets.

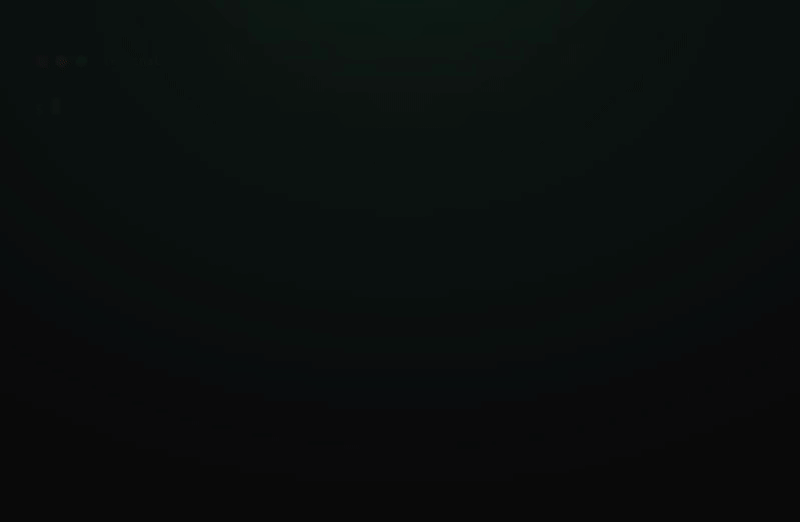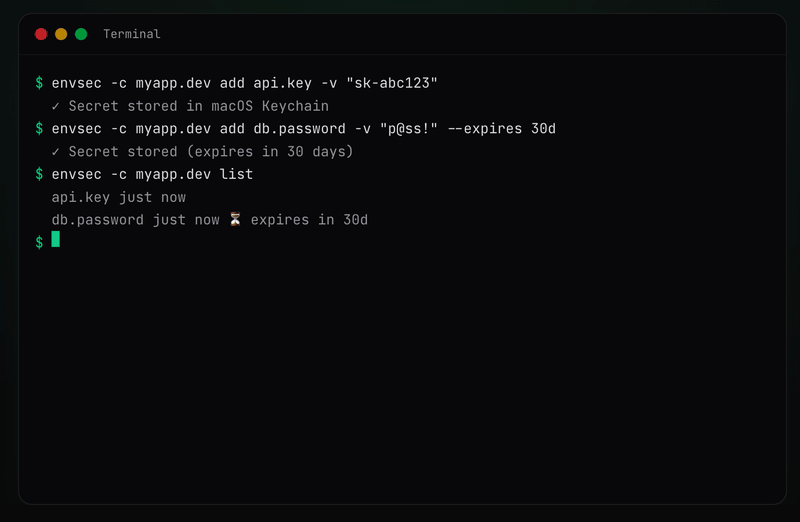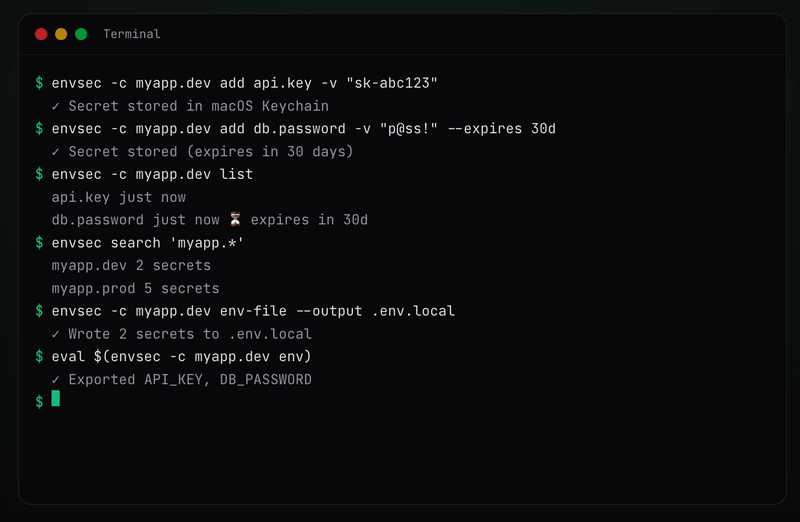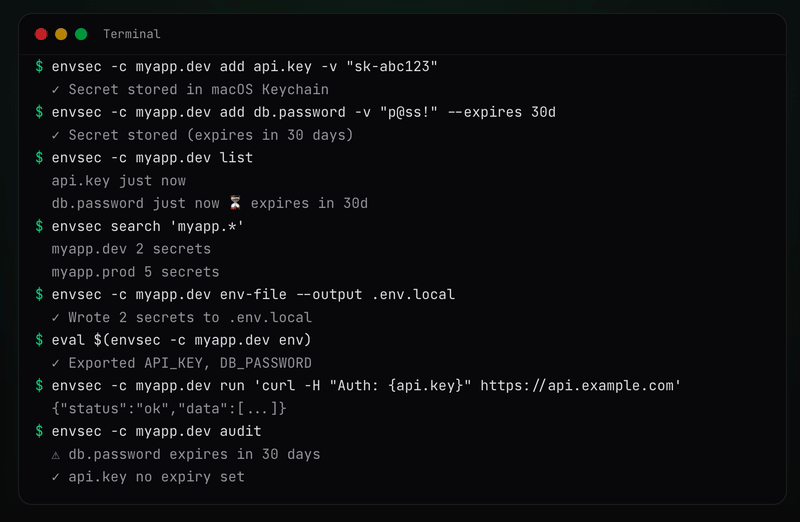
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)

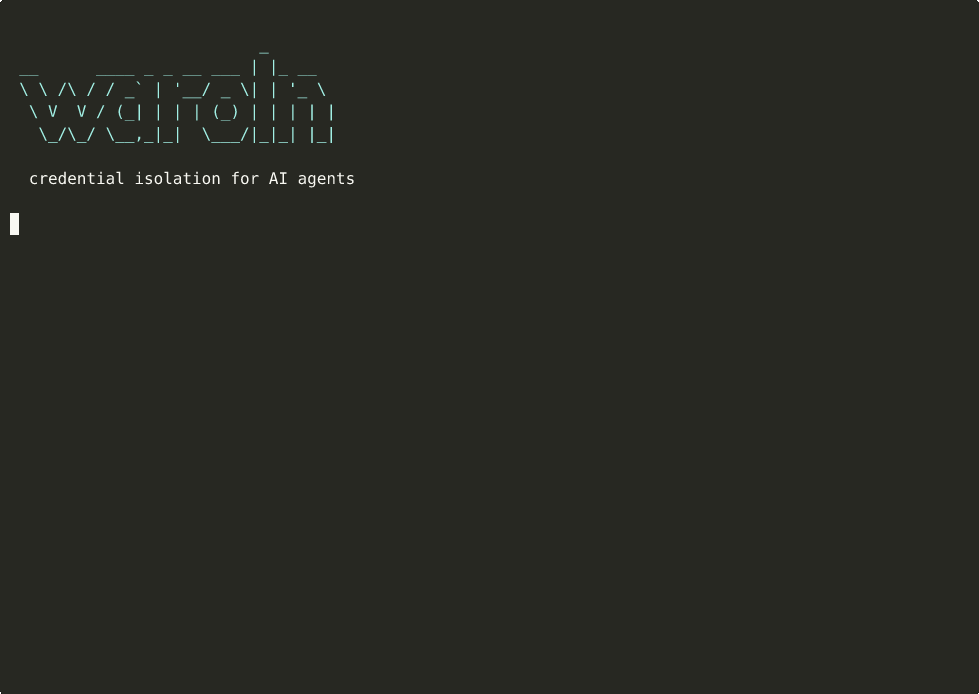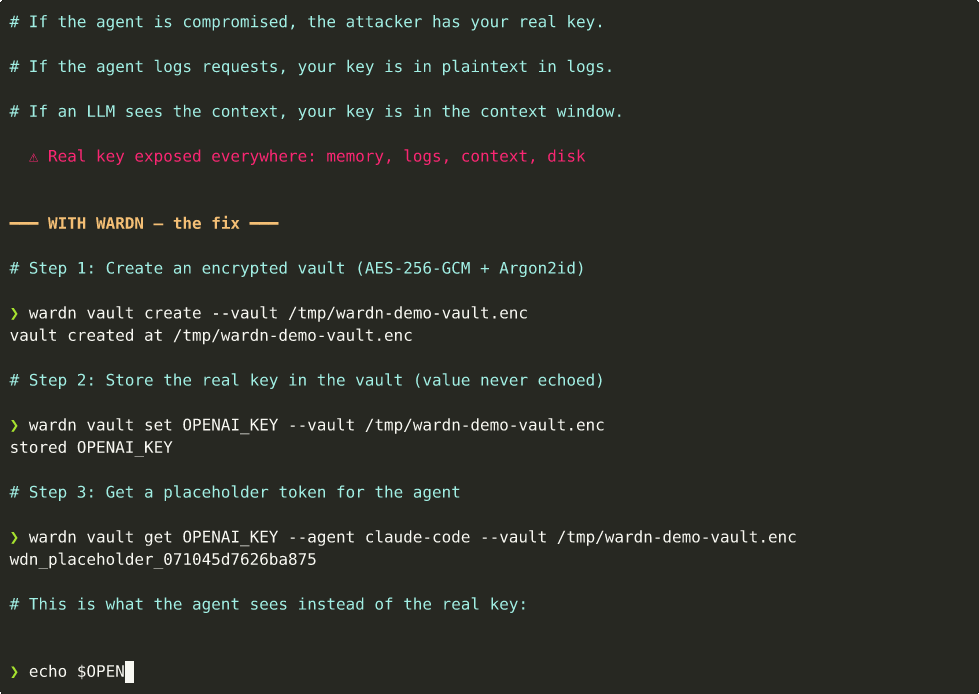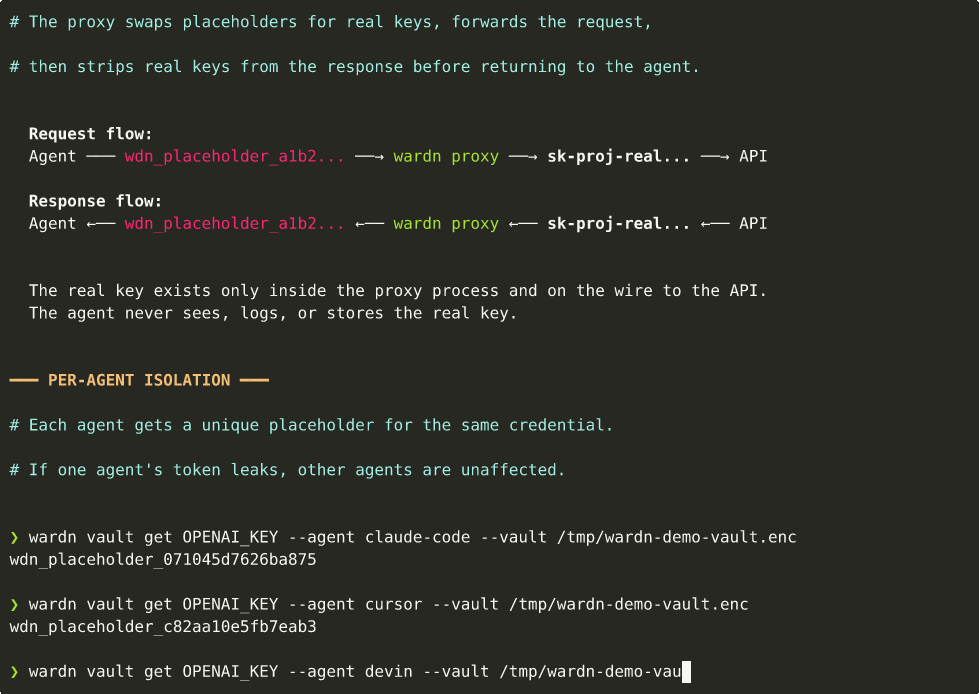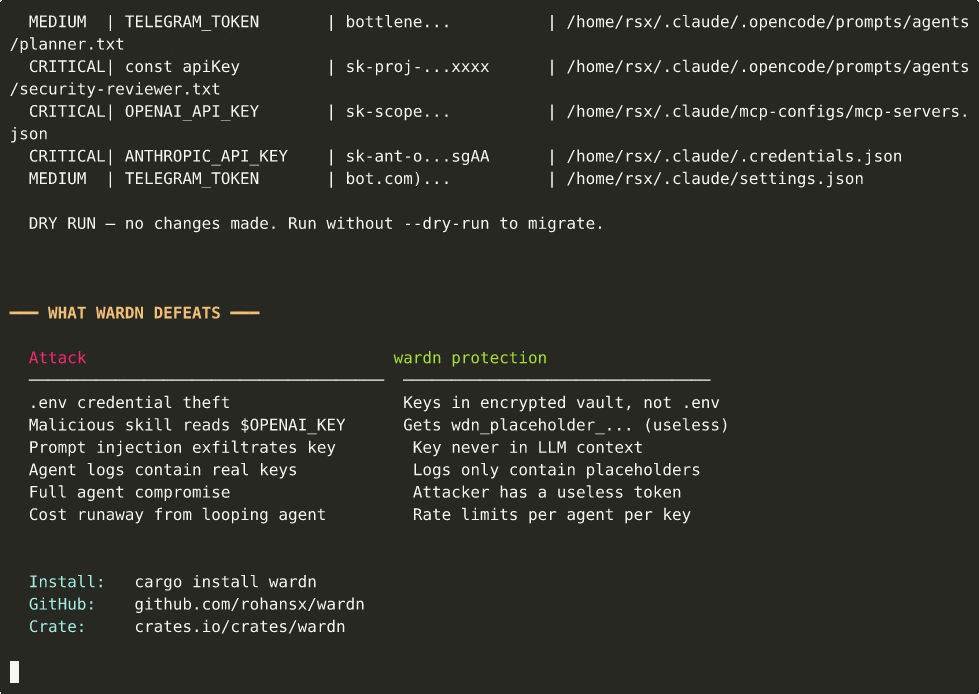
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

Lan Tian's NixOS Configuration

Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.

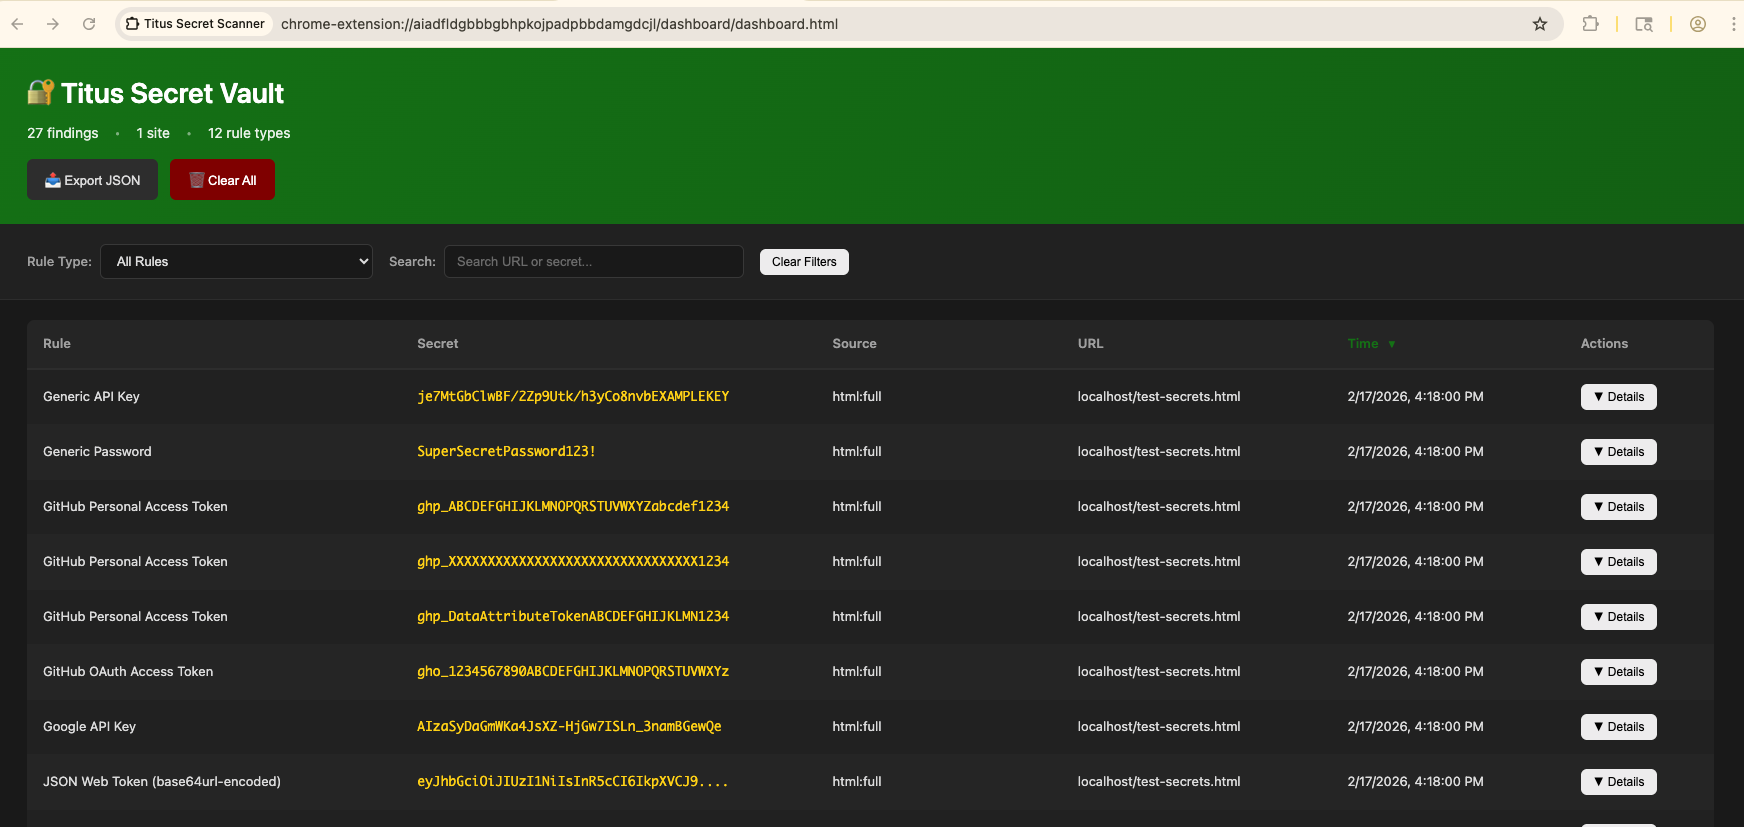
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.

A simple file-based scanner to look for potential AWS access and secret keys in files