

fad-checker
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
code-analysisconfiguration-auditingdefensive-tools+6
9pings/fad-checkerBuildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 projectdiscovery/depx
Malicious package & supply-chain intelligence
 cybergabisoft/depalert
DepAlert is an open-source security gate for your CI/CD pipeline. It analyzes SBOMs against malware intelligence data and quickly tells you whether…
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack
 actions-security-demo/compromised-packages
StepSecurity owned org for analyzing compromised packages
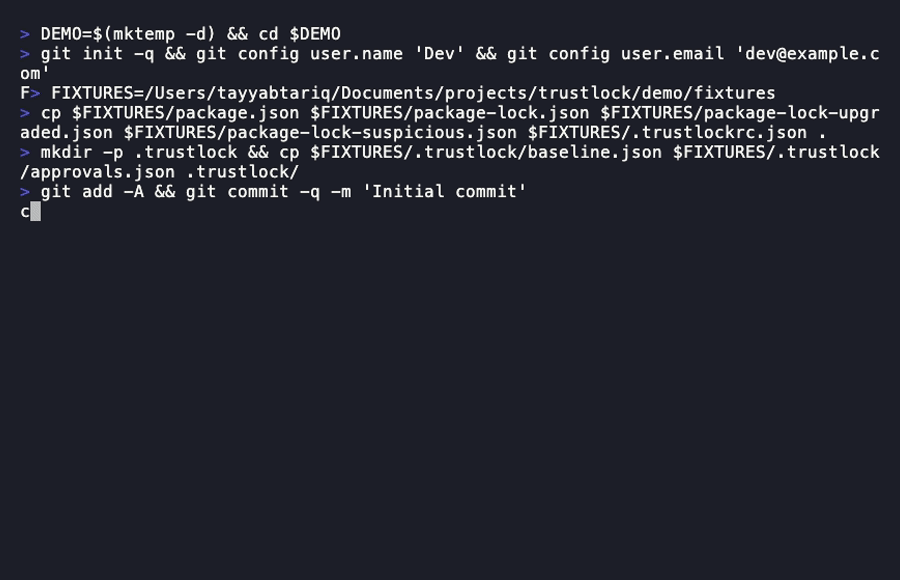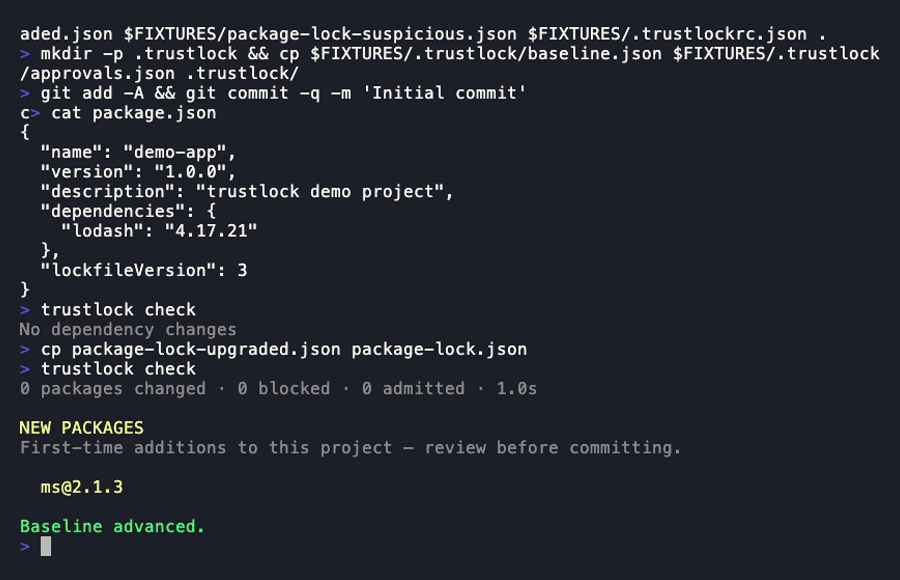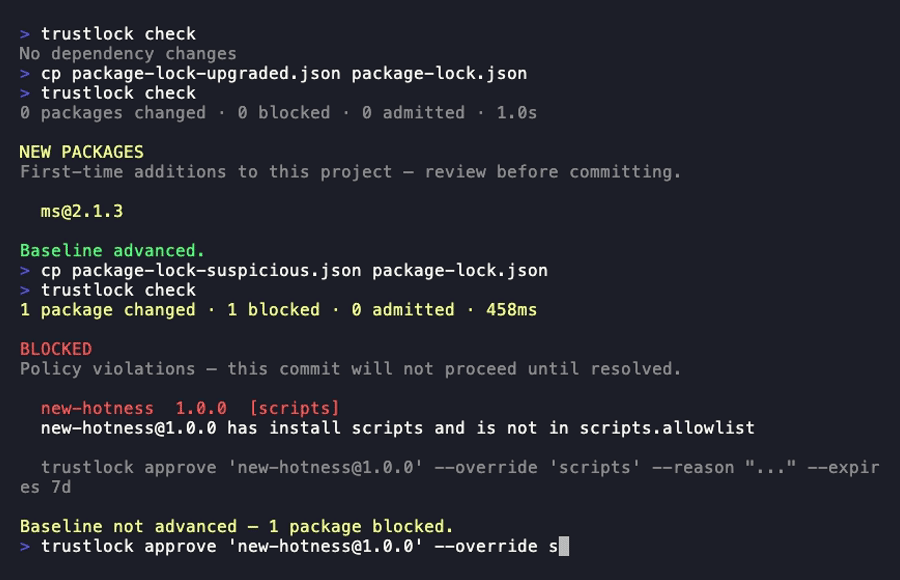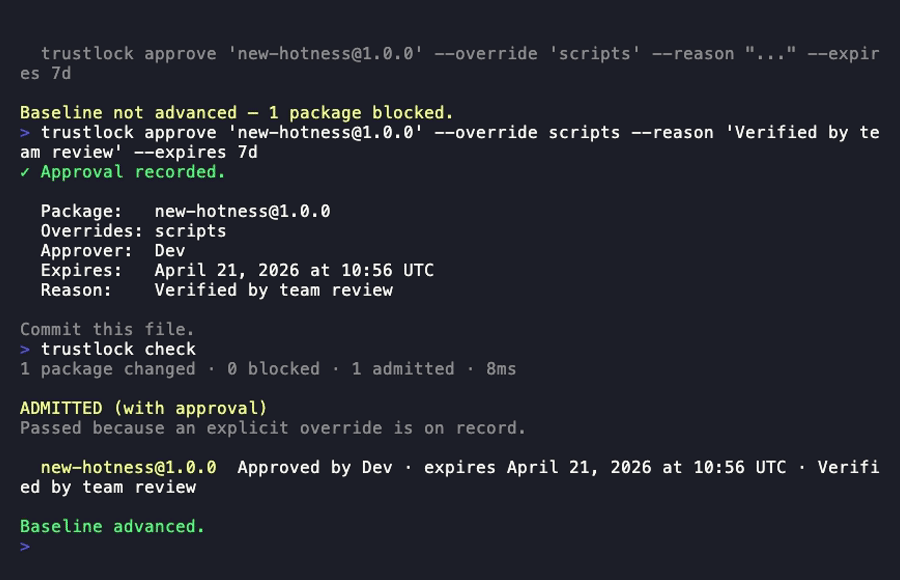 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 jayu/rev-dep
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code…
 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 jeremylong/dependencycheck
The dependency-check repository has moved: