
chart-down
 randomrobbiebf/chart-down
Extracts all the chart lists from ChartMuseum
cloud-securitycontainer-securitydevsecops+2
randomrobbiebf/chart-downExtracts all the chart lists from ChartMuseum
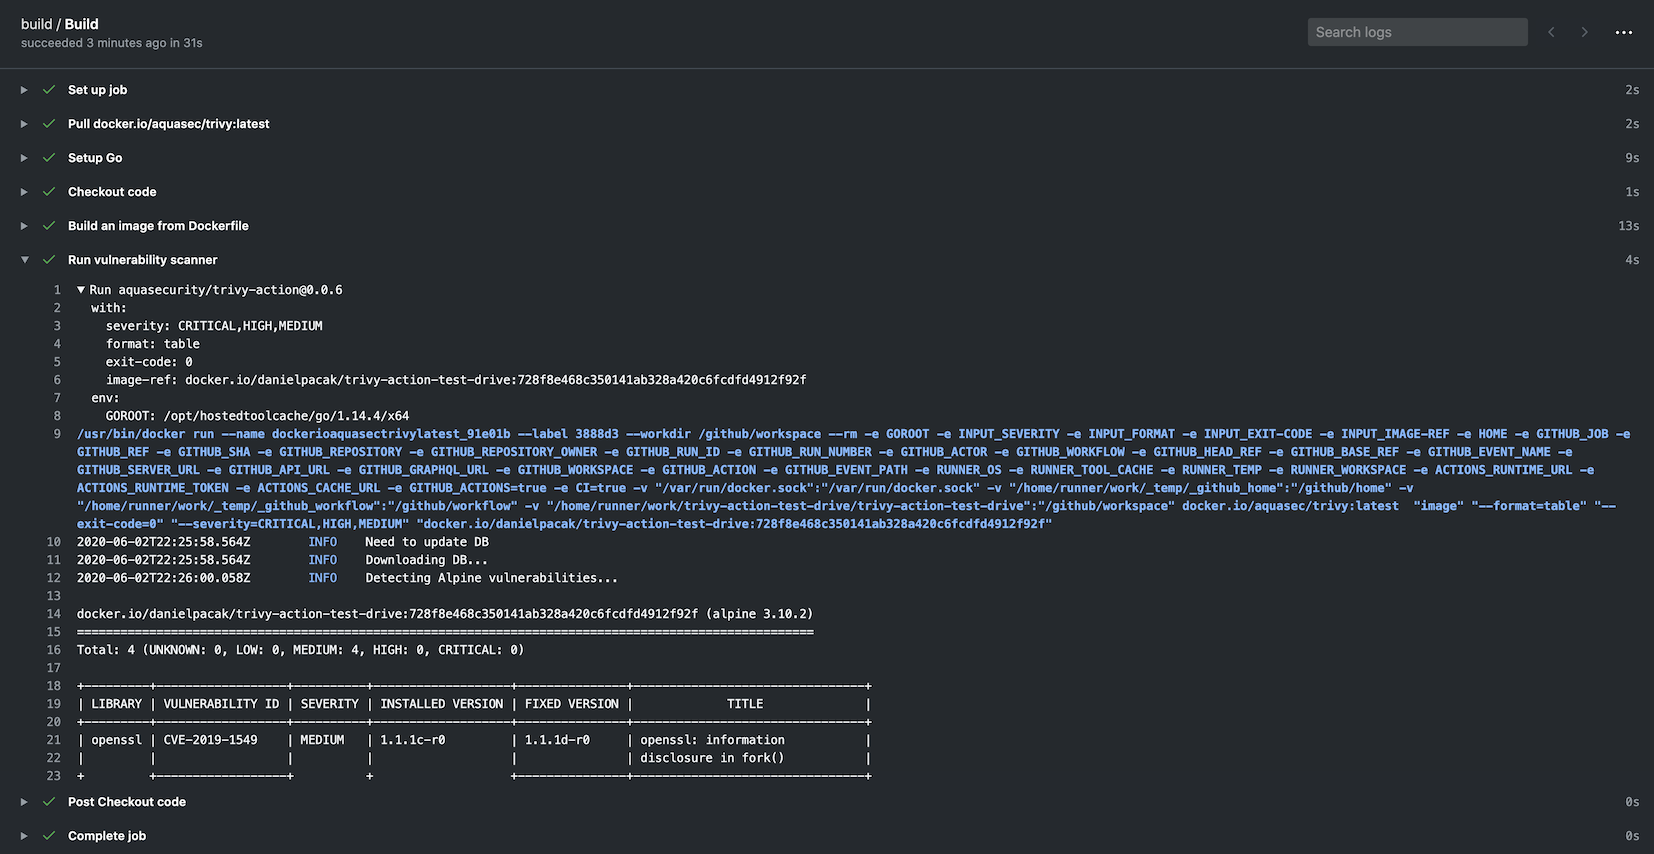 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 mhaggis/package-inferno
A Public Package Scanner for The Community
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 aquasecurity/trivy-repo
deb/rpm repository for Trivy
 404tk/cve-2022-46463
harbor unauthorized detection
 brumbelow/layerleak
layerleak the Docker Hub Secret Scanner
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
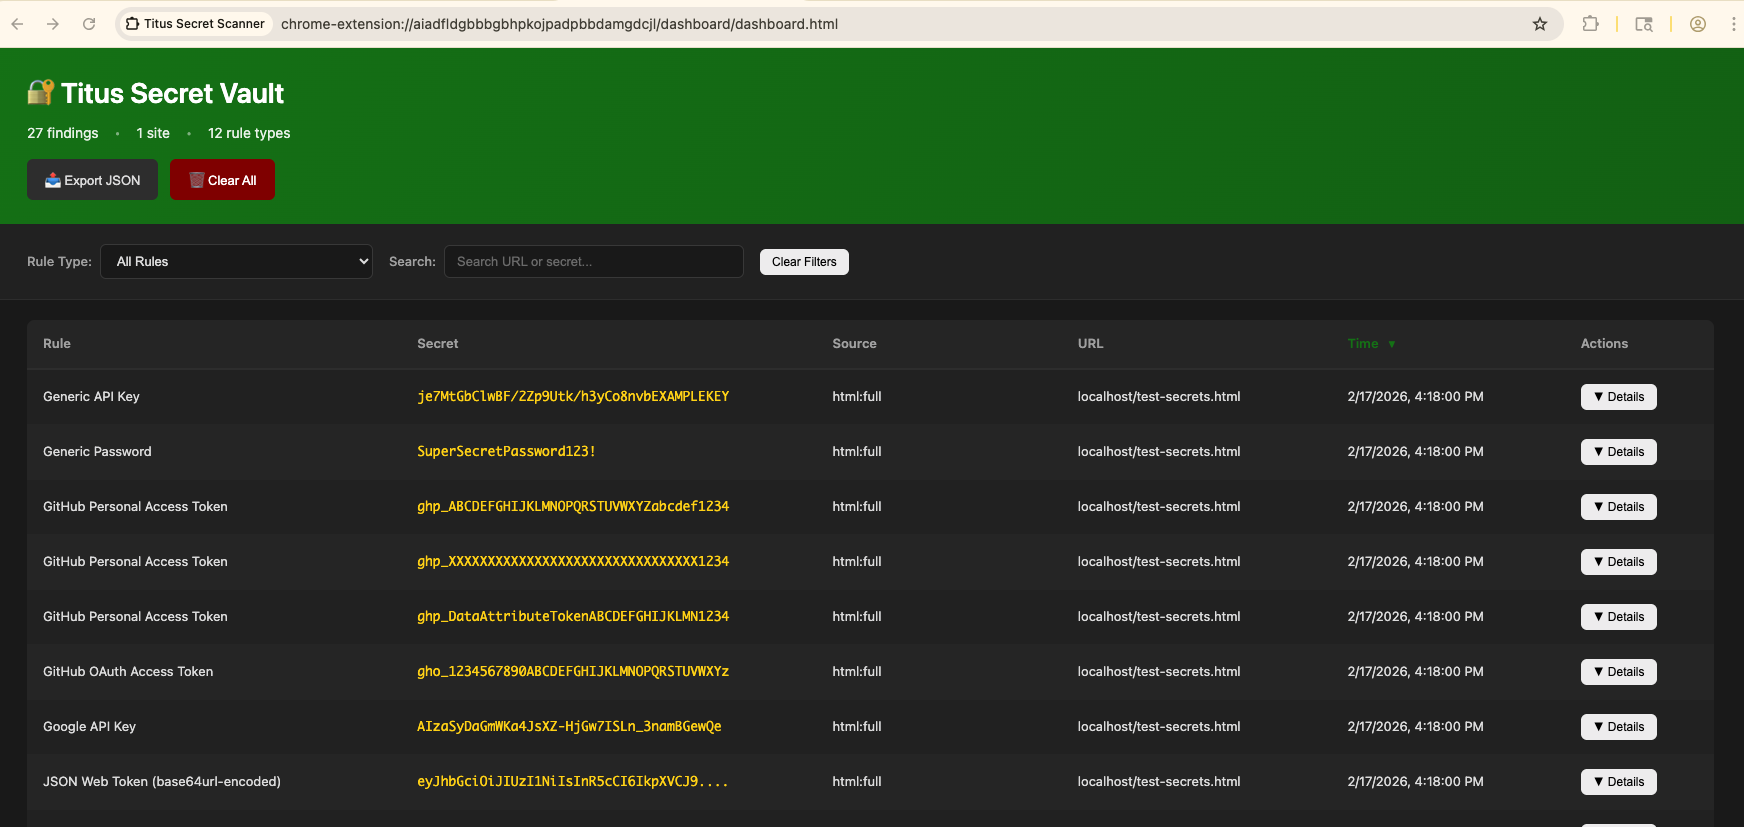 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
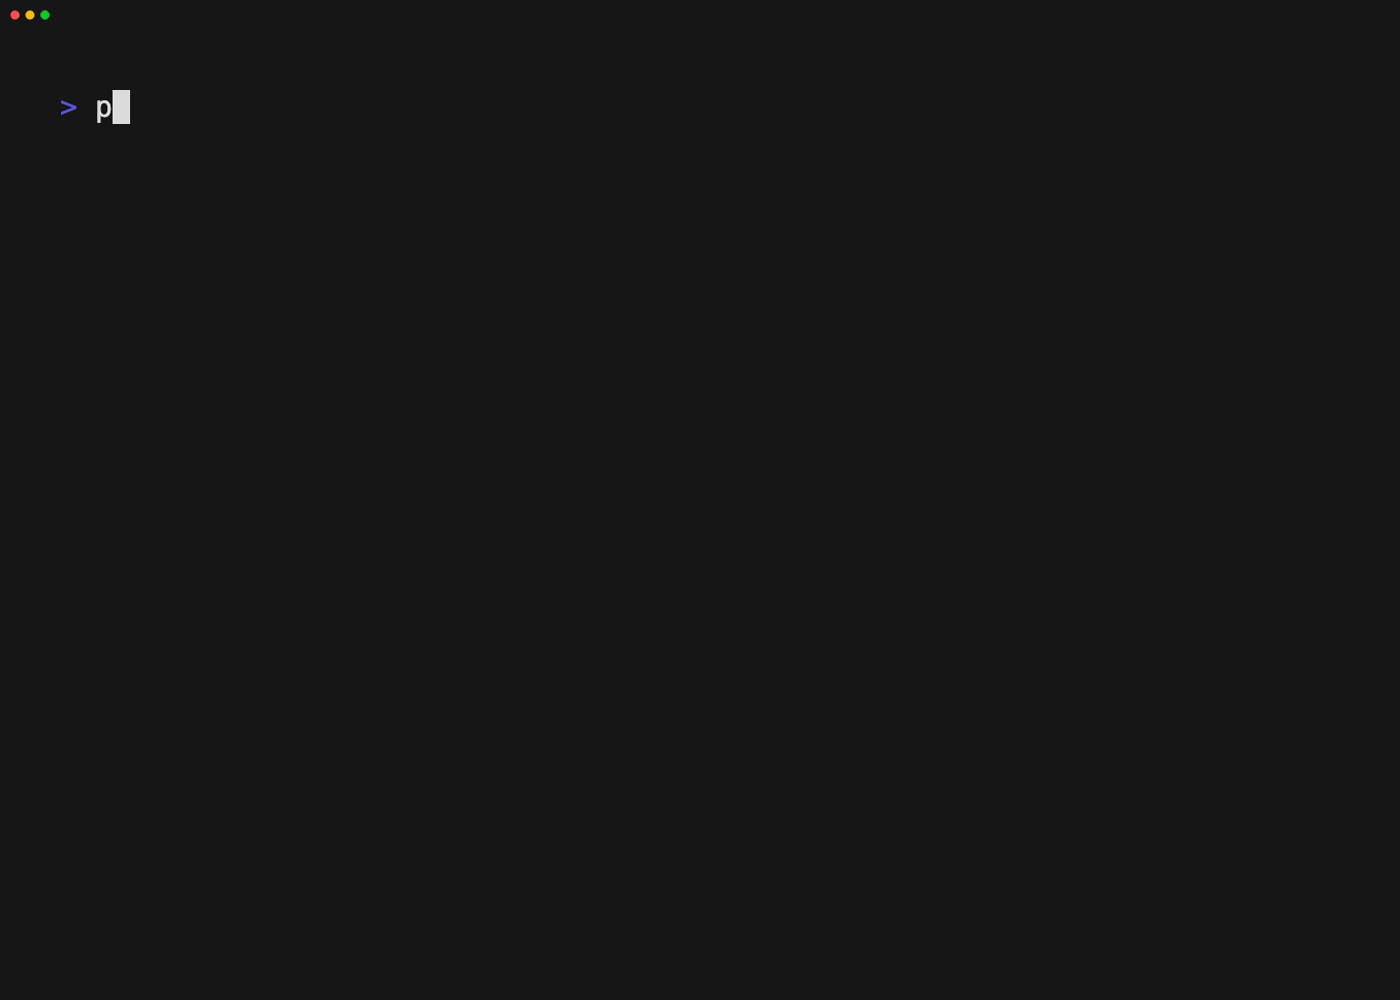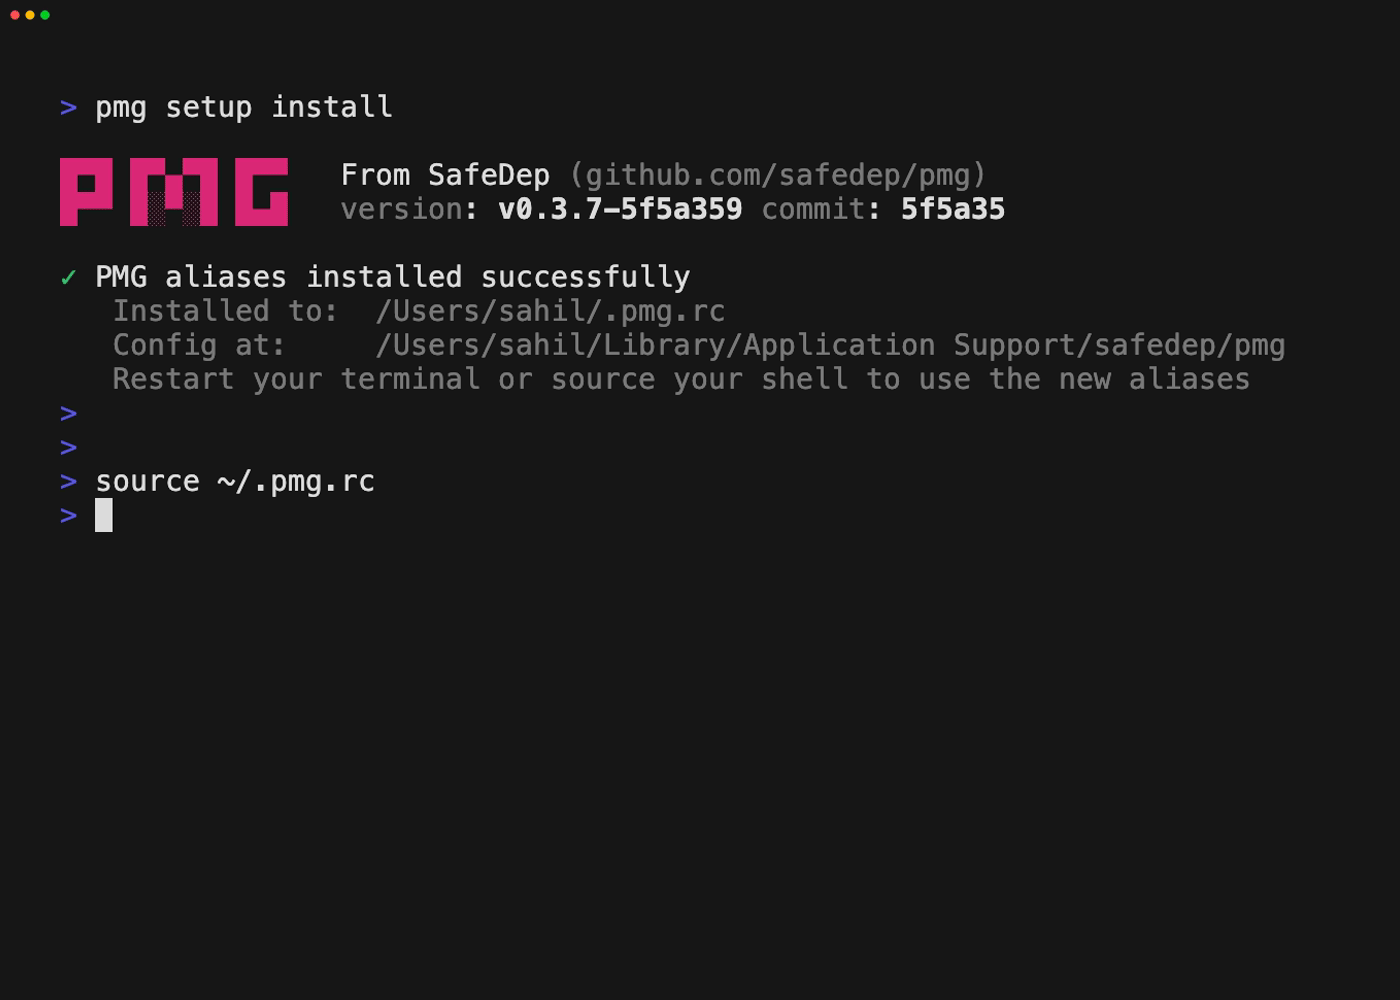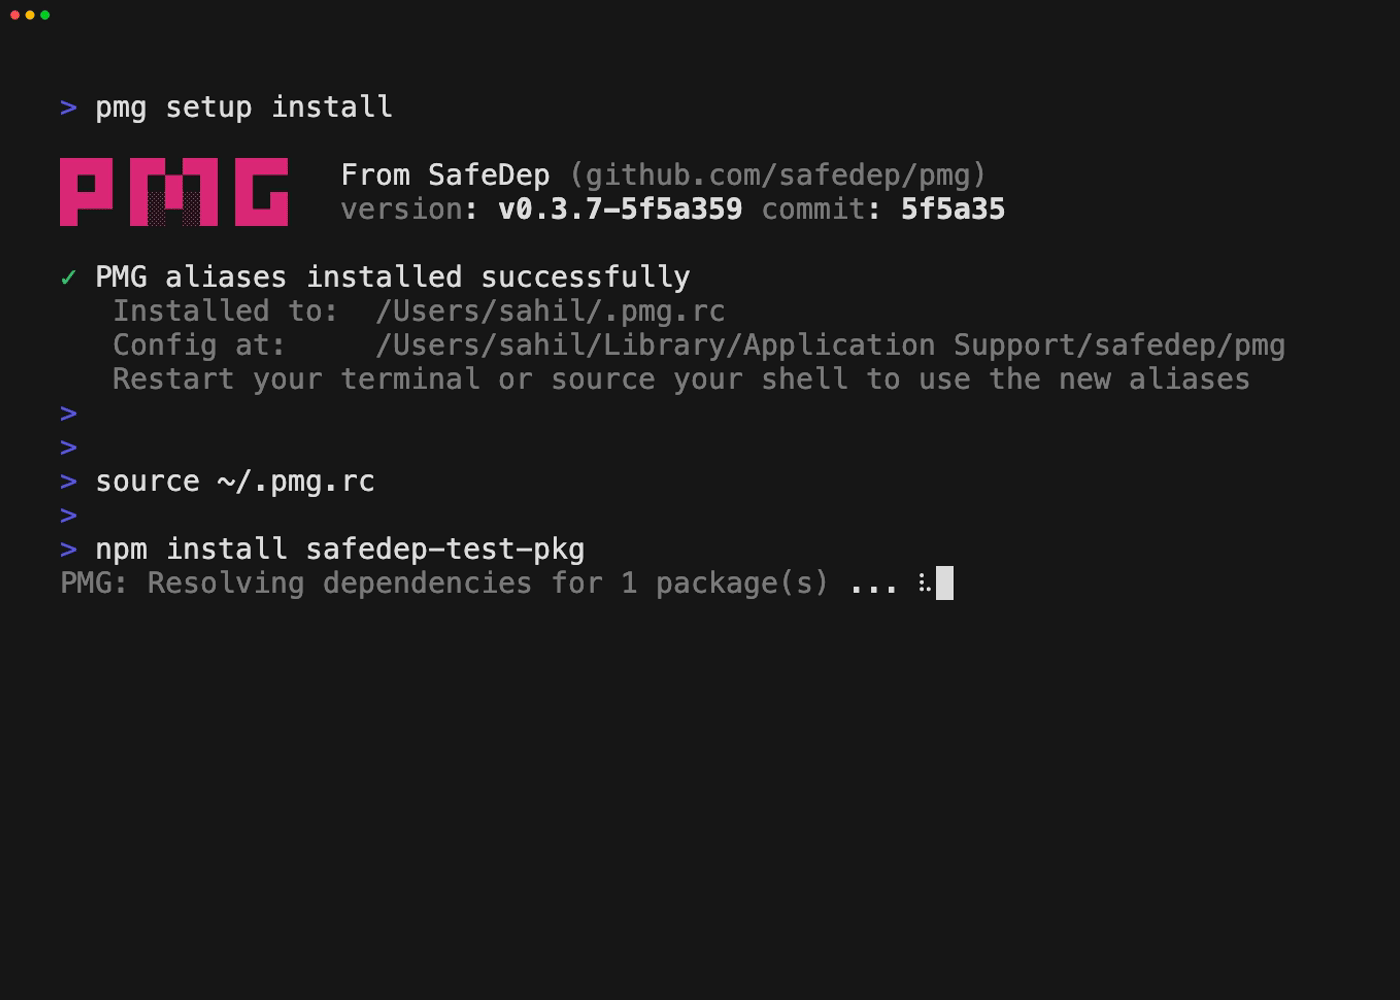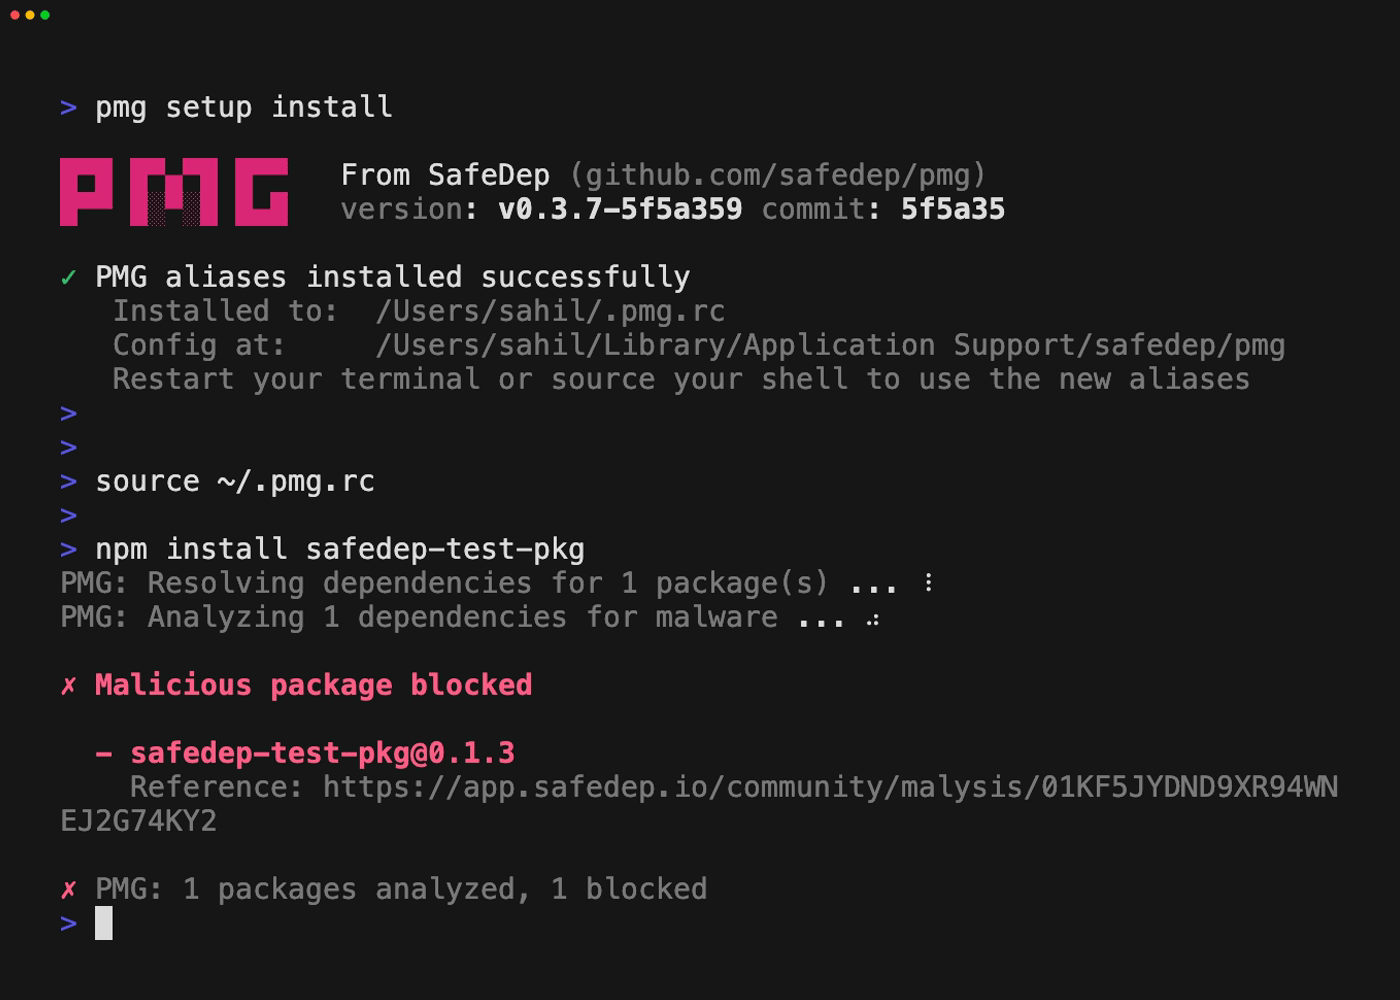 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.