
Archived
flare-qdb
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
 lmacken/pyrasite
Inject code into running Python processes
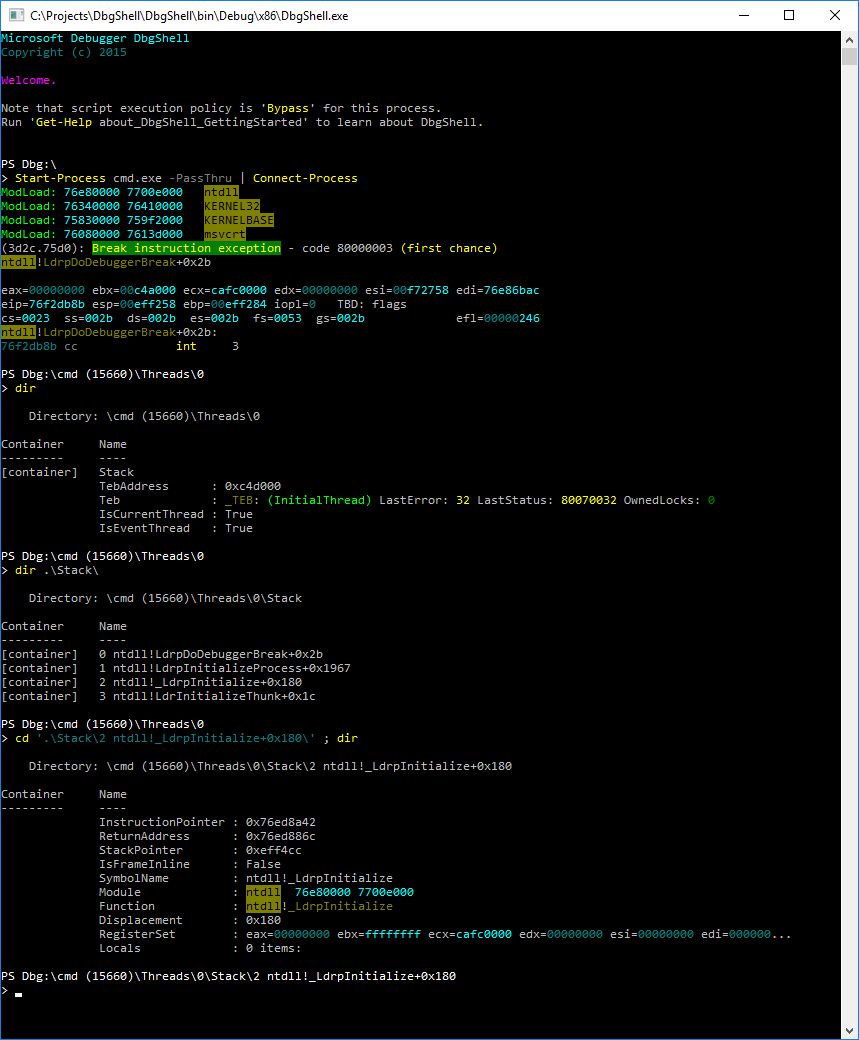 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
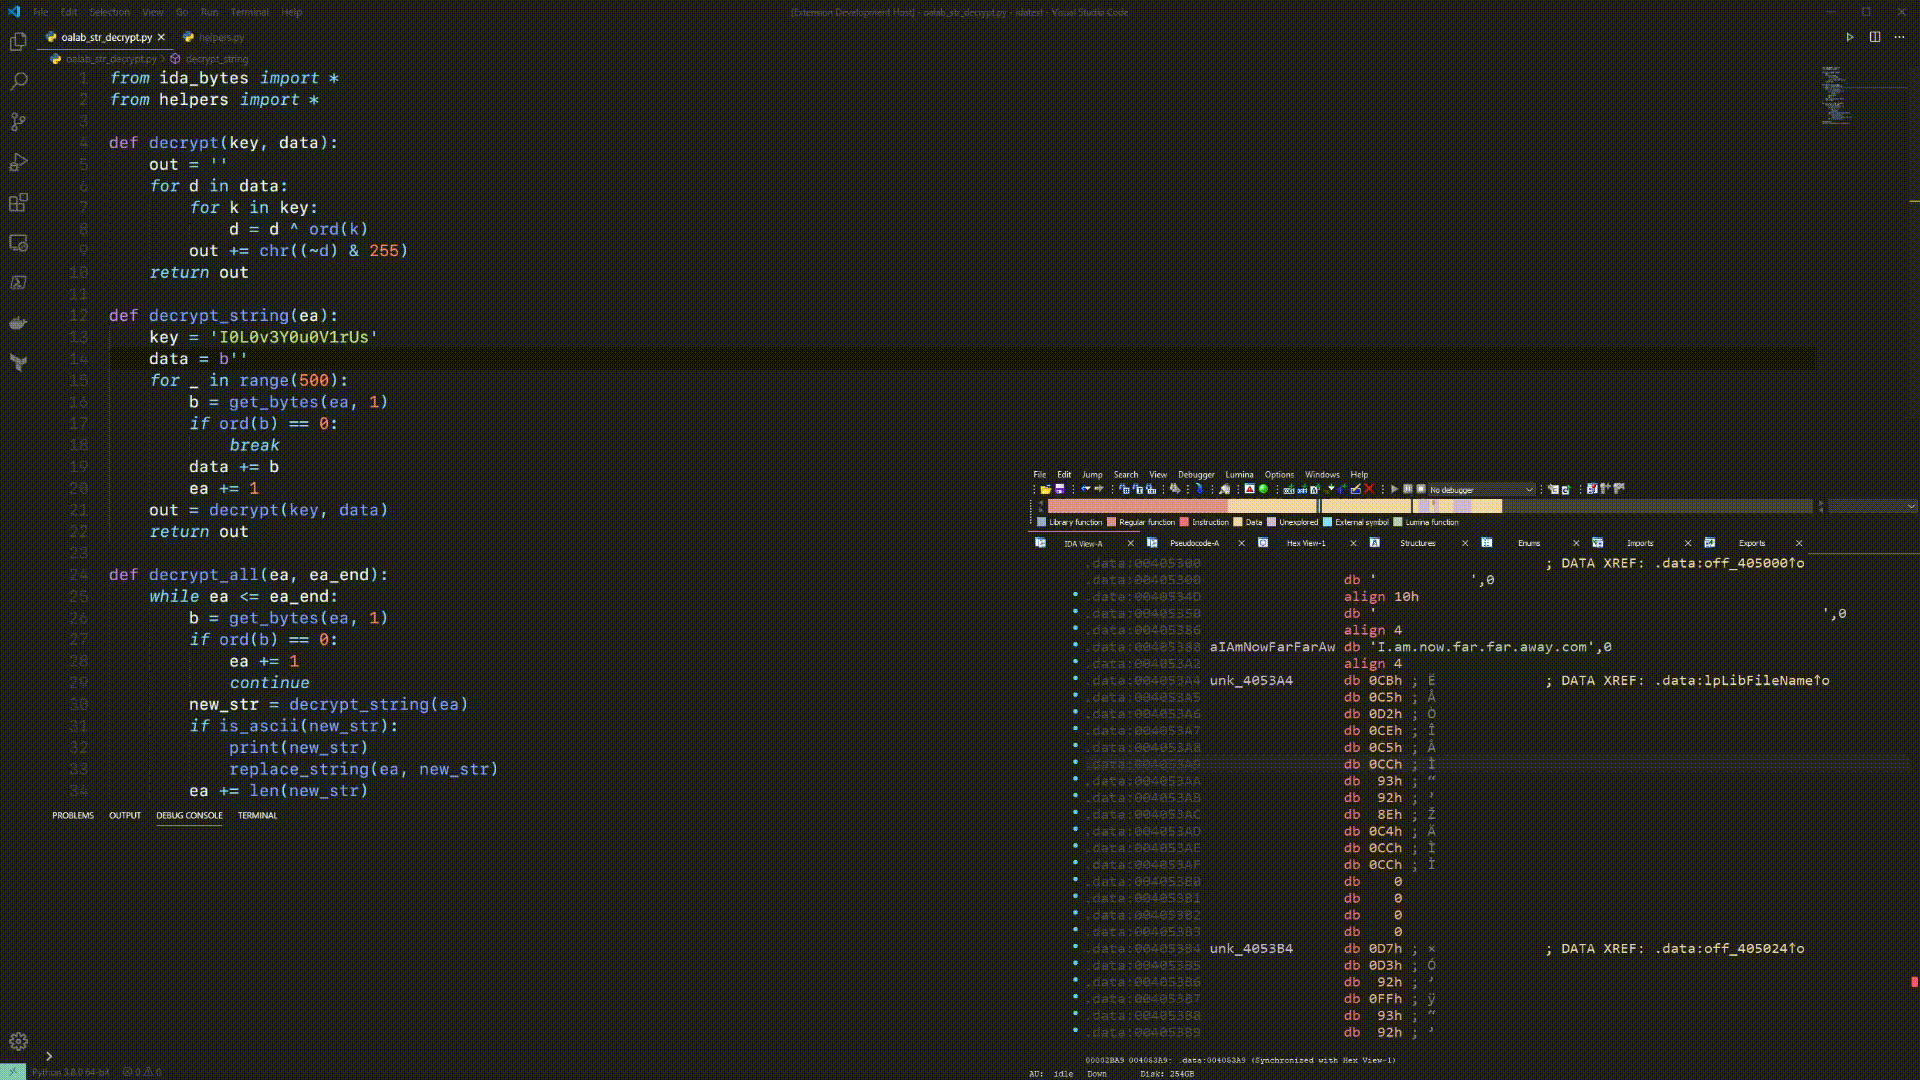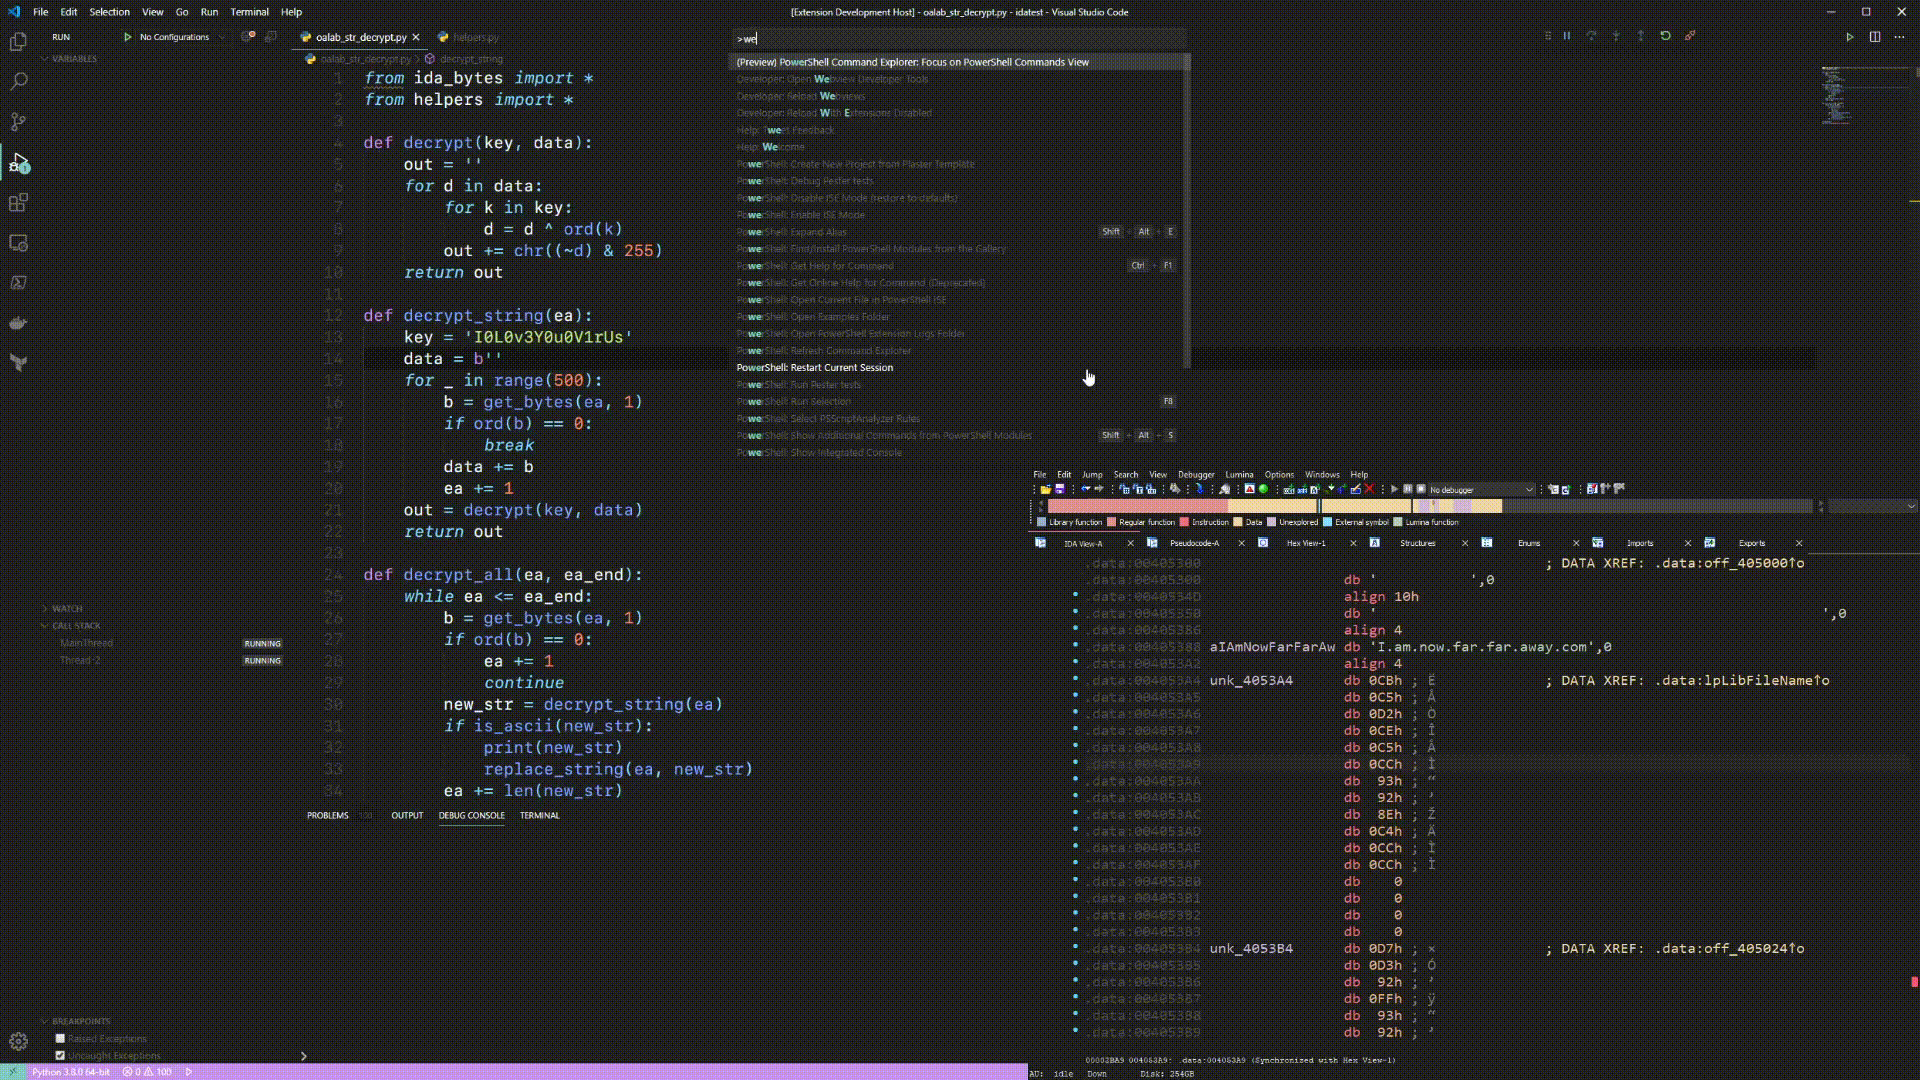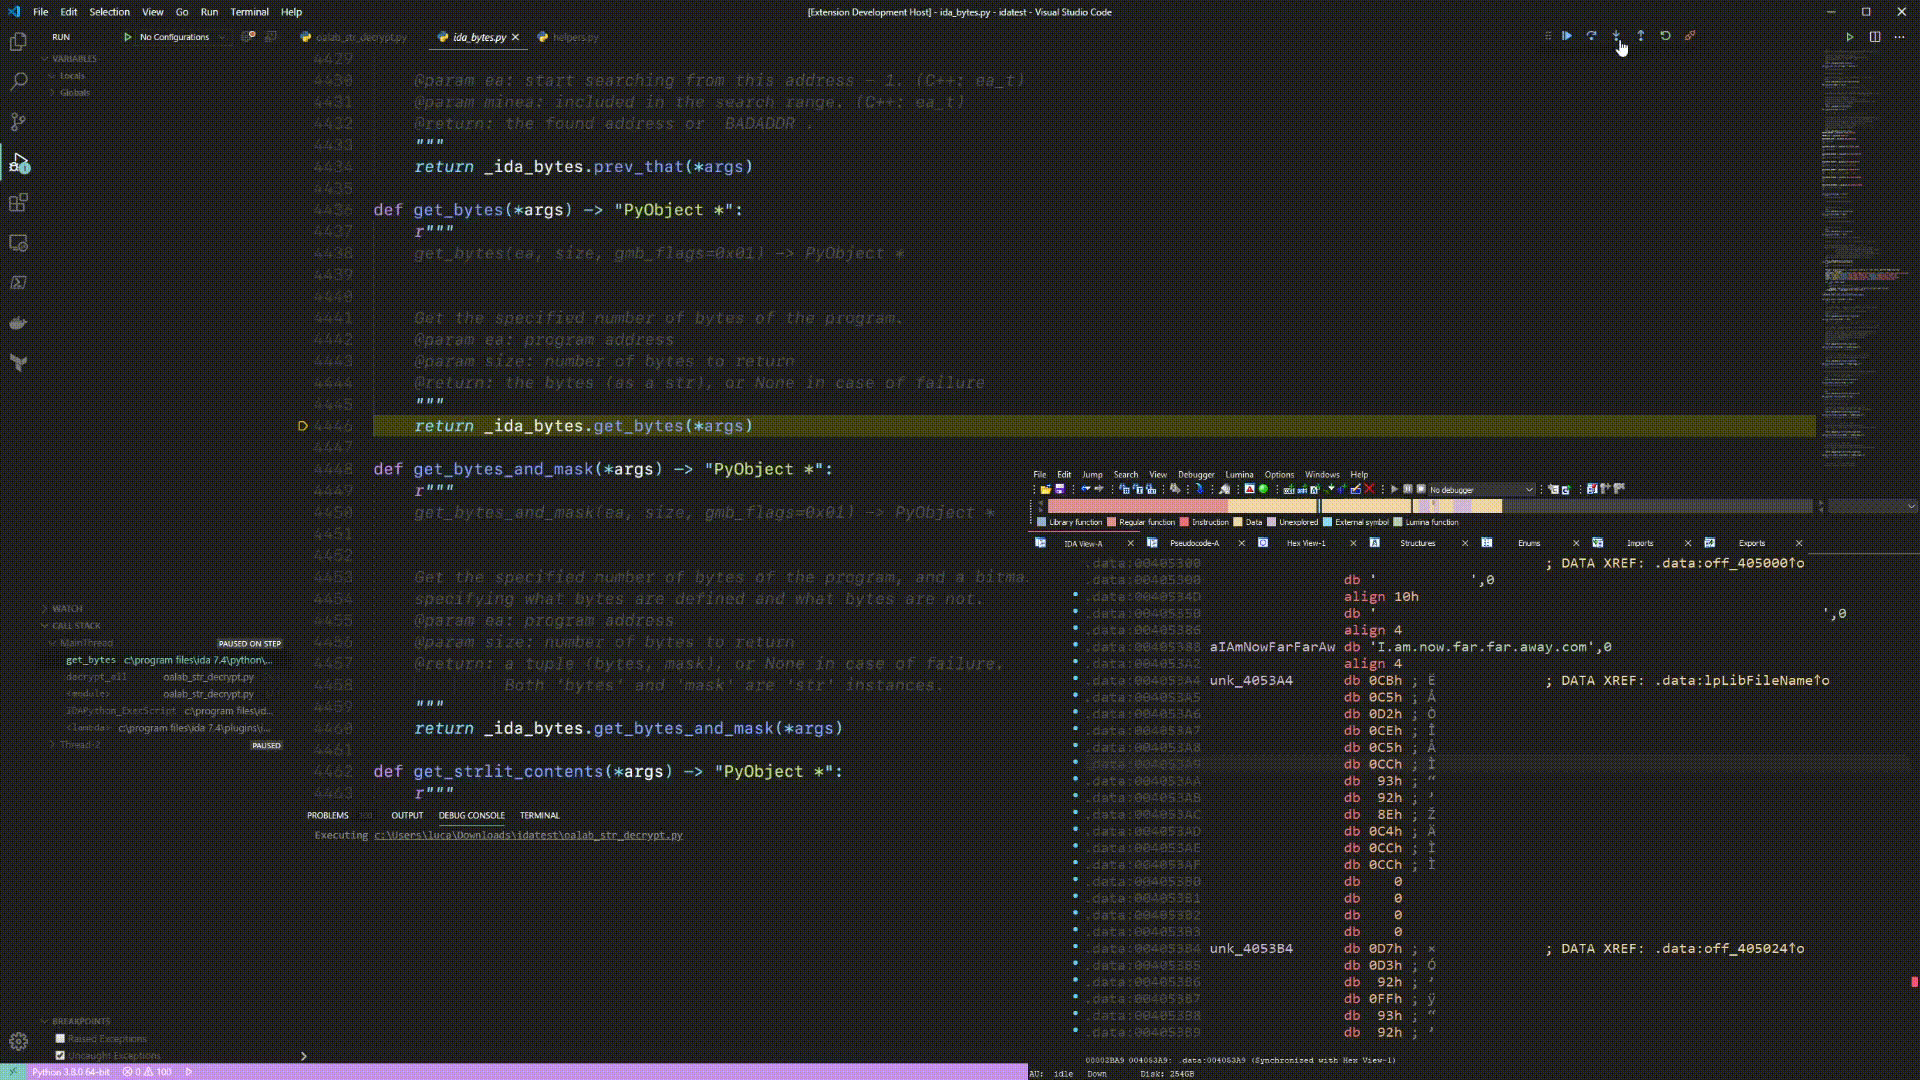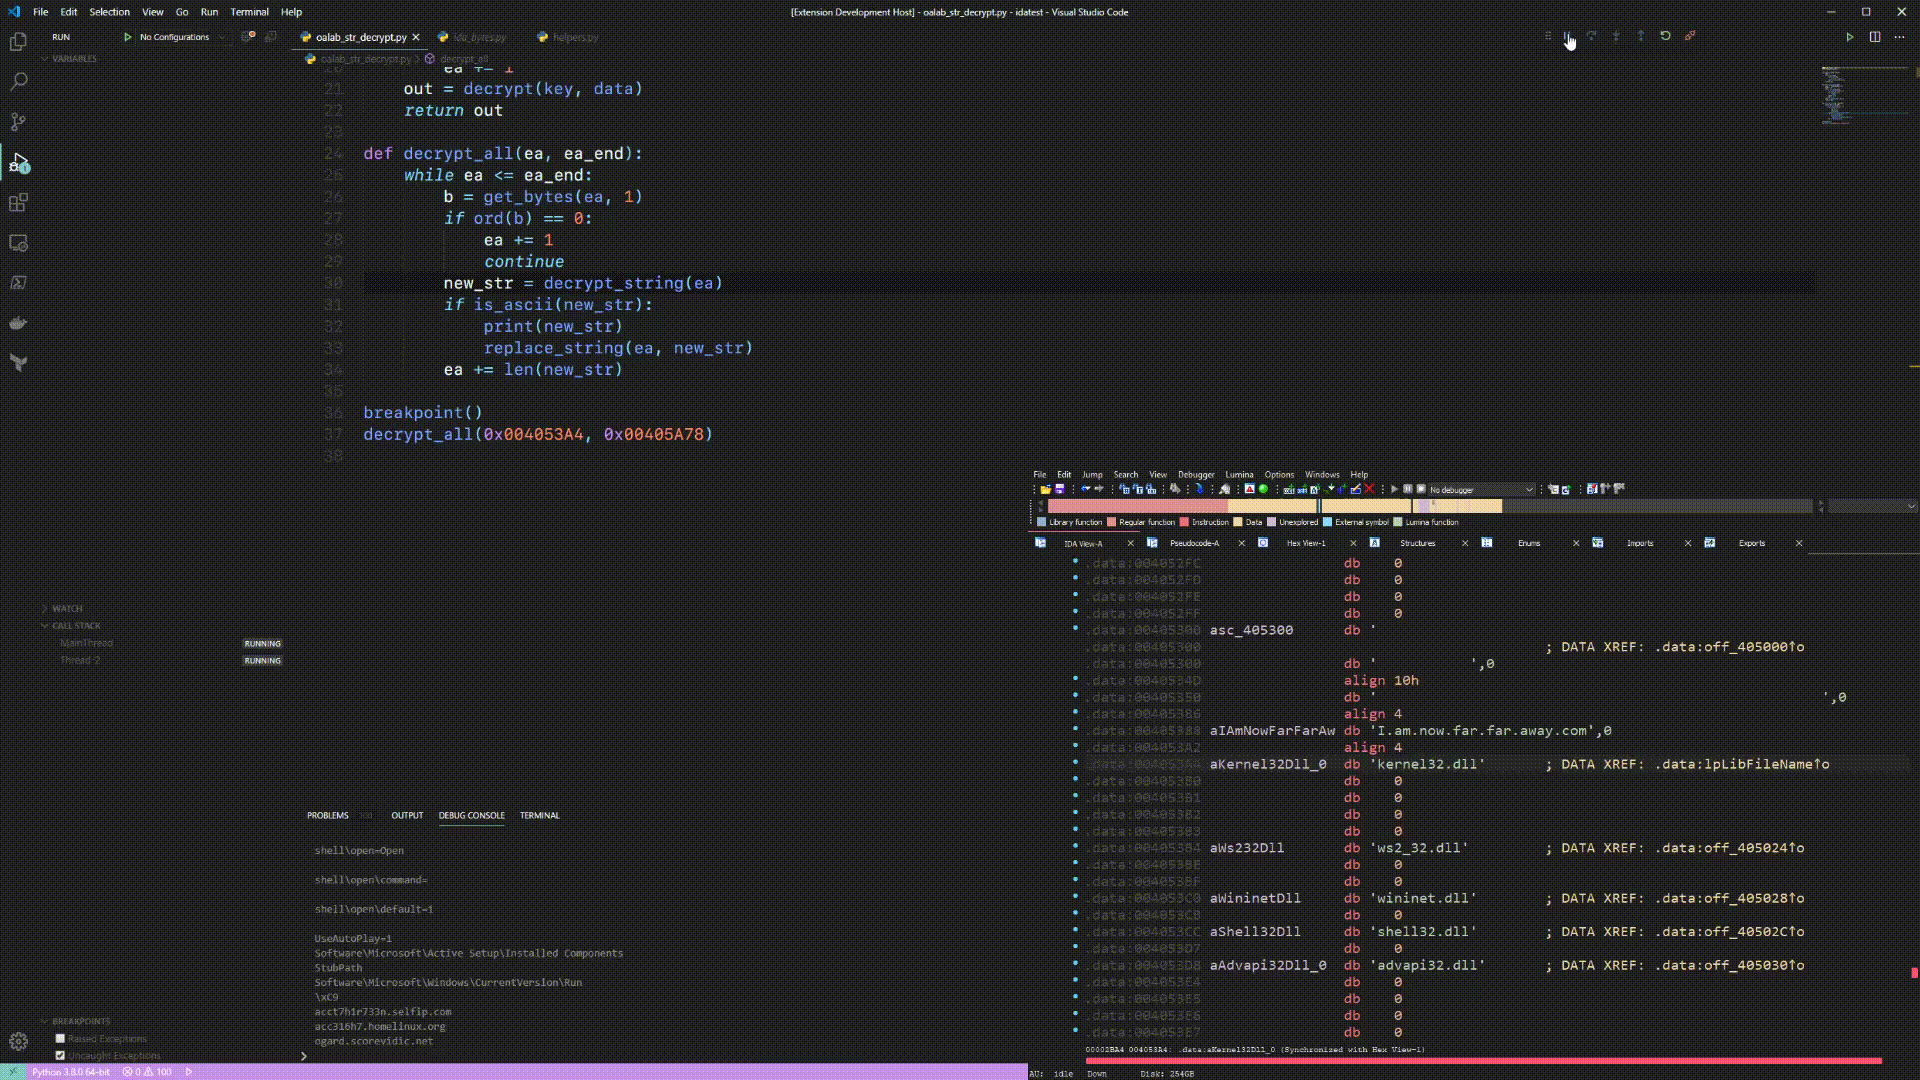 ioncodes/idacode
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
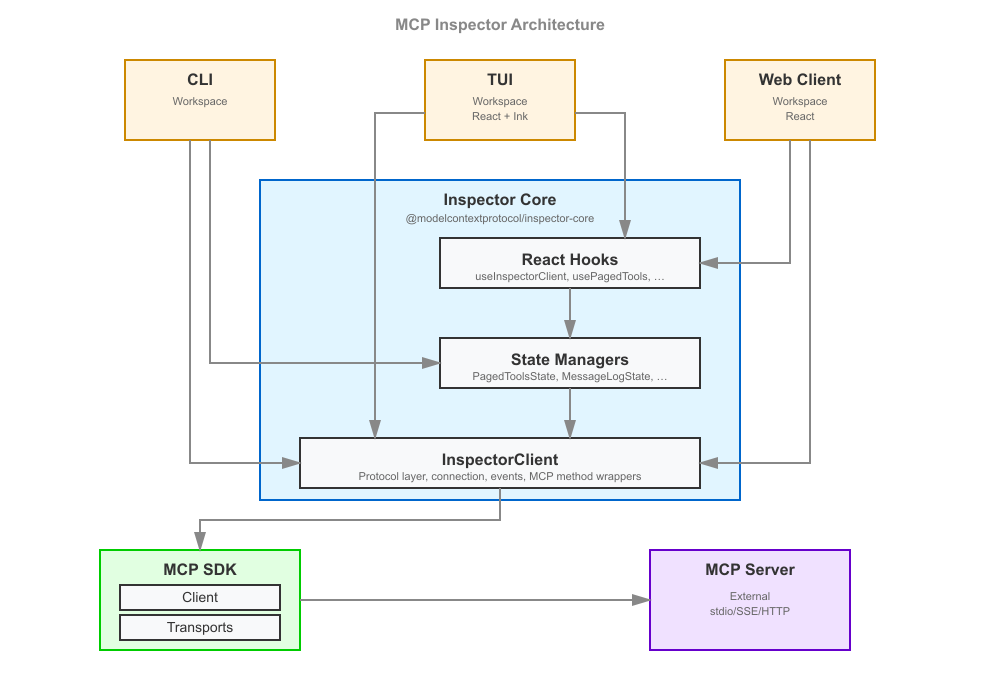 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
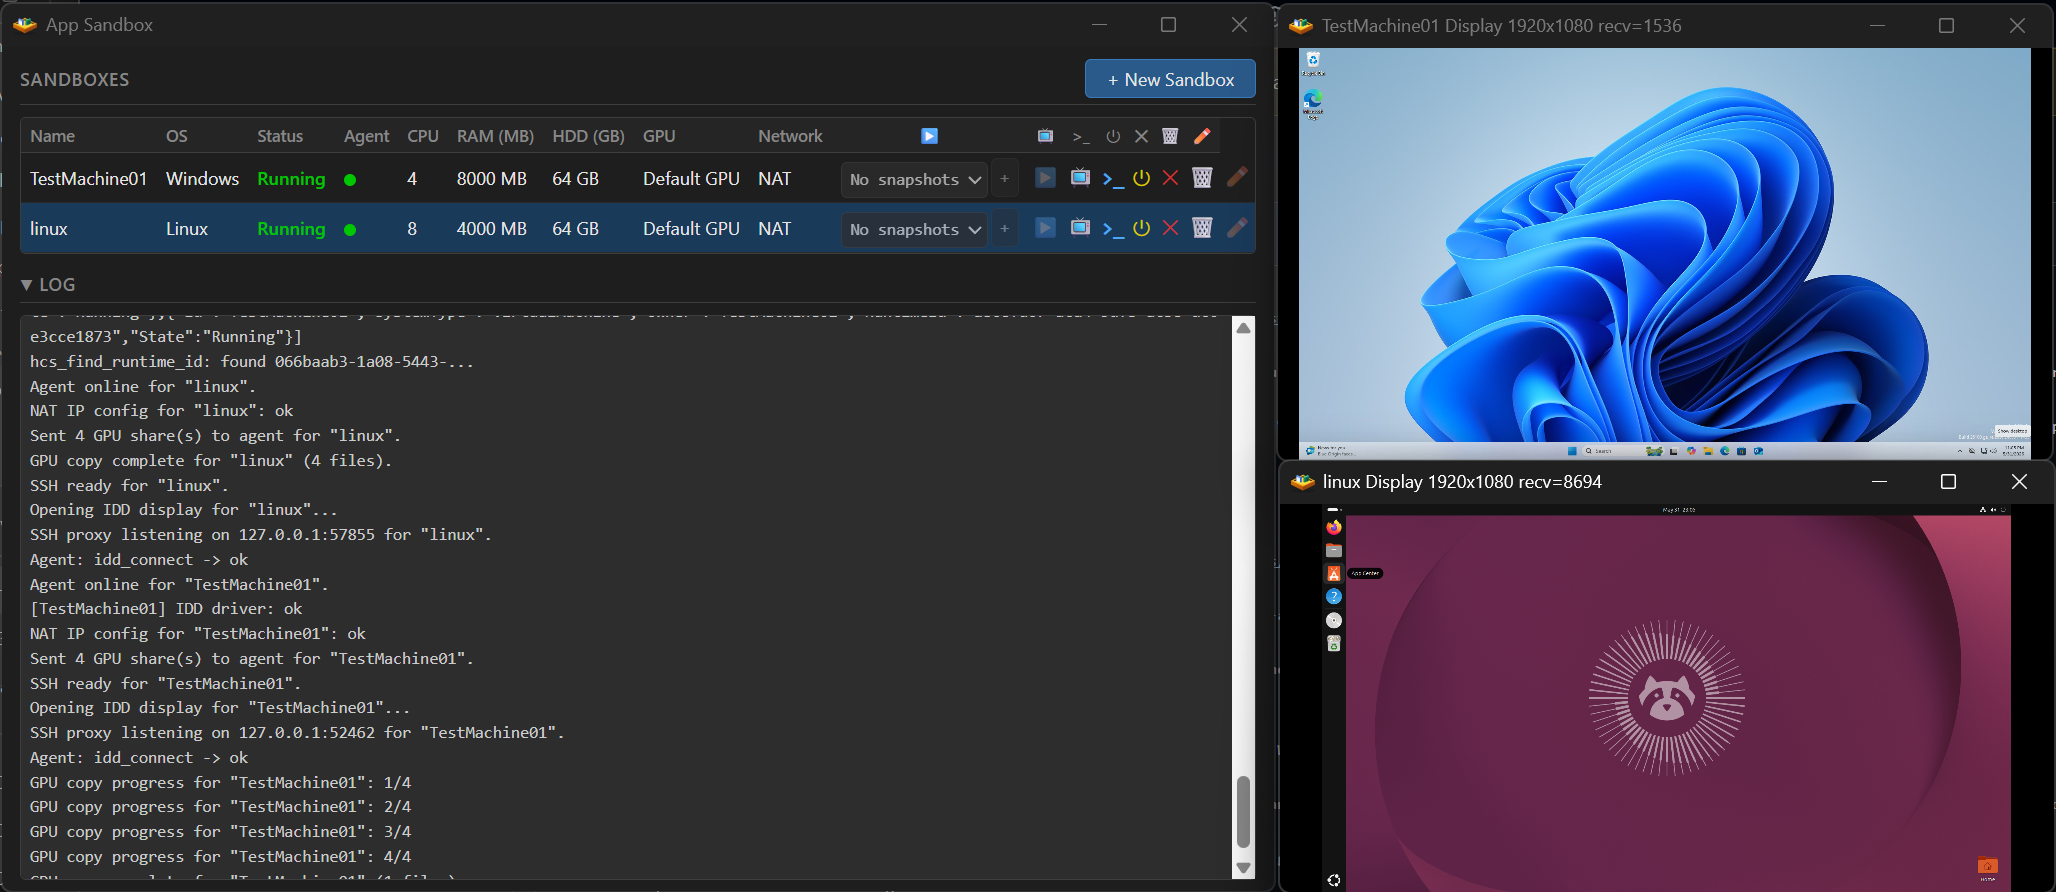 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.

 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 buguroo/cuckooautoinstall
Auto Installer Script for Cuckoo Sandbox
 oalabs/frida-wshook
Script analysis tool based on Frida.re
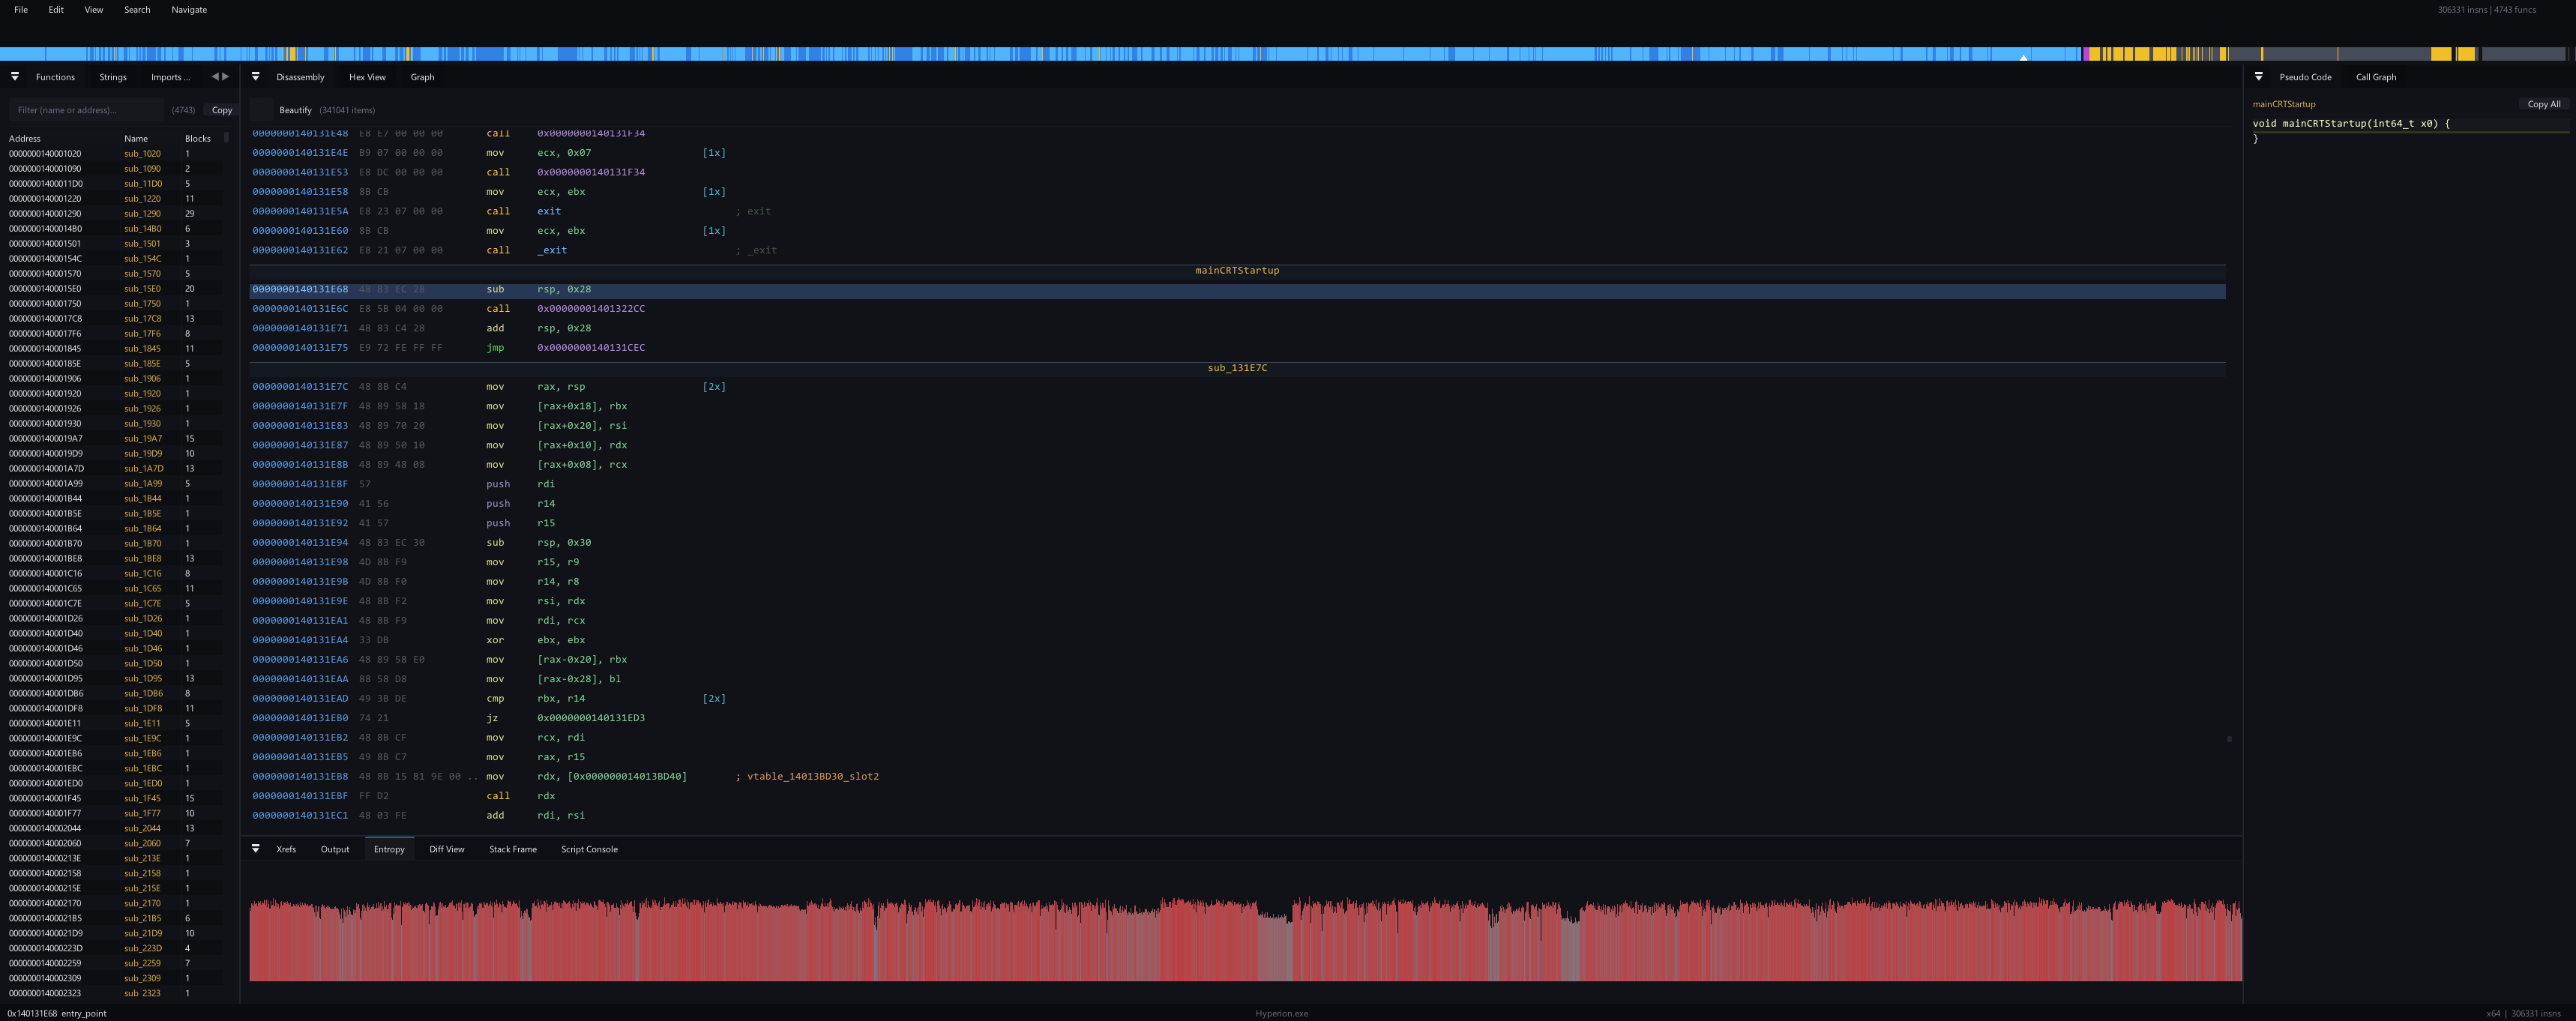 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery