
bip
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
binary-analysiscode-analysisreverse-engineering+2
synacktiv/bipObject-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
 eset/ipyida
IPython console integration for IDA Pro
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 binref/agent
Language Model Agent Instructions for Binary Refinery
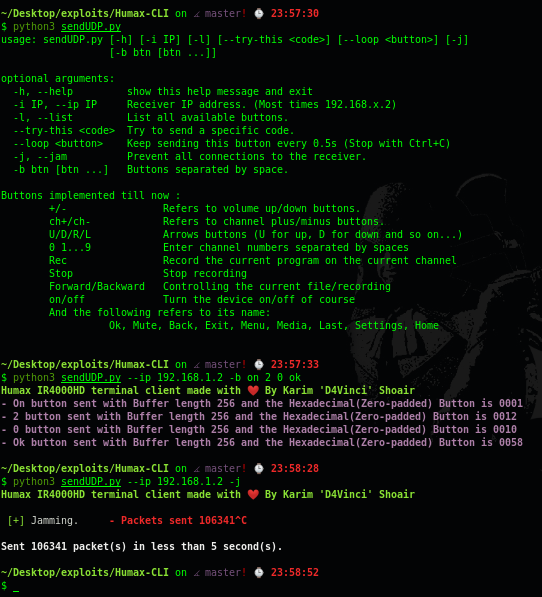 d4vinci/humax-cli
An unofficial Humax IR4000HD terminal client with enhanced features.
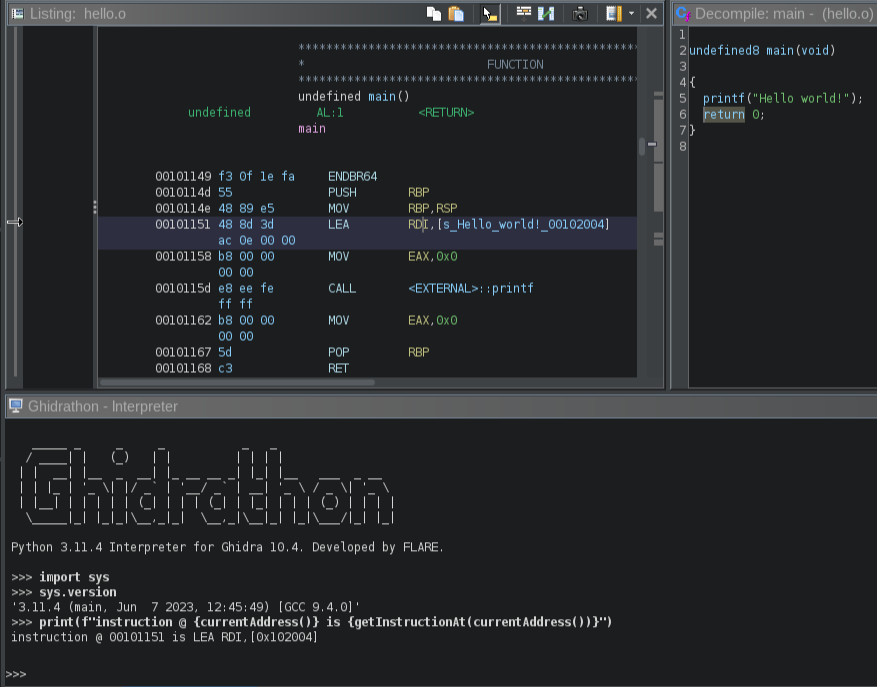 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 bytesizedmarius/rewerse-engineering
Rewe API reverse engineering in Go
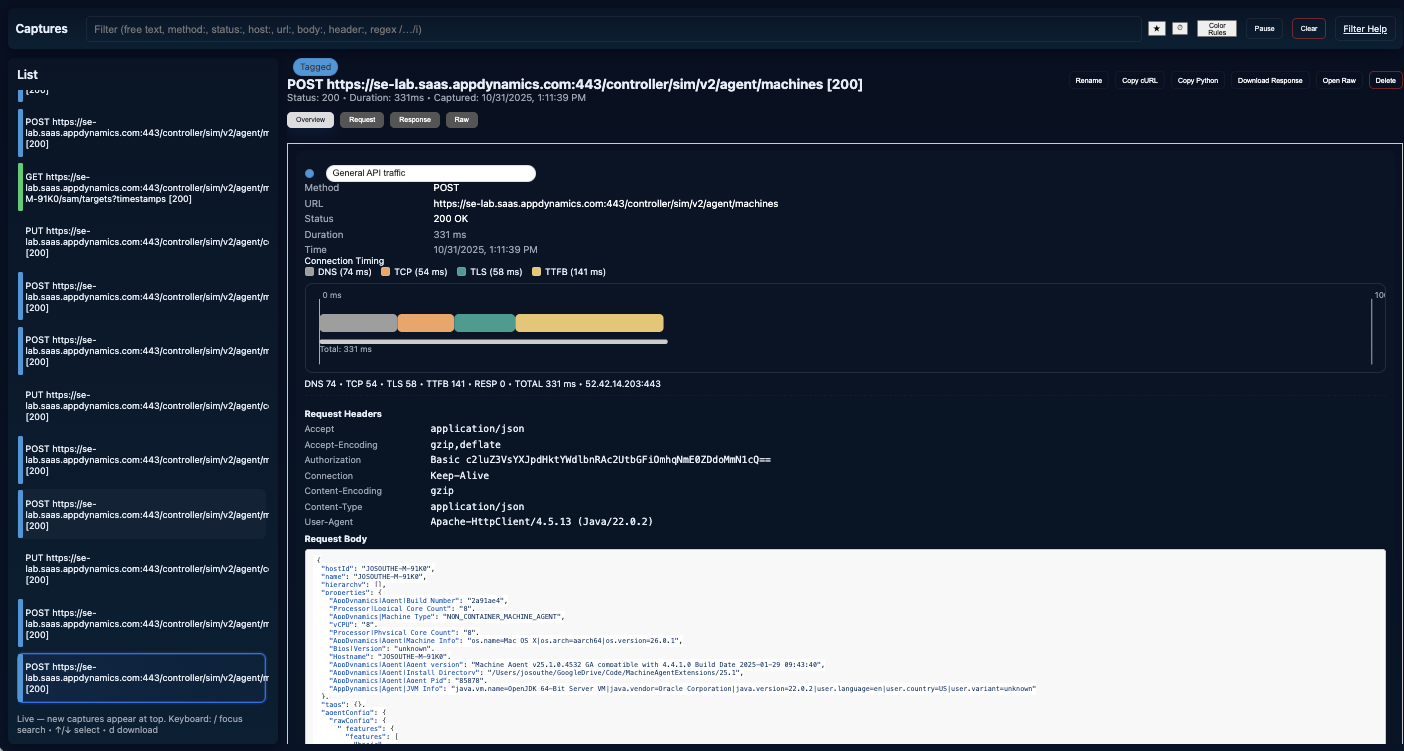 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
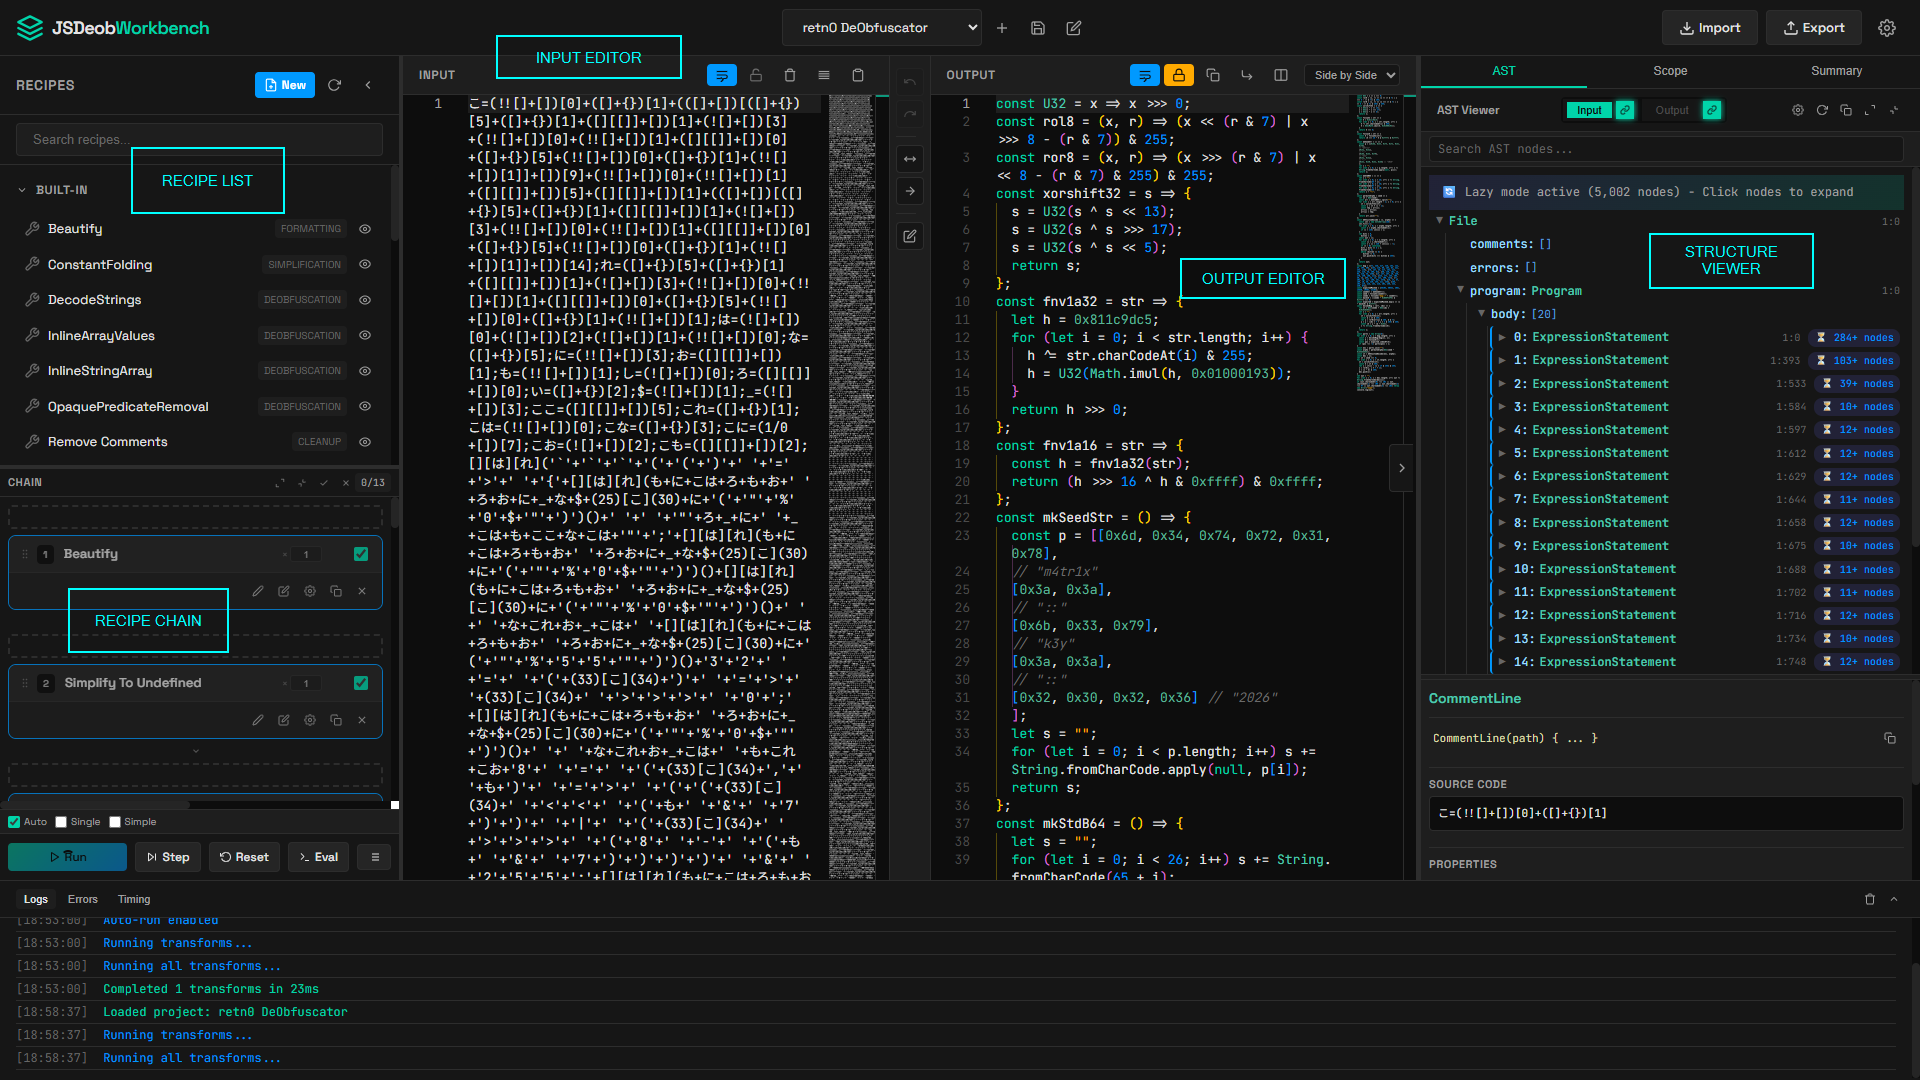 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.