

LinuxCatScale
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
digital-forensicsforensicsincident-response+2
339
withsecurelabs/linuxcatscaleIncident Response collection and processing scripts with automated reporting scripts
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
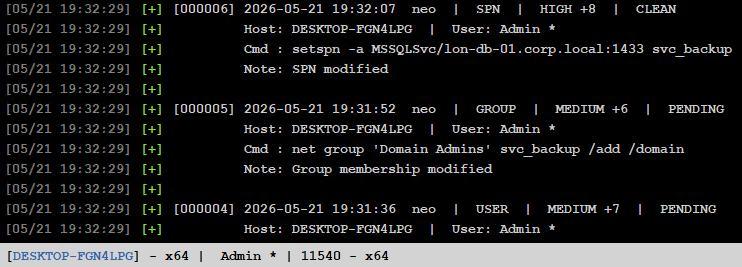 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints