

amass
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
data-exfiltrationdns-analysisdns-fuzzing+10
owasp-amass/amassIn-depth attack surface mapping and asset discovery
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
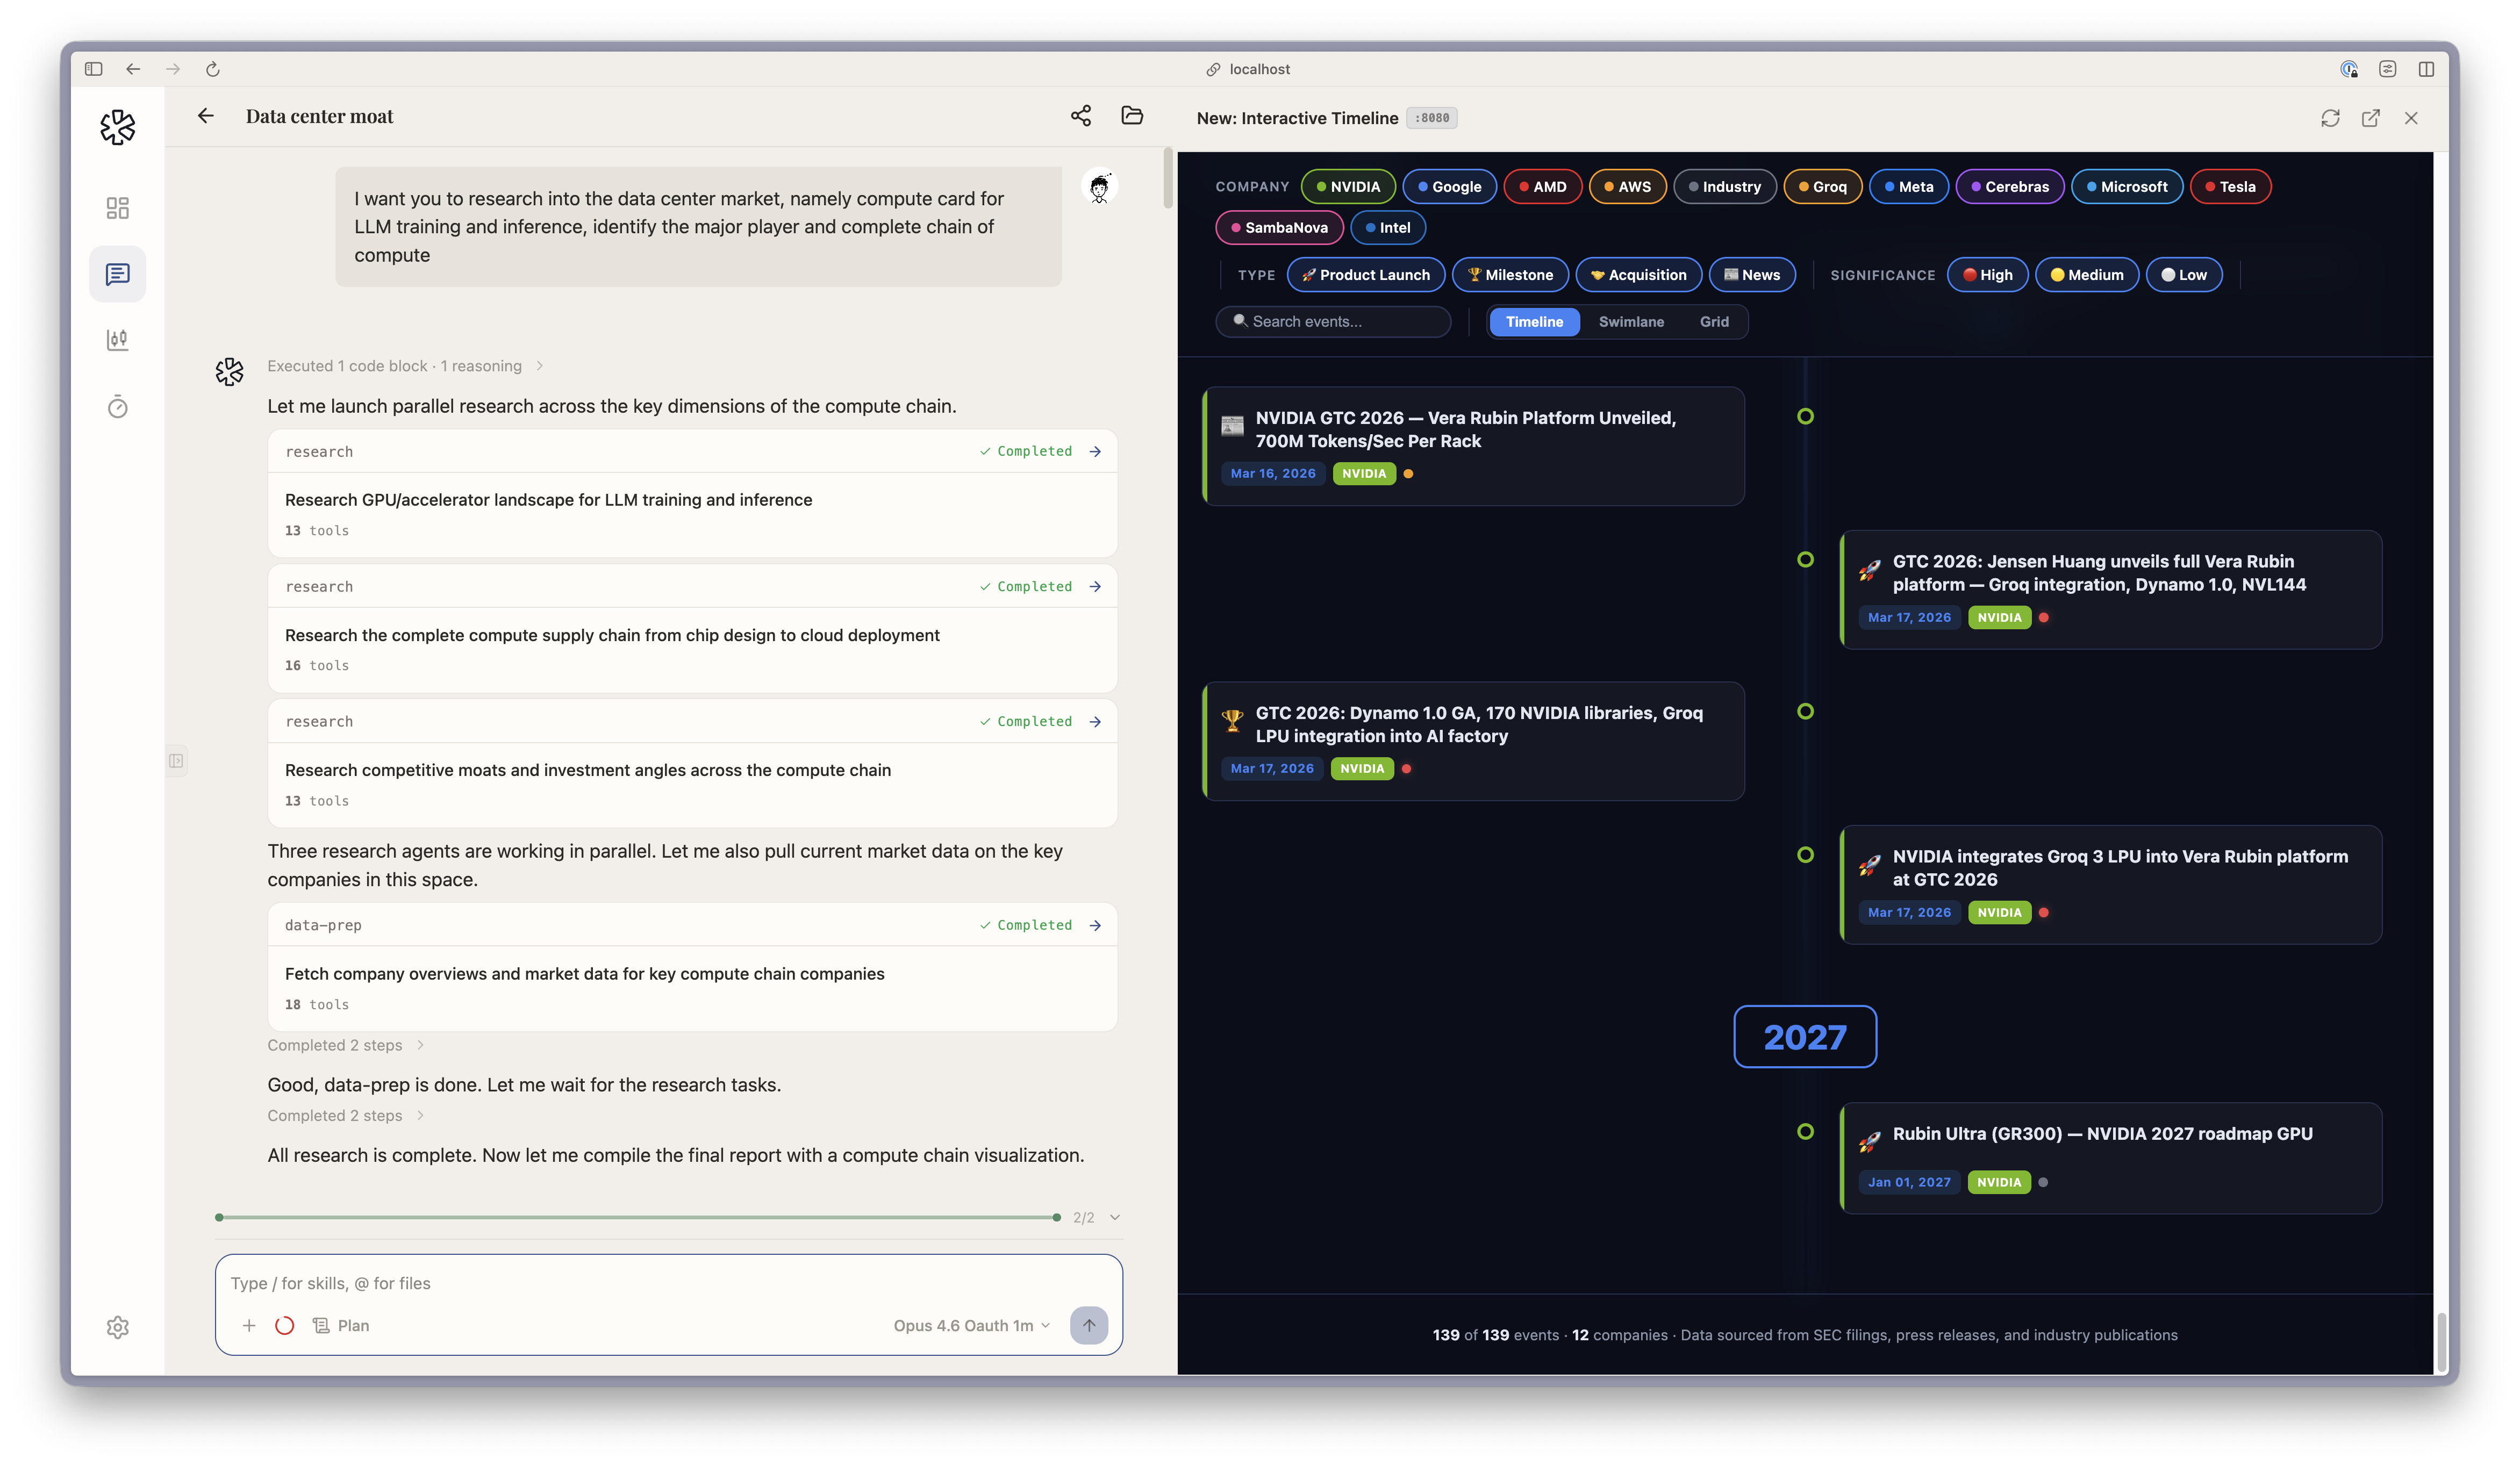 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 timbo05sec/autocrack
Hashcat wrapper to help automate the cracking process
 reedgraff/hingesdk
Hinge Dating App SDK for python for lonely bored SWEs
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
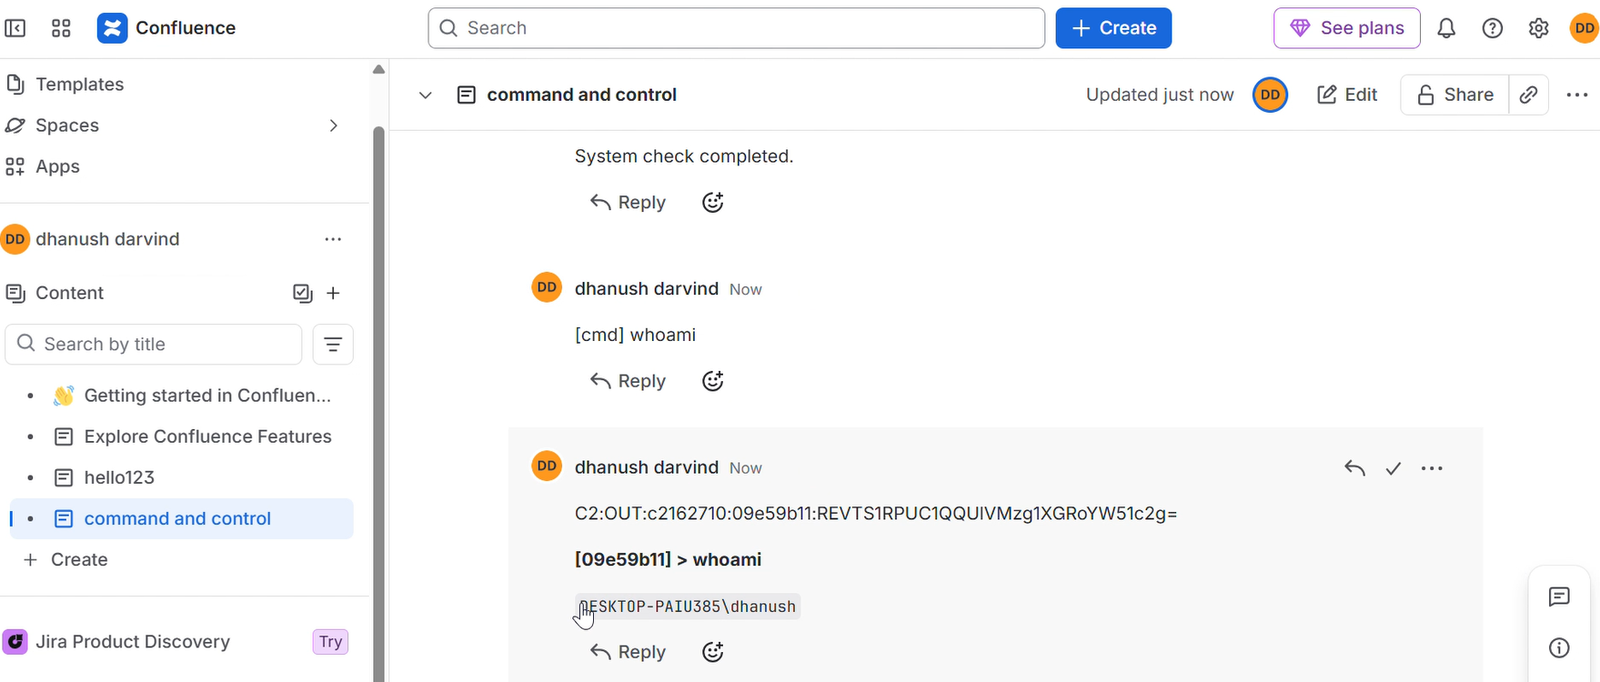 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
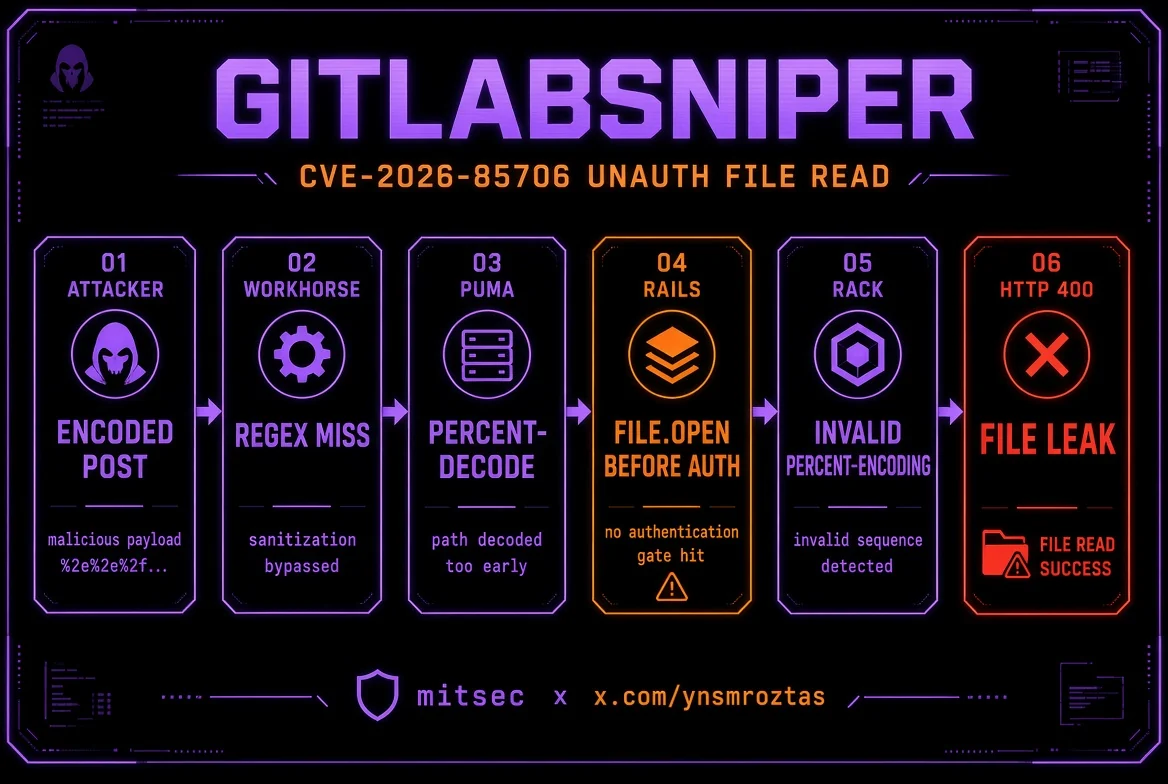 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 vulncheck-oss/jupyter-notebooks
Example Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 j0ey17/automate_exploit_cve-2022-44268
An exploit automation script that builds upon the work of Voidzone security.