
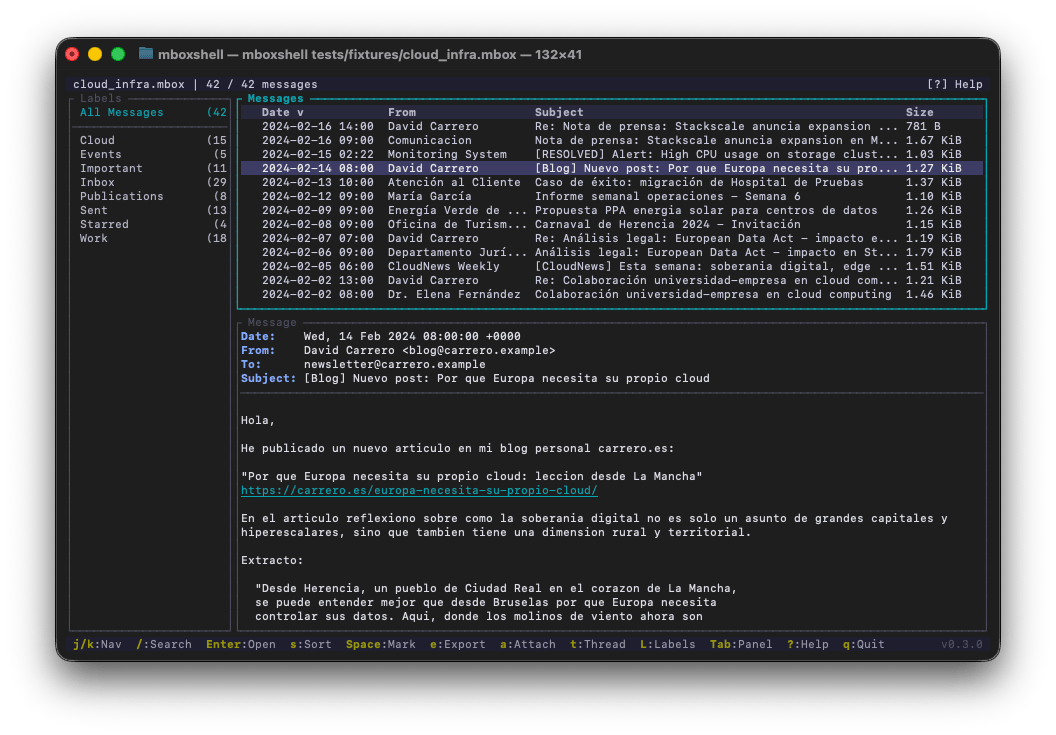
mboxshell
 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
data-recoverydigital-forensicsemail-security+4
dcarrero/mboxshellmboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
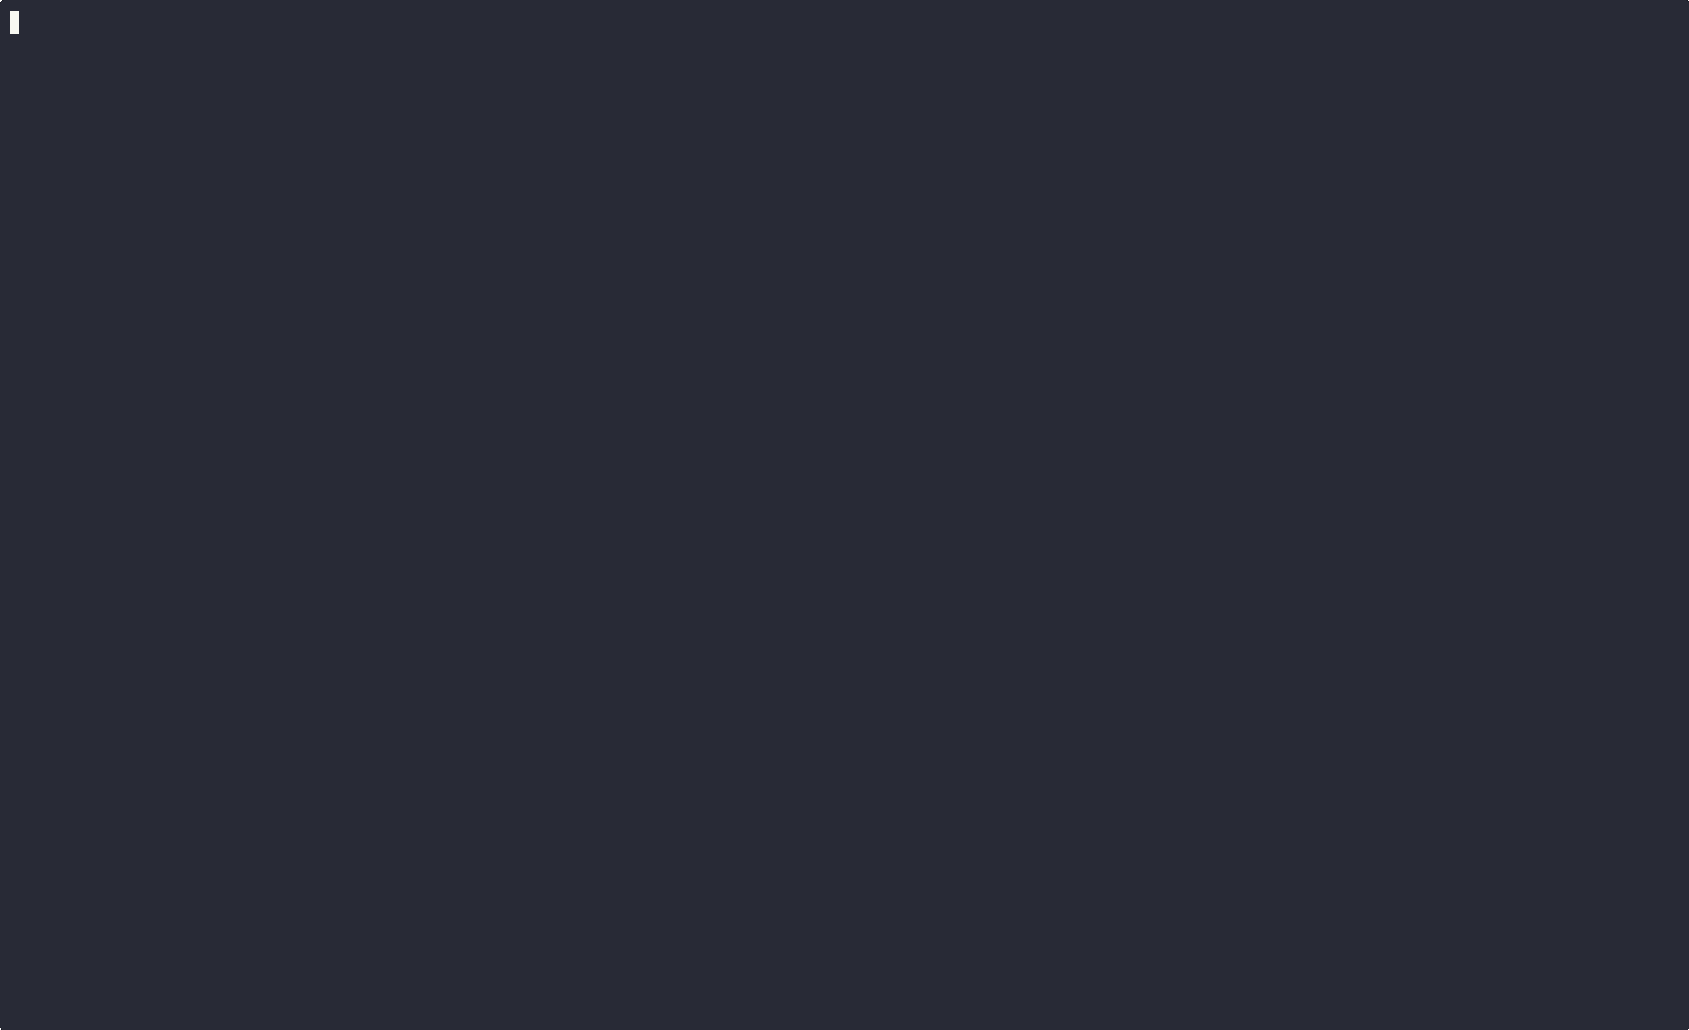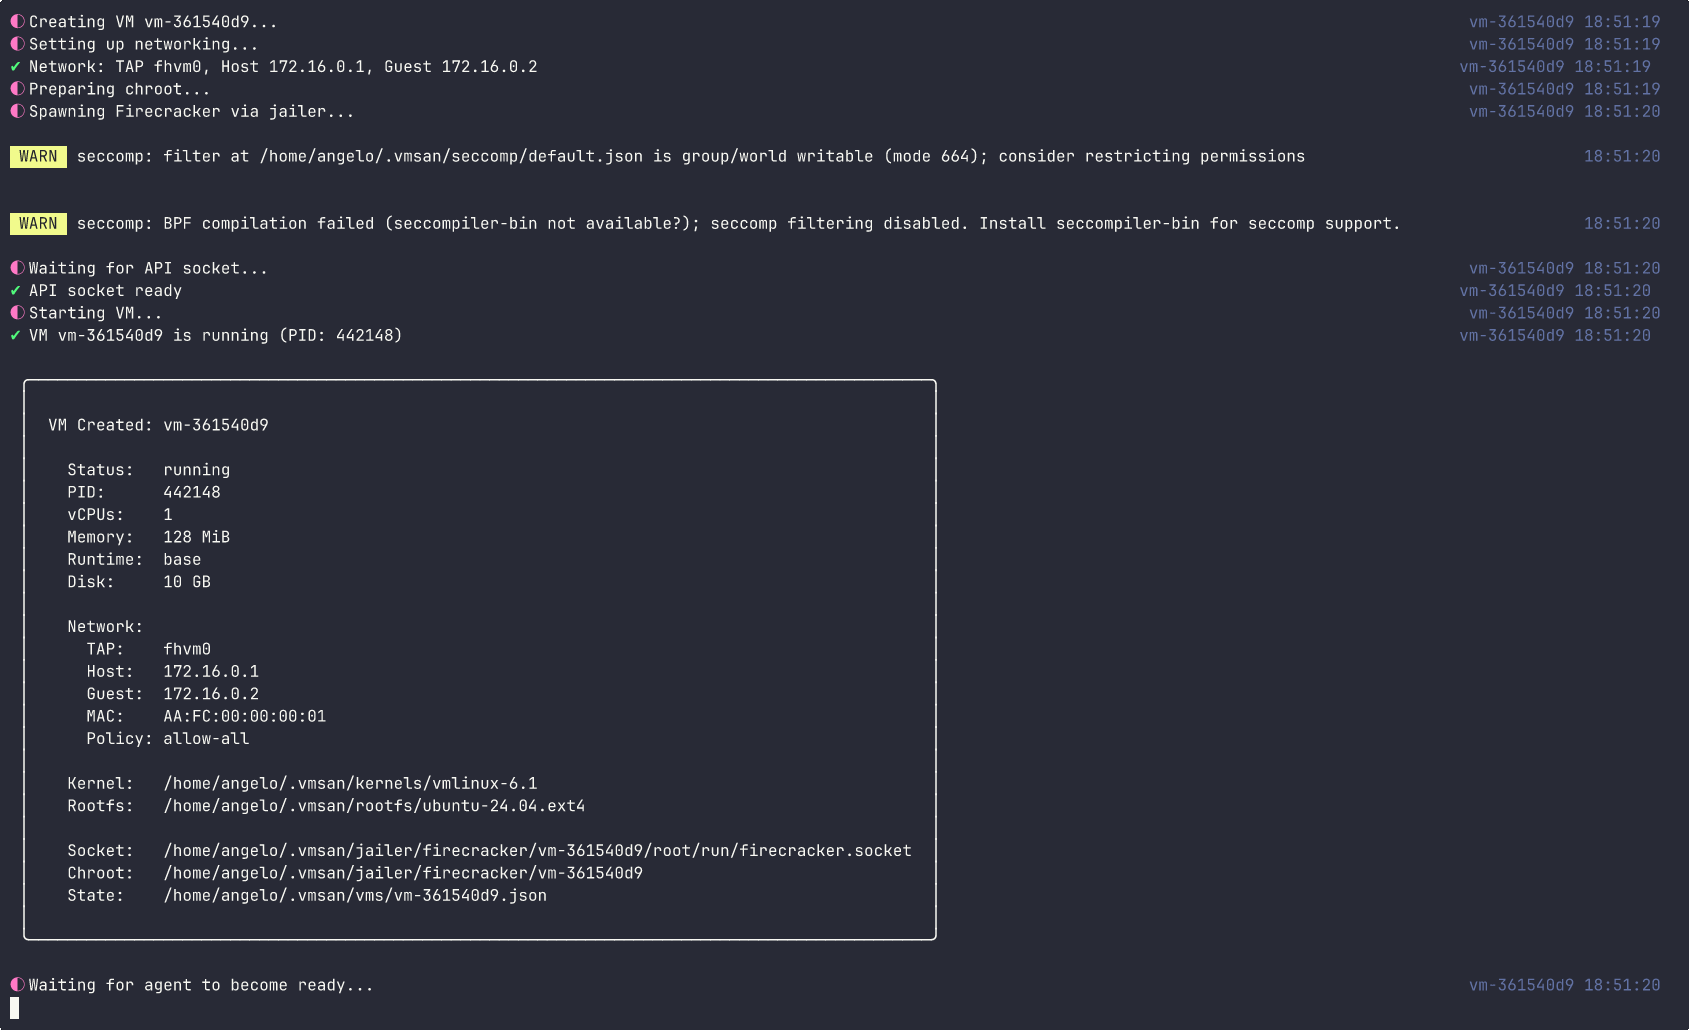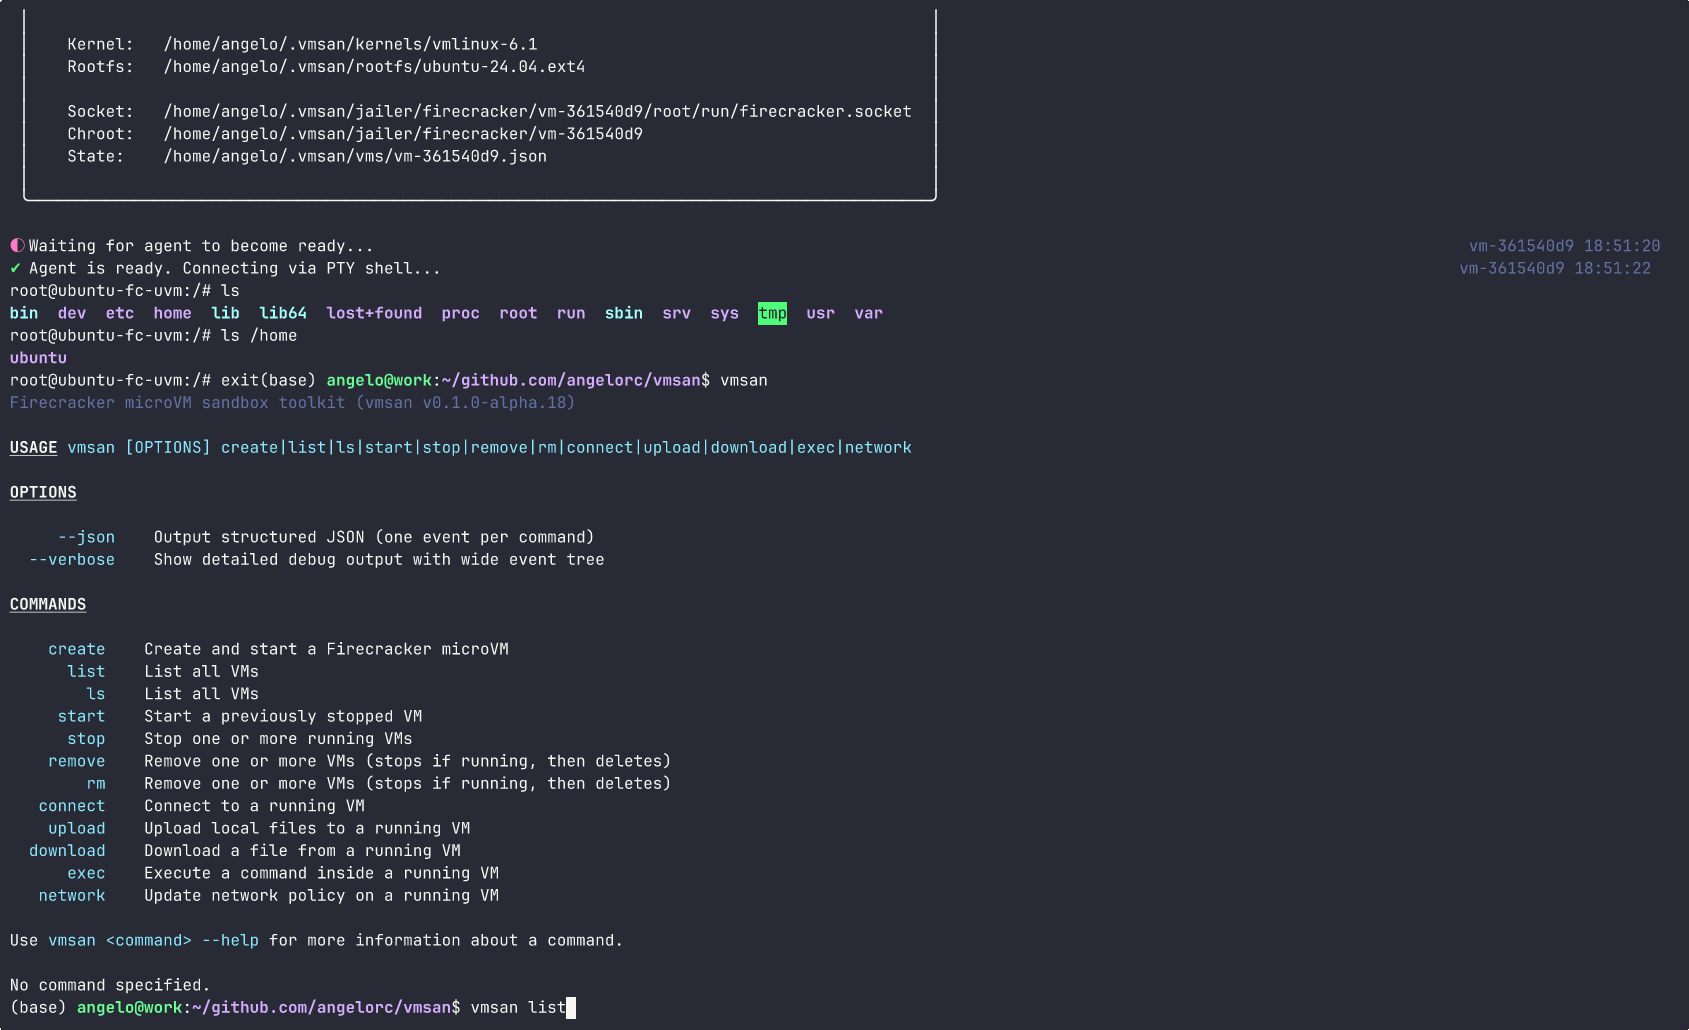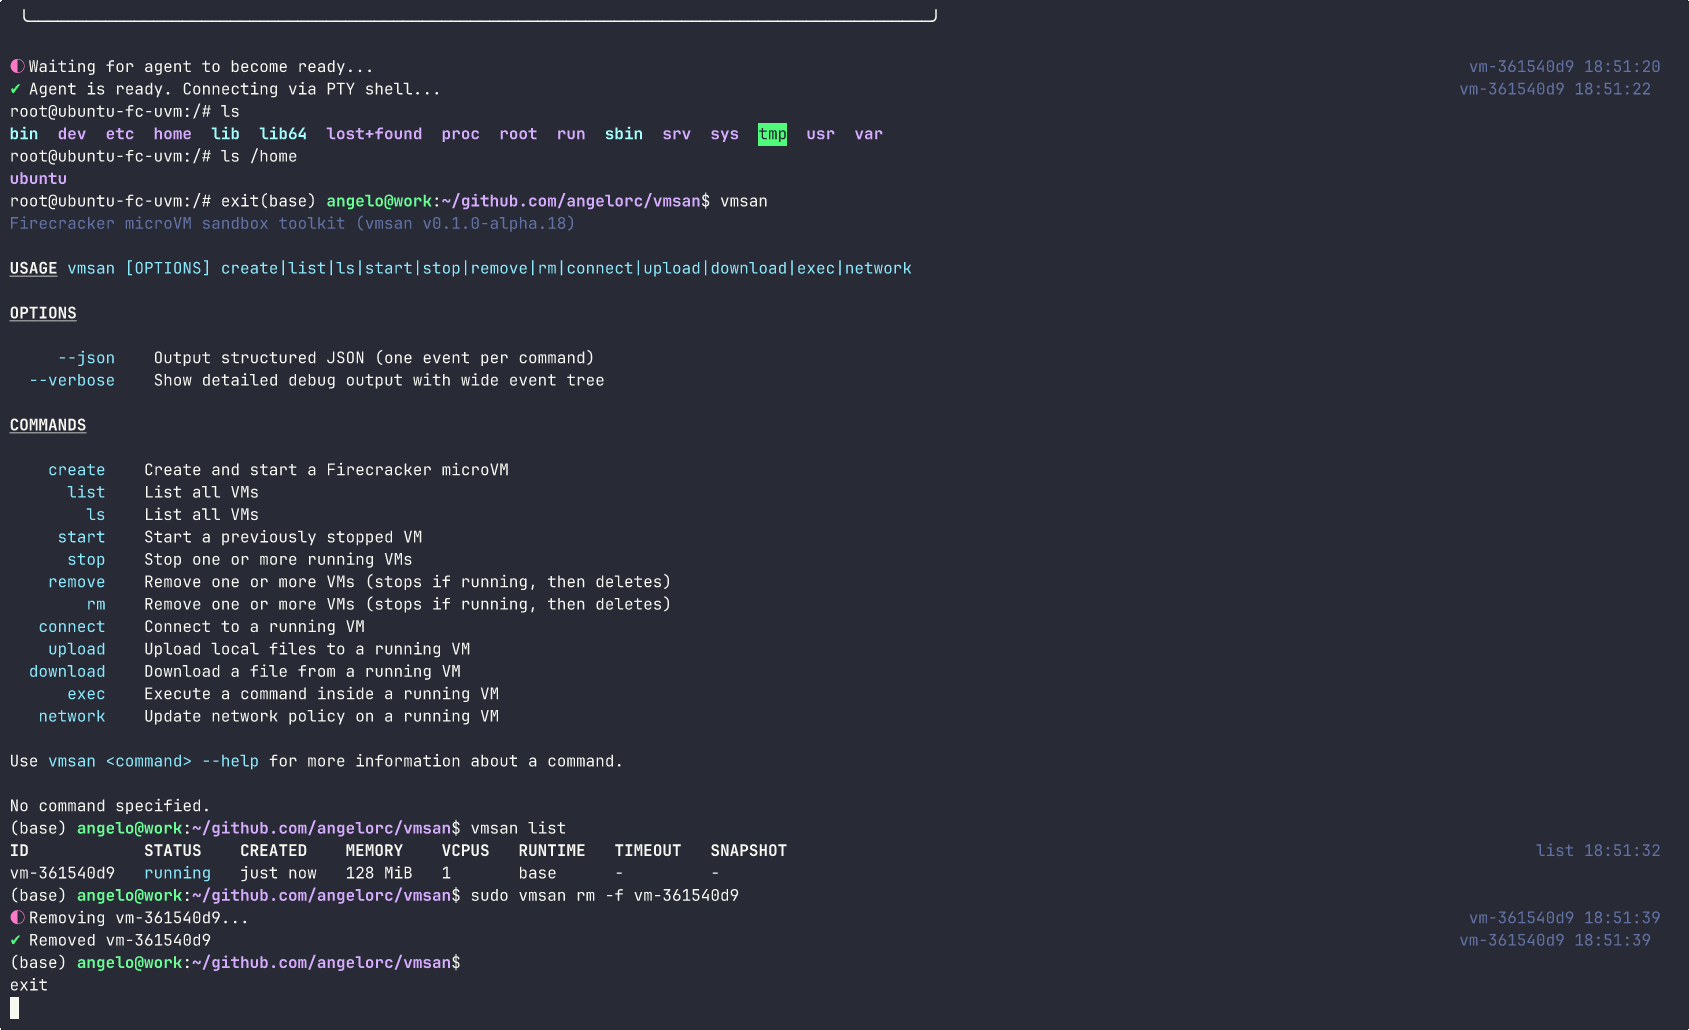 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
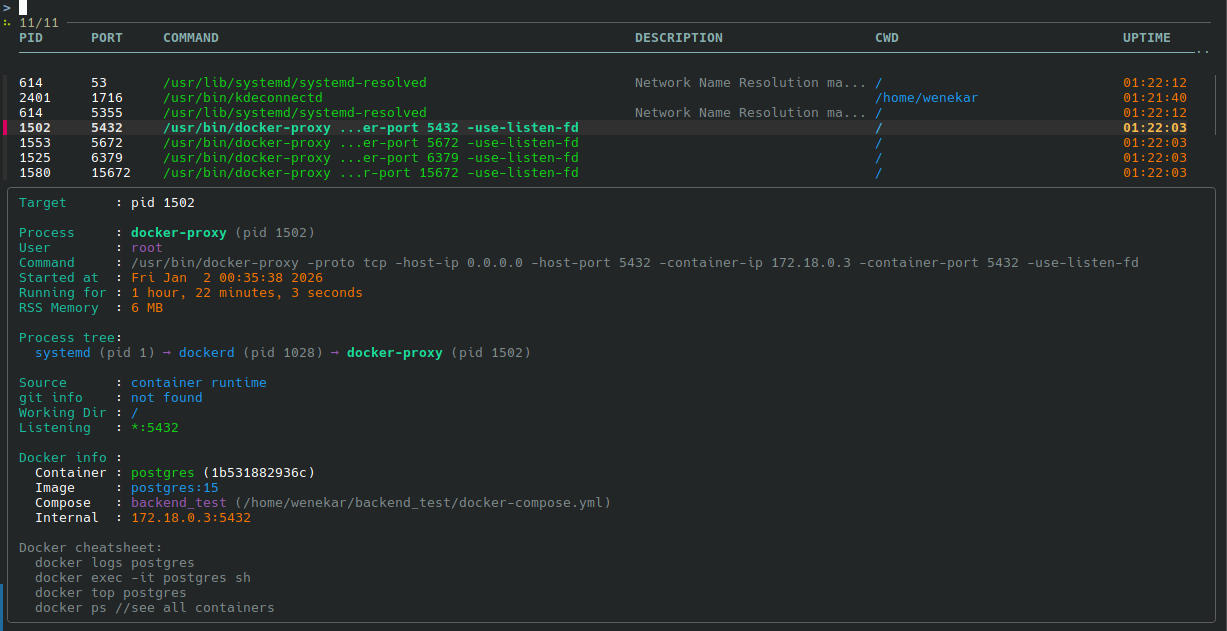 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
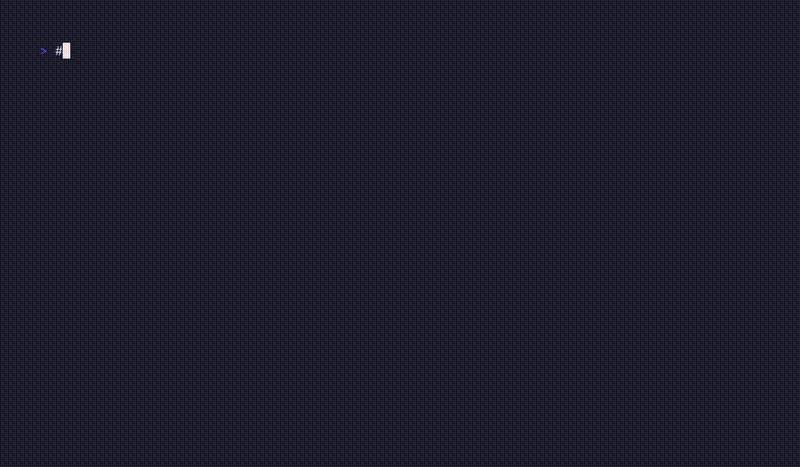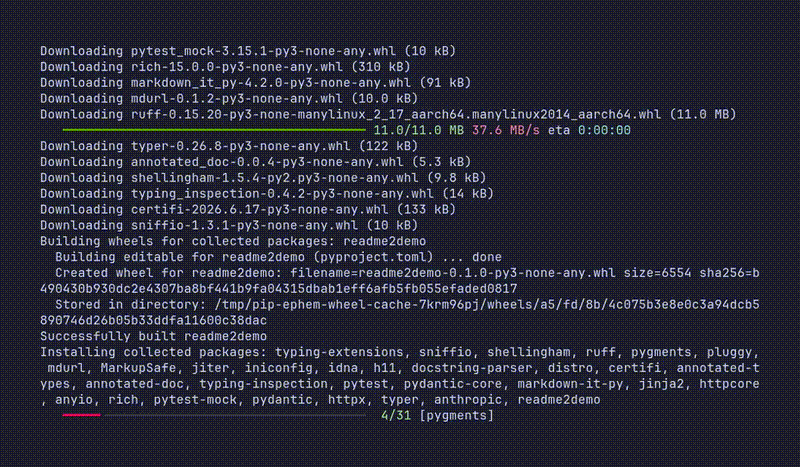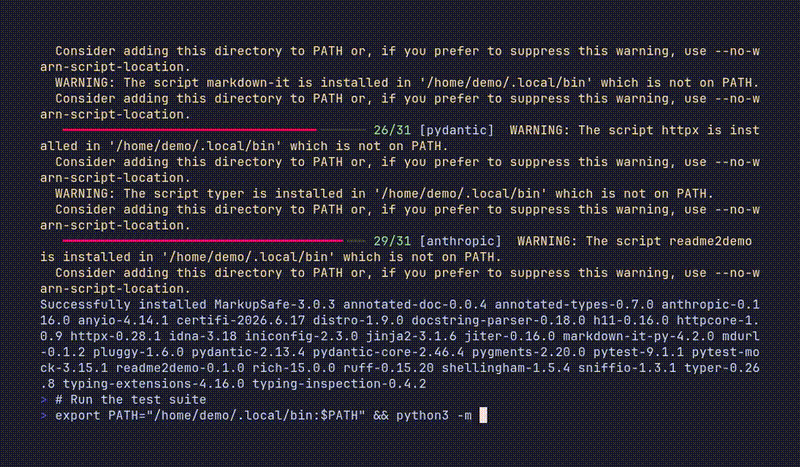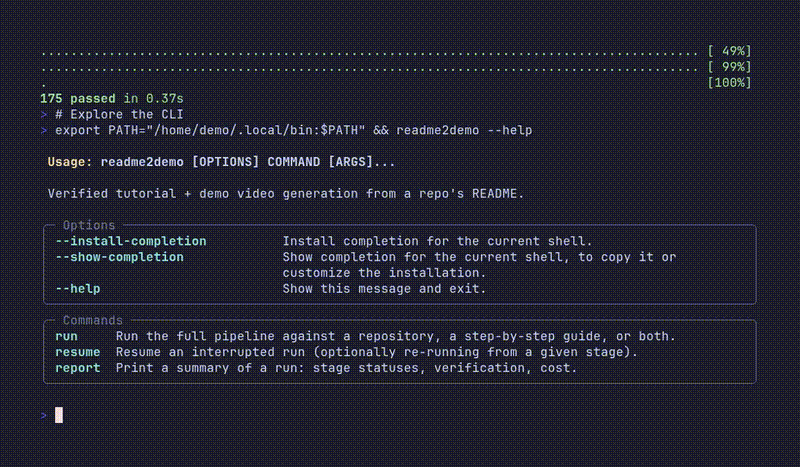 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
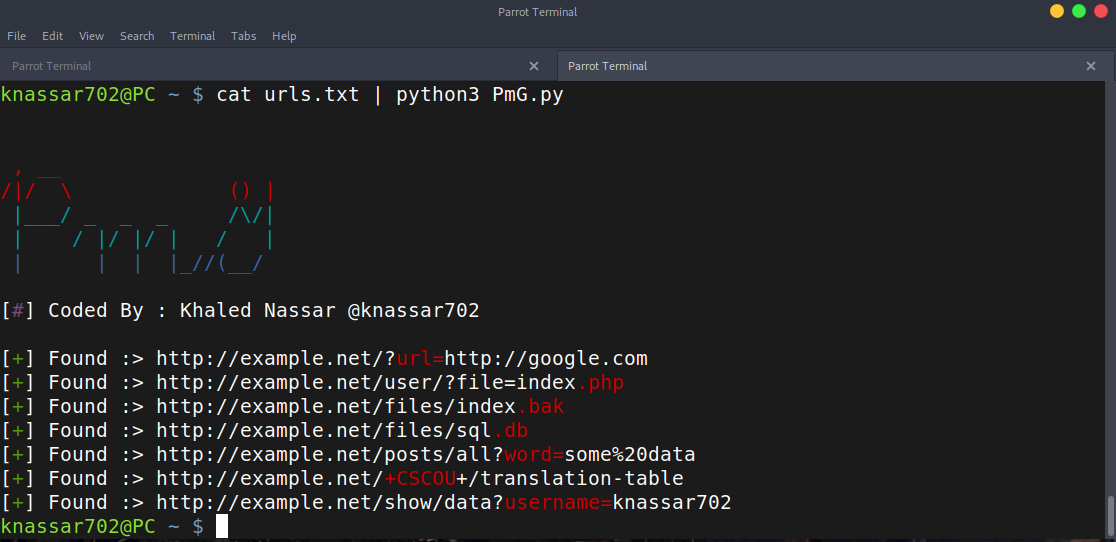 mindpatch/pmg
Extract parameters/paths from urls
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…
 iioch/ban-exploitable-bitcoin-nodes
Ban all denial-of-service vulnerability exploitable nodes from your node CVE-2018-17144
 elevenpaths/metashield-clean-up-sdk-python
Python SDK for removing hidden metadata from files (PDF, Office, images) to protect privacy and prevent data leakage via automated cleaning workflows.
 muyuanlove/cve-2024-6387fixshell
Automated bash script to patch CVE-2024-6387 by compiling and installing OpenSSH 9.8p1 from source on Debian/Ubuntu systems.
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 everest90909/yellowkey-winre-remediation
PowerShell-based Intune remediation package that detects and removes the vulnerable autofstx.exe BootExecute entry from offline WinRE images, then…
 datasurgeon-ds/ds-cve-plugin
A plugin for DataSurgeon that Extracts CVE Numbers From Text (e.g: CVE-2021-56789)