

scapy
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
bluetooth-securitycryptographydata-exfiltration+23
12.5k
secdev/scapyPython-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 shoucheng3/jlangch__venice_cve-2022-36007_1-10-16
Sandboxed Lisp dialect for the JVM with immutable data structures, macros, and over 900 core functions. Ideal for safe scripting, automation, and…
 a-real-virus/stealthcrypter
AES-256 file and directory encryption tool with interactive CLI, progress bar, and optional secure deletion of originals. Supports large files and…
 screetsec/imr0t
imR0T: Send a quick message with simple text encryption to your whatsapp contact and protect your text by encrypting and decrypting, basically in…
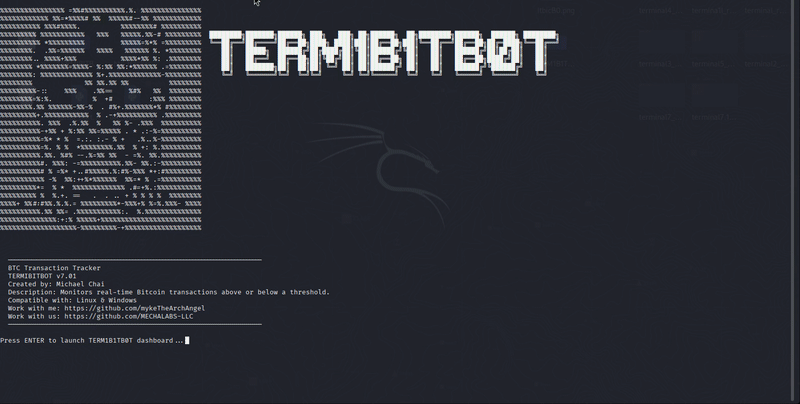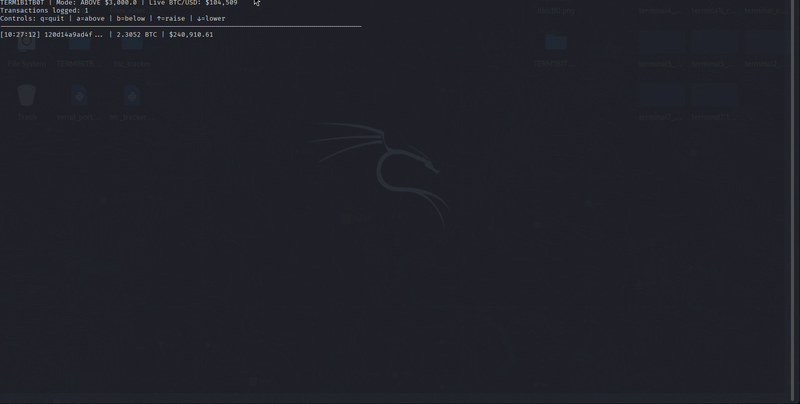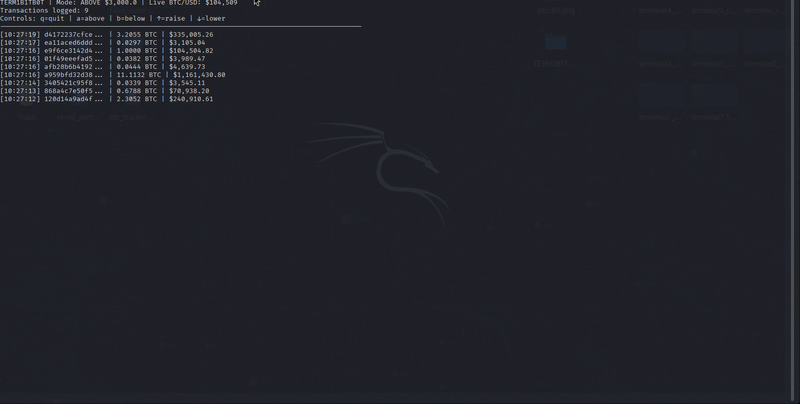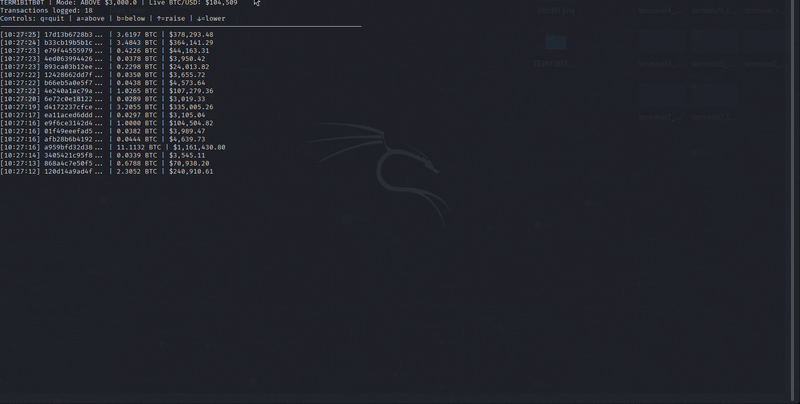 mykethearchangel/term1b1tb0t
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
 mbhudson/cve-2020-1971
CVE-2020-1971 Auto Scan & Remote Exploit Script. Auto Local Scan & Patch Script.
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 stevemcilwain/quiver
Quiver is the tool to manage all of your tools for bug bounty hunting and penetration testing.
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 seguridadentrerios/cve-2026-33829
Automated Bash script to passively audit Windows assets for CVE-2026-33829 search: protocol handler vulnerability using tcpdump and SMB connection…
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 sbaresearch/stop-zenbleed-win
PowerShell script to apply Zenbleed (CVE-2023-20593) MSR workaround on Windows
 call123x/-cve-2025-55182
cve-2025-55182
 yayateayayatea/cve-2017-8917
python script to exploit Joomla 3.7
 shoucheng3/apache__uima-uimaj_cve-2022-32287_3-3-0
Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.