

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 bishopfox/sliver
Adversary Emulation Framework
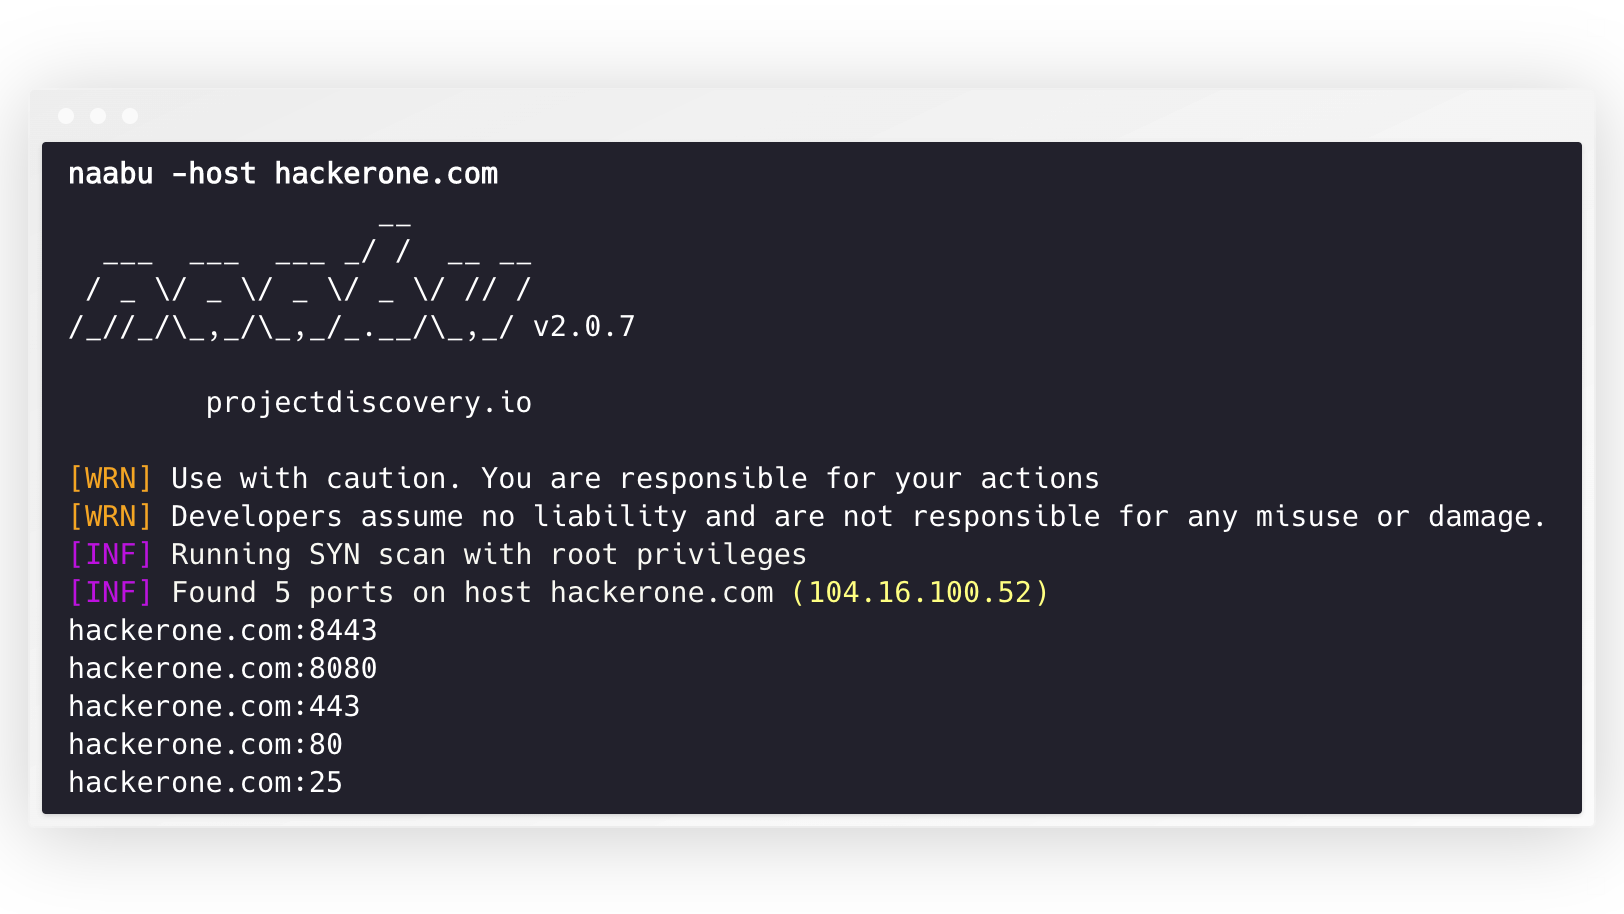 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 abhishekghosh/freak-attack-cve-2015-0204-testing-script
Basic BASH Script to Automate OpenSSL based testing for FREAK Attack (CVE-2015-0204) as advised by Akamai.
 masjohncook/netsec-project
Script of Network Security Project - Attack on CVE-2021-22555
 psycostea/pi-zero-2w-bad-usb
Configure your Pi Zero 2W to be a BadUSB
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
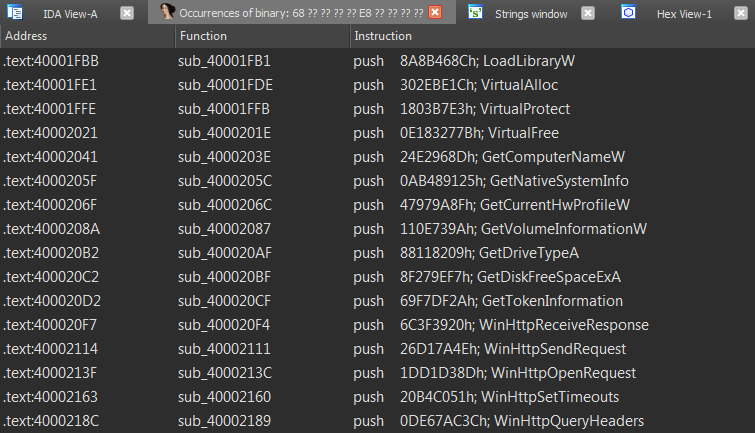 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 goncalopolido/overload
A network stress testing tool for simulating high traffic loads.
 threatexpress/threatbox
Ansible-based attack platform for deploying and managing a standardized Linux penetration testing environment with automated tool installation,…
 withsecurelabs/shadowhammer
Batch-mode checker for Shadowhammer malware indicators, scanning local or provided MAC addresses against known malicious hashes, with offline support…

 lucthienphong1120/full-60-ddos-tools
Collection of 60 Python-based DDoS attack tools for network stress testing and security assessment, featuring automated packet flooding scripts to…
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
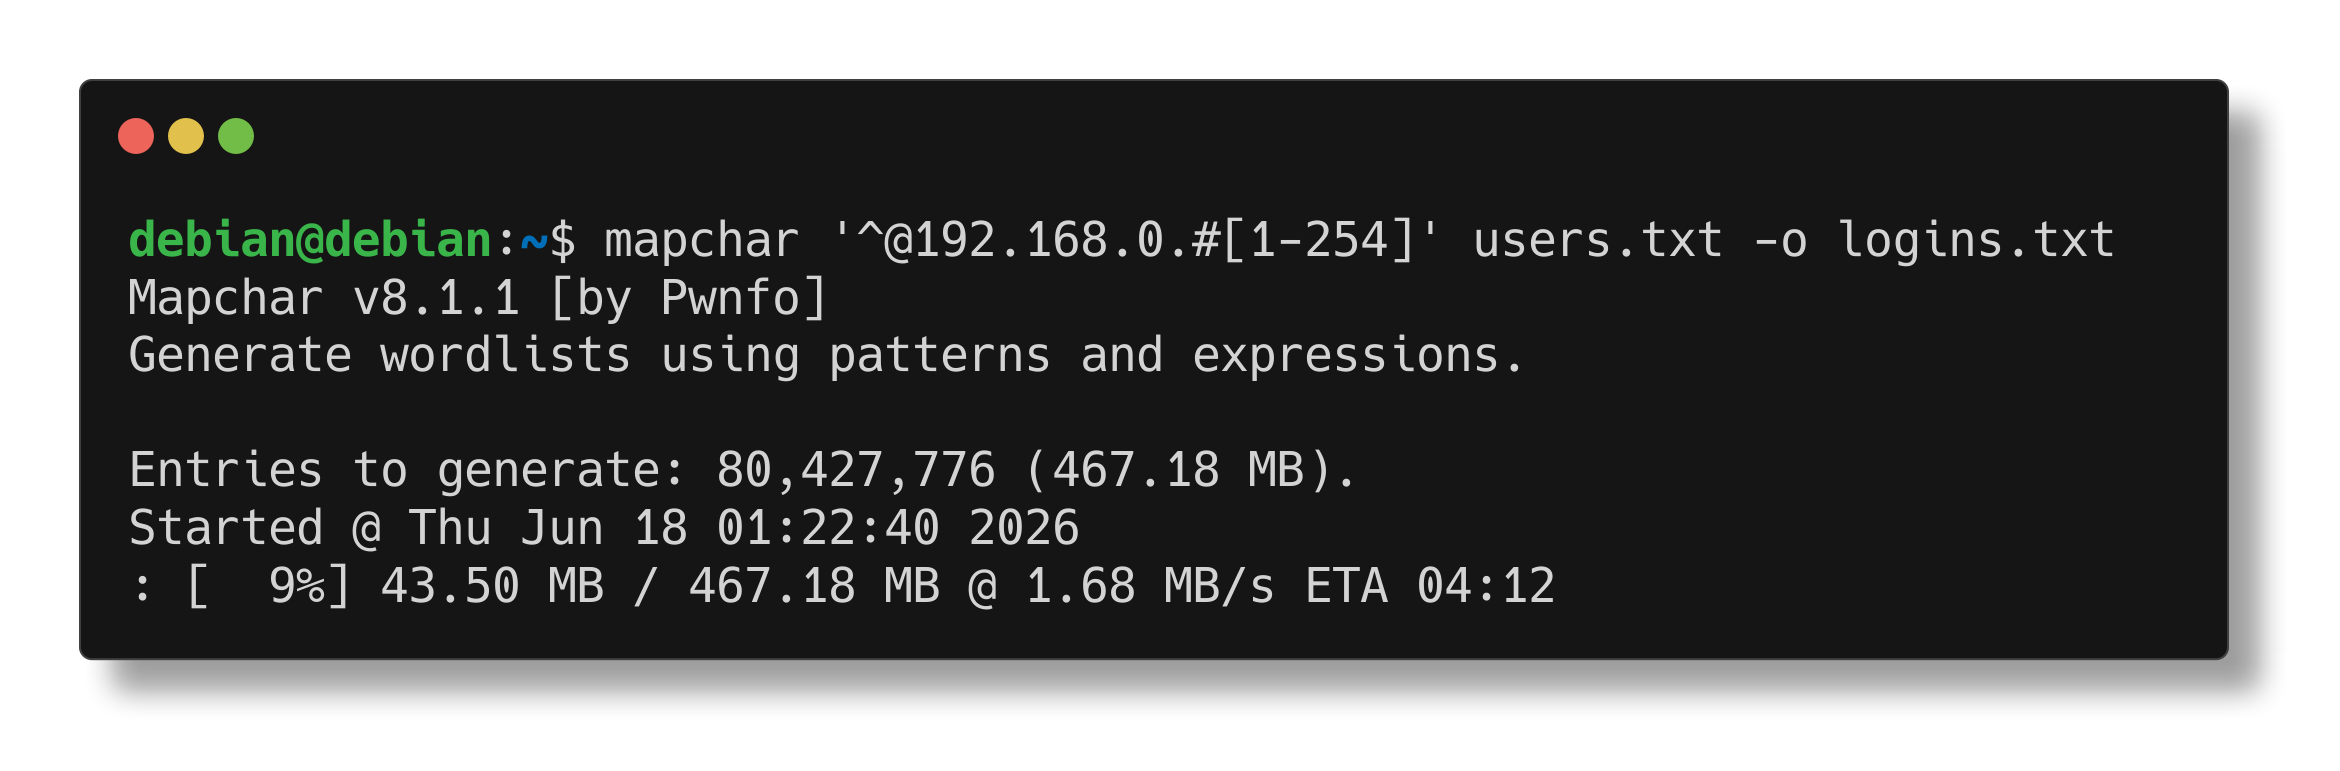 pwnfo/mapchar
Generate wordlists using pattern logic and expressions.