
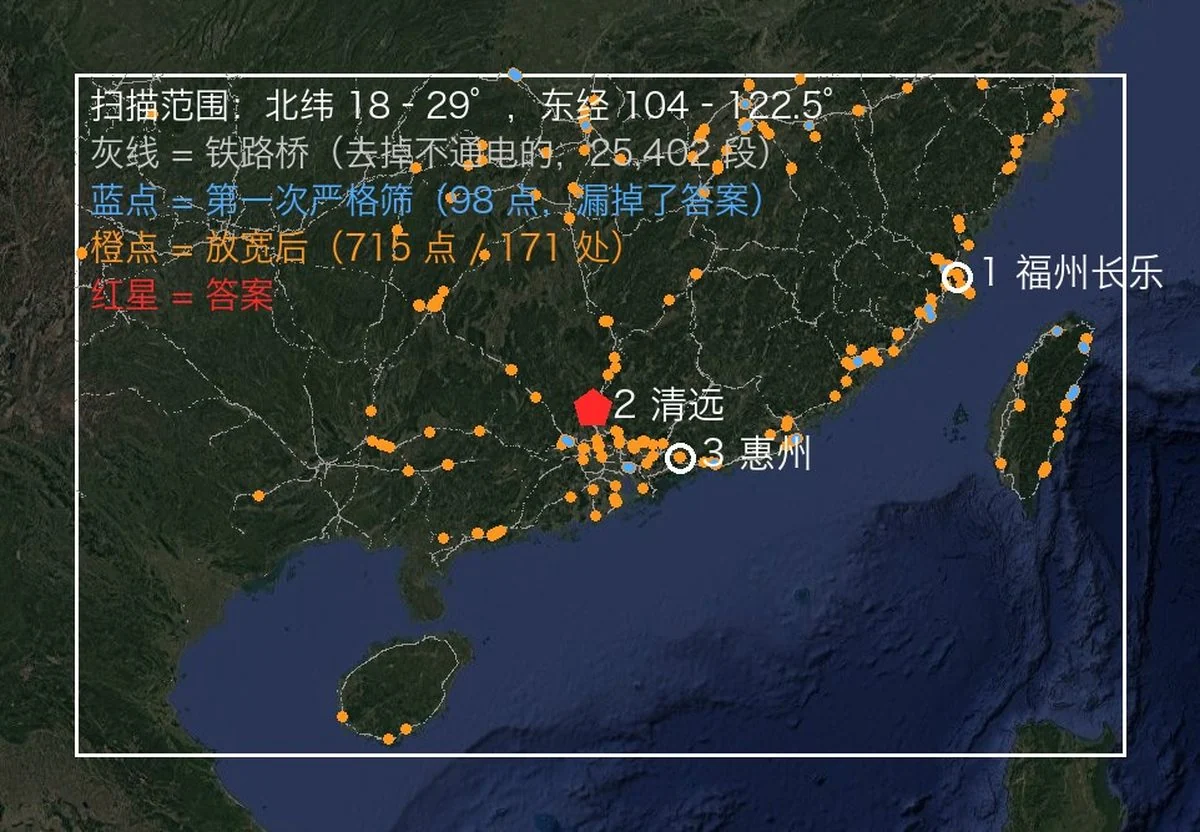
geo-sleuth
 oldcircle/geo-sleuth
An agent skill that finds where a photo was taken — OpenStreetMap geometry, elevation skylines, satellite imagery and street view — and shows its…
ai-securityinformation-gatheringosint+4
5.2k
oldcircle/geo-sleuthAn agent skill that finds where a photo was taken — OpenStreetMap geometry, elevation skylines, satellite imagery and street view — and shows its…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 840+ social media identities across the web
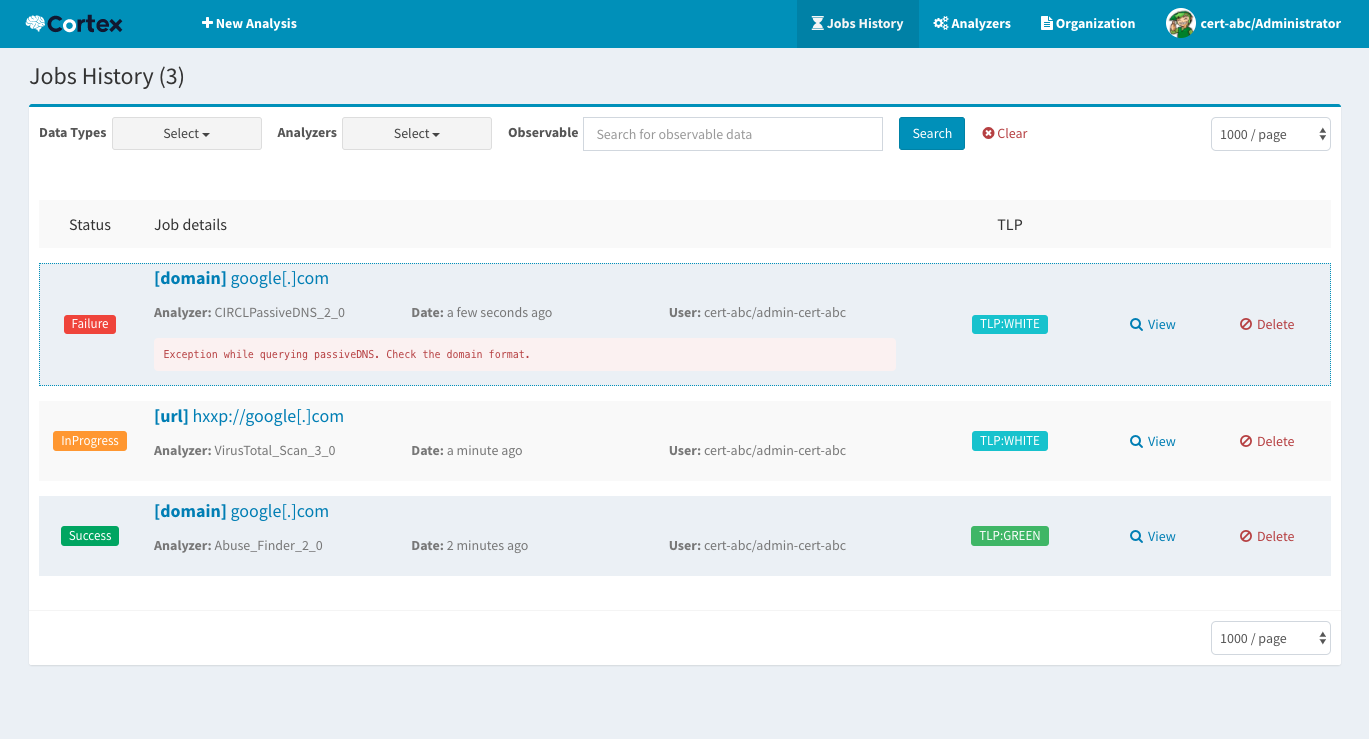 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 kevincrrl/evillimiter-ng
EvilLimiter Next Generation: monitor, analyze and limit the bandwidth
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 vulncheck-oss/cli
VulnCheck's official command line tool
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 jarryshaw/darc
Darkweb crawler that uses requests and Selenium workers to fetch pages, capture headers and cookies, extract links, and save rendered screenshots for…
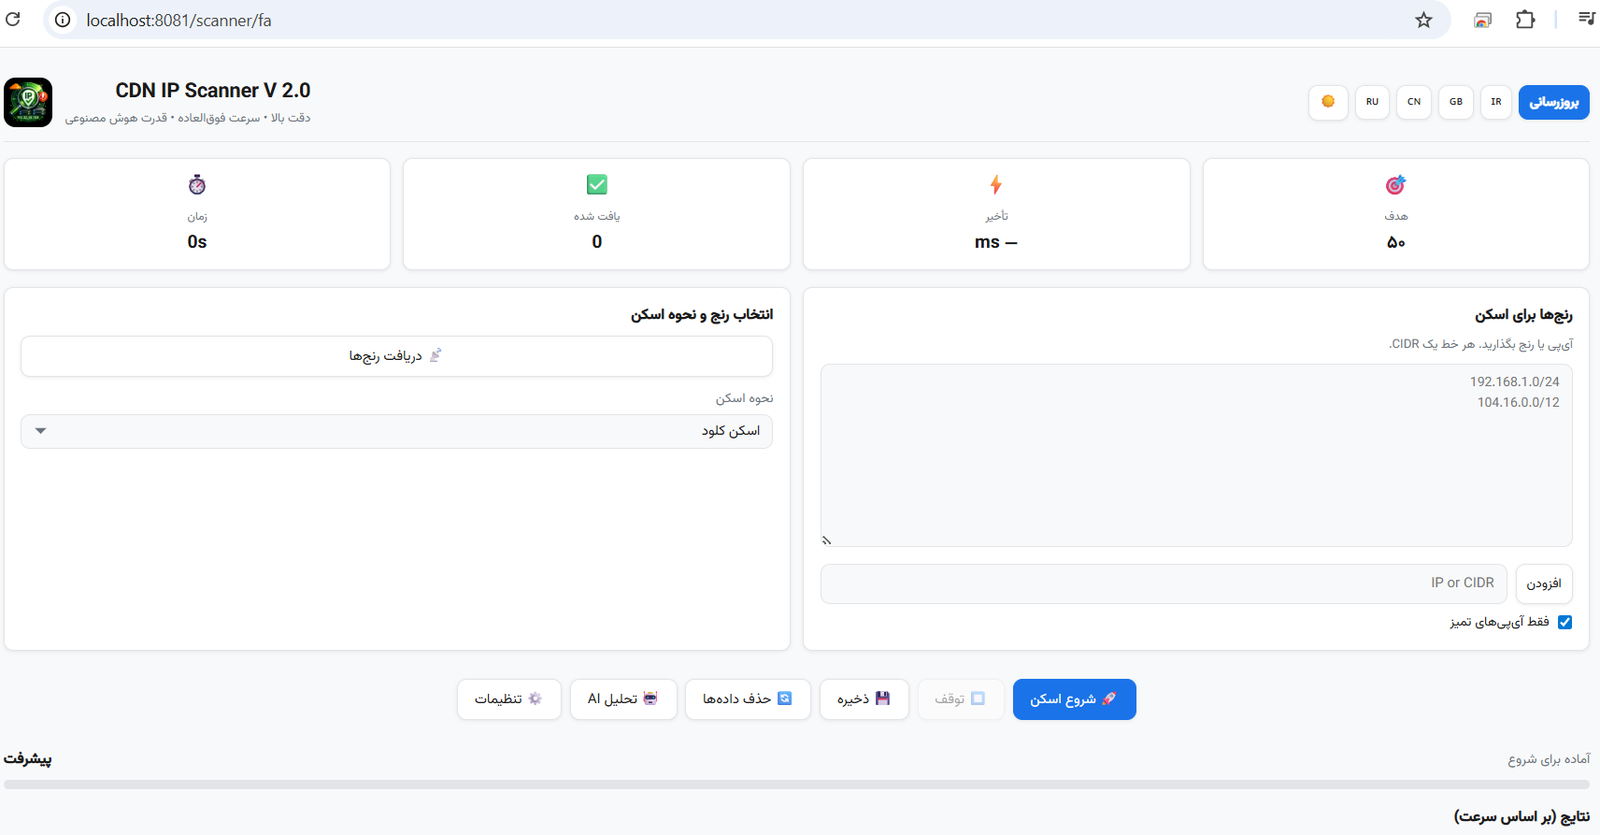 shahinst/cdn-ip-scanner
Web-based scanner that discovers fast, low-latency CDN IP addresses from Cloudflare, Fastly and other providers using multi-threaded 5-attempt…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.