
sandbox-agent
 rivet-dev/sandbox-agent
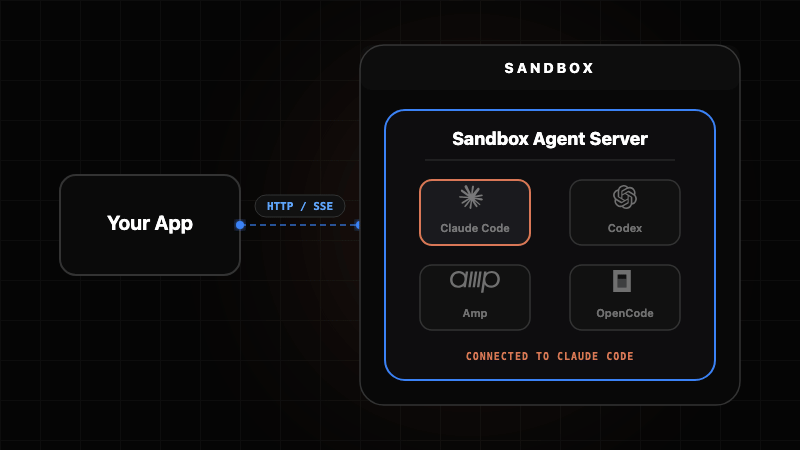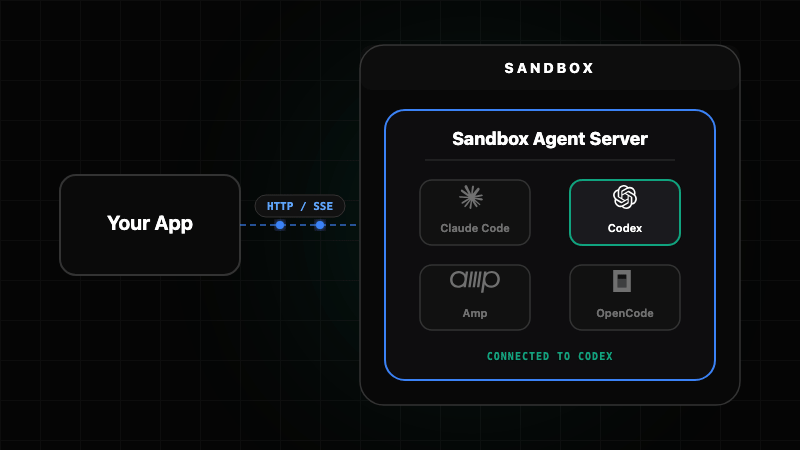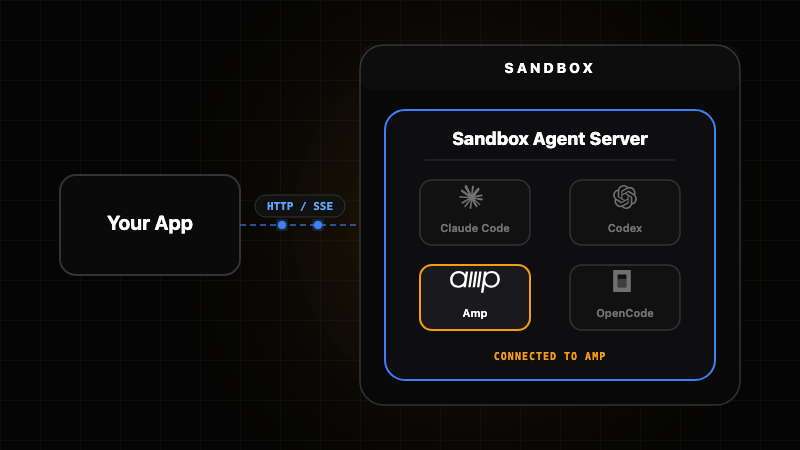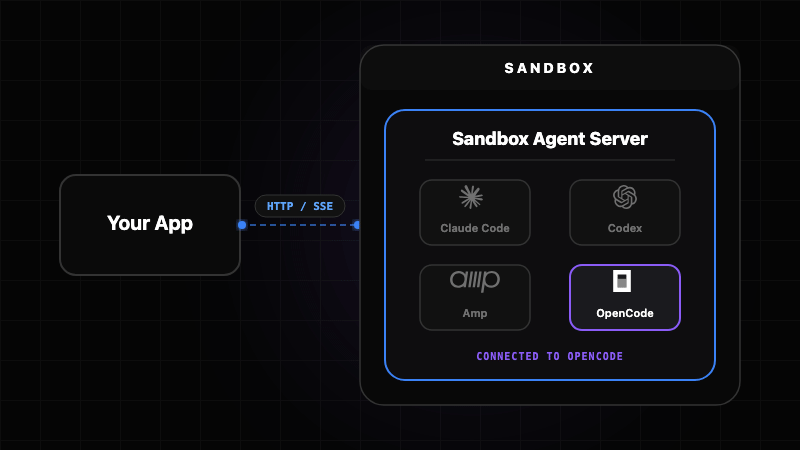
A durable process per agent, with memory that survives restarts
api-securitycontainer-securitydevsecops+3
1.6k1 day ago
rivet-dev/sandbox-agentA durable process per agent, with memory that survives restarts
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 m8sec/taser
Python resource library for creating security related tooling
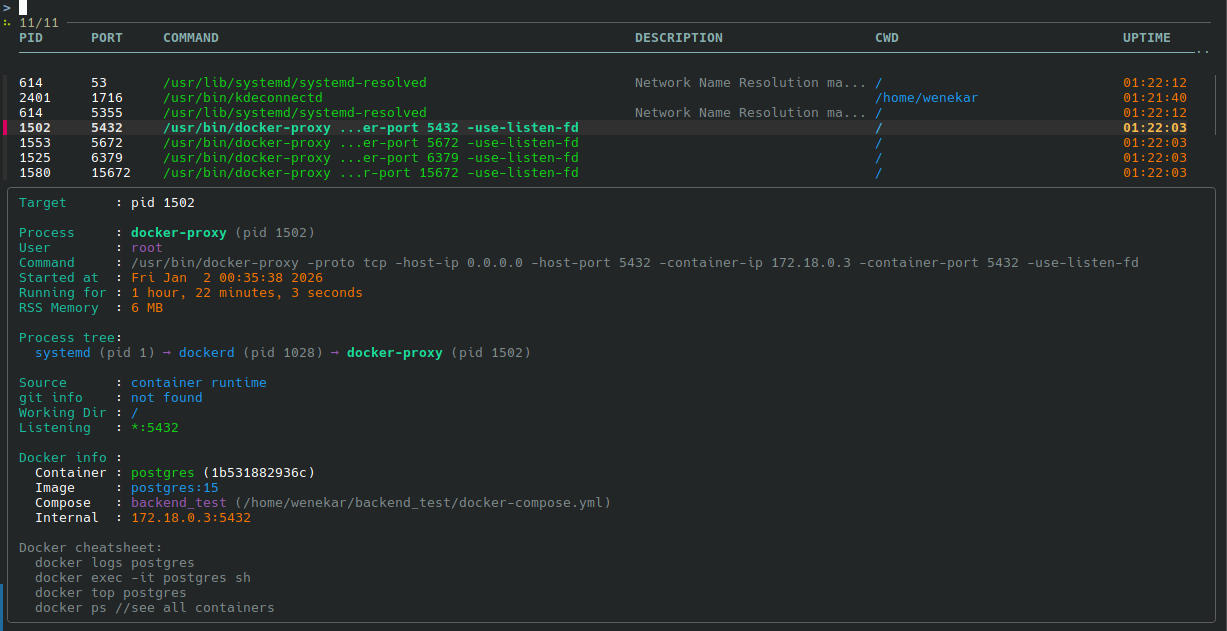 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 netspi/autodirbuster
Automatically run and save ffuf scans for multiple IPs
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 shoucheng3/apache__uima-uimaj_cve-2022-32287_3-3-0
Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
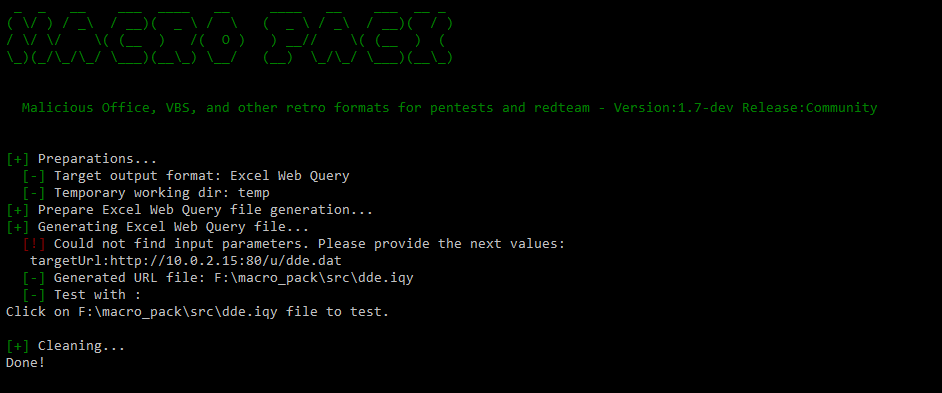 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
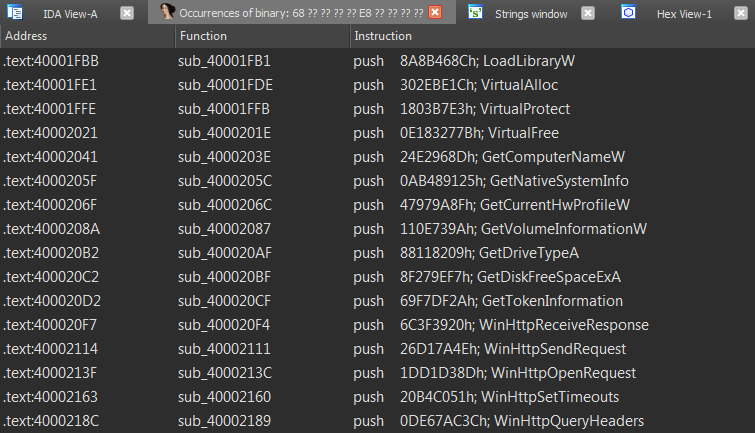 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 blacksnufkin/pwnbox-kali
Bash Script to automate the process of setting up a new Kali Linux virtual machine to look a like HTB PwnBox
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 ajtech-hue/cve-2021-3156-mitigation-shellscript-build
Shell script that monitors for a vulnerable sudo process and triggers authentication lockout to mitigate CVE-2021-3156.