

pySigma
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
defensive-toolsintrusion-detectionlog-analysis+2
59910h 49m ago
sigmahq/pysigmaPython library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
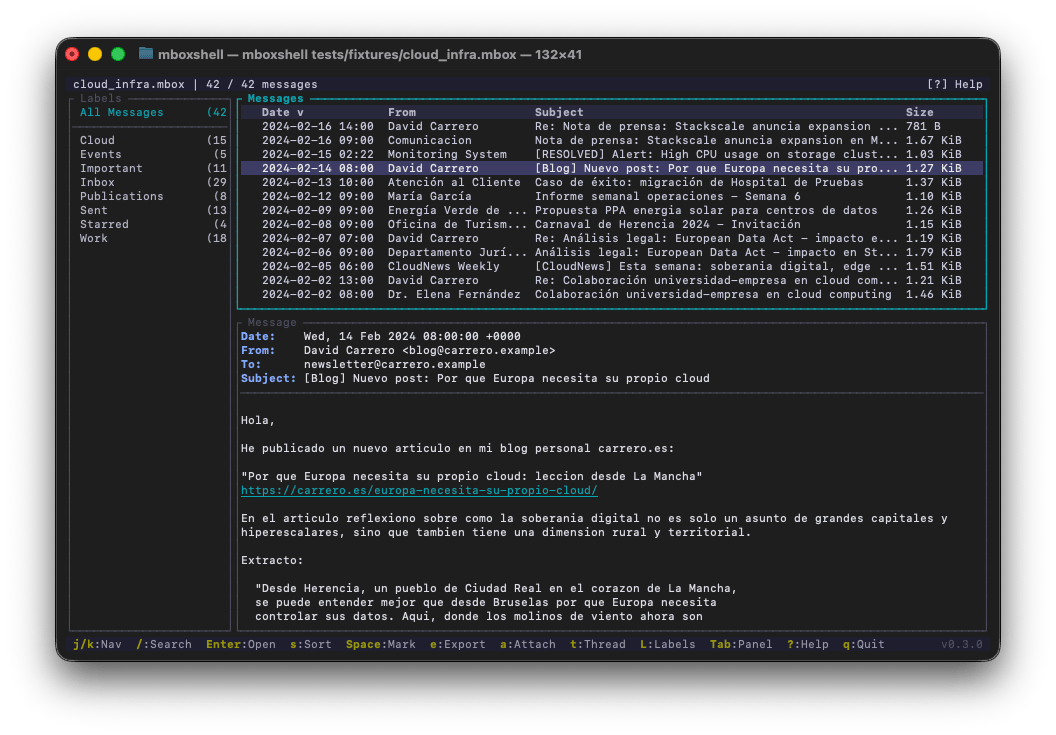 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
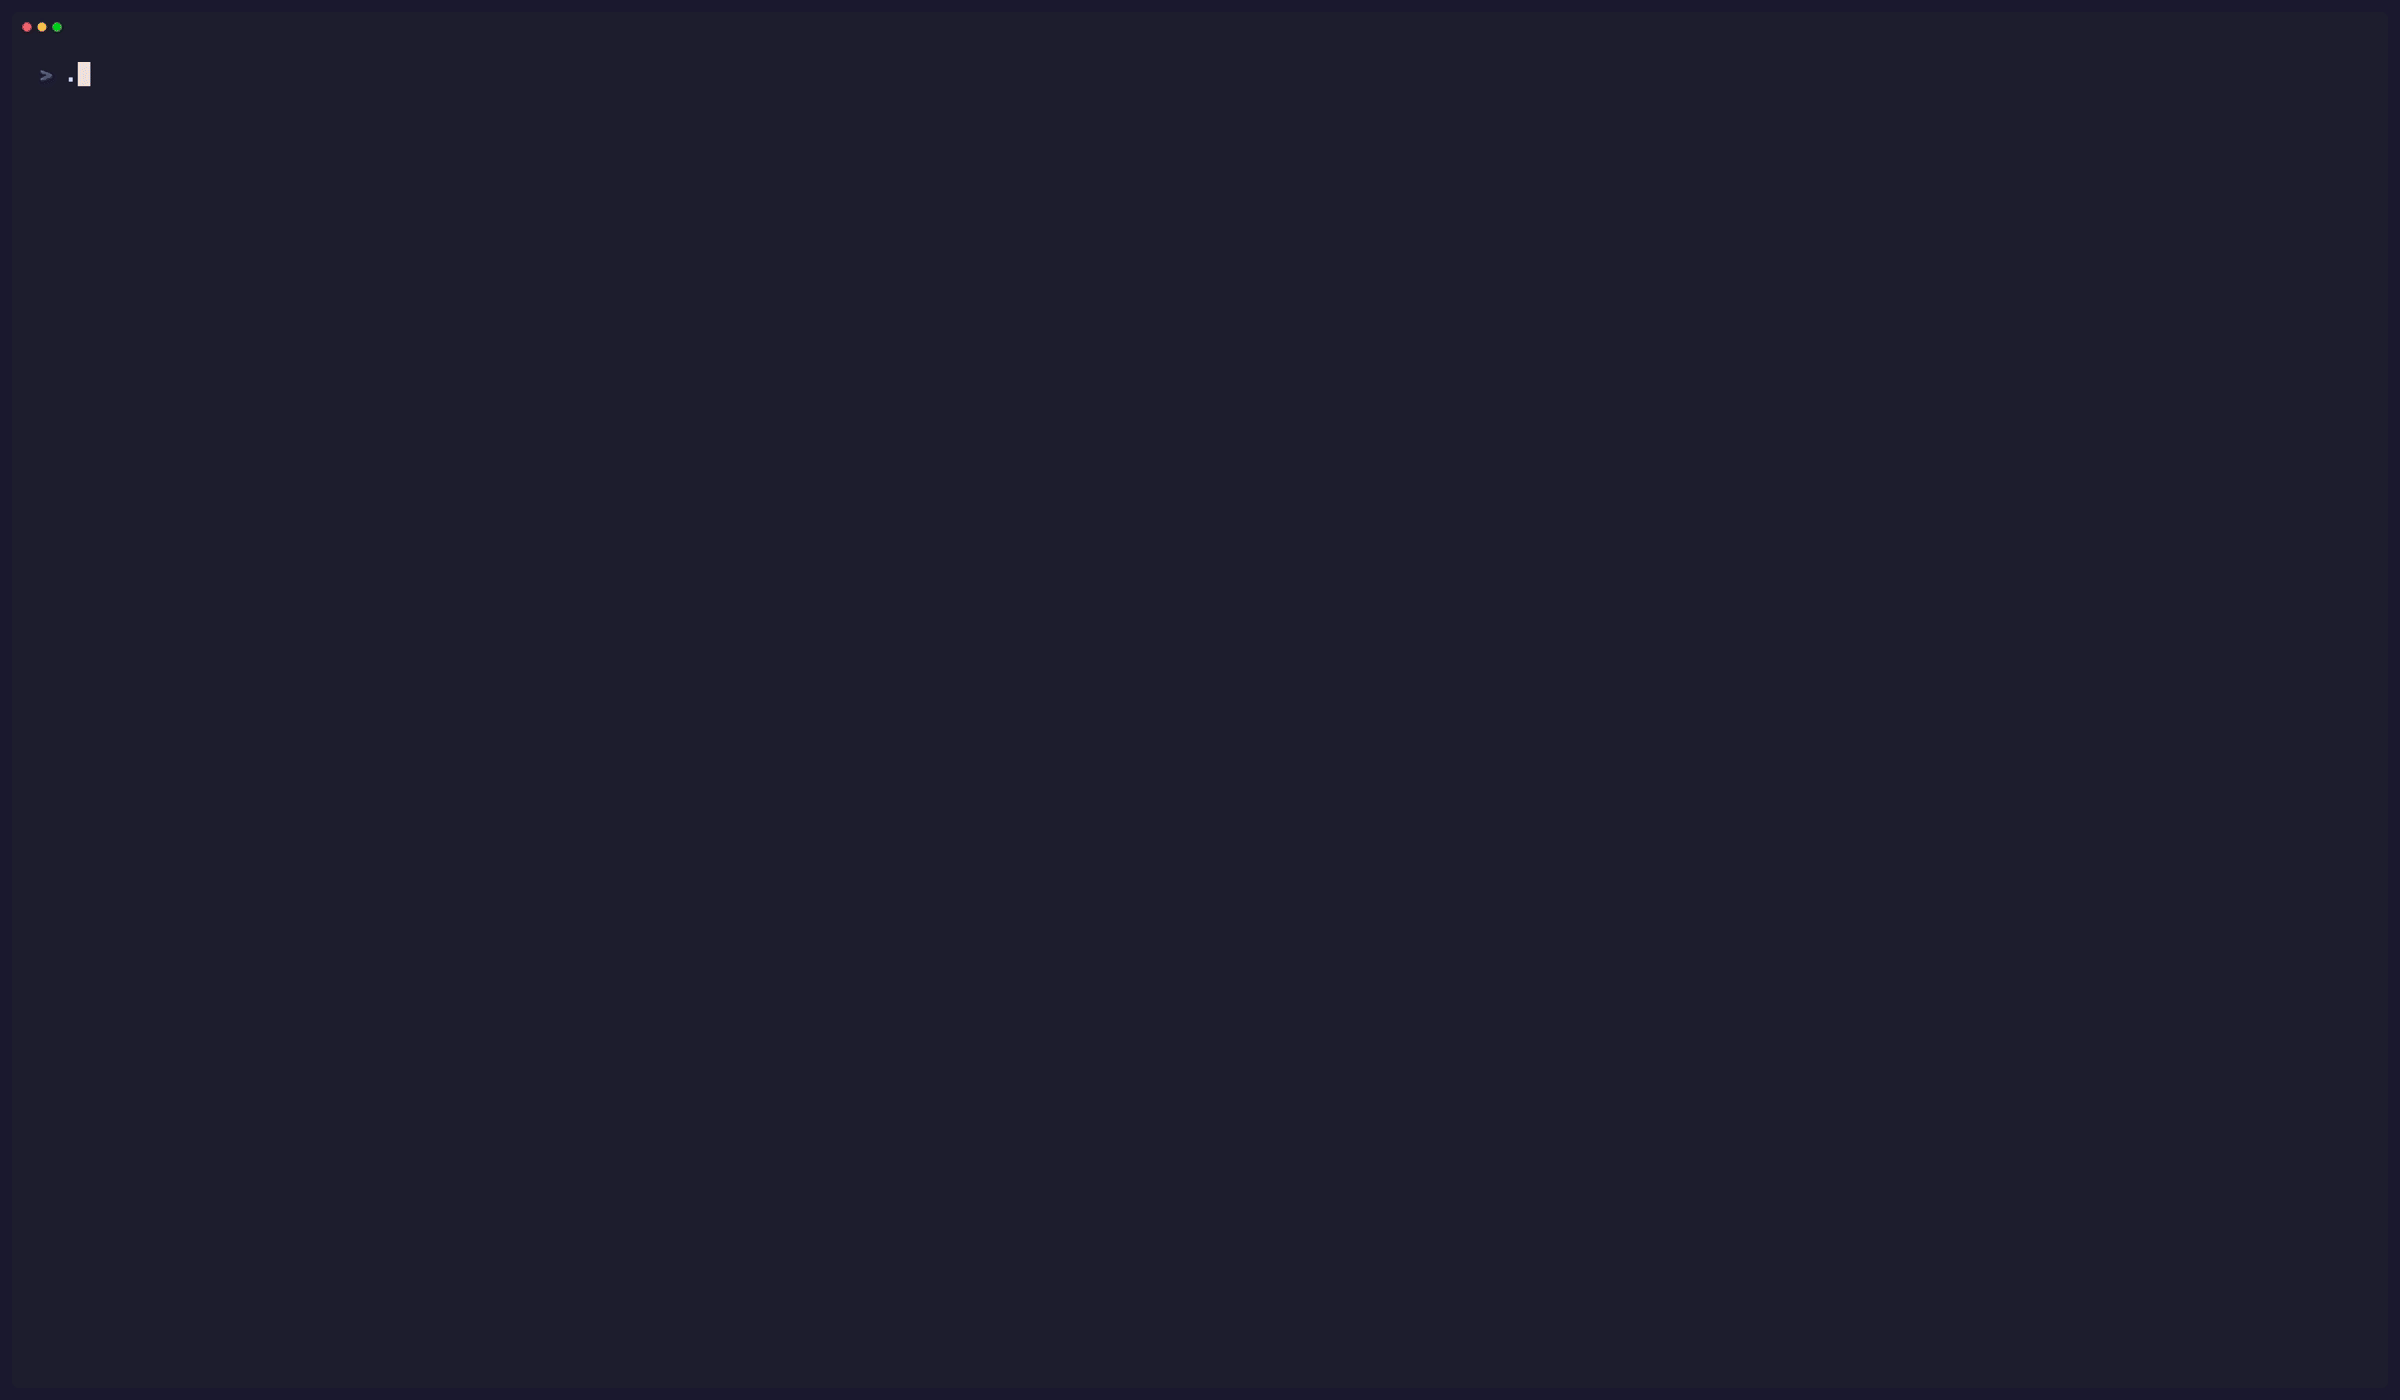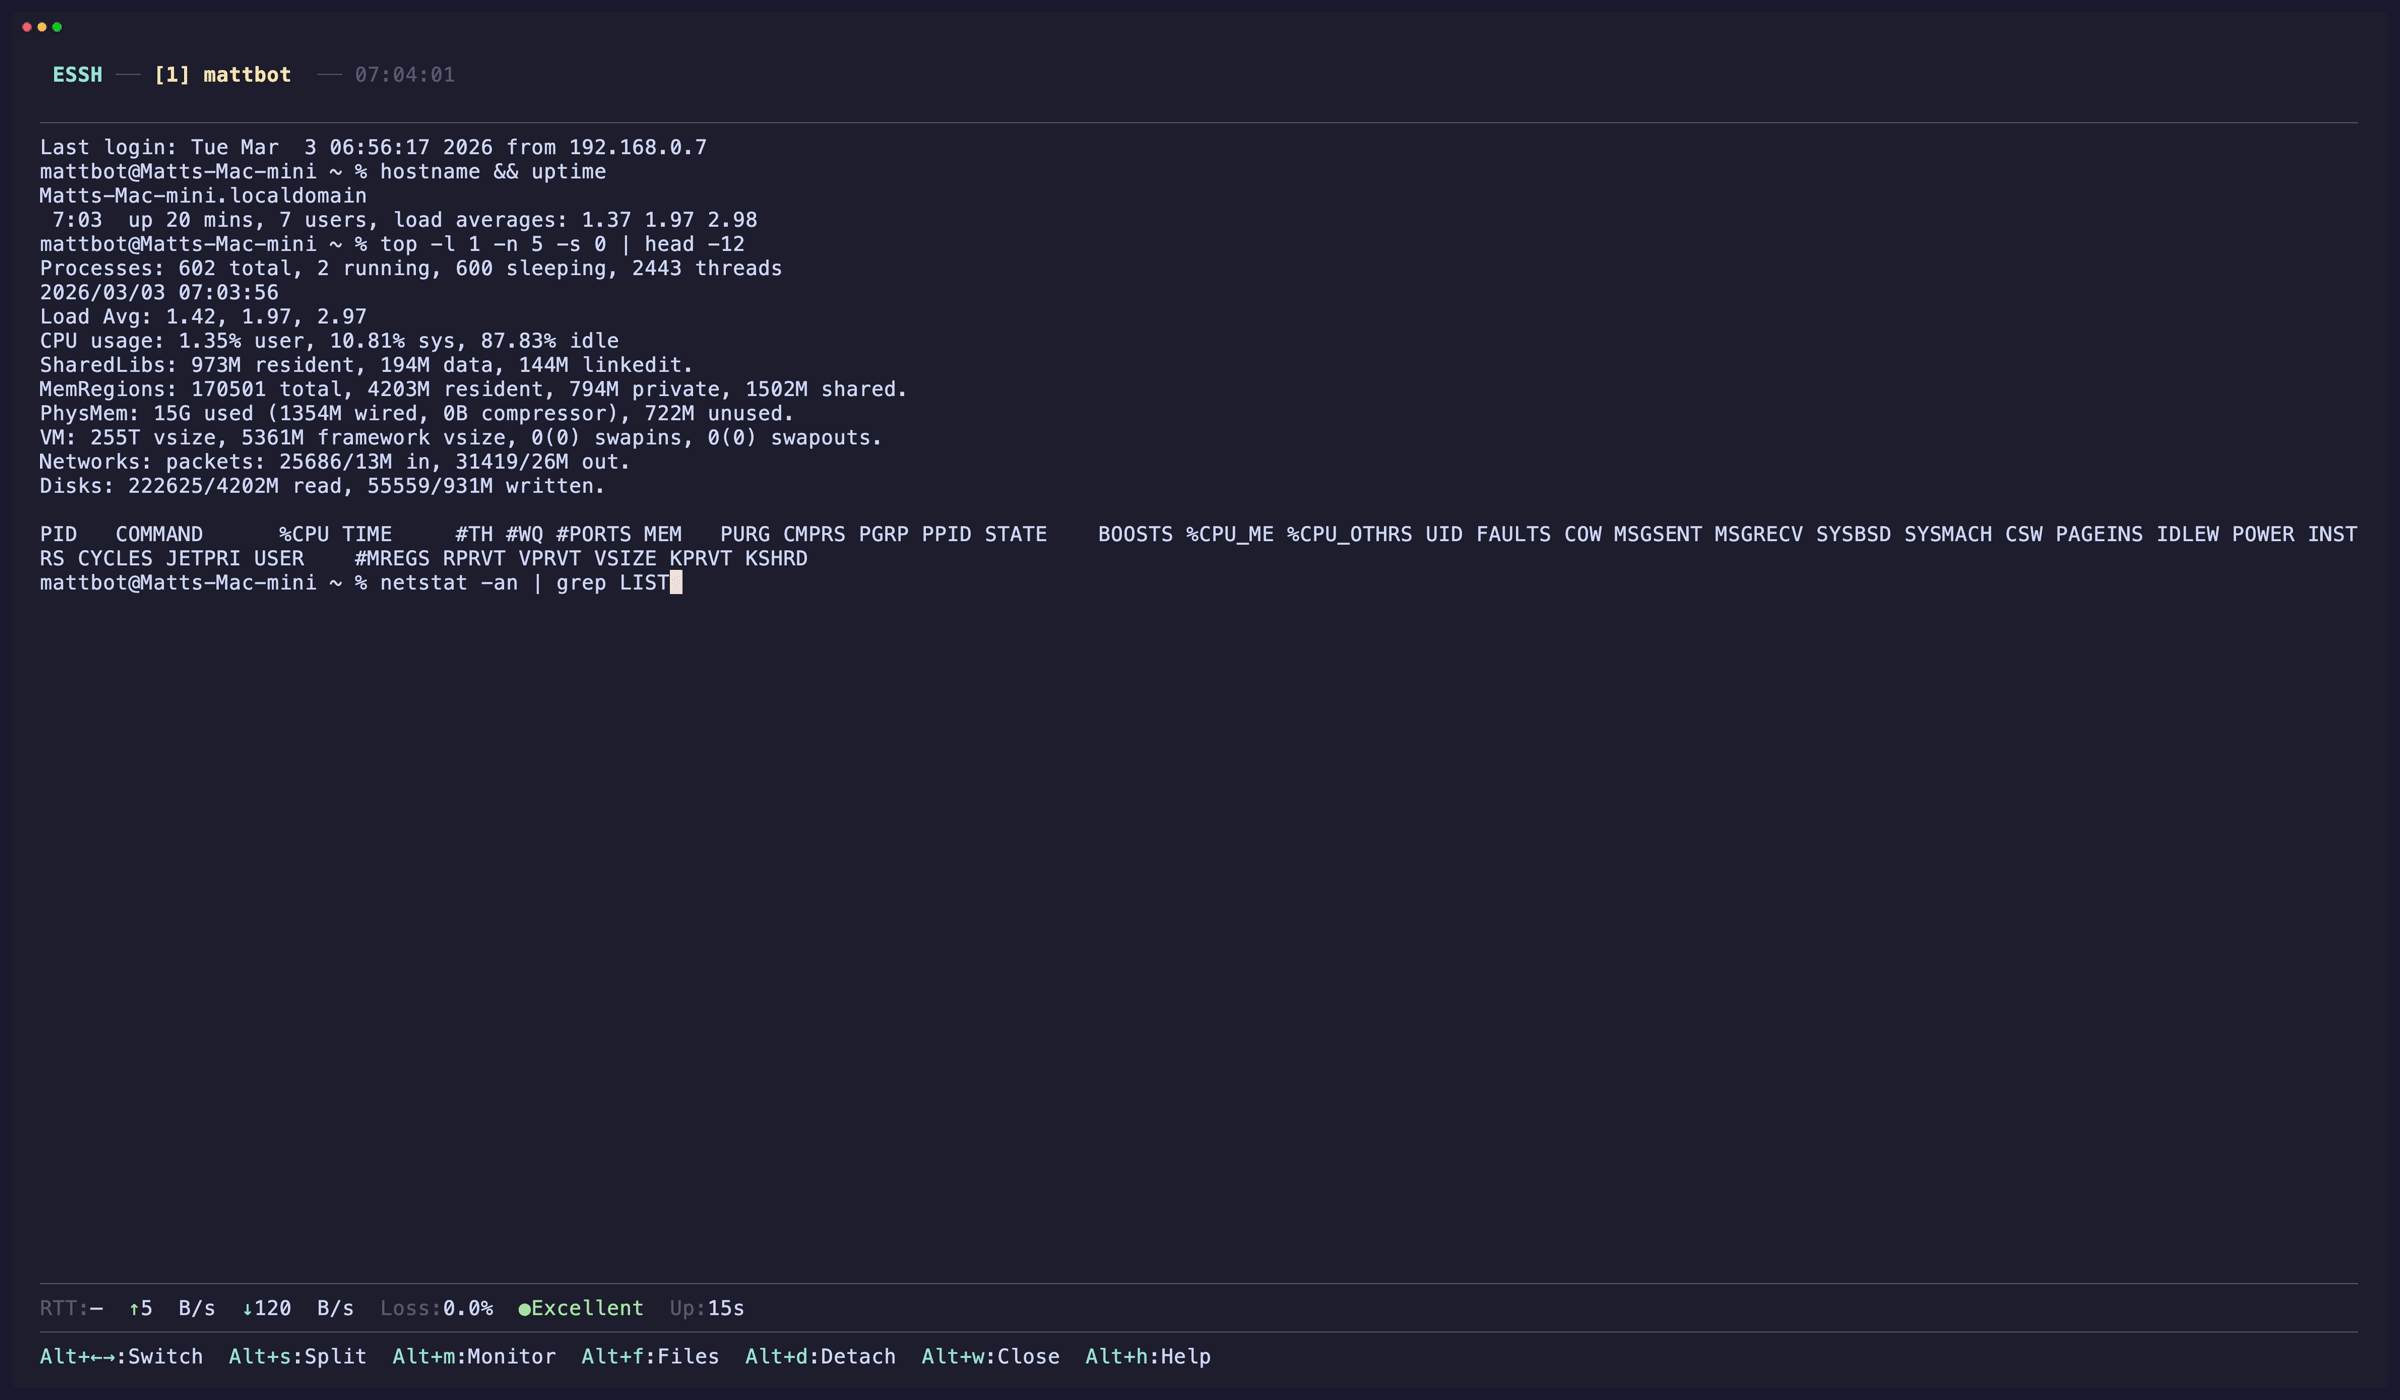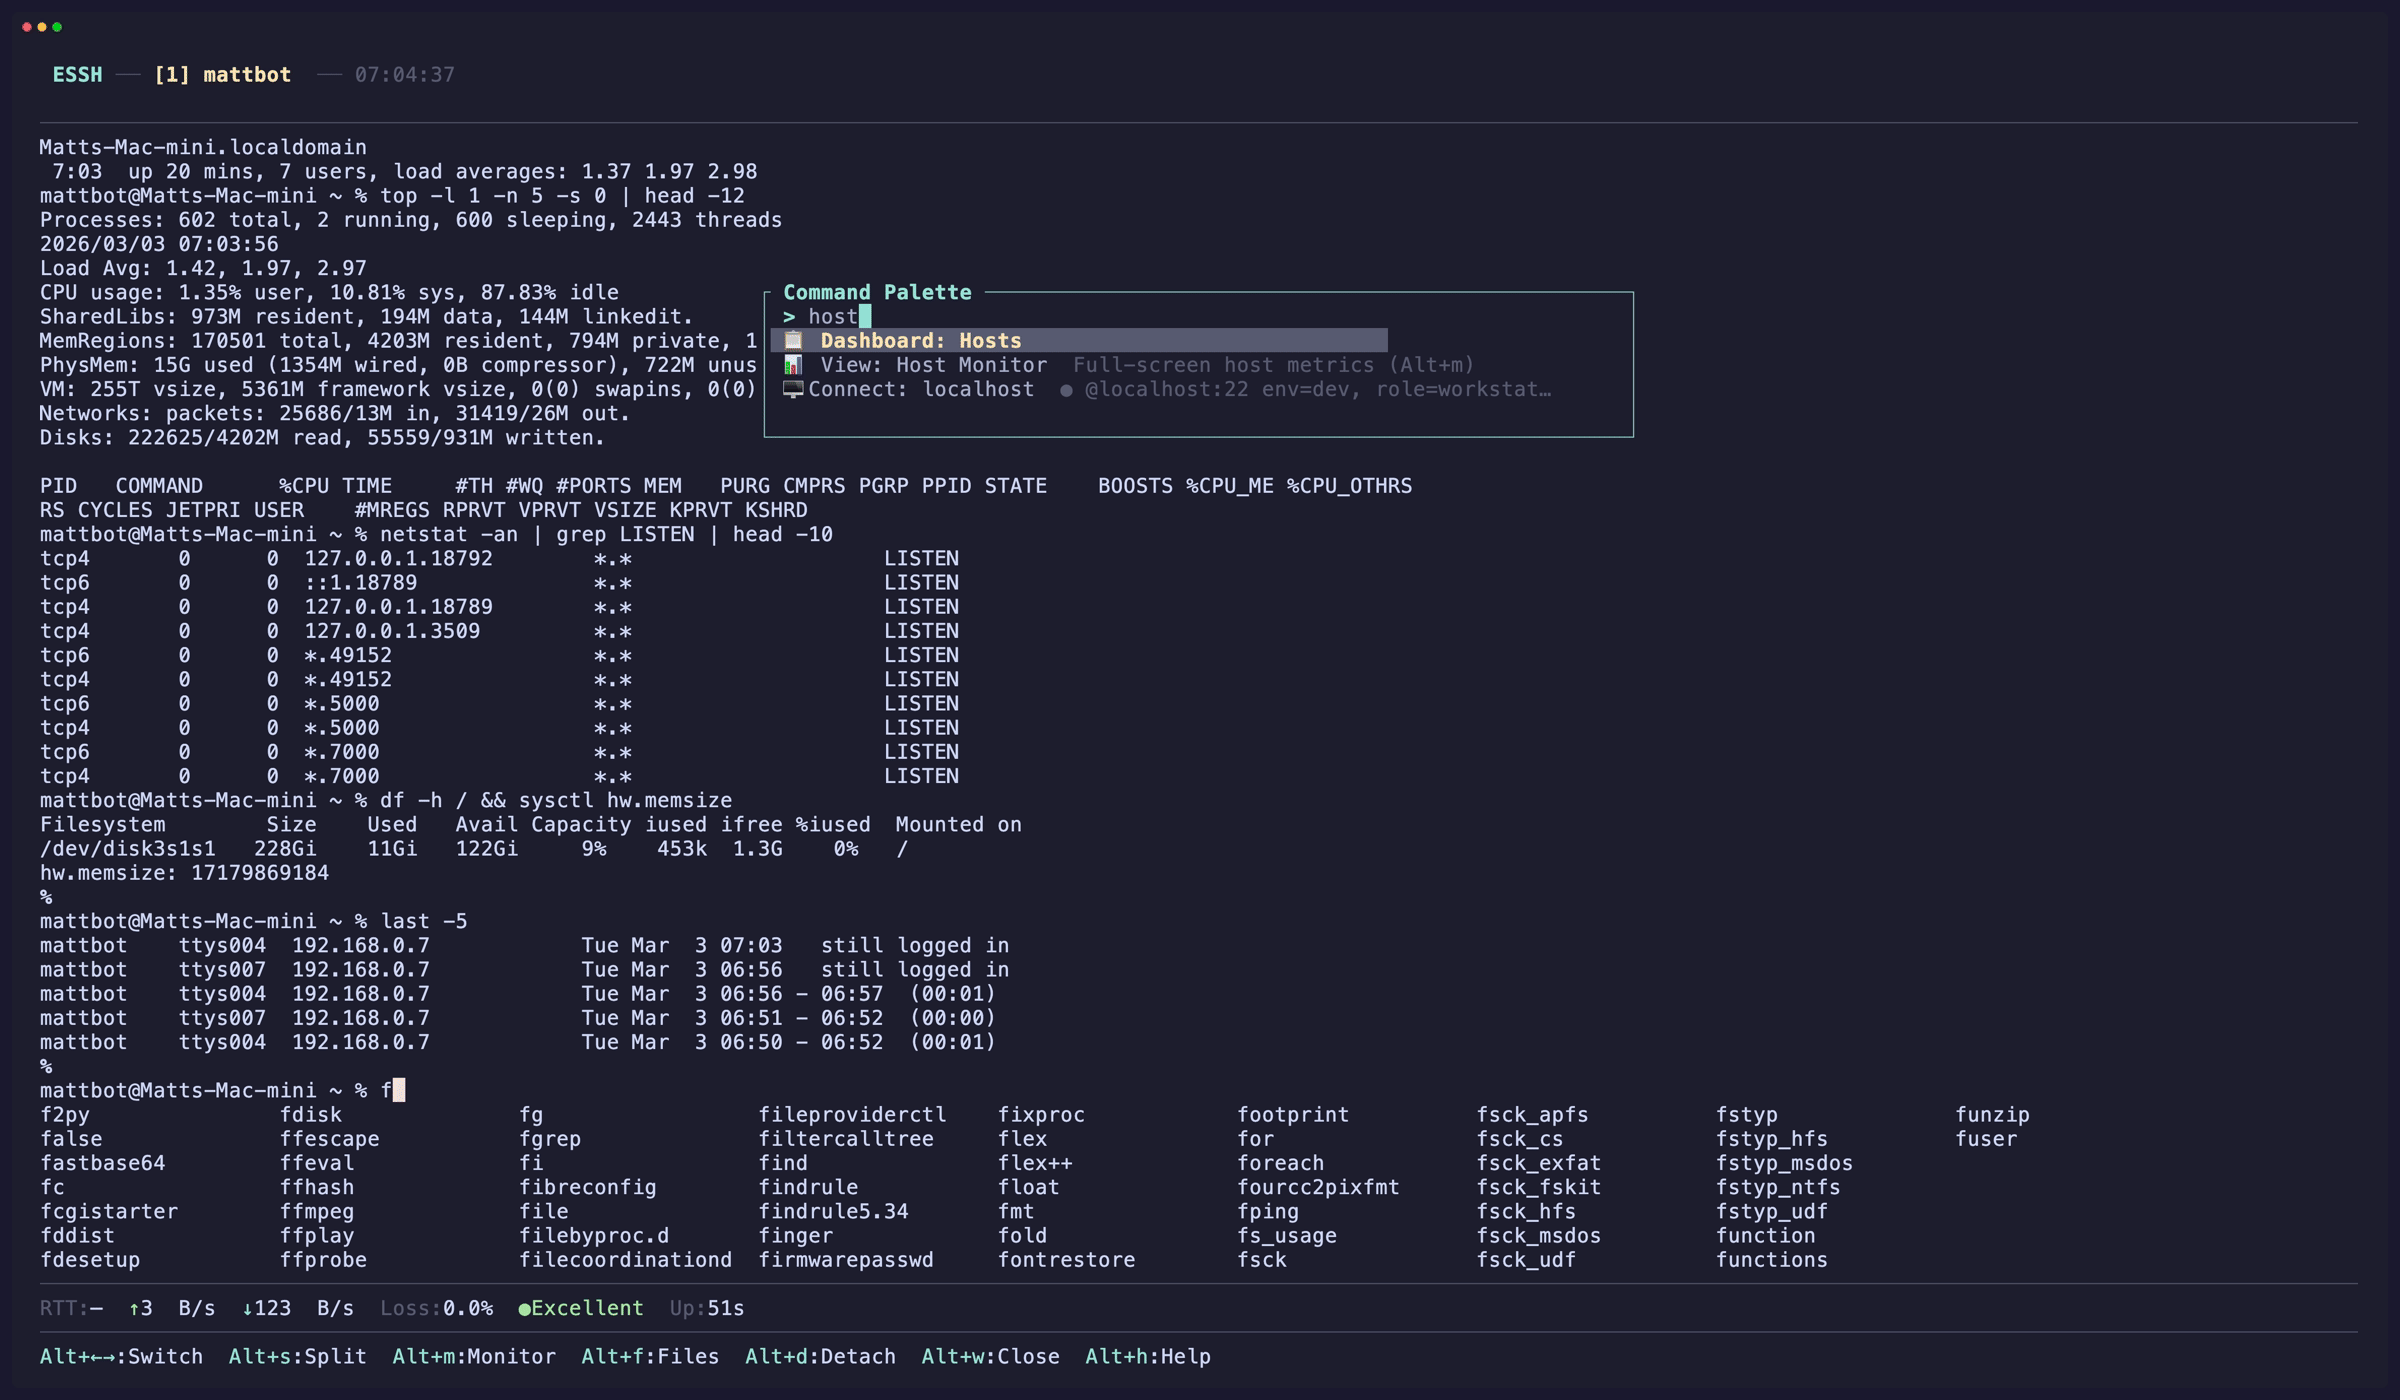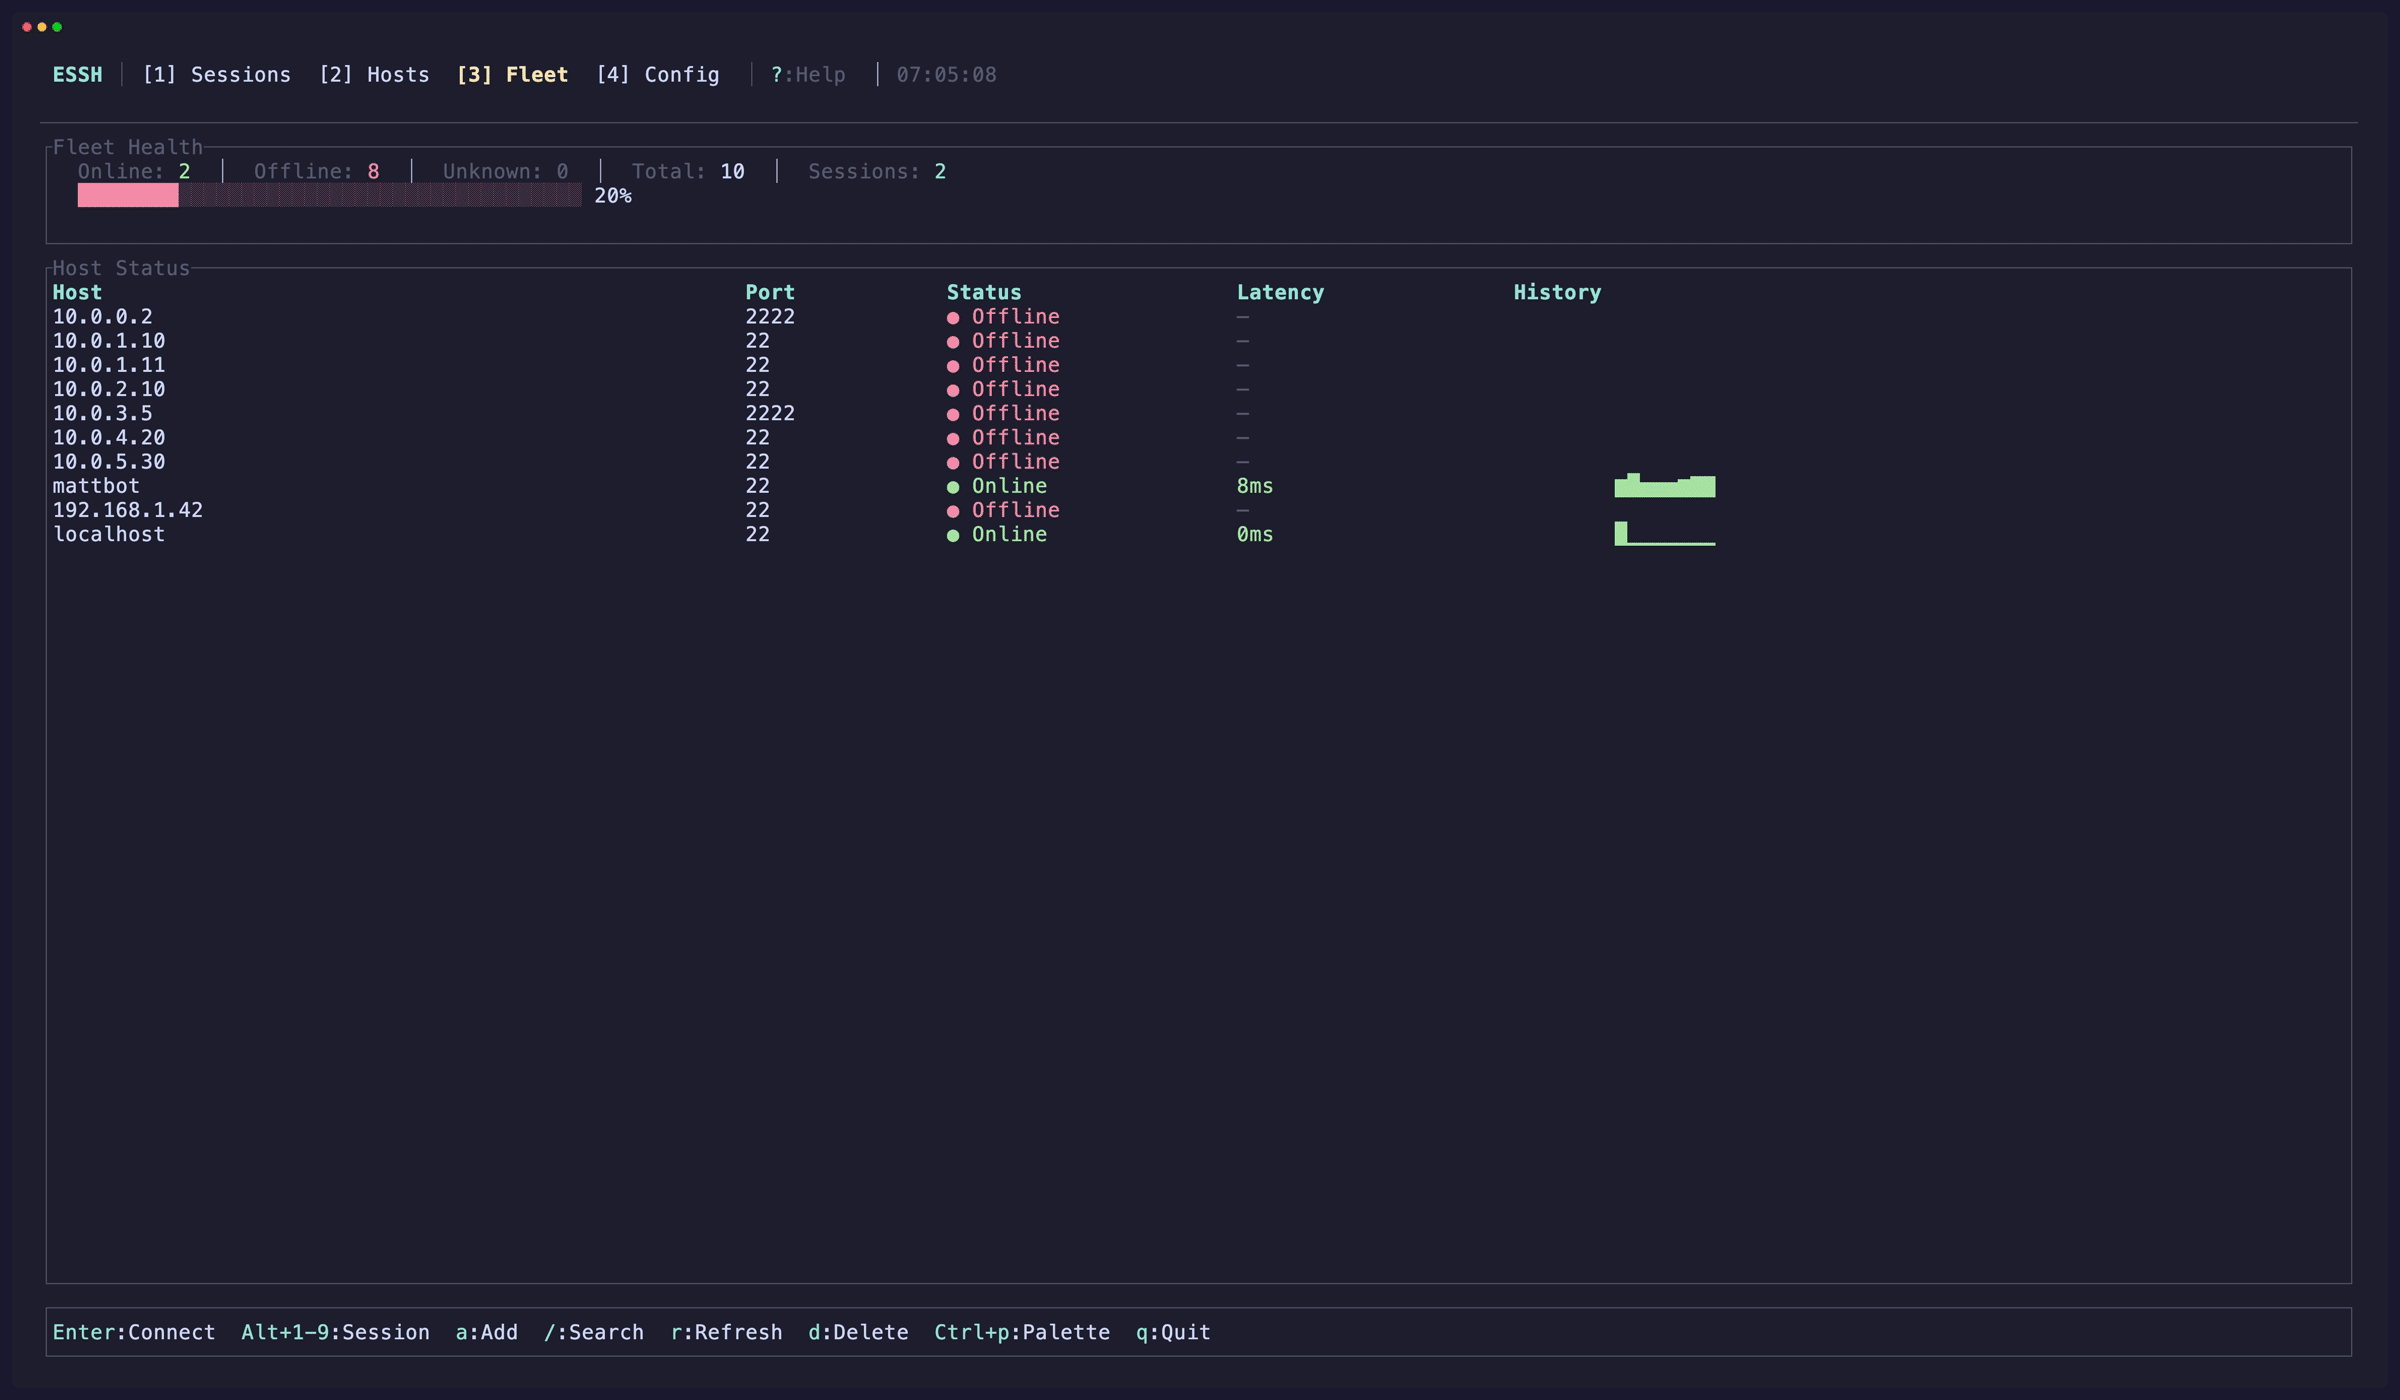 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 trinadh465/external_tcpdump_cve-2018-14880
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
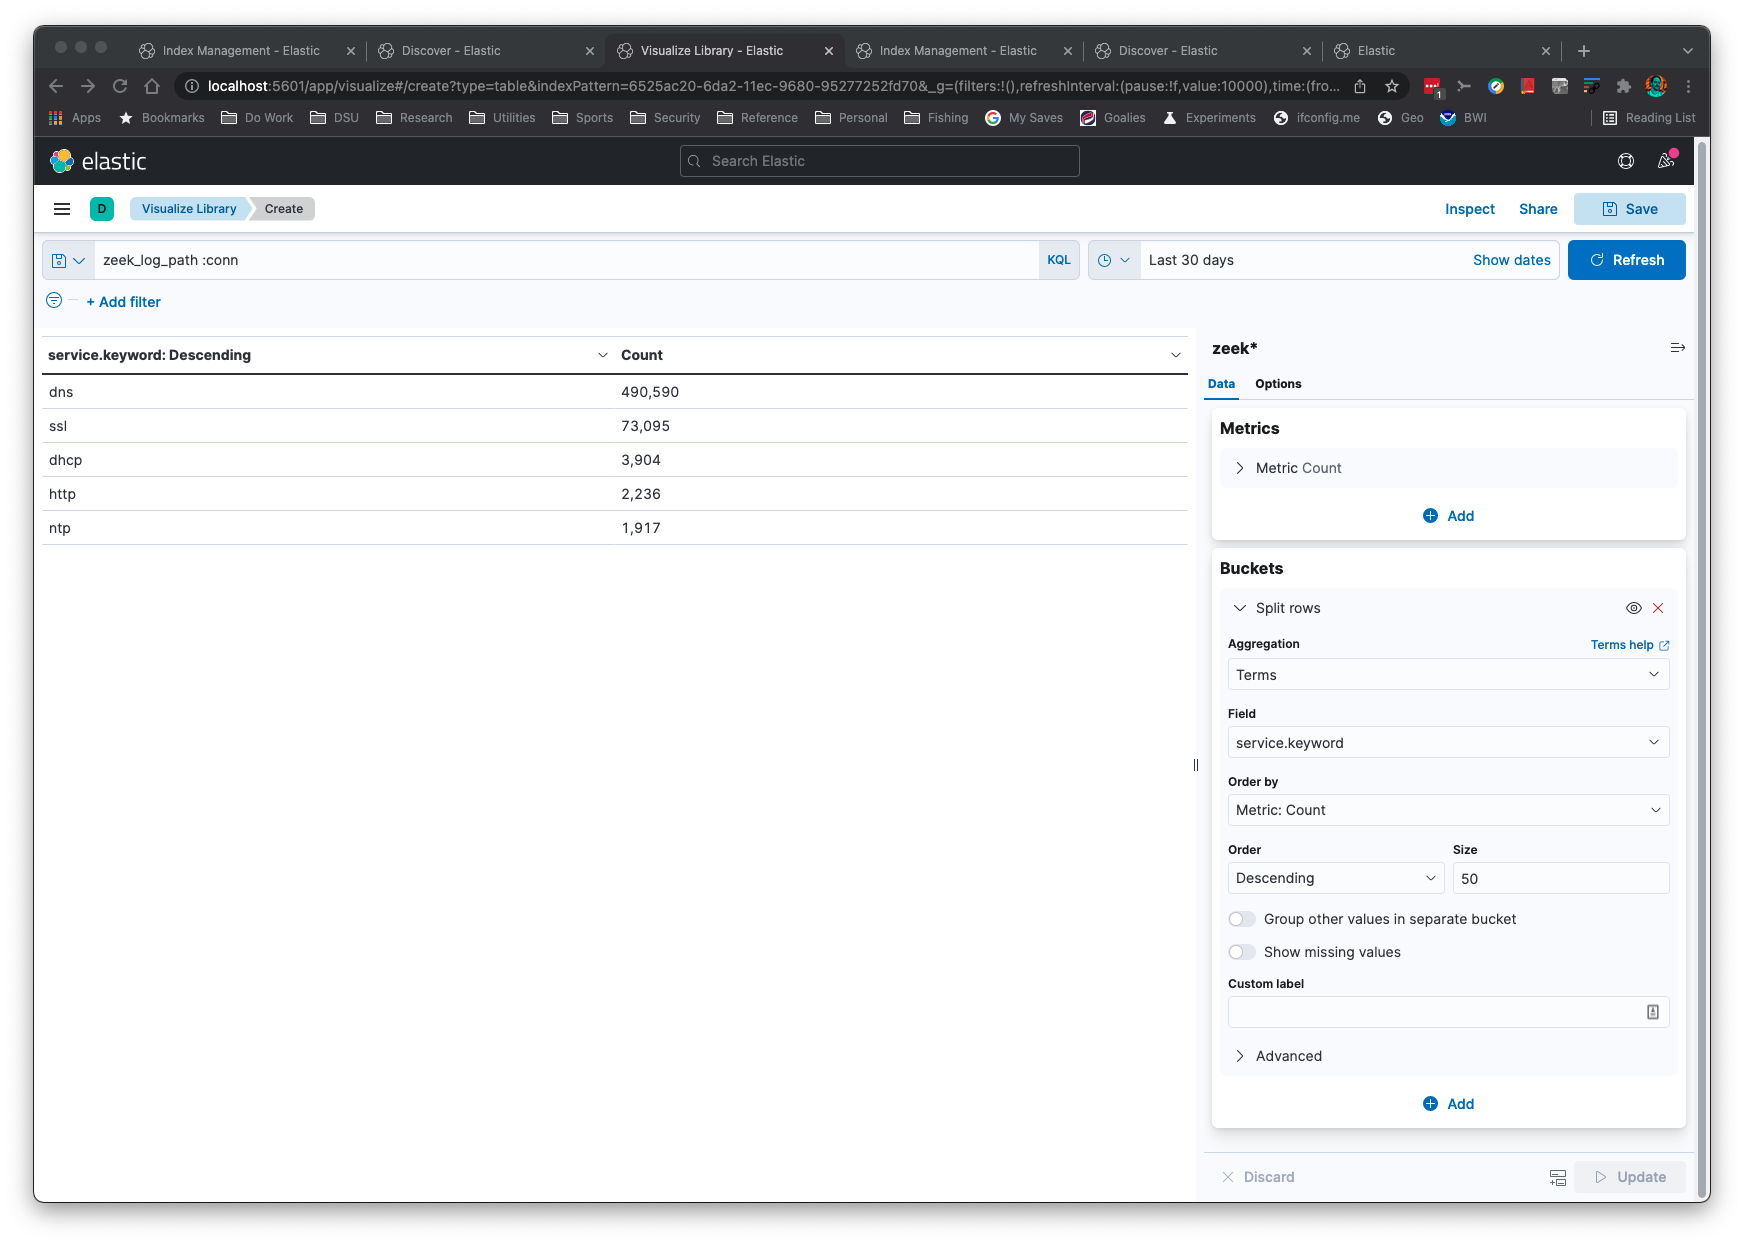 corelight/zeek2es
A Python application to filter and transfer Zeek logs to Elastic/OpenSearch+Humio. This app can also output pure JSON logs to stdout for further…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.