SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…

Python PoC scanner and exploit for CVE-2026-89274, an unauthenticated arbitrary shortcode execution flaw in WP Recipe Maker <=10.8.1 via recipe…

Python 3 PoC scanner and exploit for CVE-2026-92229, an unauthenticated arbitrary shortcode execution flaw in Forminator WordPress plugin versions…

Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.

Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…

Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…

The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…

Offline and security-first tool for syncing and managing agent skills

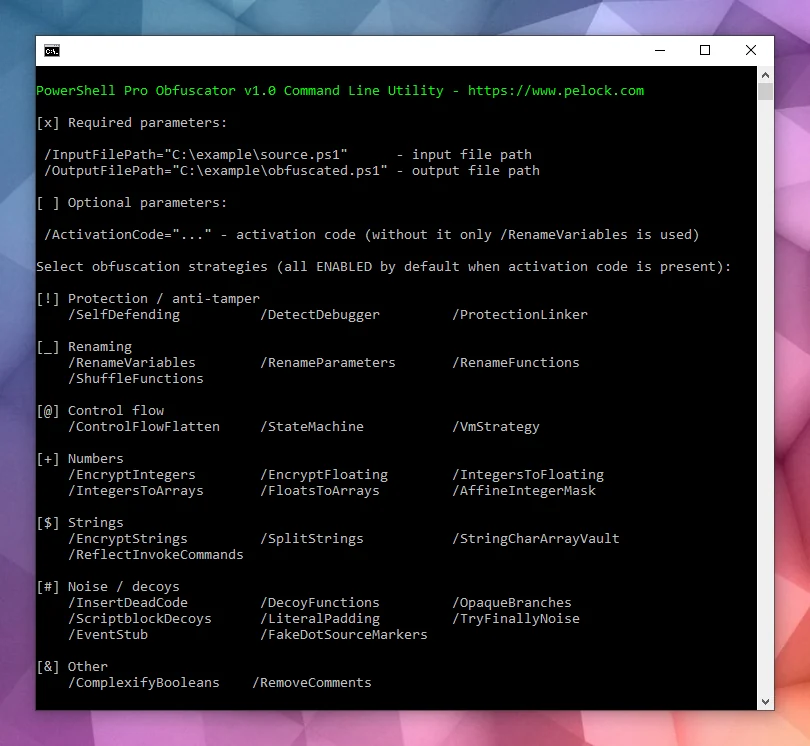
Automate PowerShell script source code obfuscation & virtualization with a flexible Web API for Python (pip package).

Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…

This Pwsh script run AppScan Standard scans against a list of web sites (URLs.txt) checking for Log4J (CVE-2021-44228) vulnerability

💯 Teach puppeteer new tricks through plugins.

A tool for adding new lines to files, skipping duplicates

Chaos Engineering Toolkit & Orchestration for Developers

Ansible Playbook for CVE-2023-36845(Juniper Networks Junos OS 远程代码执行漏洞)

Kali Linux VM images build script

Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.