
Ledger
 shellkraft/ledger
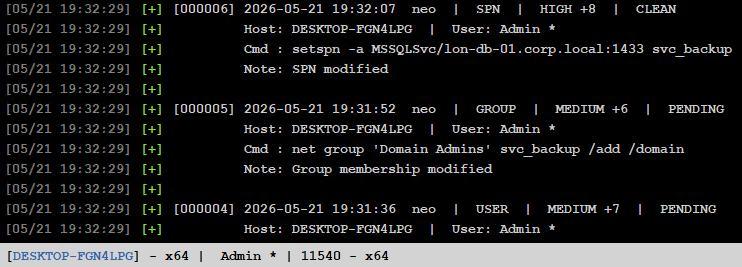
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
command-and-controlincident-responselog-analysis+5
shellkraft/ledgerAn aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…