
Archived
APOLOGEE
 rosesecurity/apologee
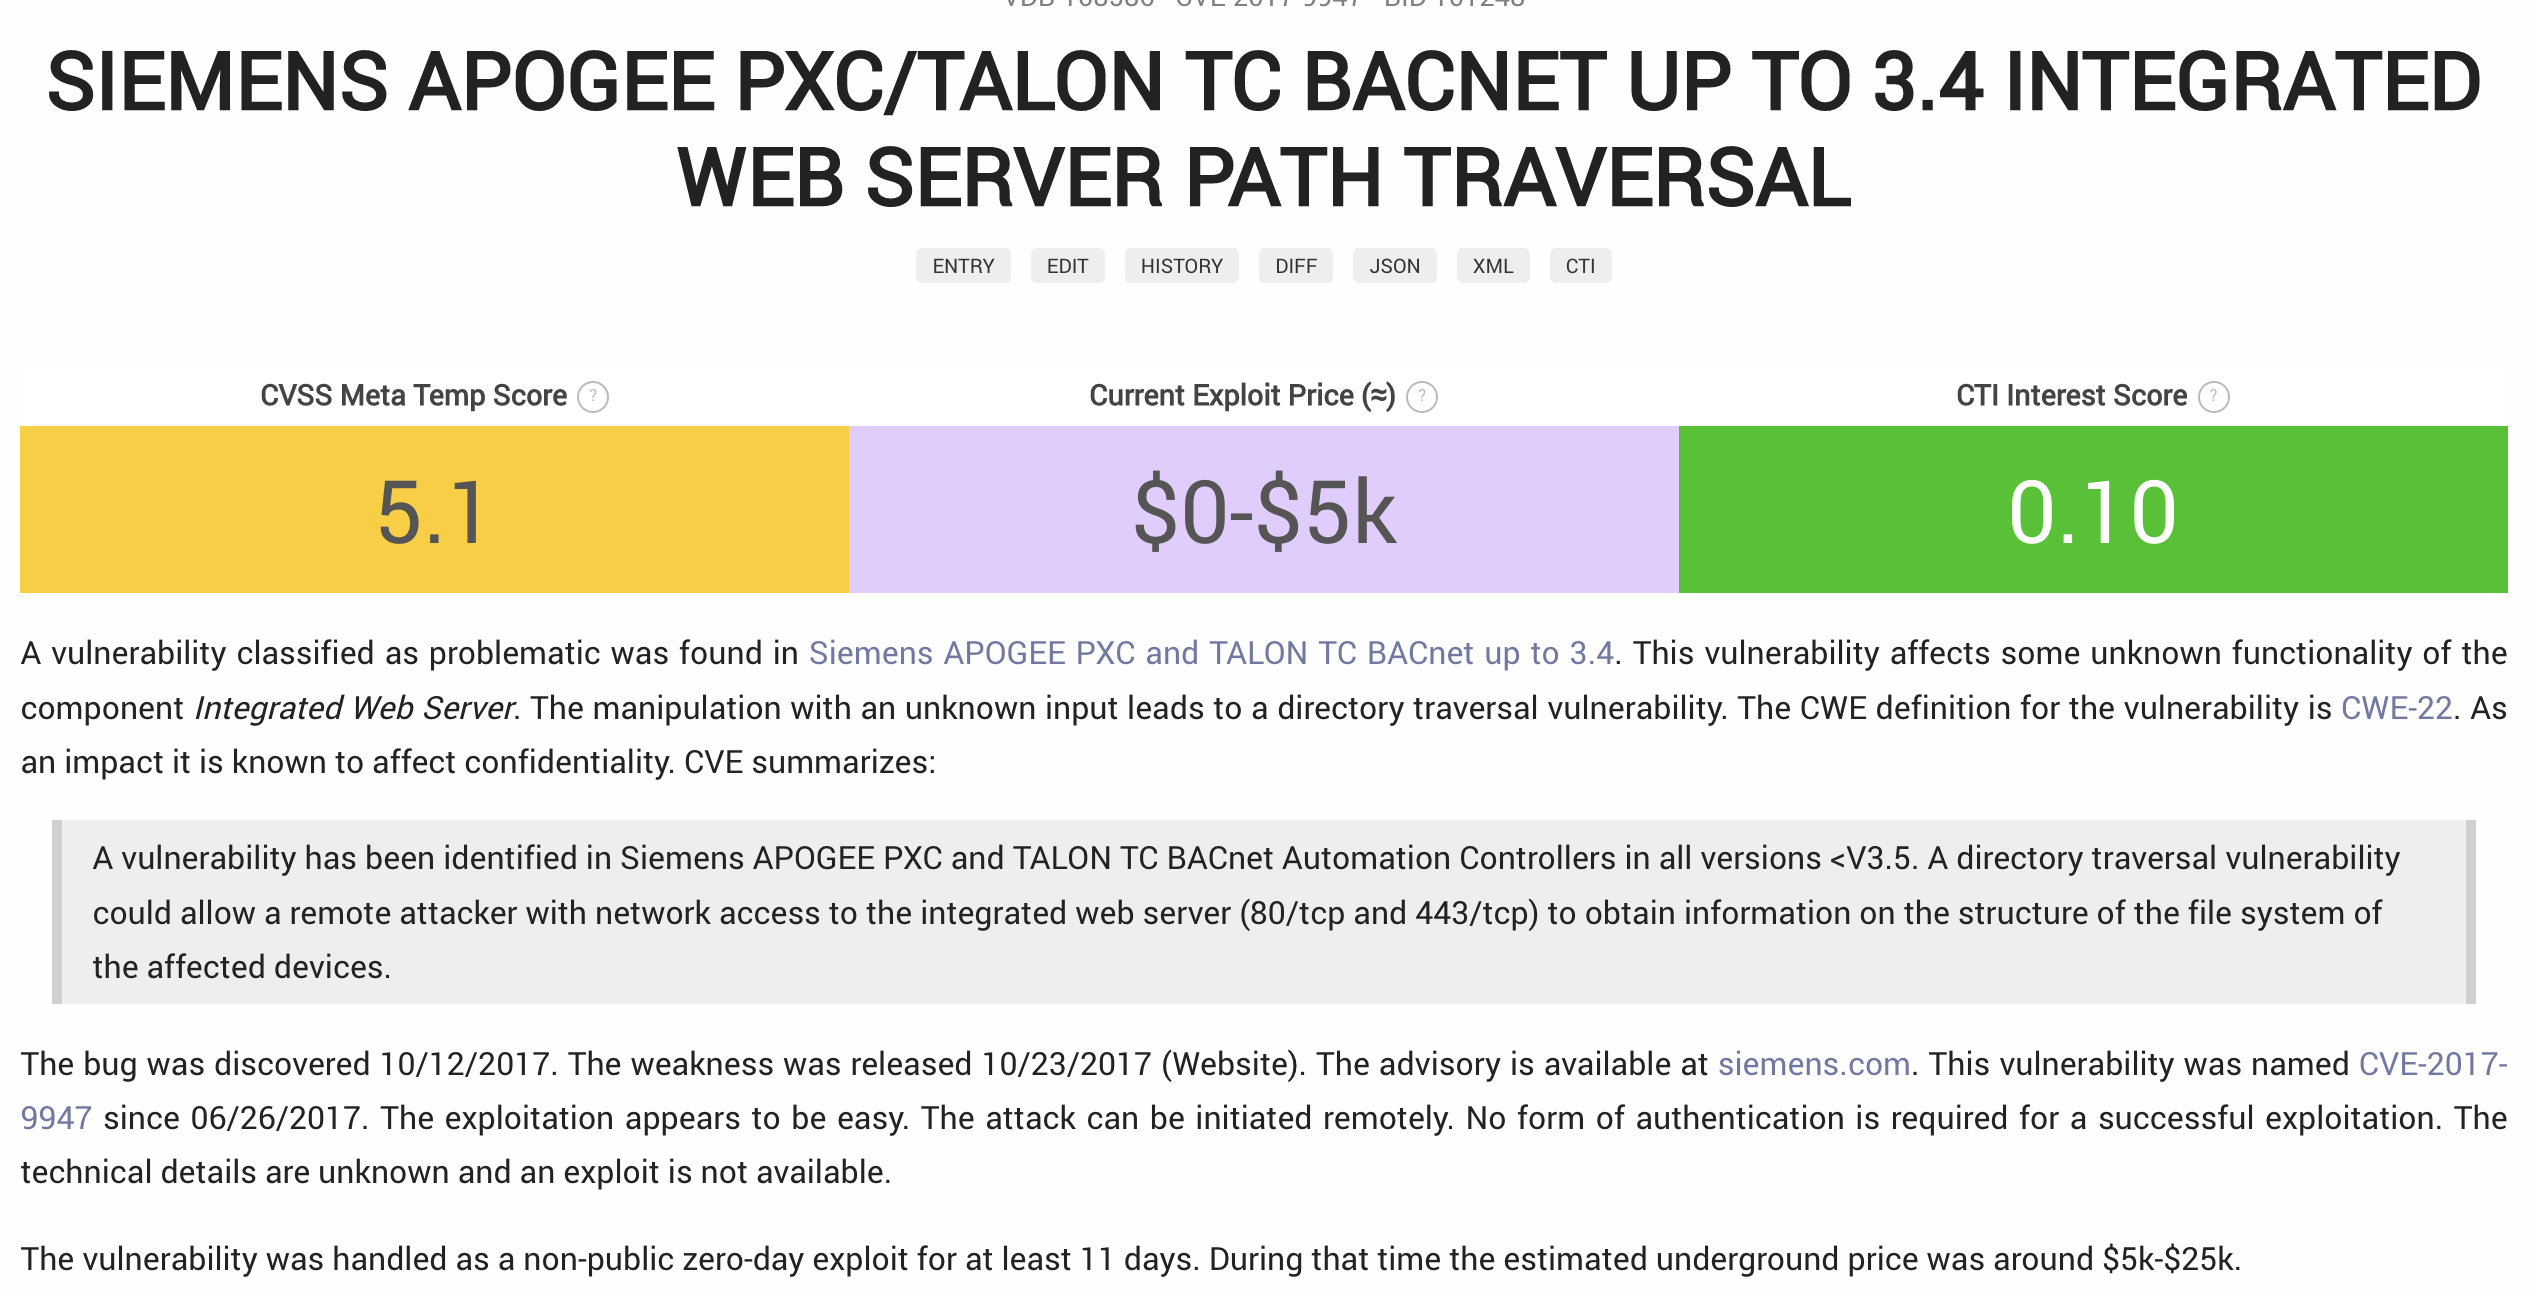
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
authenticationexploitationexploit-frameworks+8

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 0vercl0k/paracosme
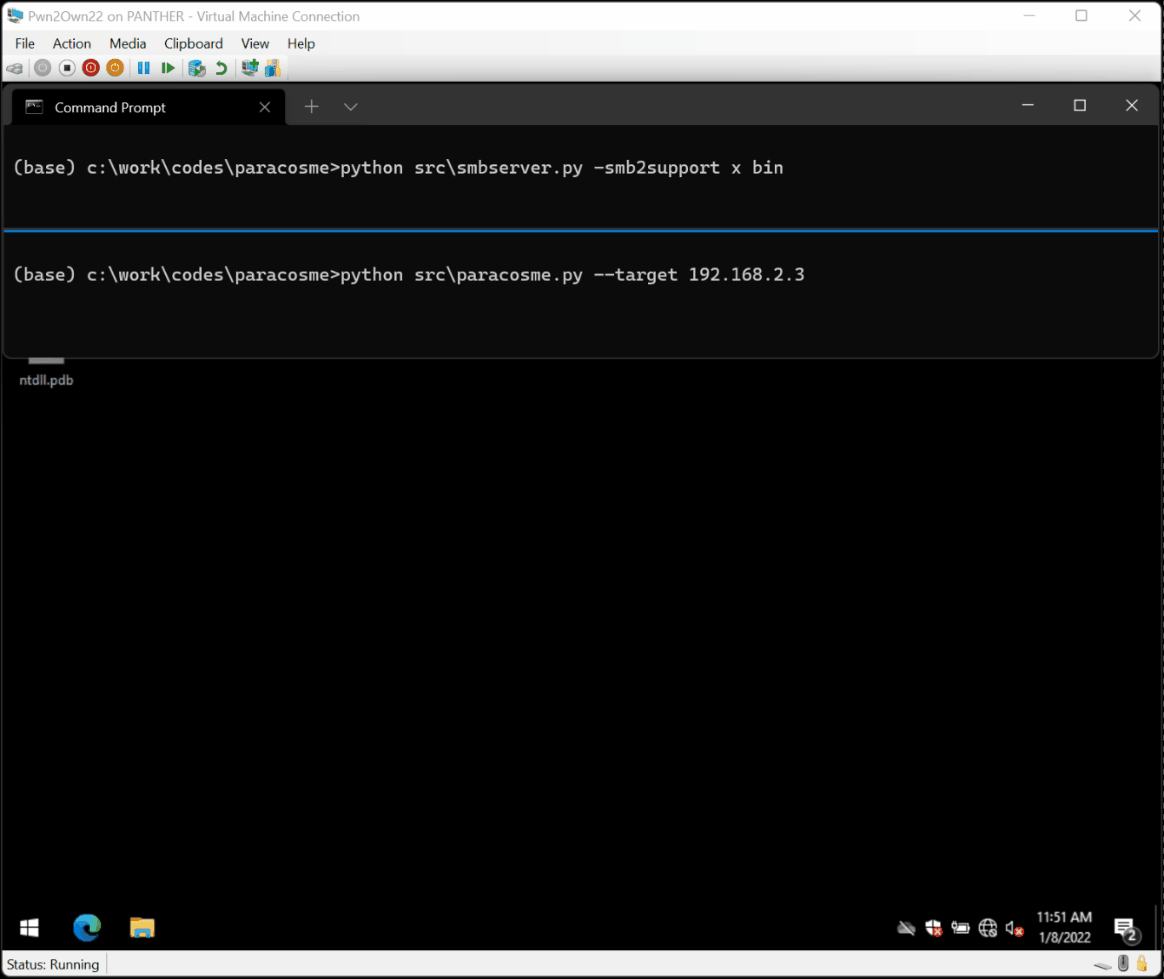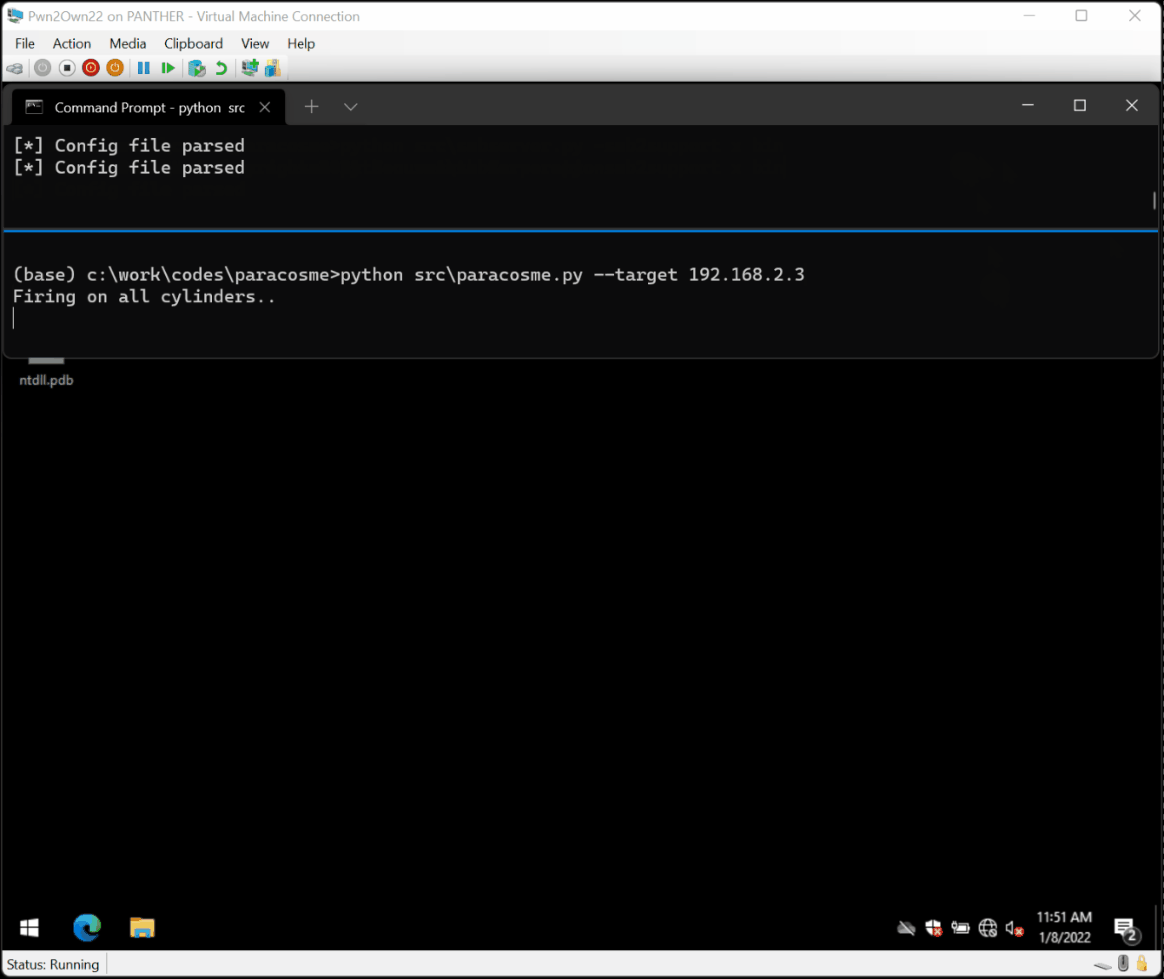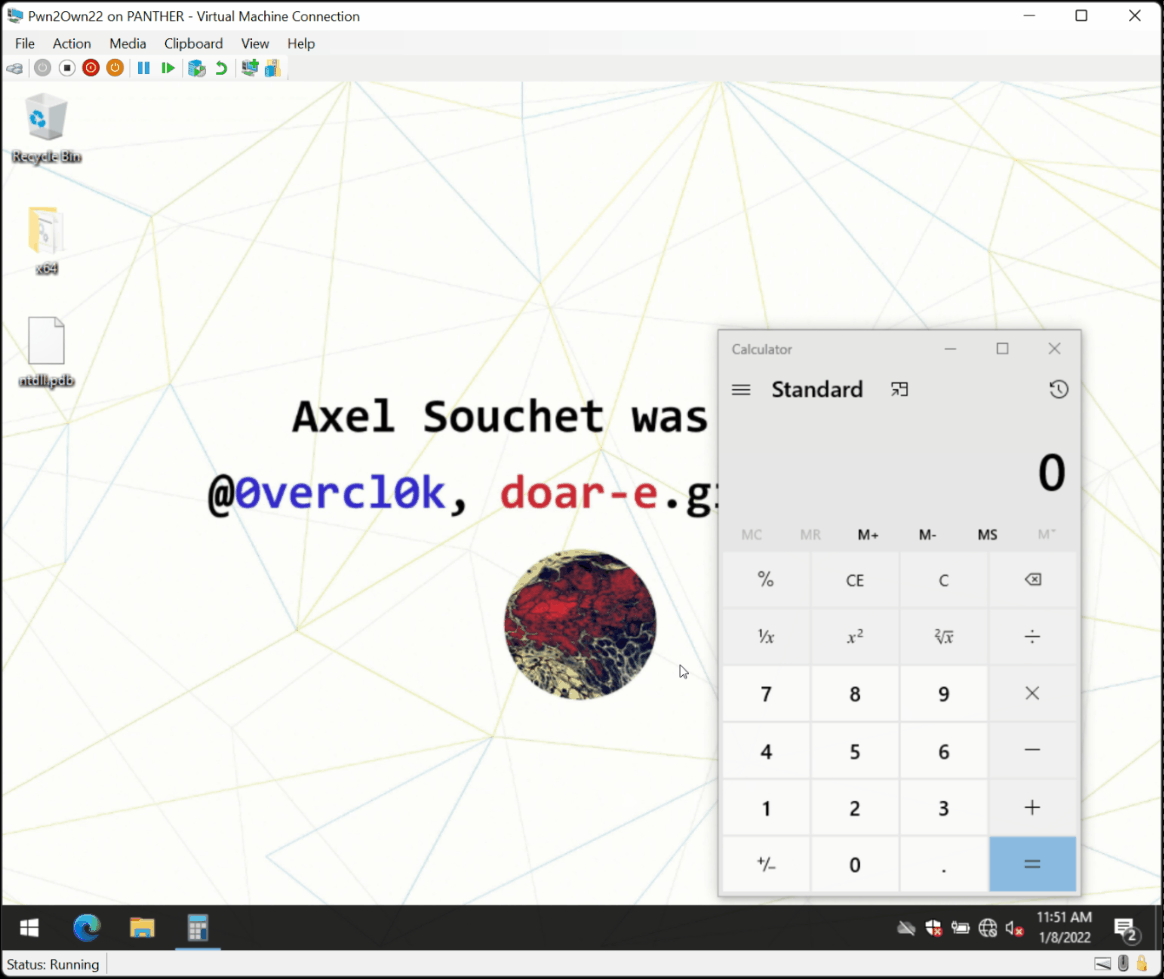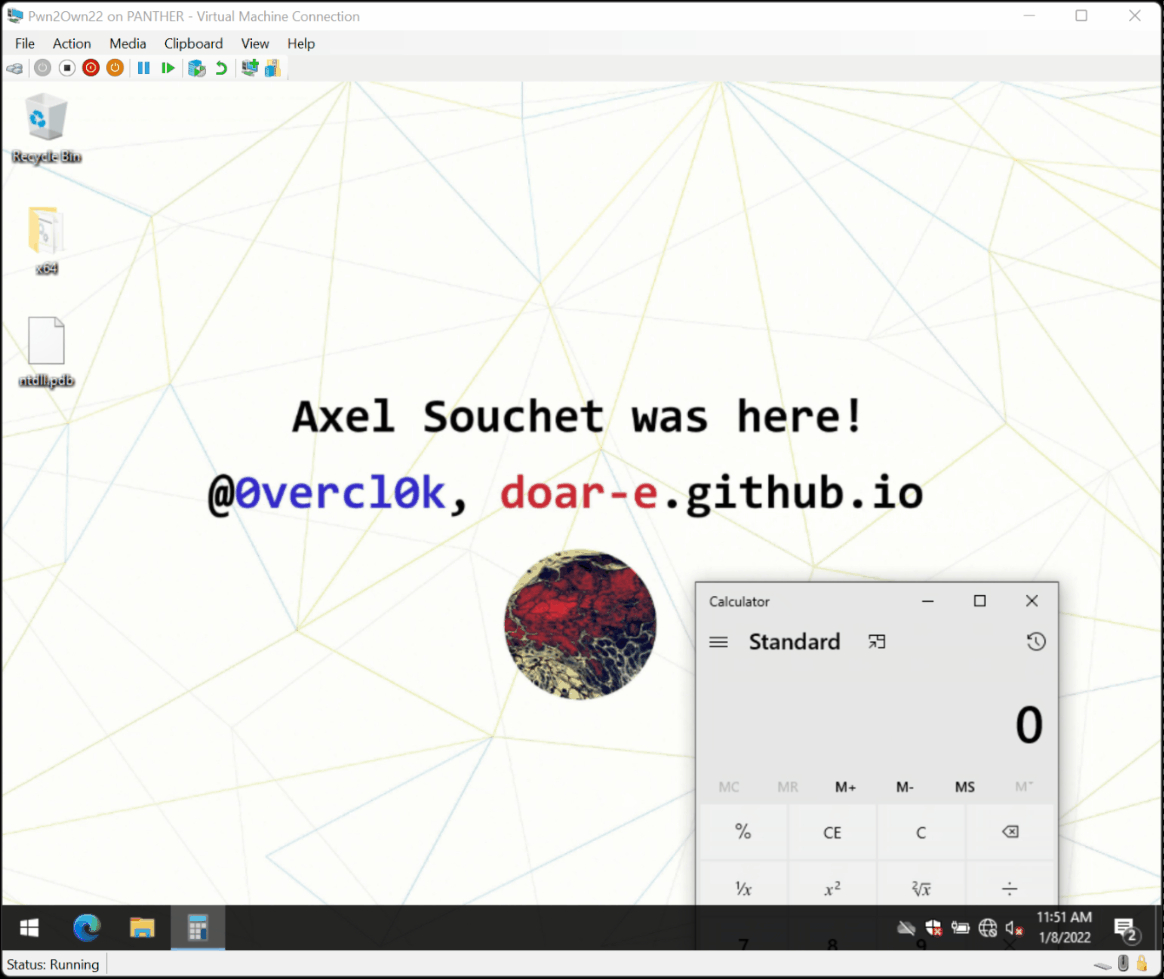
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…
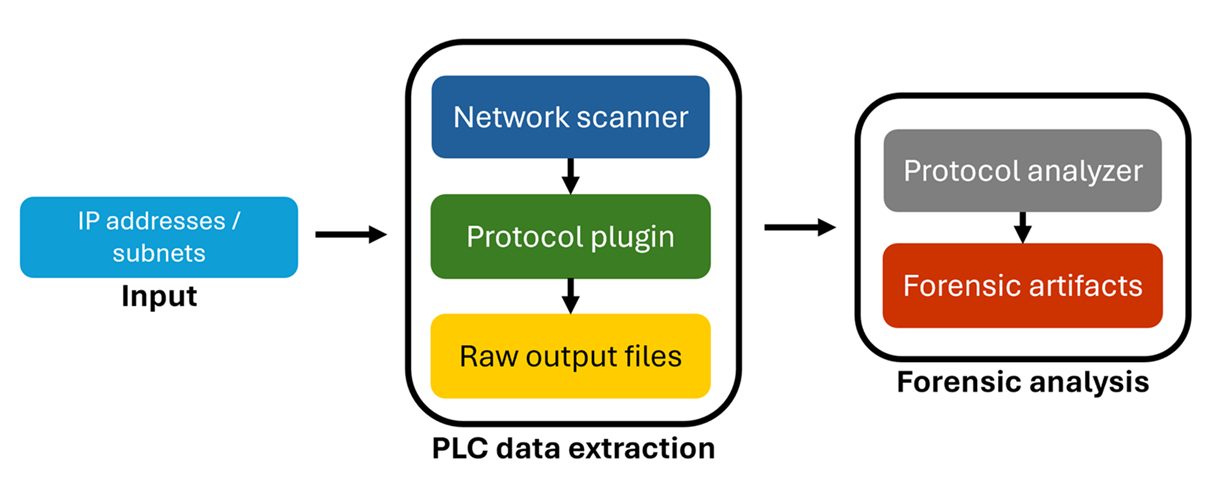 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 jensregel/advisories
This repository contains a few vulnerabilities that were found and reported during vulnerability assessments.
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 seifallahhomrani1/cve-2023-0861-poc
Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers
 webraybtl/cve-2022-1068
Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现
 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…