
ICSFuzz
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
dynamic-code-analysisembedded-systems-securityfuzzing+3
30
momalab/icsfuzzInstrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
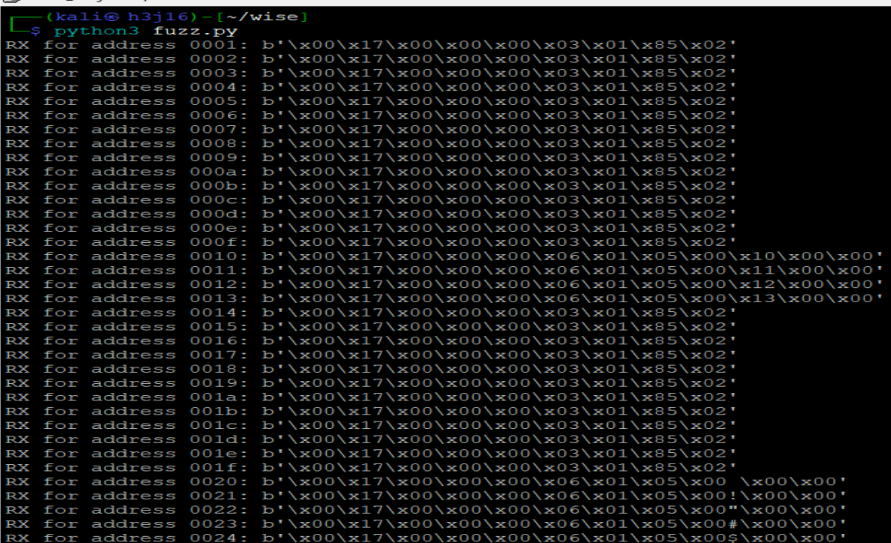 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
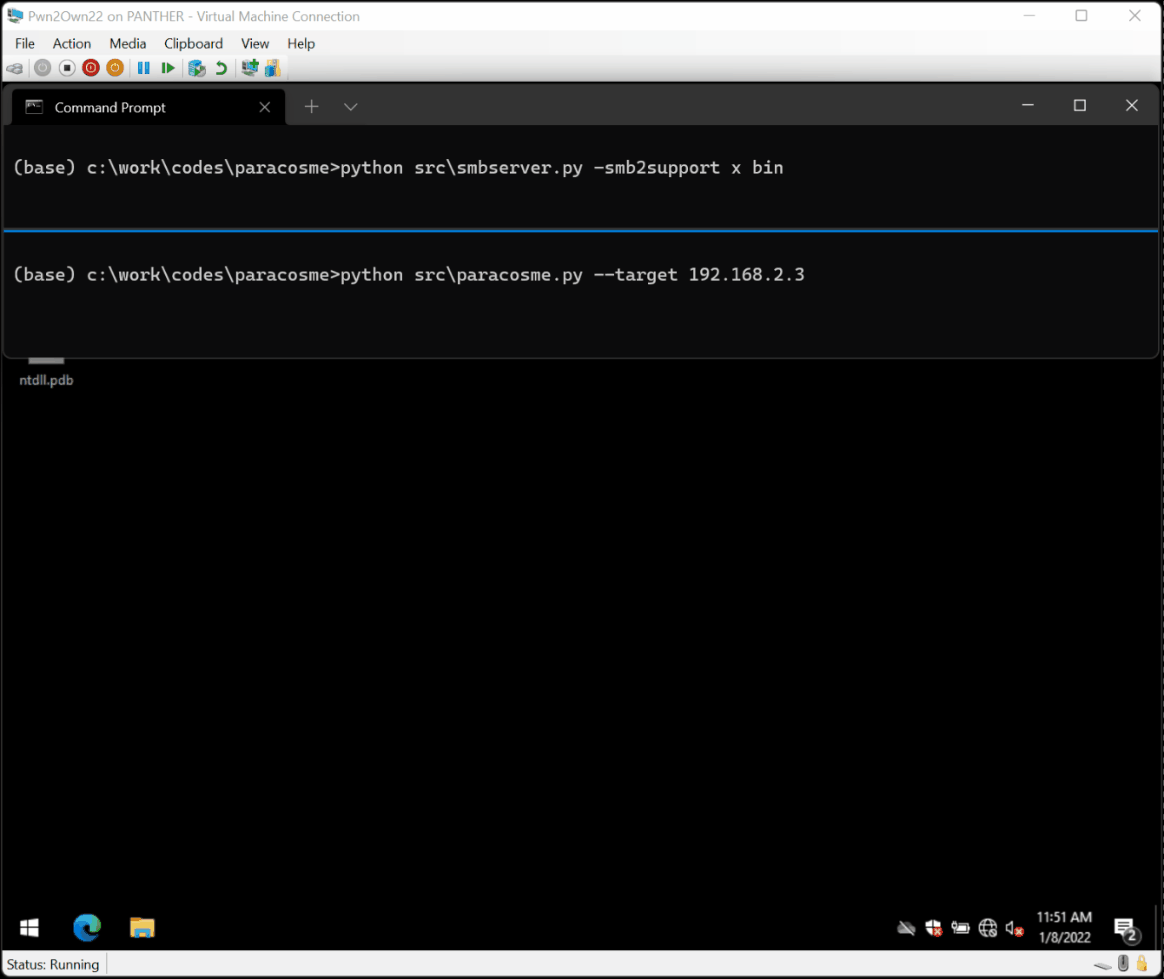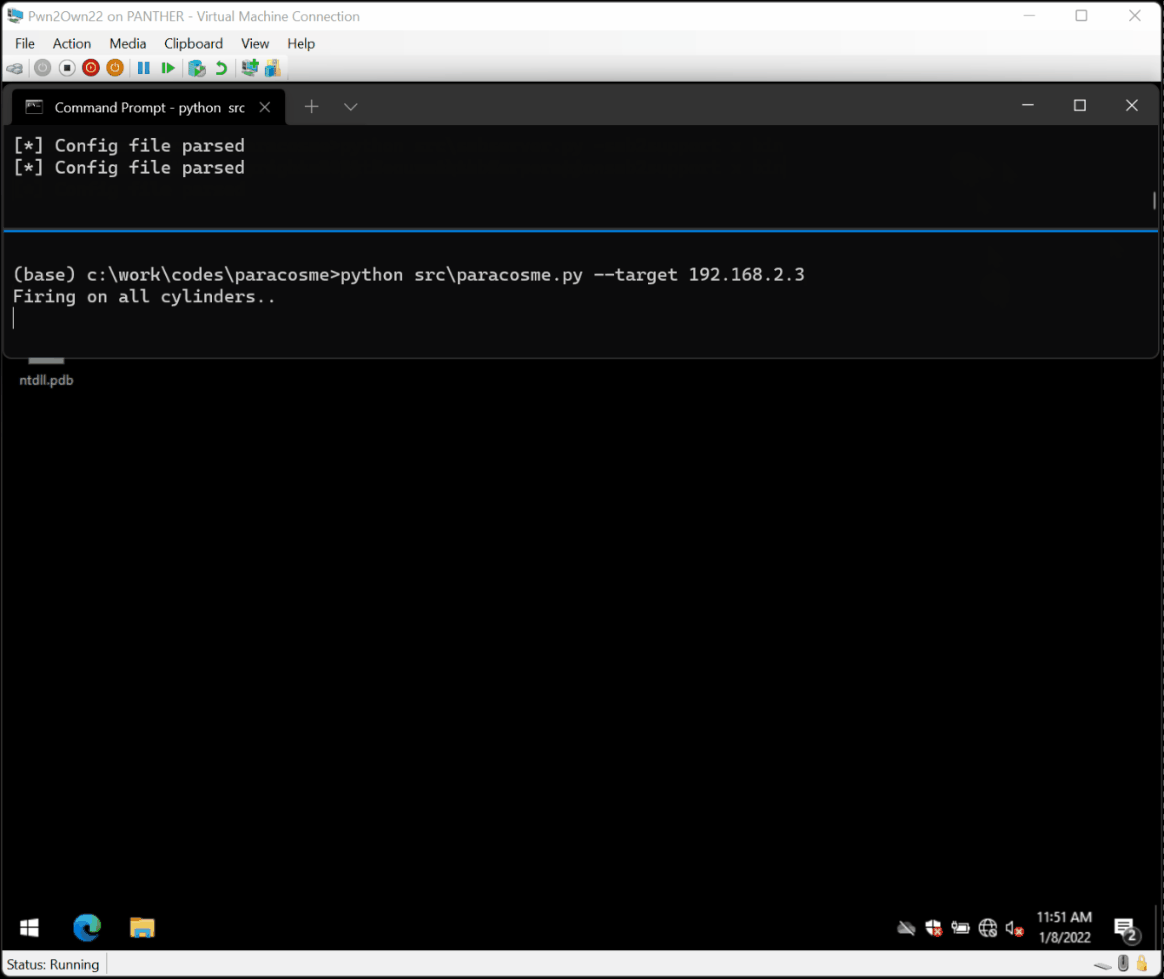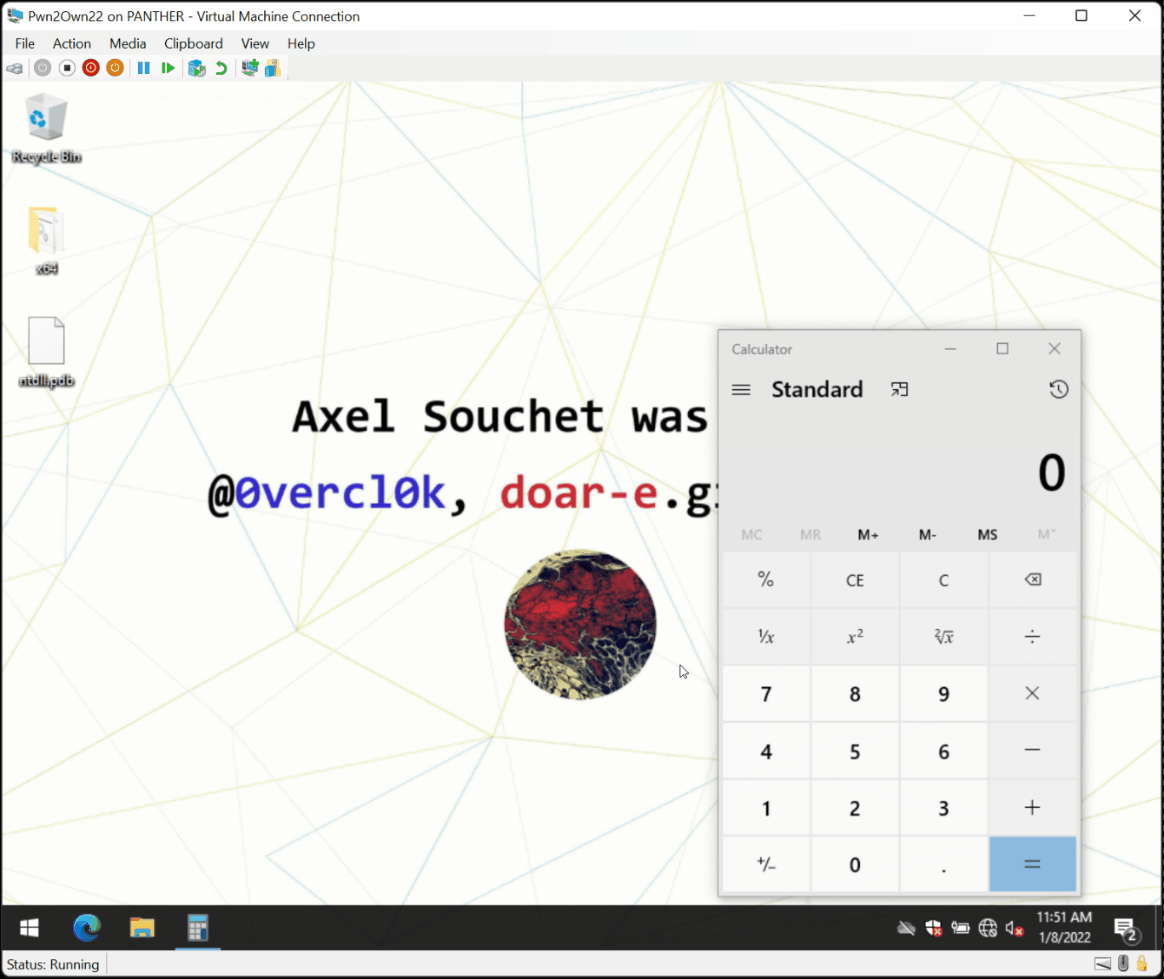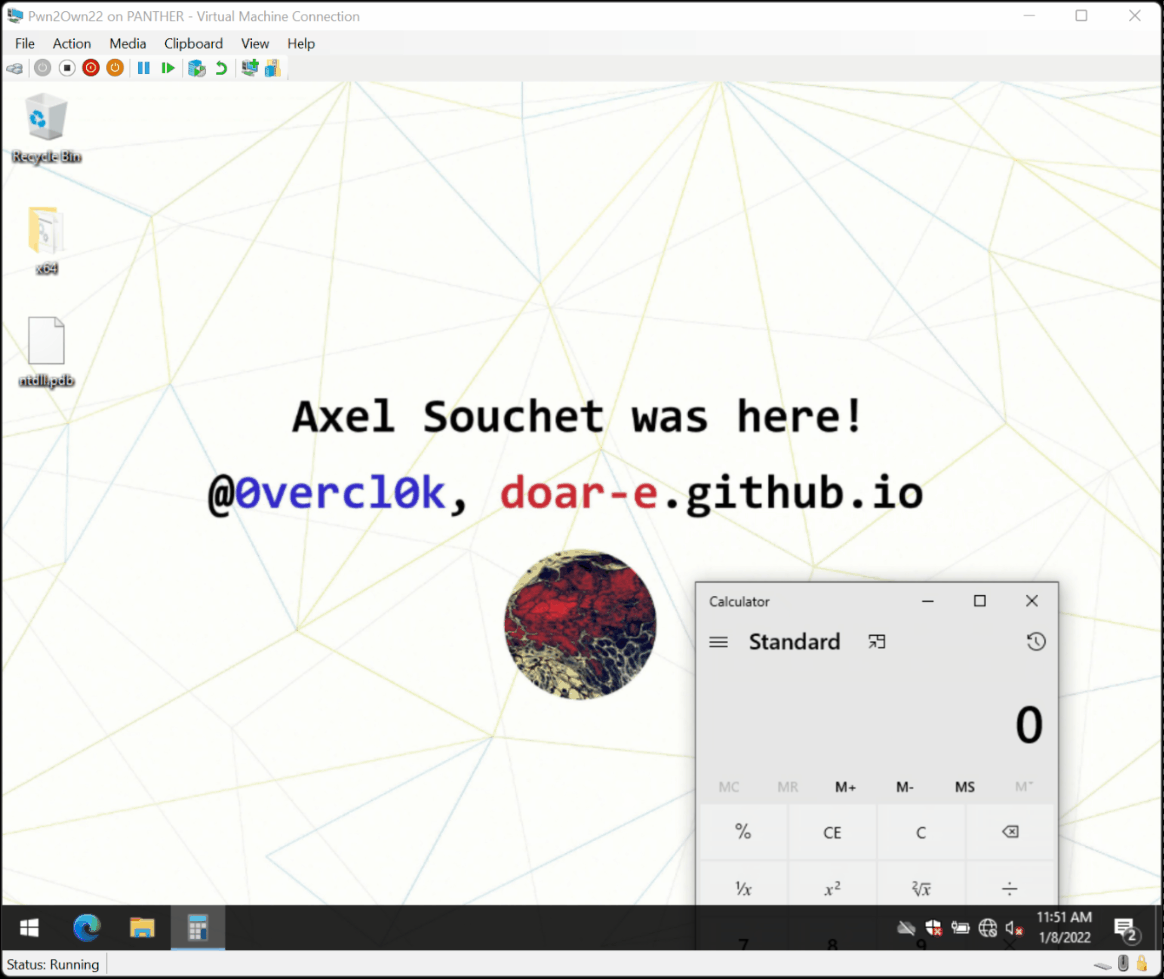 0vercl0k/paracosme
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
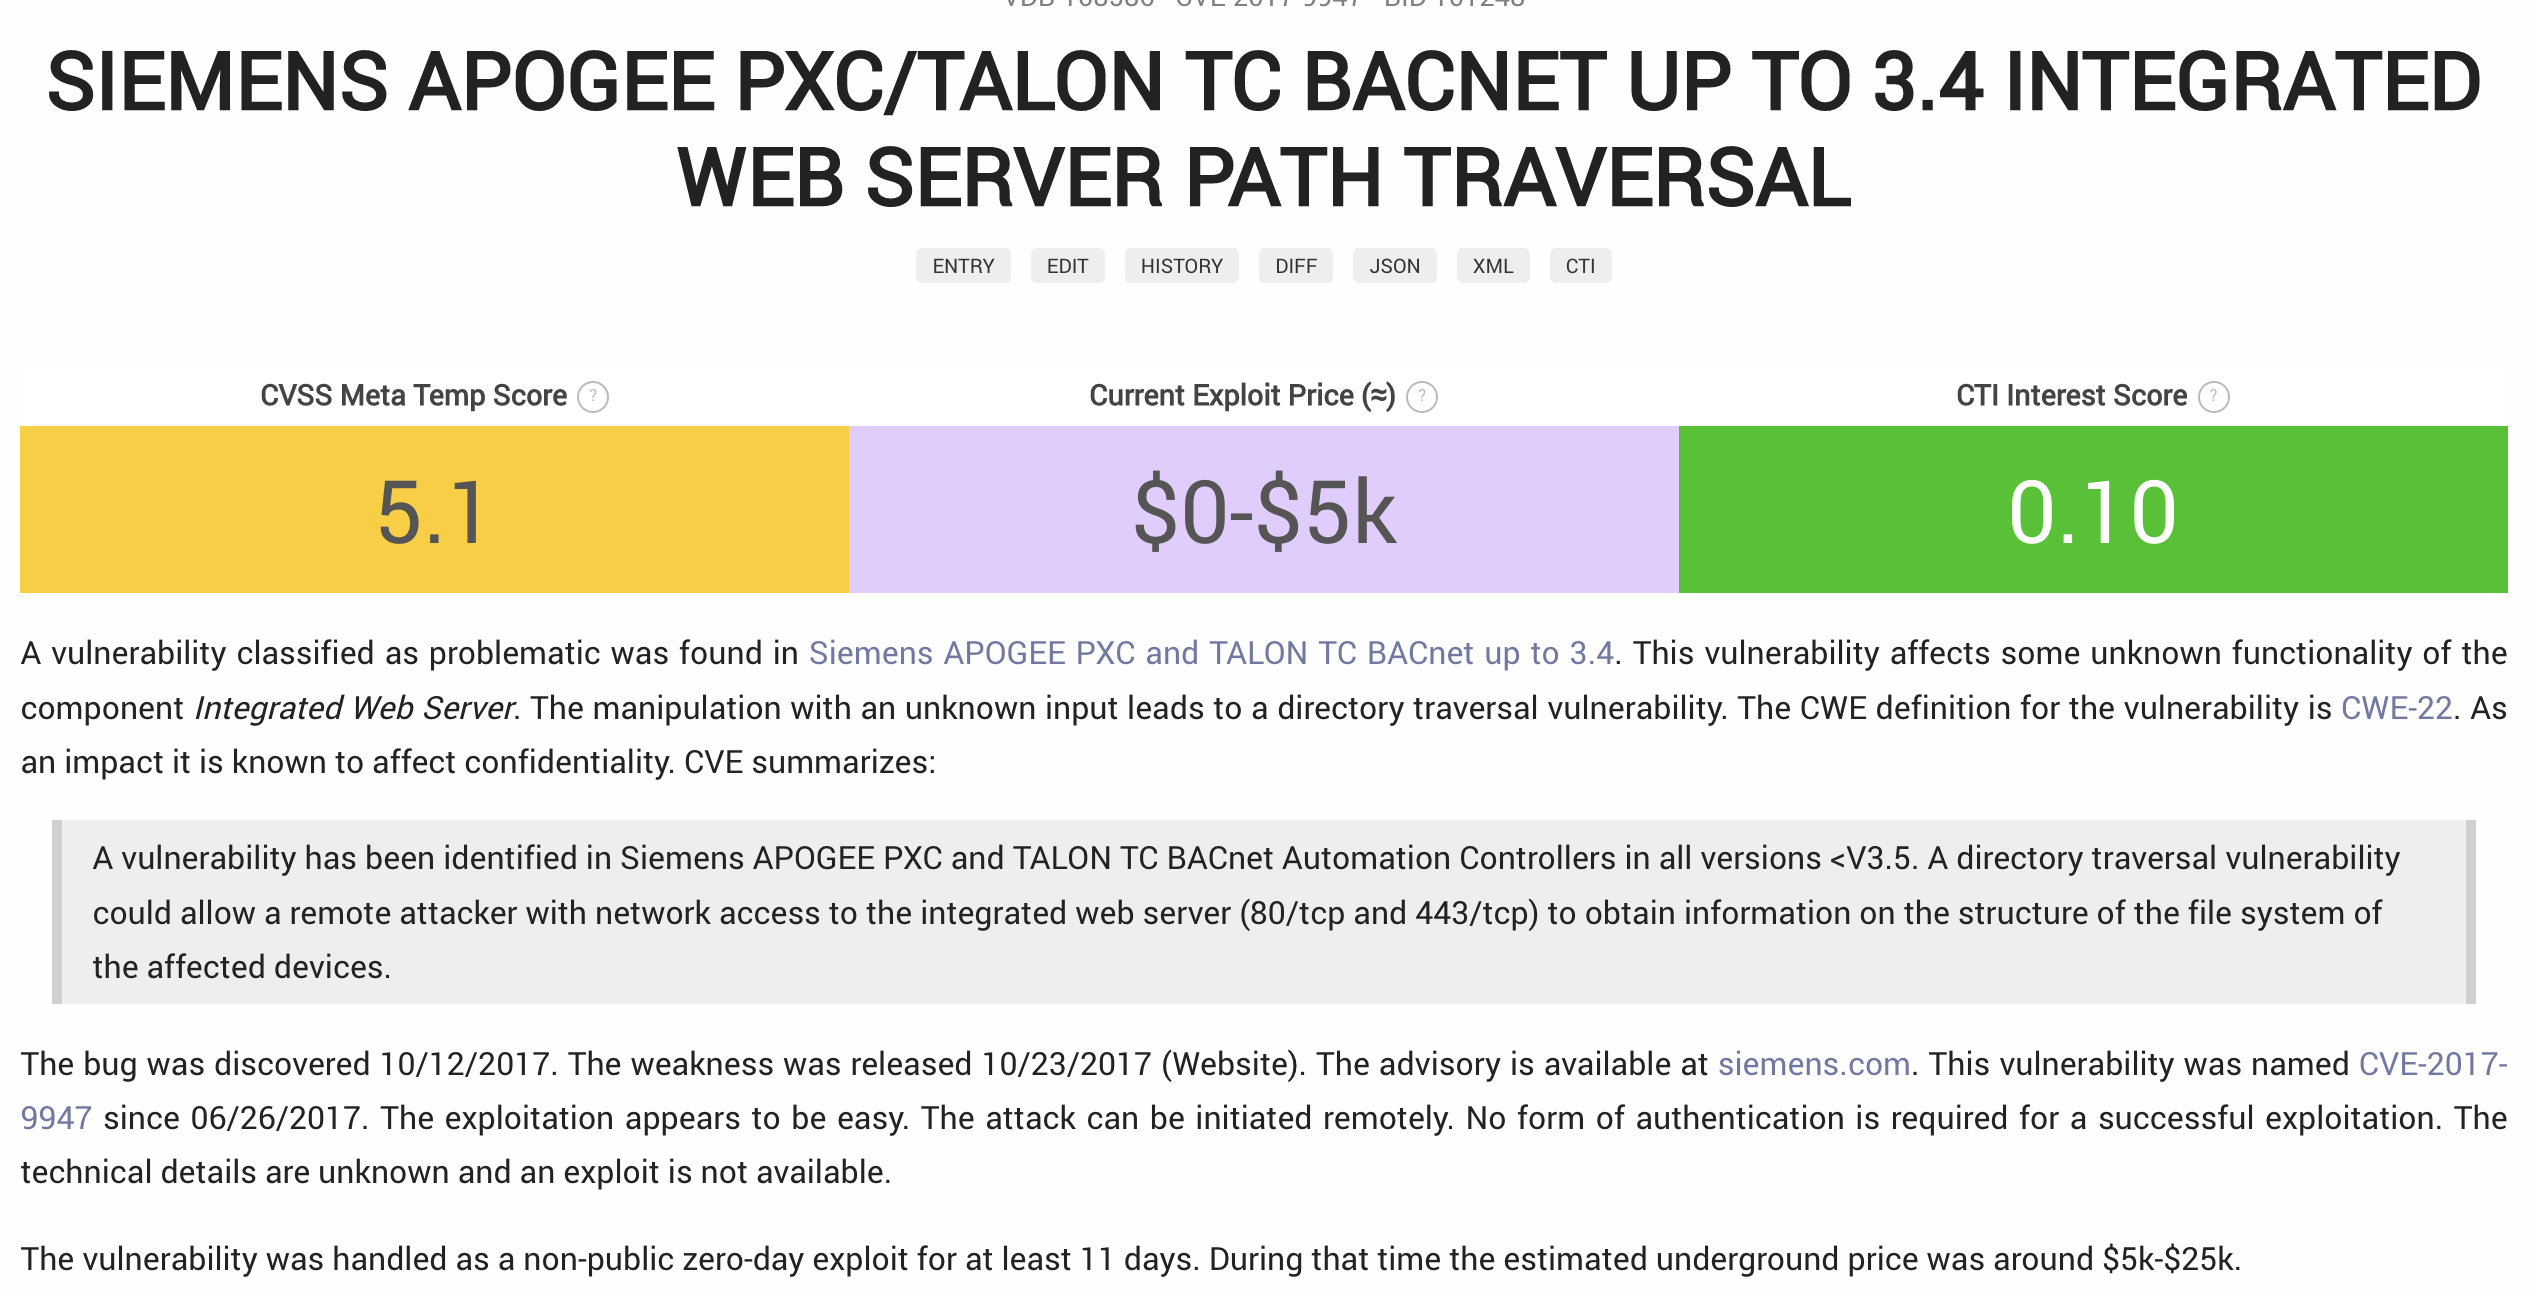 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…