CVE-2021-26828_ScadaBR_RCE

Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

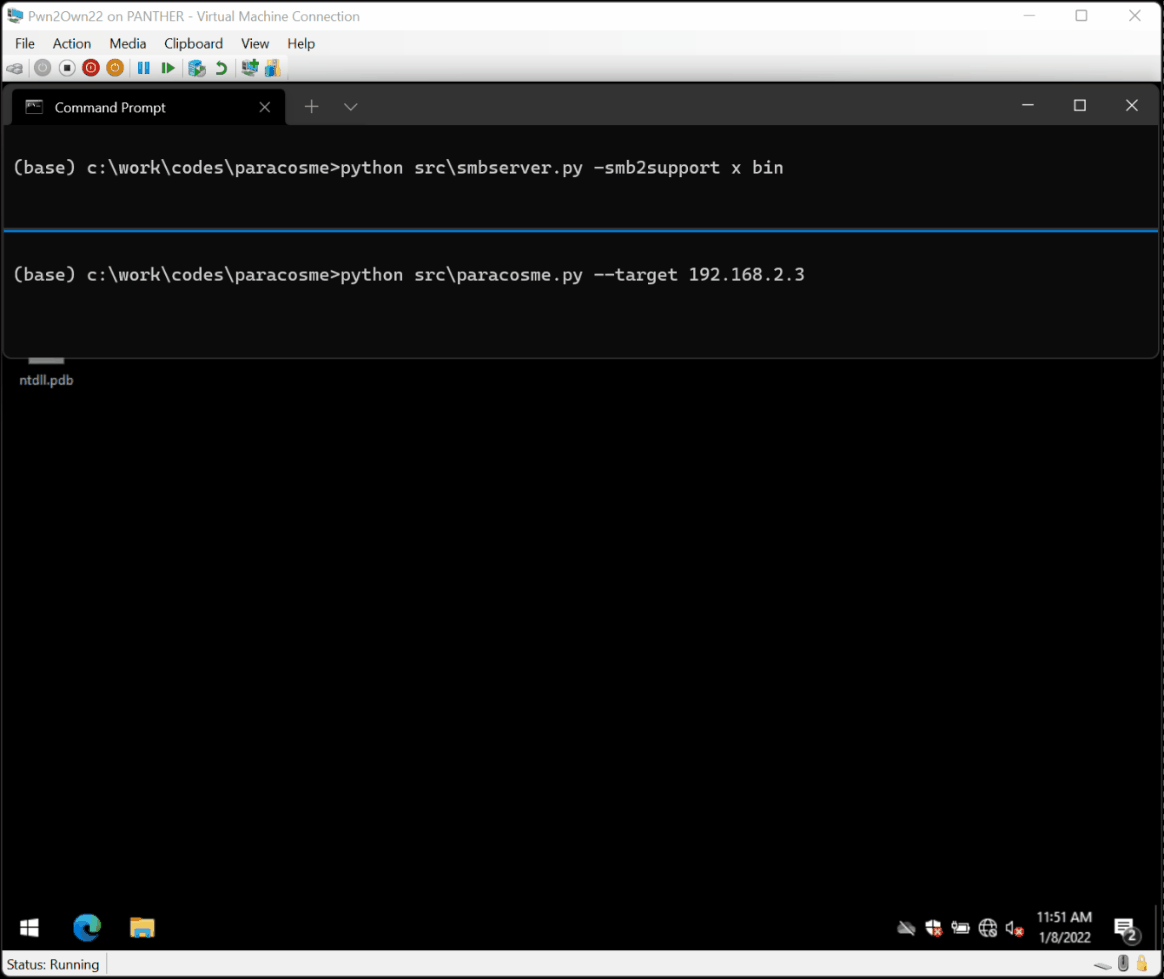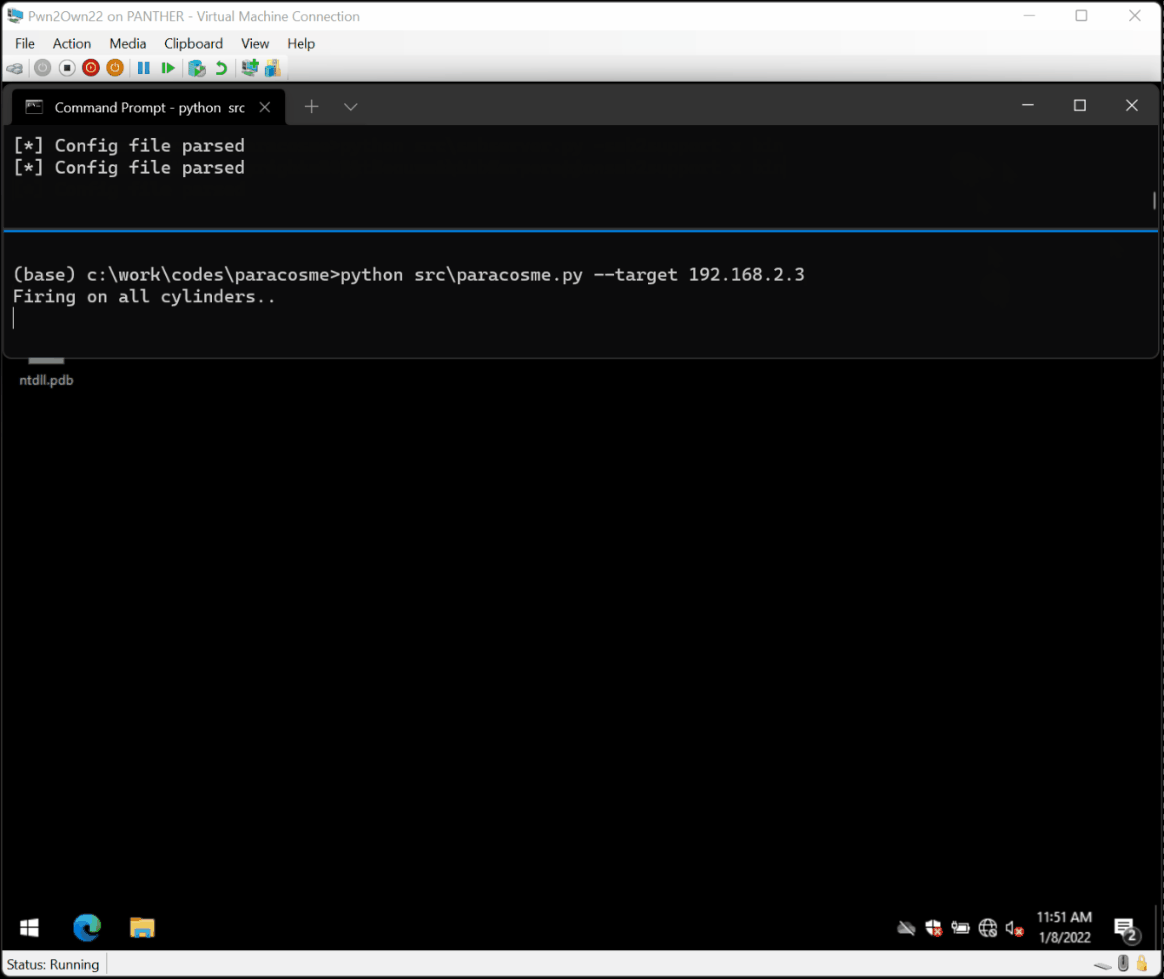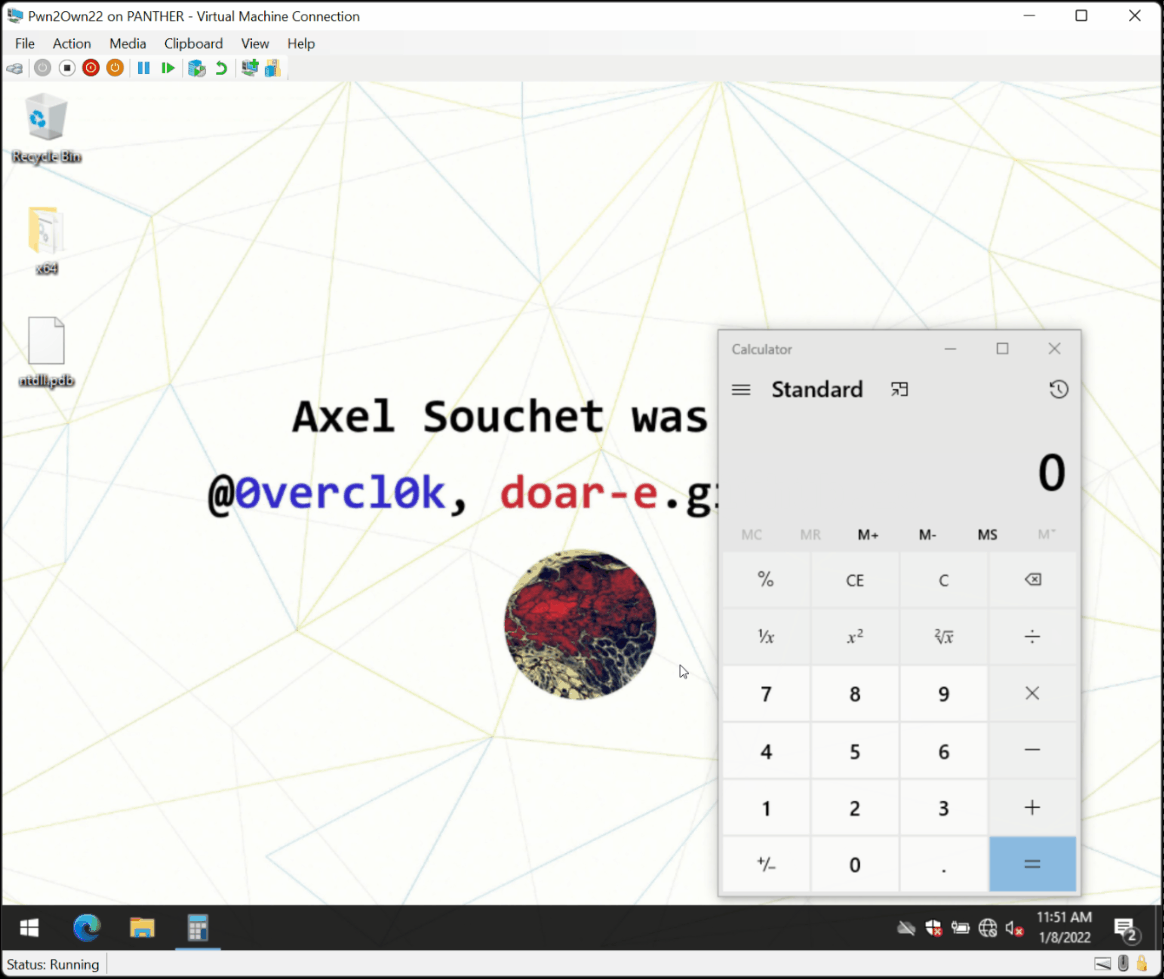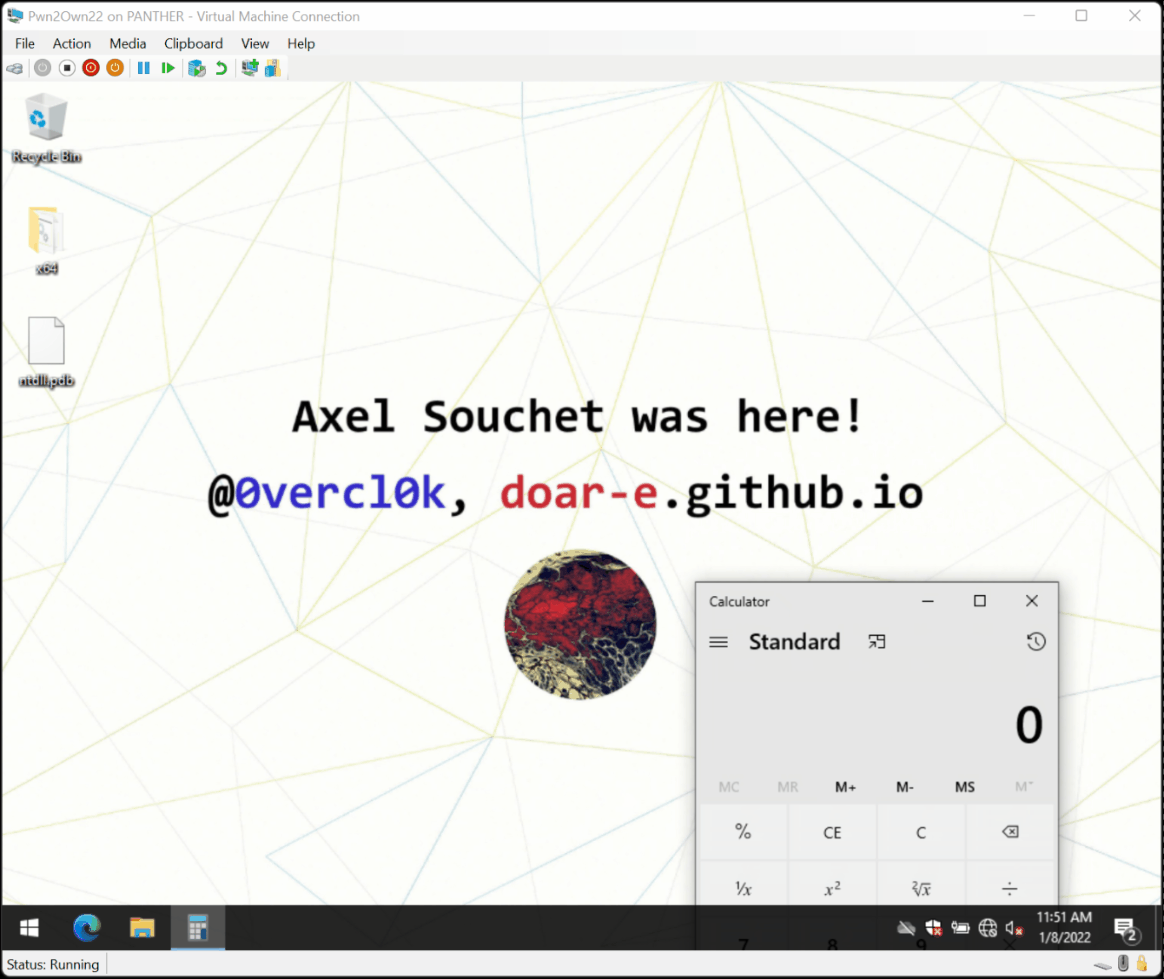
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…


SCADA Security Testing tool

A fork and successor of the Sulley Fuzzing Framework

PoC C&C for the Industroyer malware

Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748

PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.

Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver

Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A

ICS-Park Smart Park Management System v2.0

Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability

Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…

CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation

CVE-2018-7843

OpenPLC 3 WebServer Authenticated Remote Code Execution.

OpenPLC 3 WebServer Authenticated Remote Code Execution.