CVE-2021-26828_ScadaBR_RCE

Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

A curated list of resources related to Industrial Control System (ICS) security.

ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

Cybersecurity Evaluation Tool

Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian

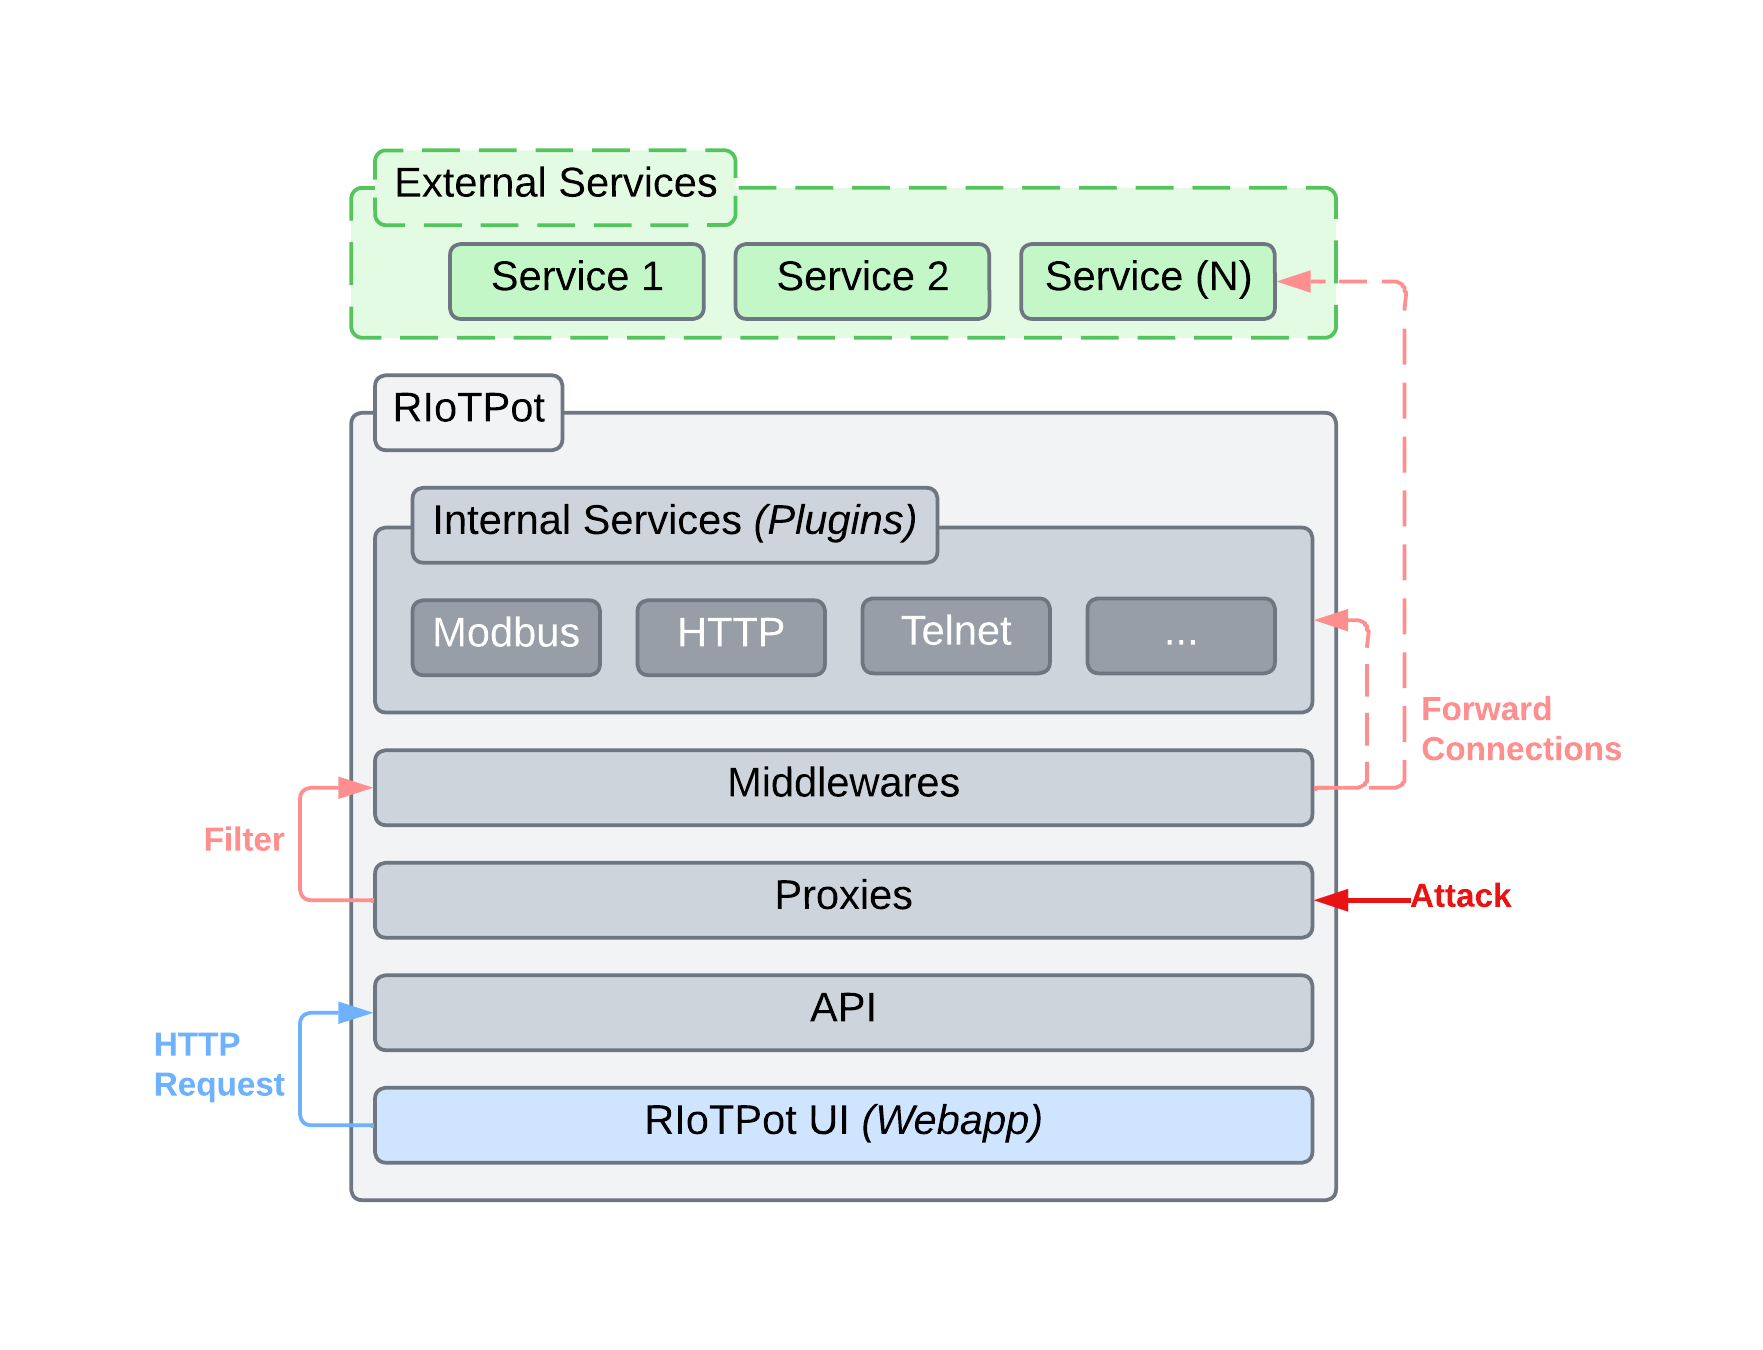
IoT and Operational Technology Honeypot


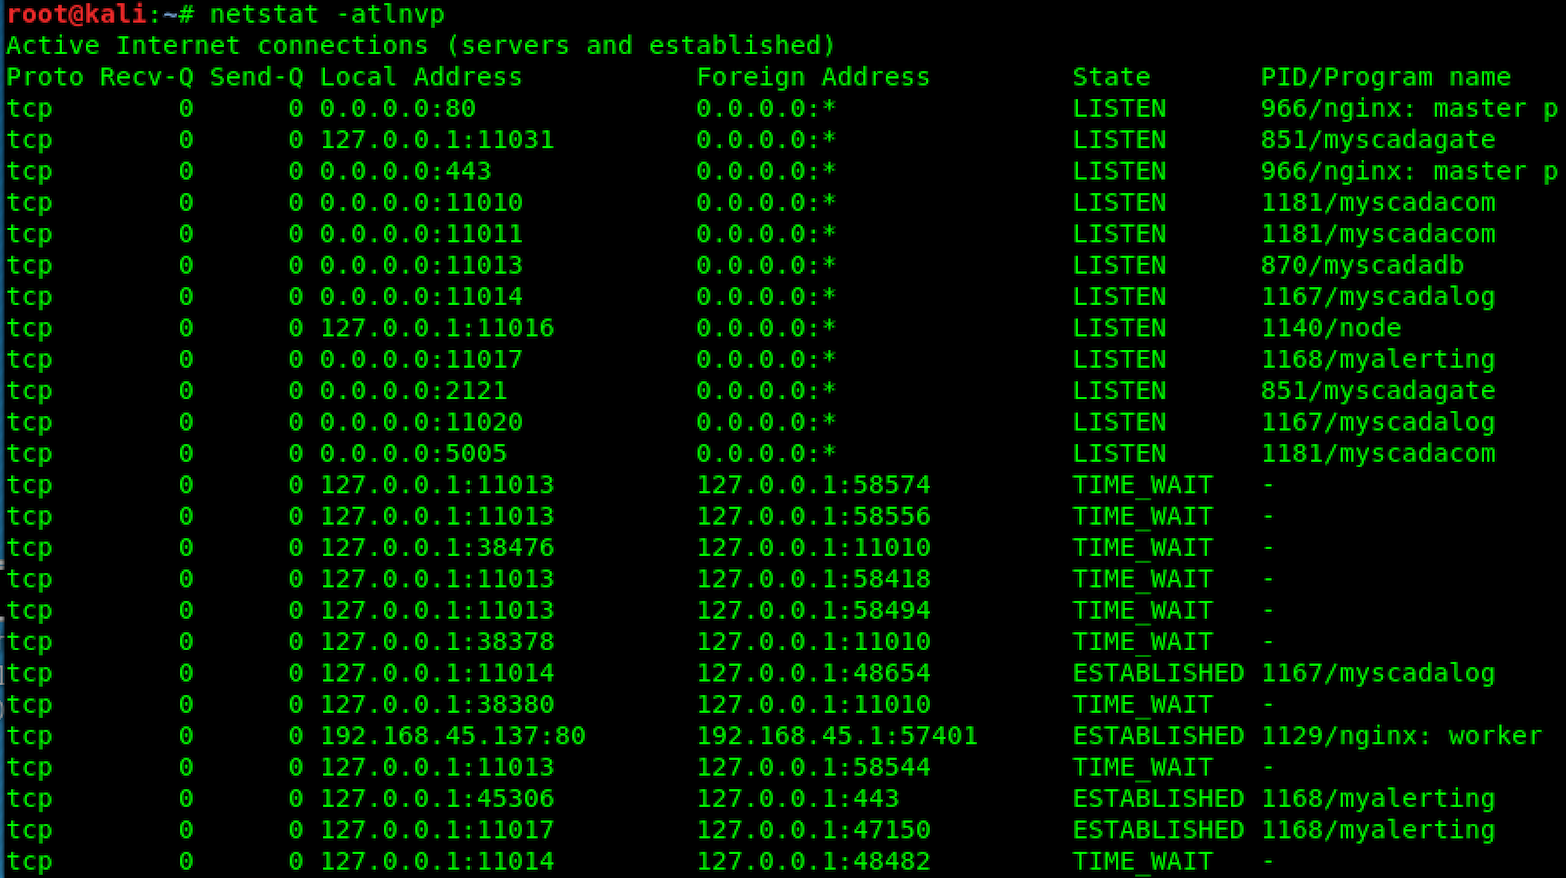
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

To reproduce CVE-2021-31630

Defensive security demo: seL4 microkernel gateway protecting vulnerable ICS from CVE-2019-14462

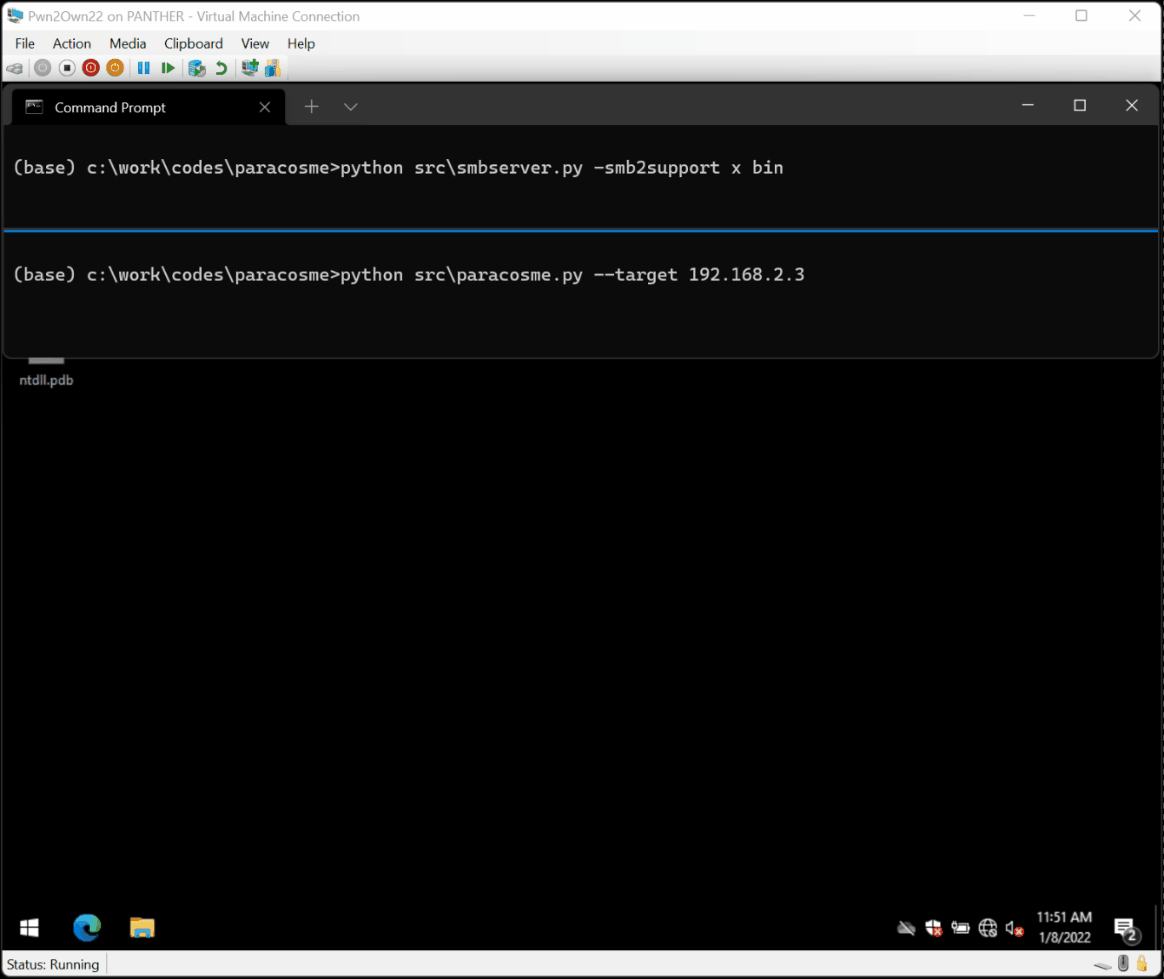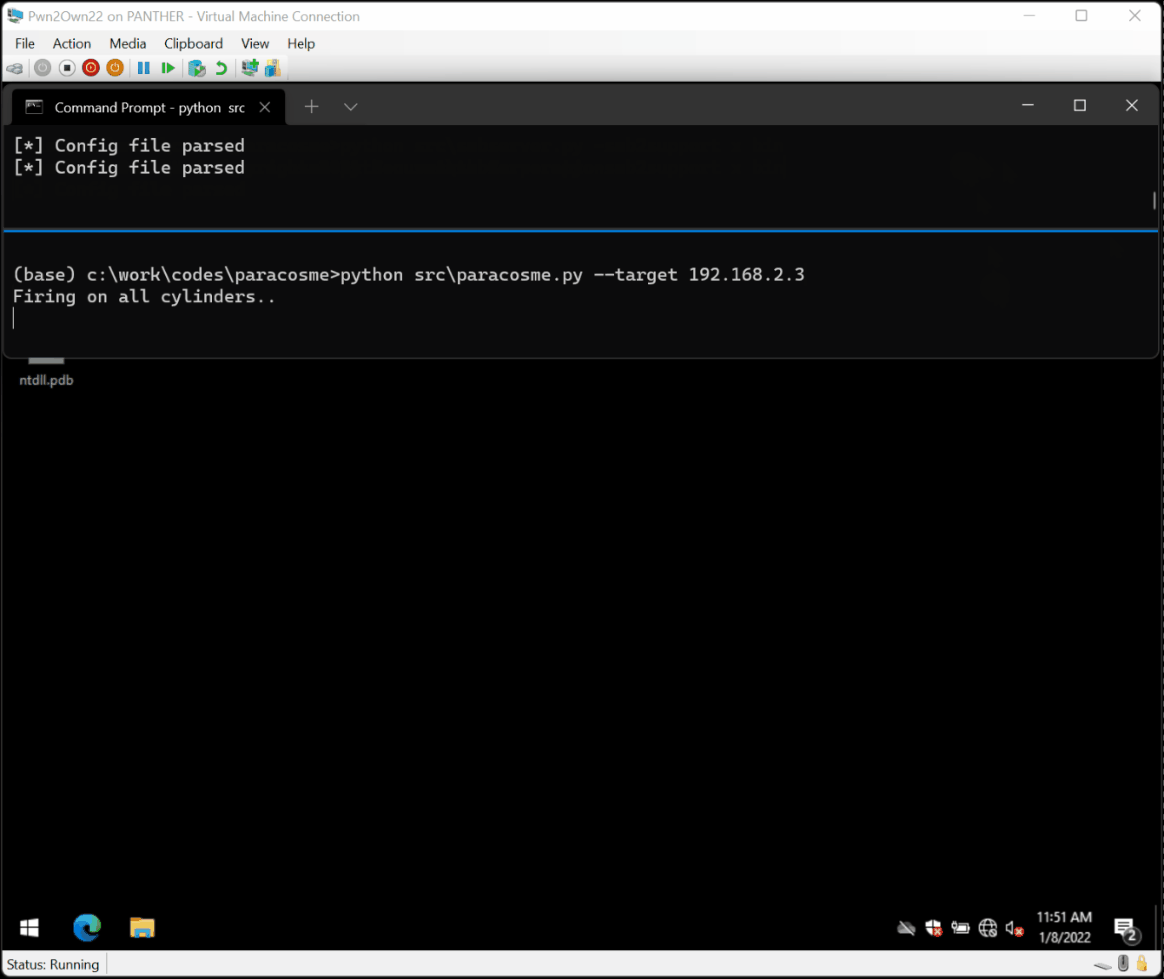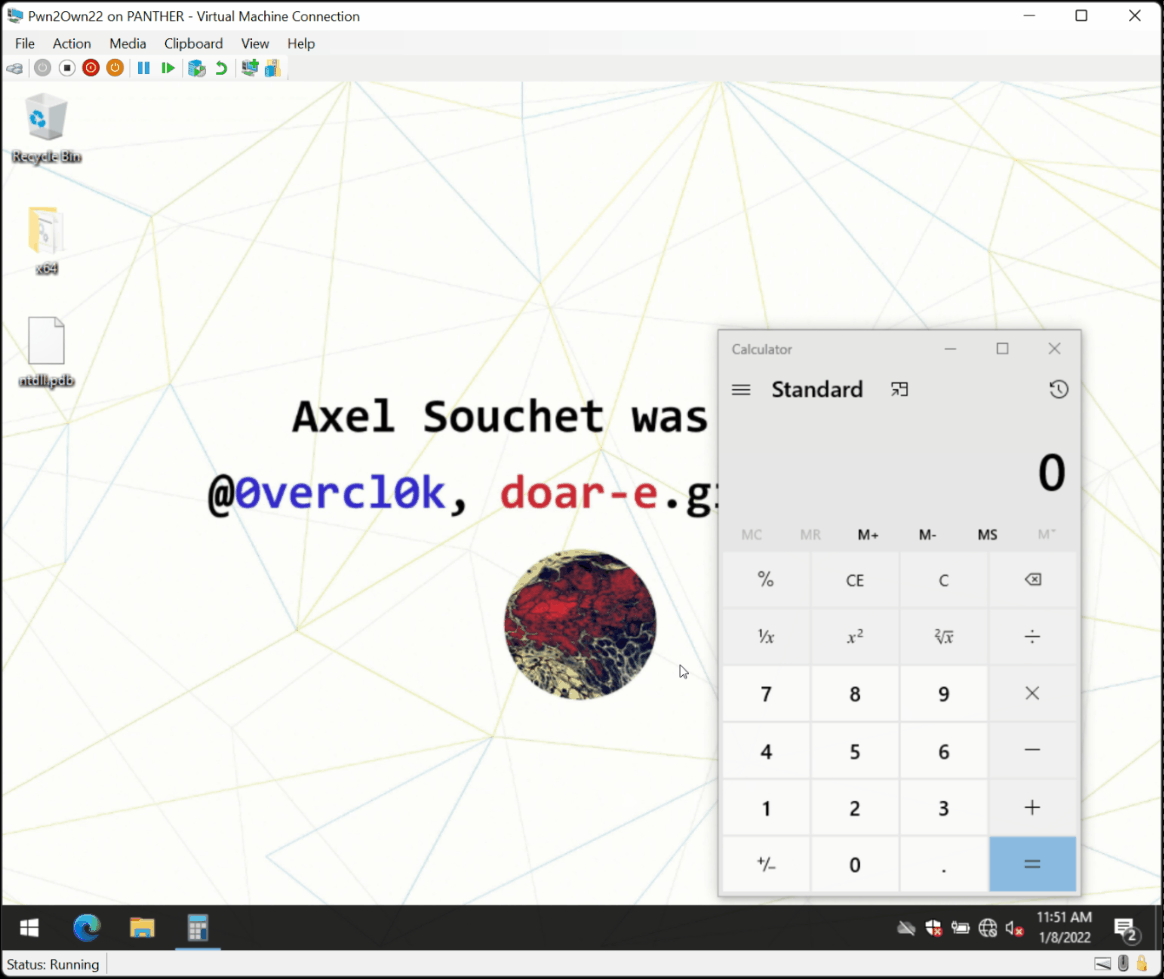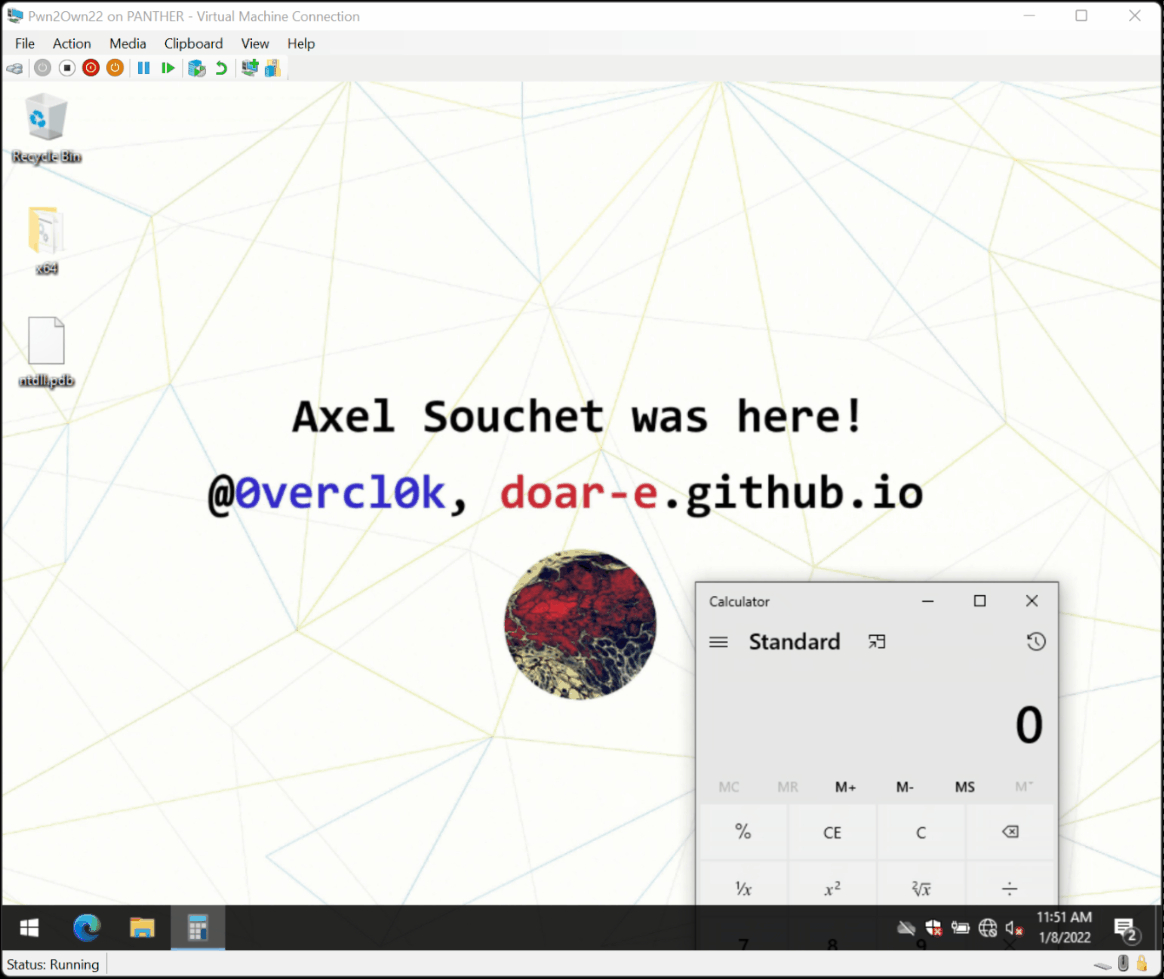
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…

OpenPLC Runtime version 3