
OpenPLC_v3
 tranquac/openplc_v3
To reproduce CVE-2021-31630
code-analysiscommand-and-controlexploitation+3
tranquac/openplc_v3To reproduce CVE-2021-31630
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
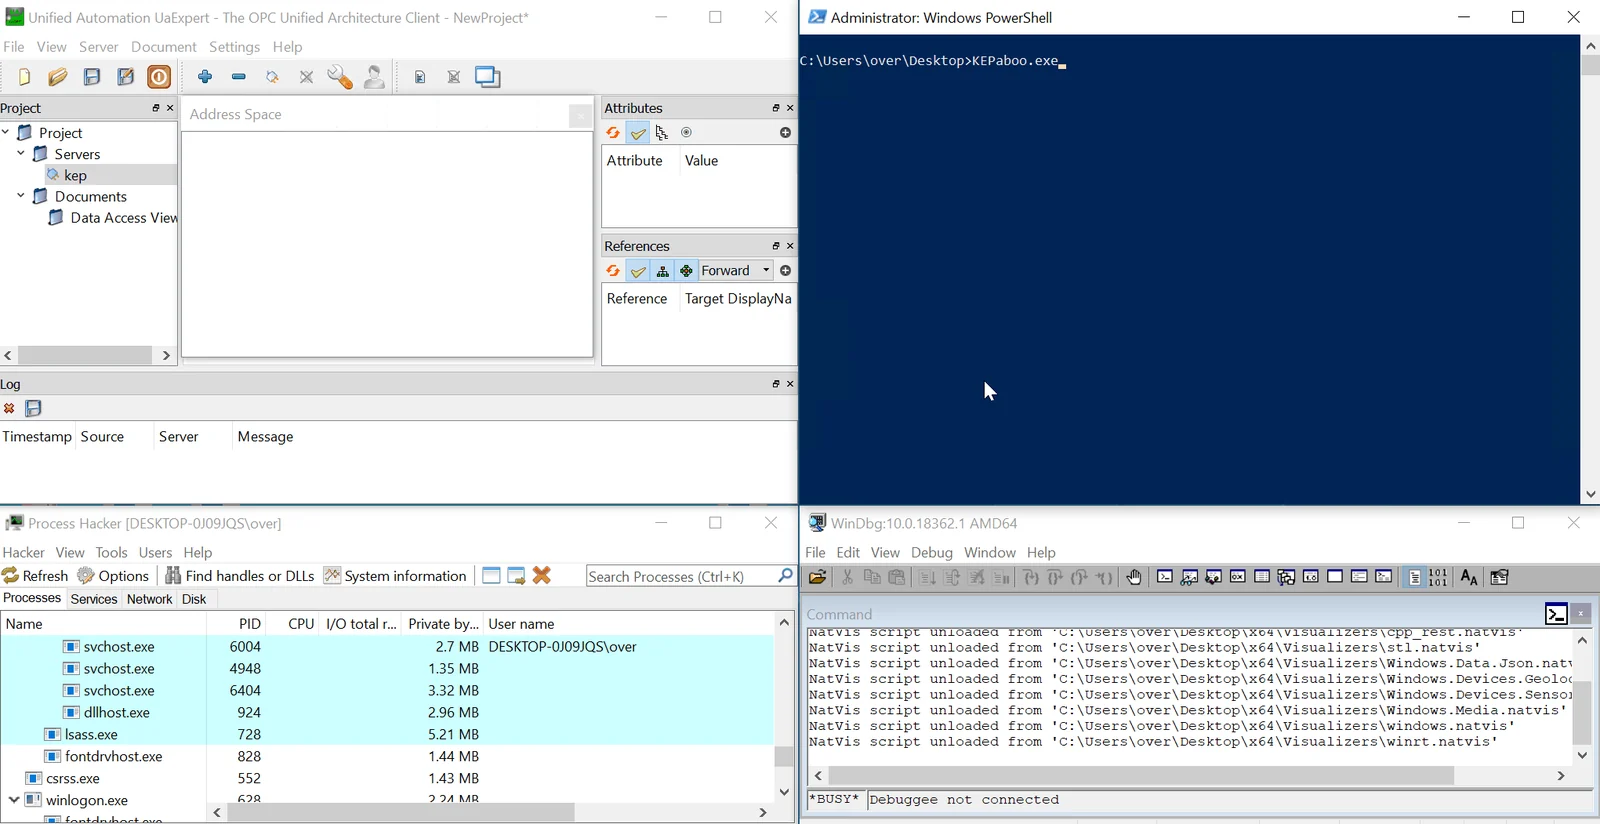 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian