CVE-2021-41579-LCDS-LAquis-SCADA-4.3.1.1085-Arbitrary-File-Write

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock

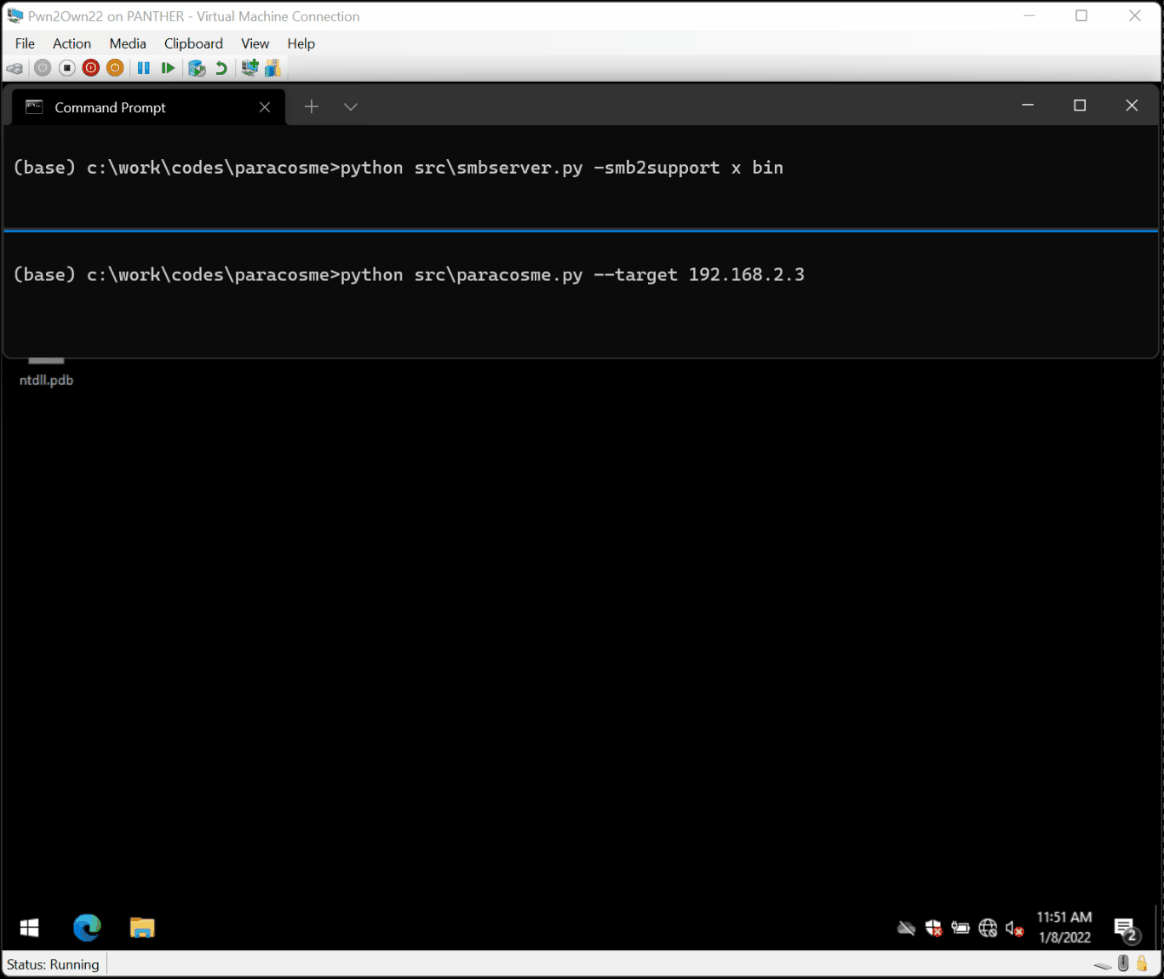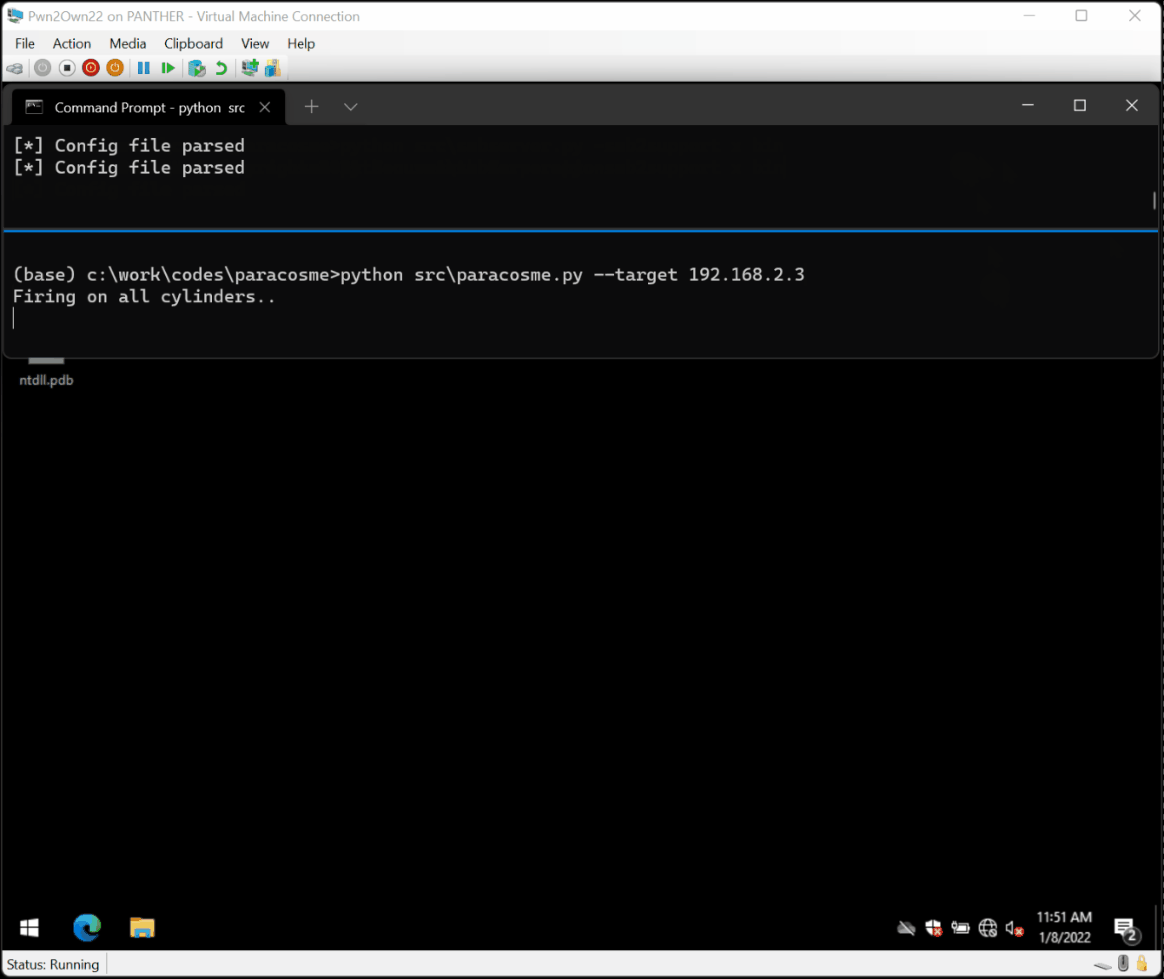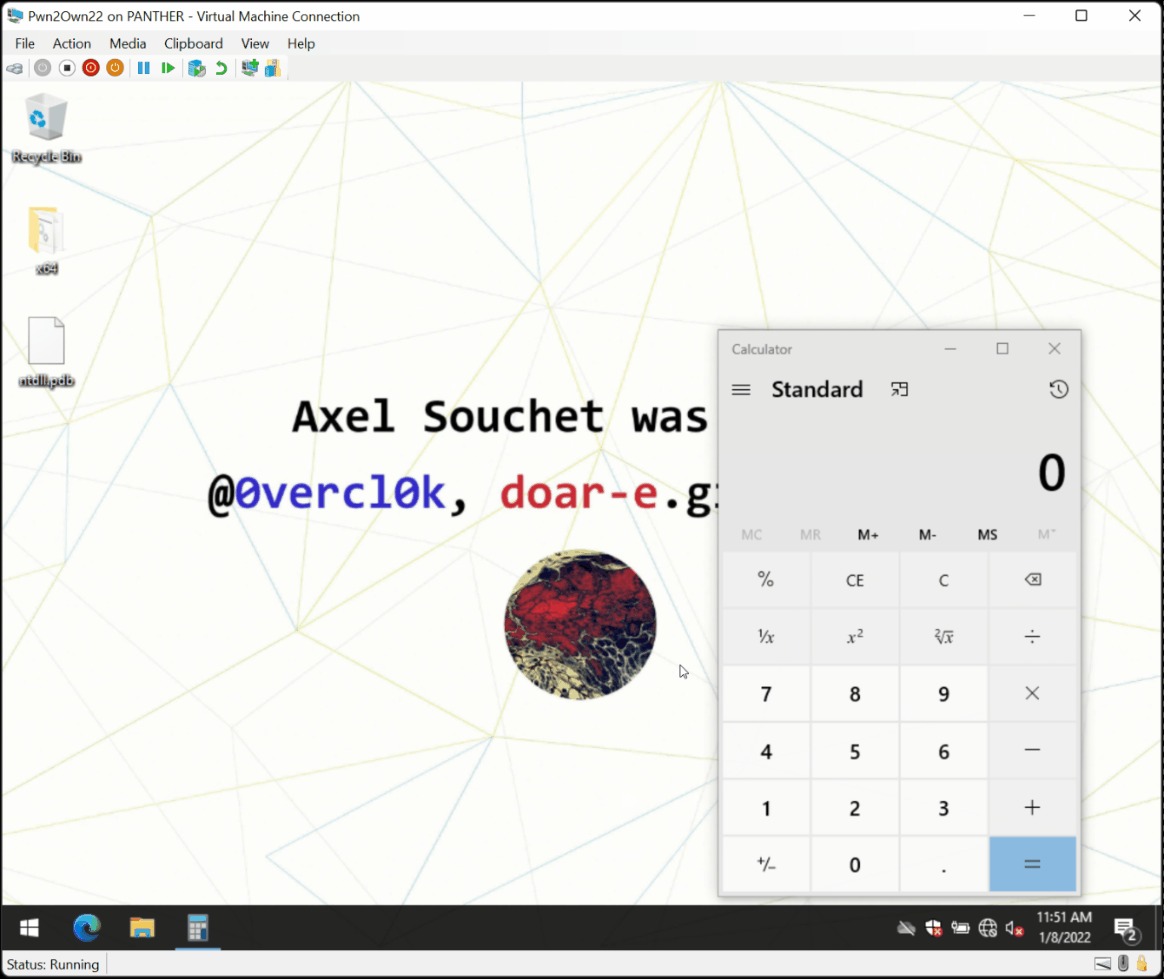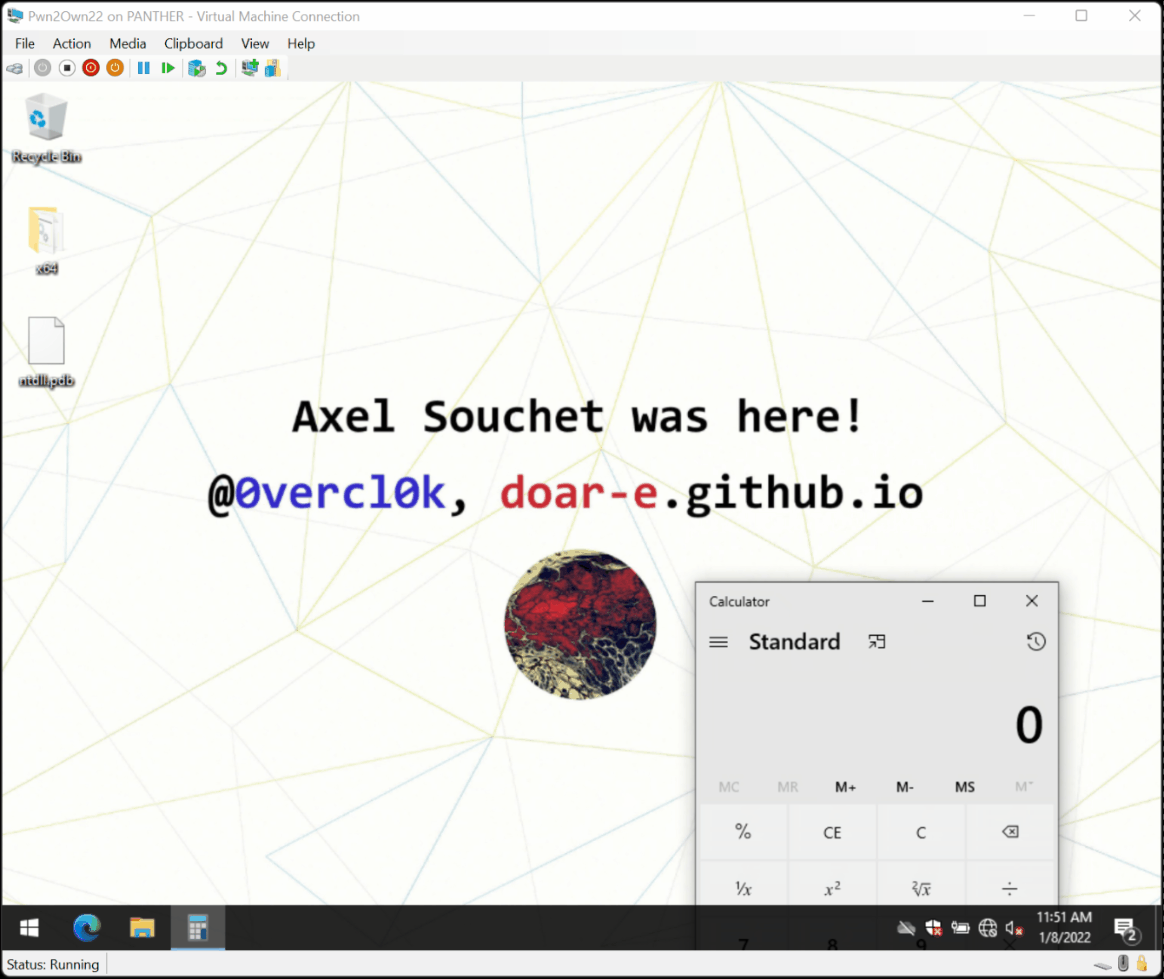
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…

proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.

Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…

Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…

This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656

Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…

CVE-2025-41646 - Critical Authentication bypass

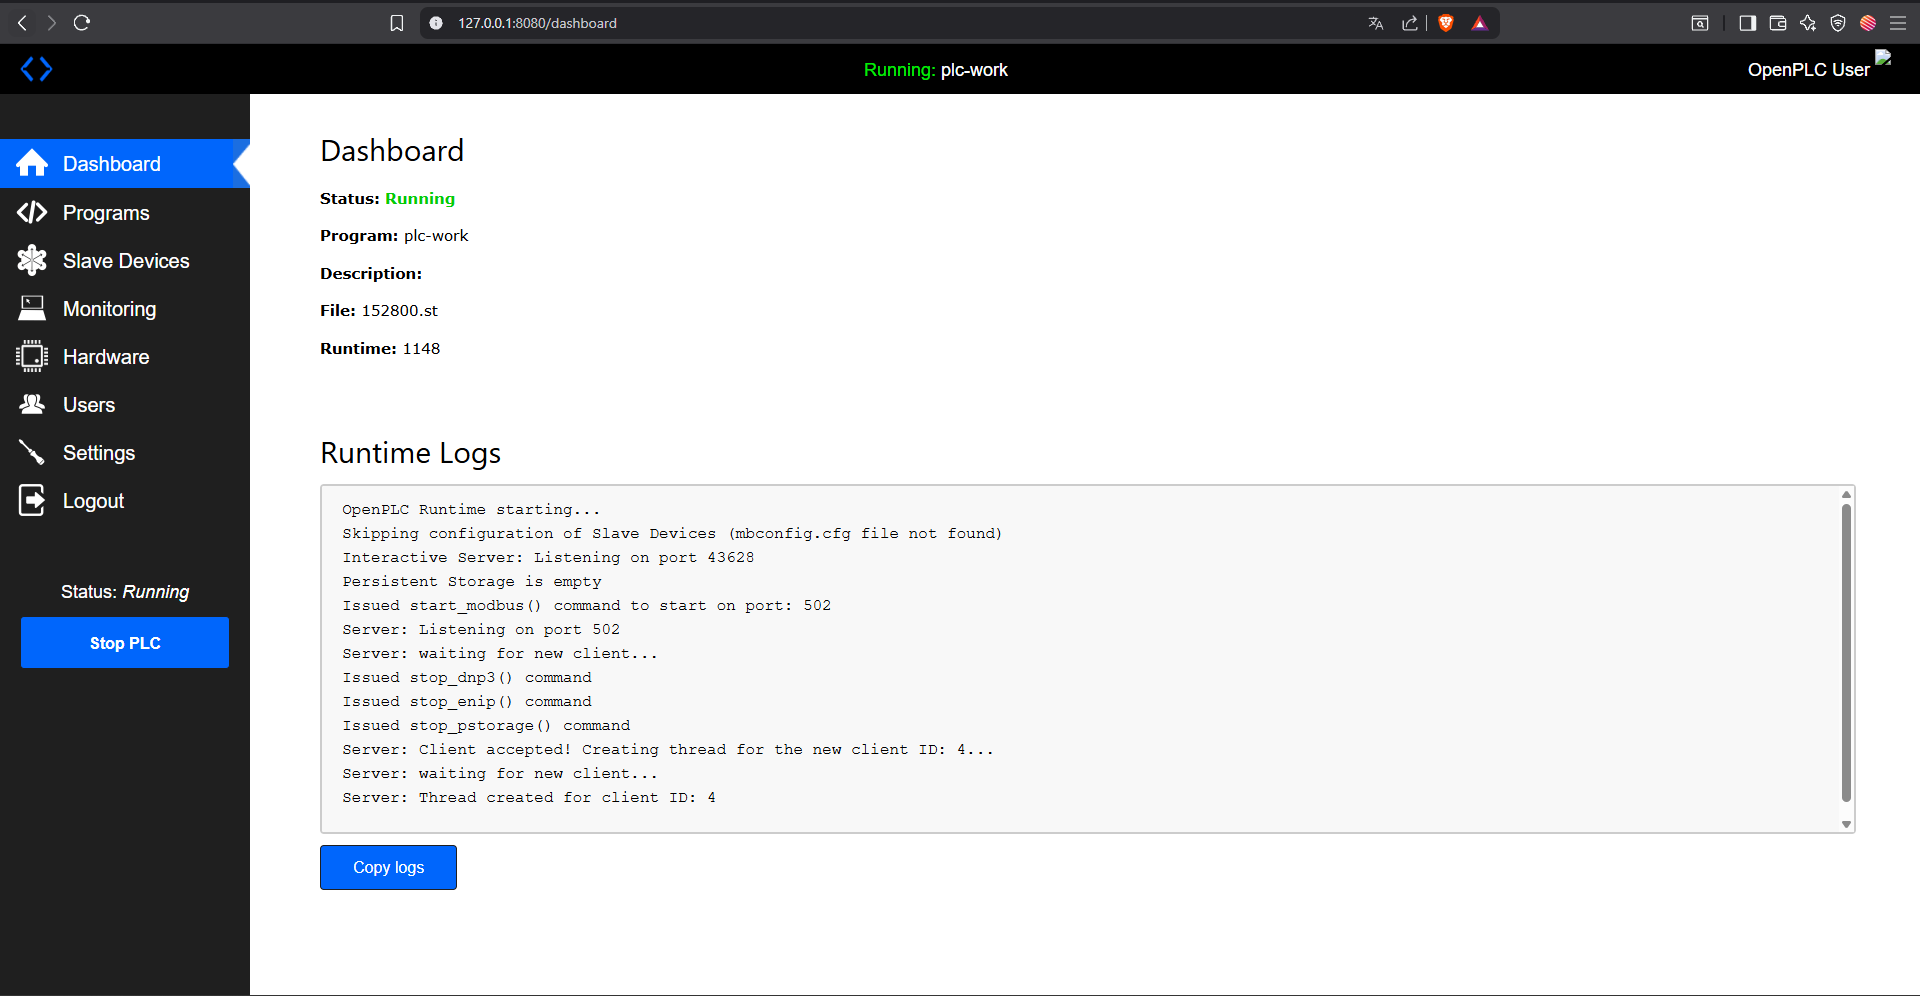
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.

CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation

Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…

Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.