
CVE-2021-31630-OpenPLC-3-Authenticated-RCE
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
command-and-controlexploitationpenetration-testing+3
mind2hex/cve-2021-31630-openplc-3-authenticated-rceOpenPLC 3 WebServer Authenticated Remote Code Execution.
 0xfml/cve-2023-30765
CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation
 aau-network-security/hostage
Low Interaction Mobile Honeypot
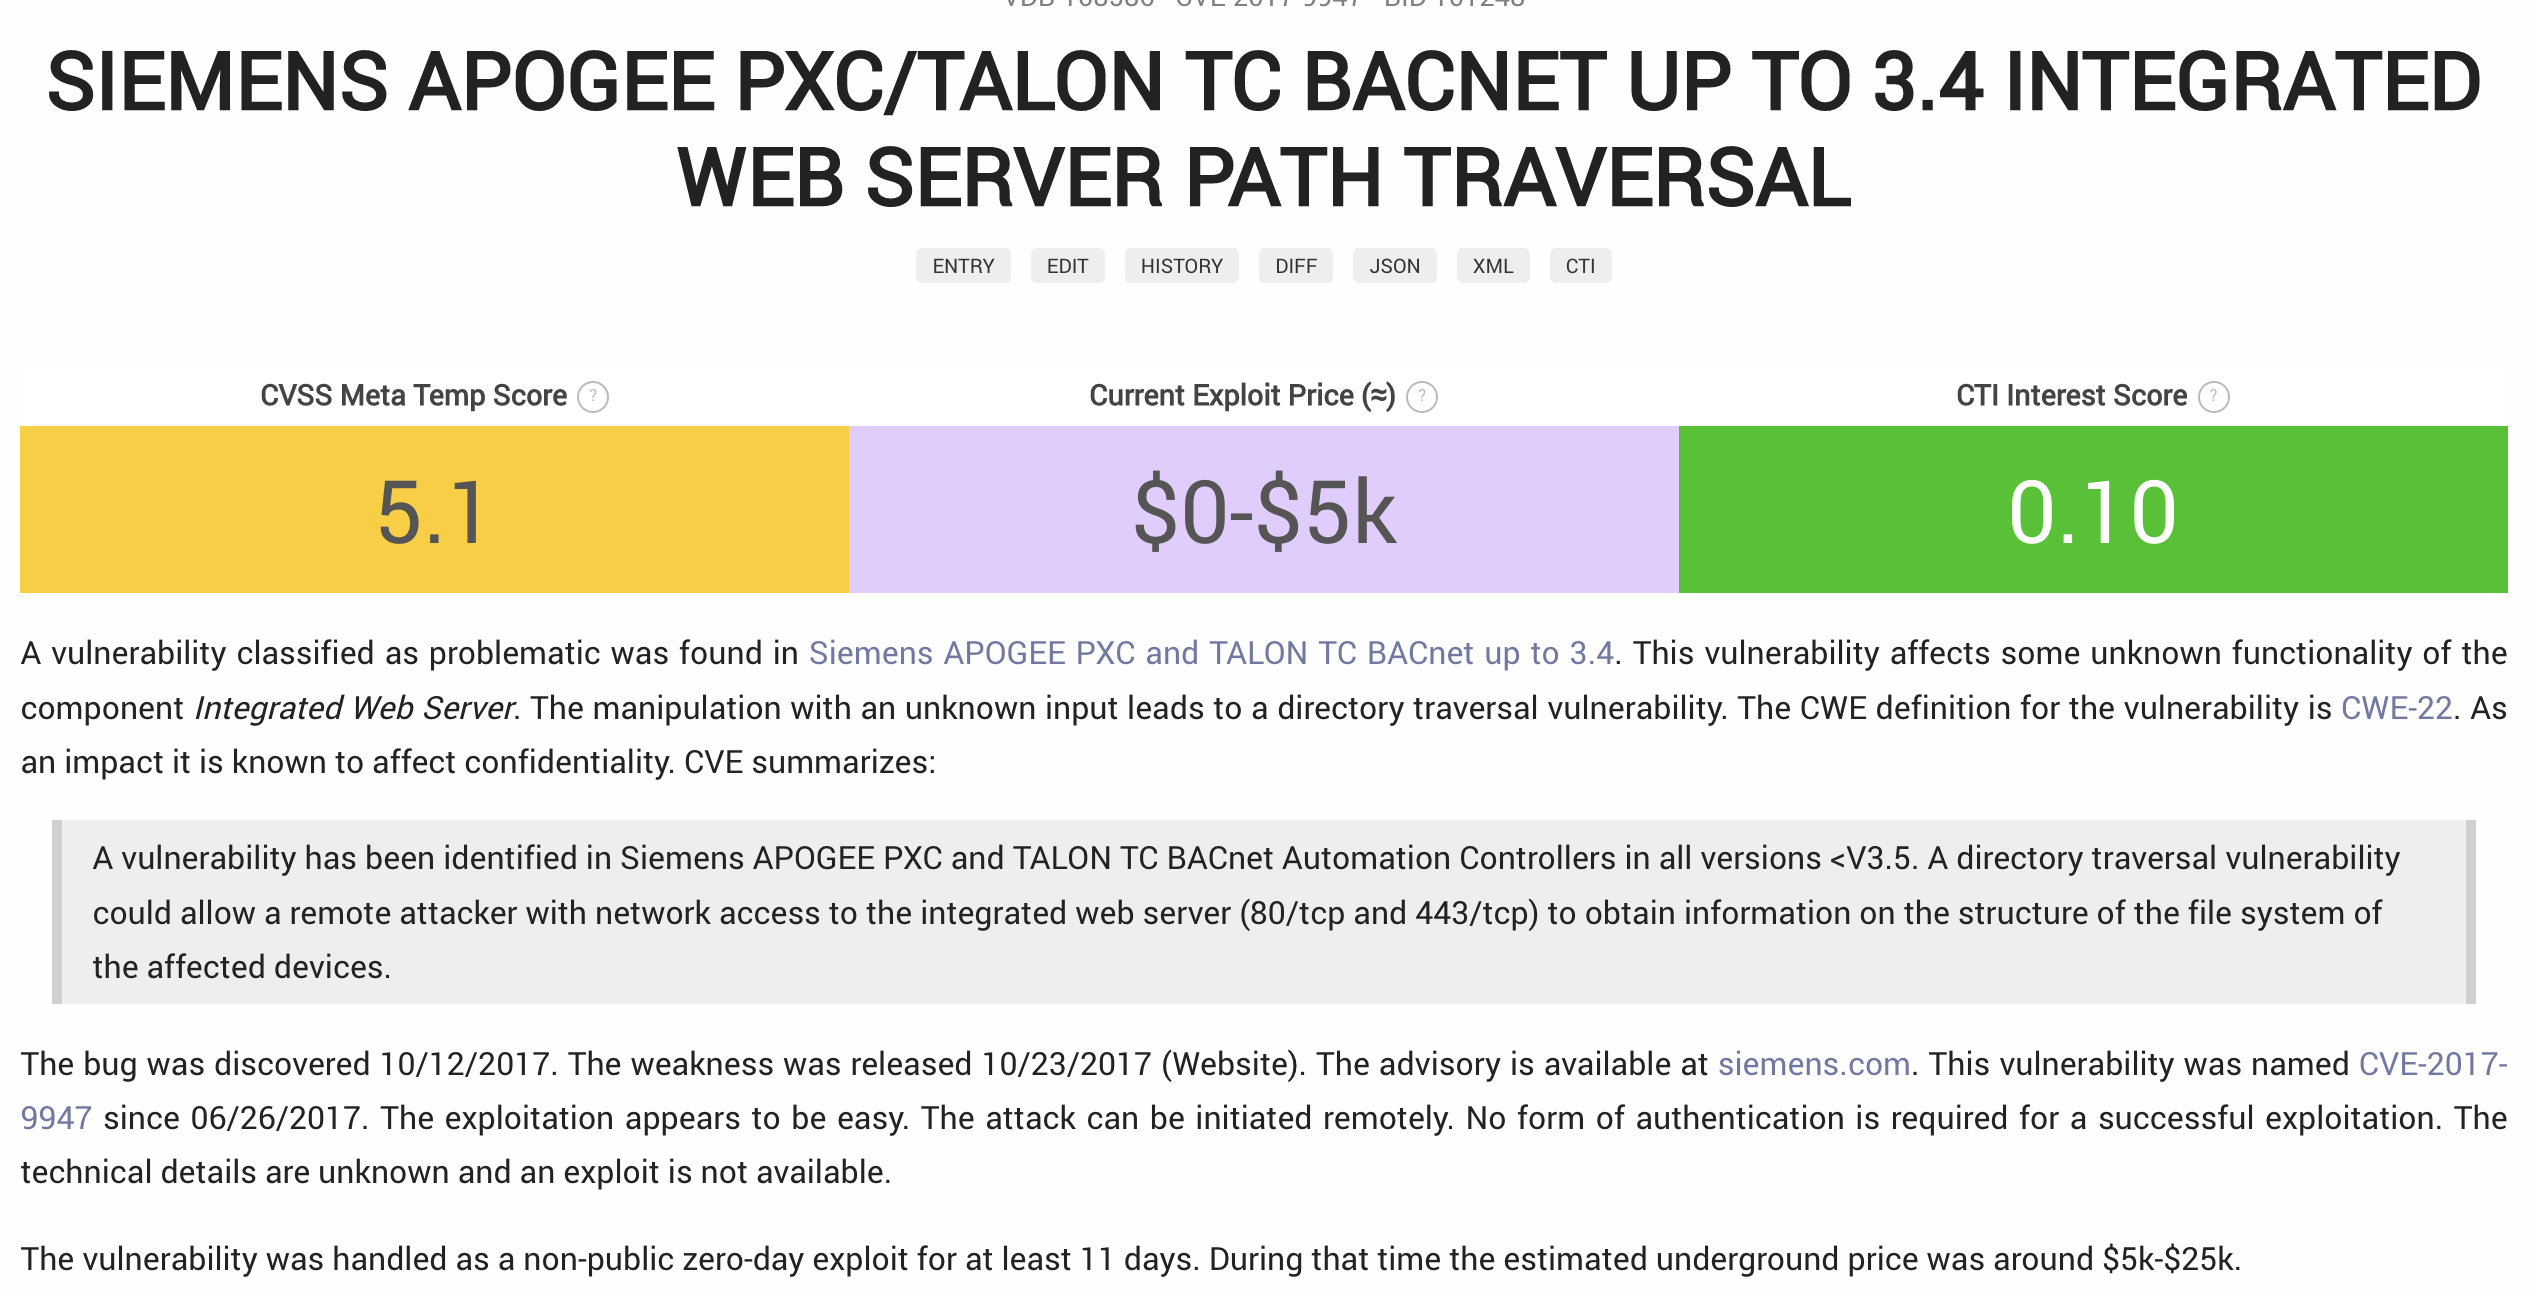 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
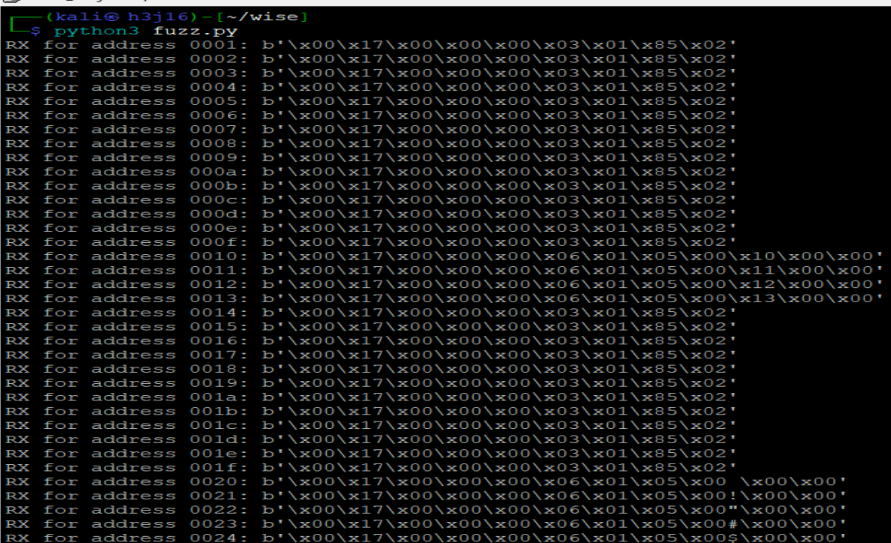 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
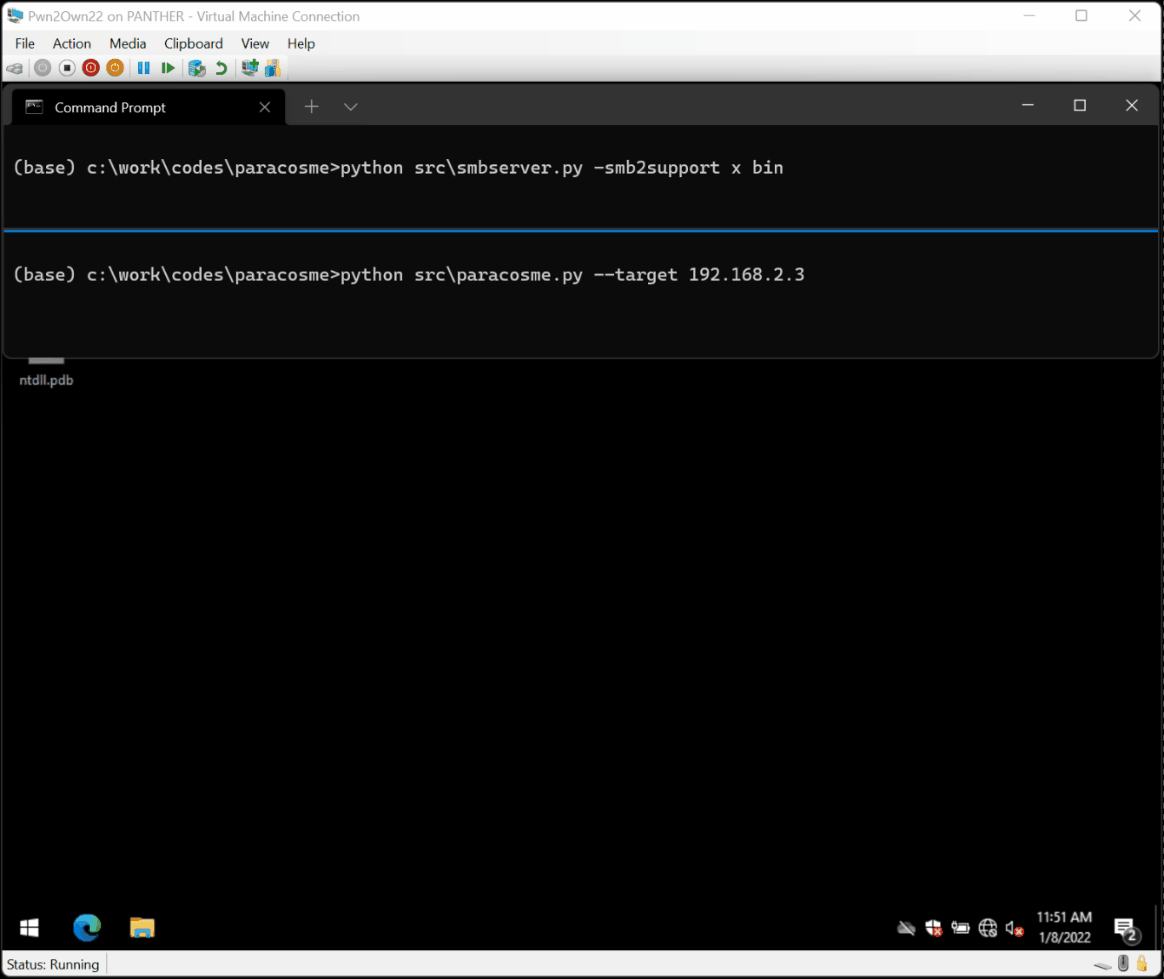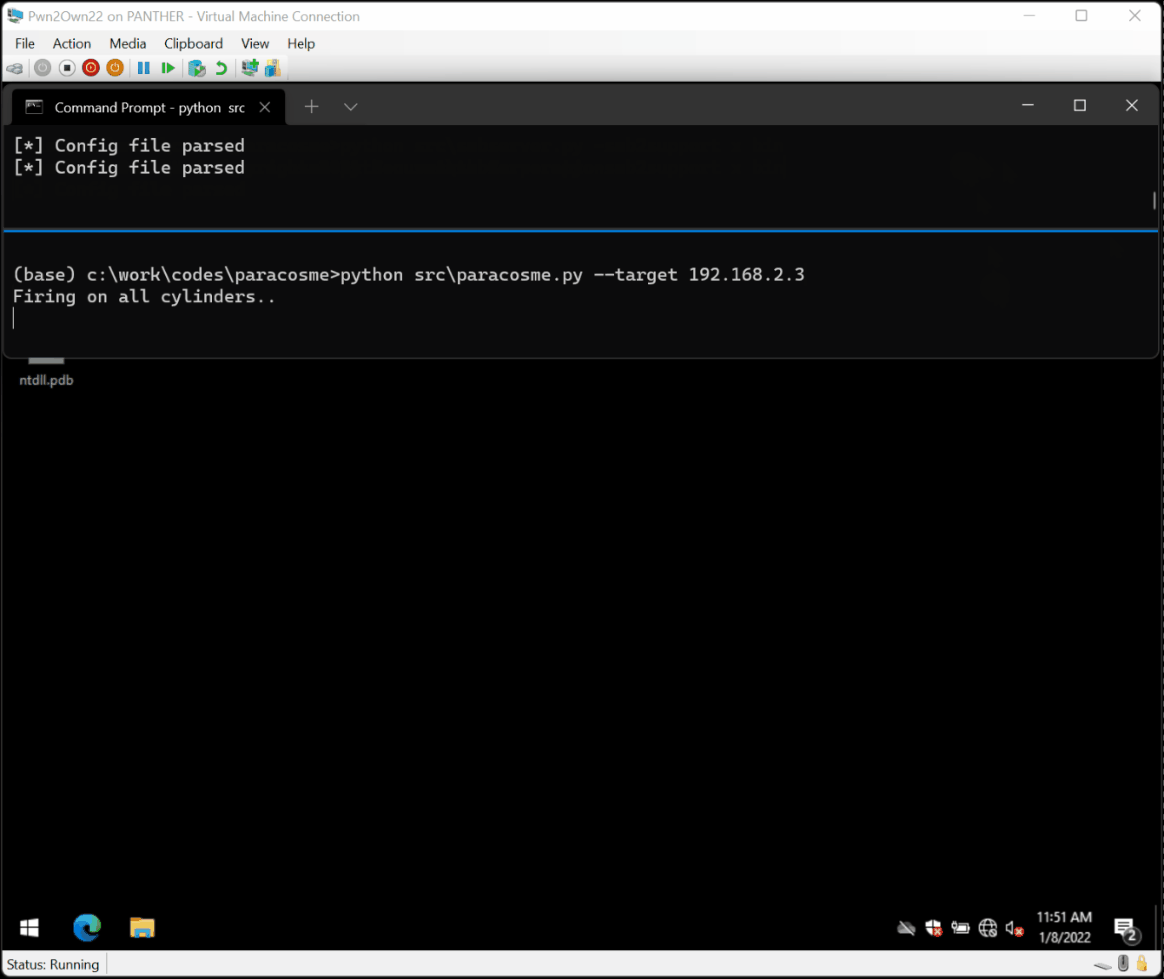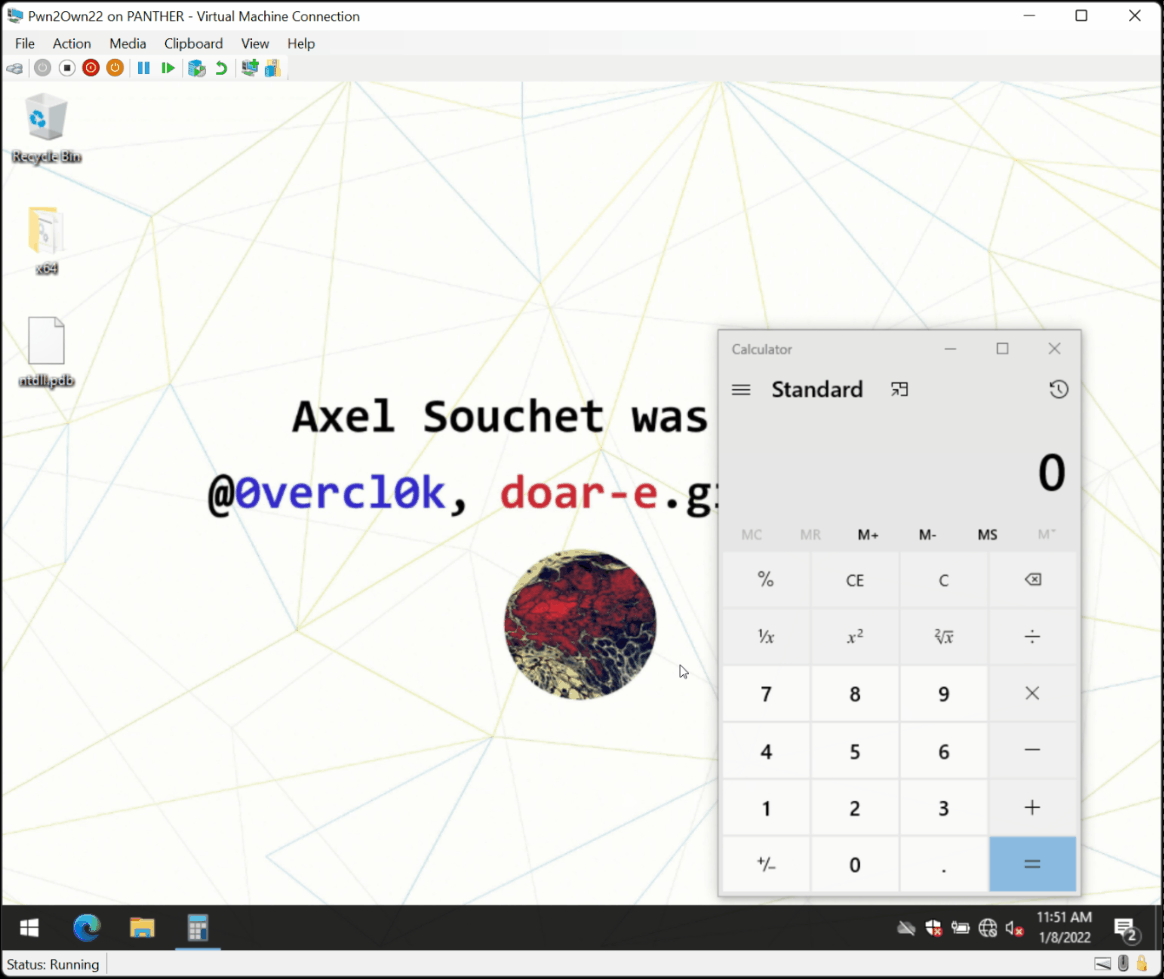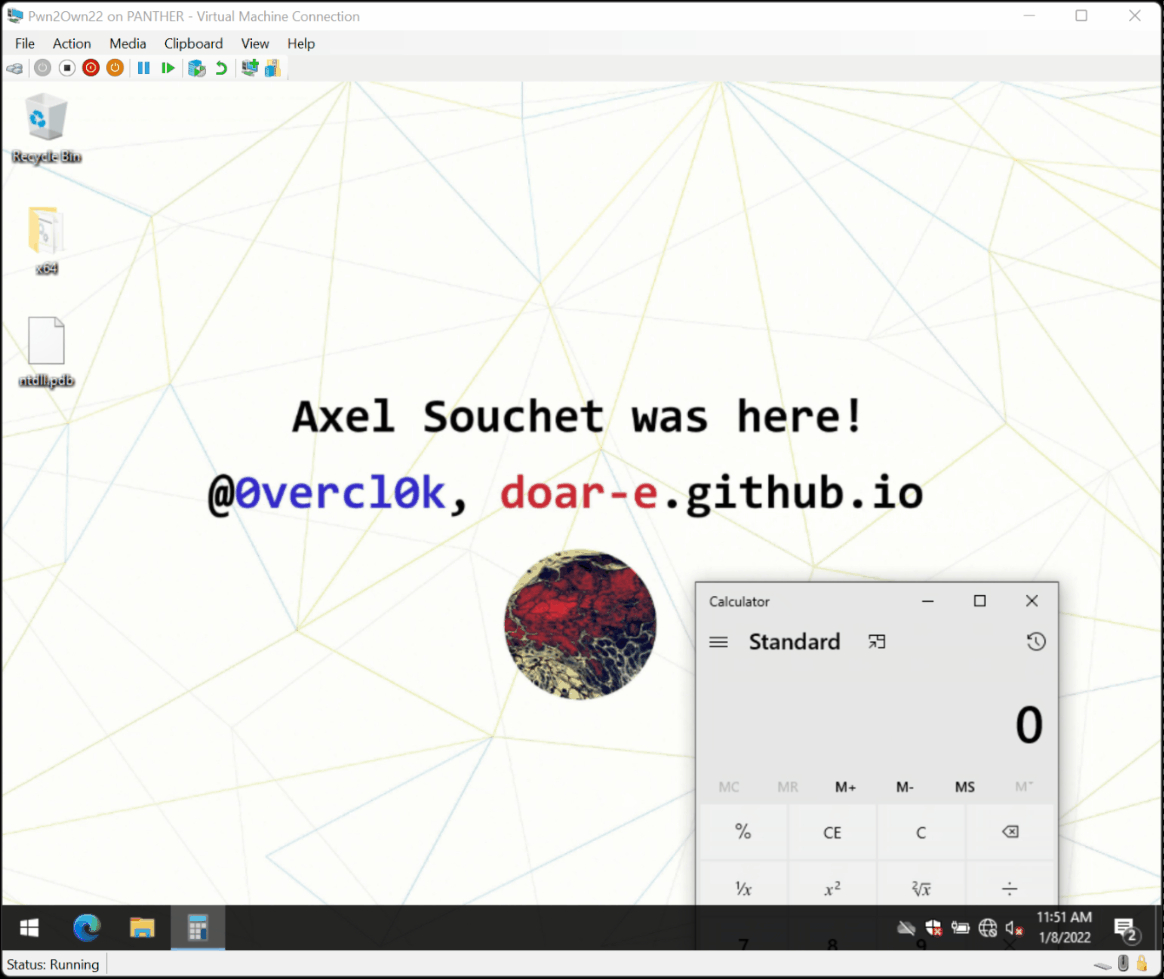 0vercl0k/paracosme
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 toxich4/cve-2023-30459
CVE-2023-30459
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats