


 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition
 reidmefirst/moxapass
Small script to retrieve passwords from many types of Moxa device, including NPort, OnCell, MGate, etc.
 sbaresearch/amlsec
Automated Security Risk Identification Using AutomationML-based Engineering Data
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 abhinavagarwal07/scadapack-secure-lock-poc
Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
 akbarq/cve-2009-0473-check
Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
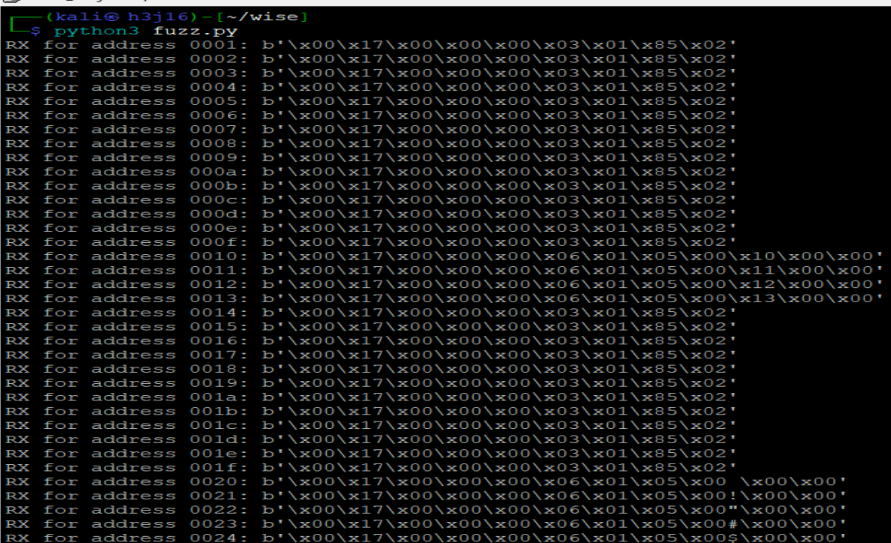 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 0xicf/panelshock
Schneider Electric Magelis HMI Resource Consumption Vulnerabilities [ICSA-16-308-02, CVE-2016-8367, CVE-2016-8374]
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…