
OpenPLC_v3
 tranquac/openplc_v3
To reproduce CVE-2021-31630
code-analysiscommand-and-controlexploitation+3
tranquac/openplc_v3To reproduce CVE-2021-31630
 mbanyamer/cve-2021-41579-lcds-laquis-scada-4.3.1.1085-arbitrary-file-write
Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 kevinherron/stack-overflow-poc
PoC for CVE-2018-12086 affecting various OPC UA stacks
 0xfml/cve-2023-30765
CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation
 yanissec/cve-2018-7843
CVE-2018-7843
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
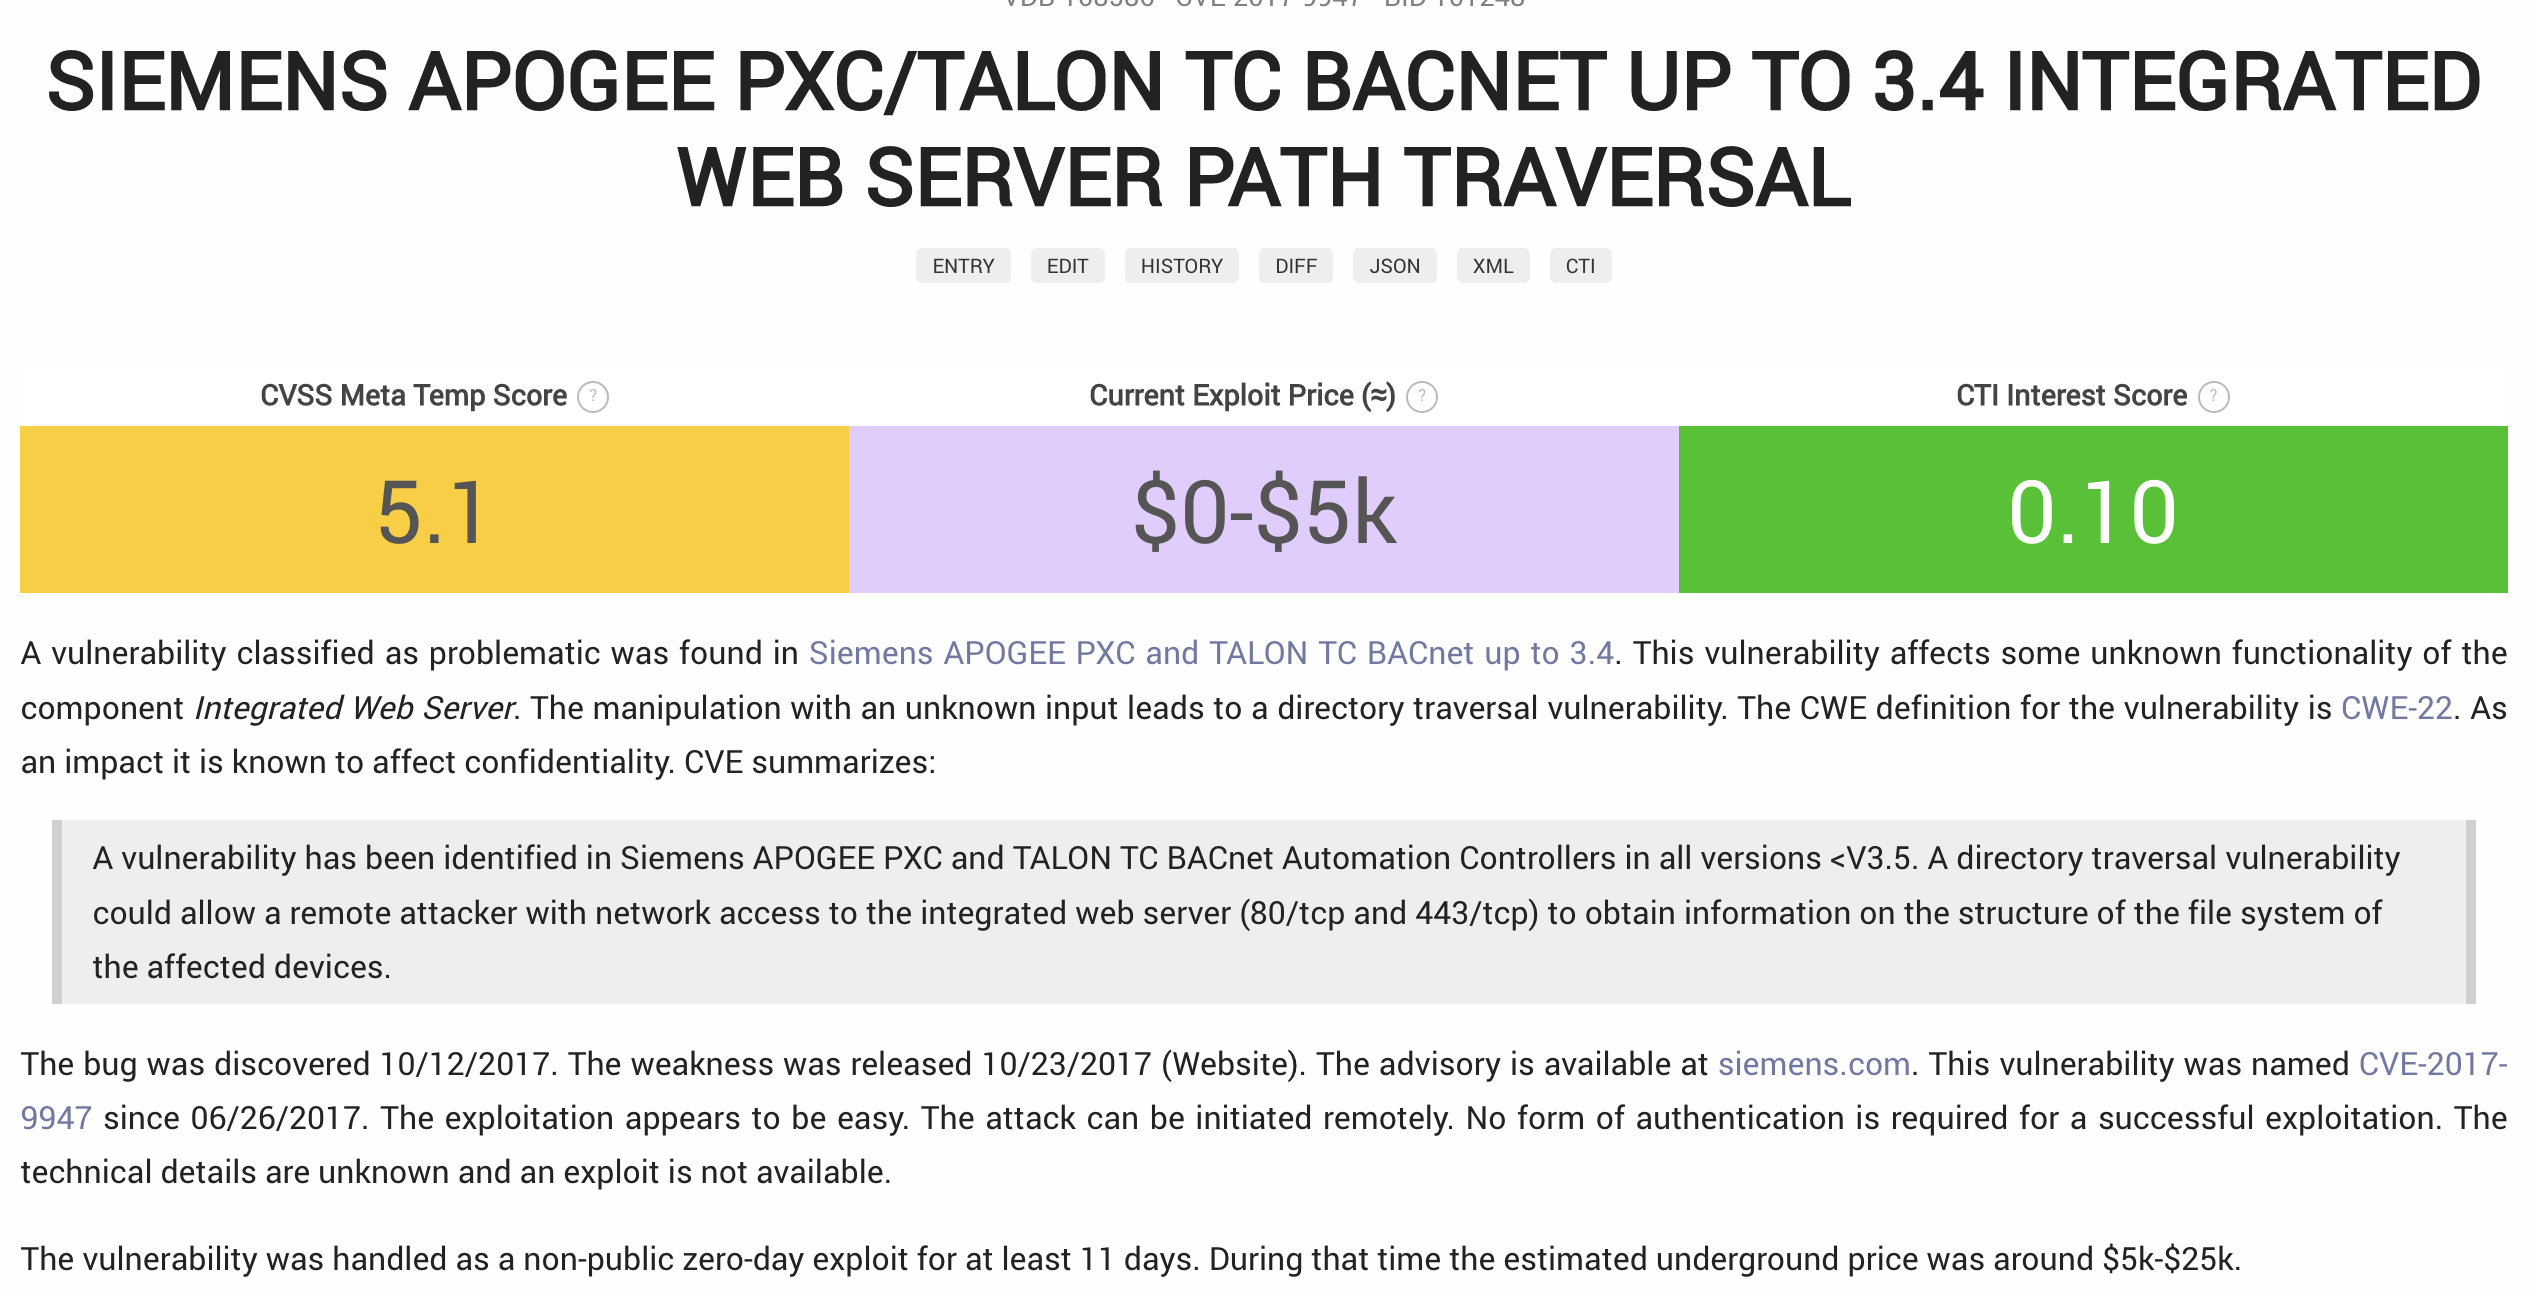 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 thezdi/poc
Collection of proof-of-concept exploits and vulnerability research artifacts published by Trend Micro's Zero Day Initiative, covering SCADA, RPC, and…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 kernoelpanic/cve-2015-8299
Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…