
0day-Rubbish
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
ai-securitycurated-resourcesexploitation+3
227
exploit-garbage/0day-rubbishRedefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 reidmefirst/moxapass
Small script to retrieve passwords from many types of Moxa device, including NPort, OnCell, MGate, etc.
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 kevinherron/stack-overflow-poc
PoC for CVE-2018-12086 affecting various OPC UA stacks
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 0vercl0k/paracosme
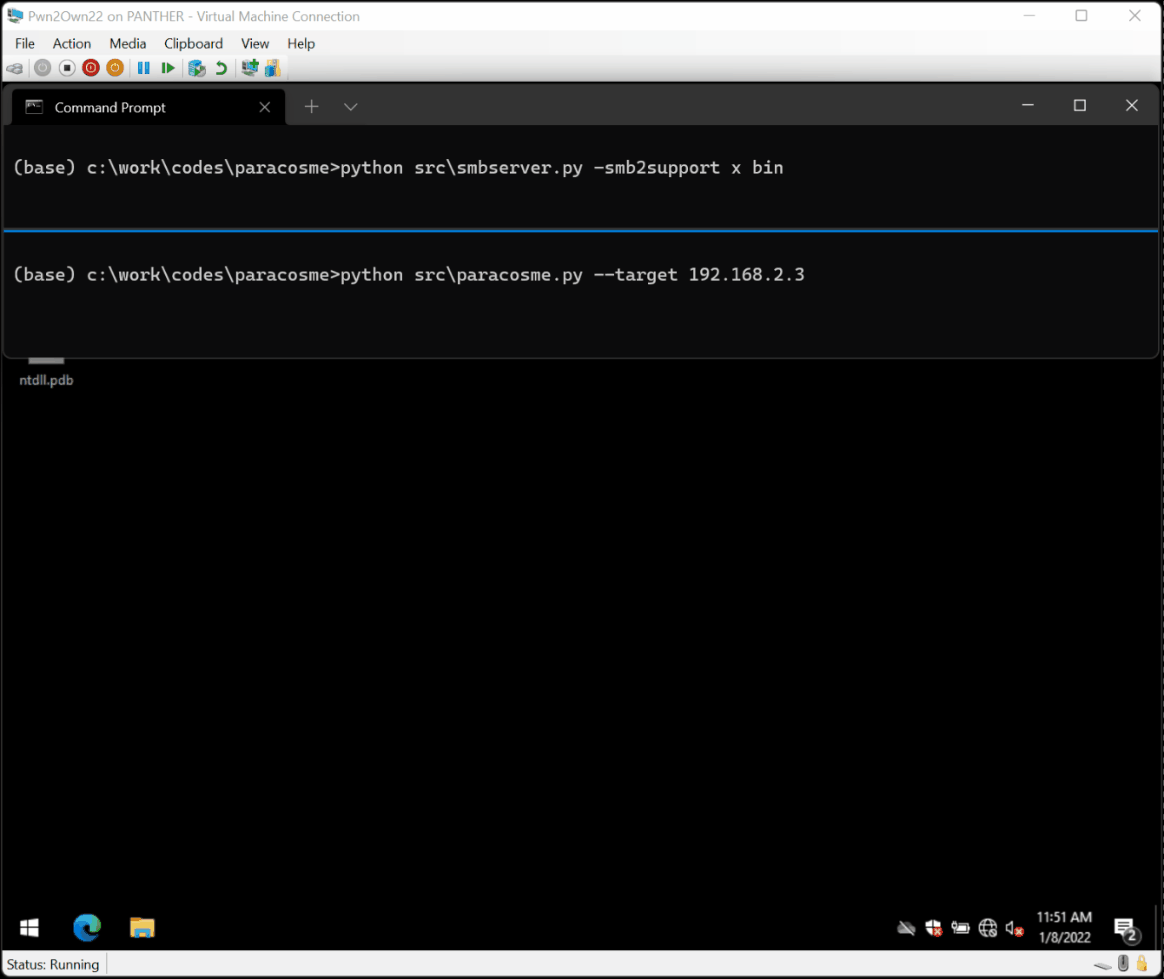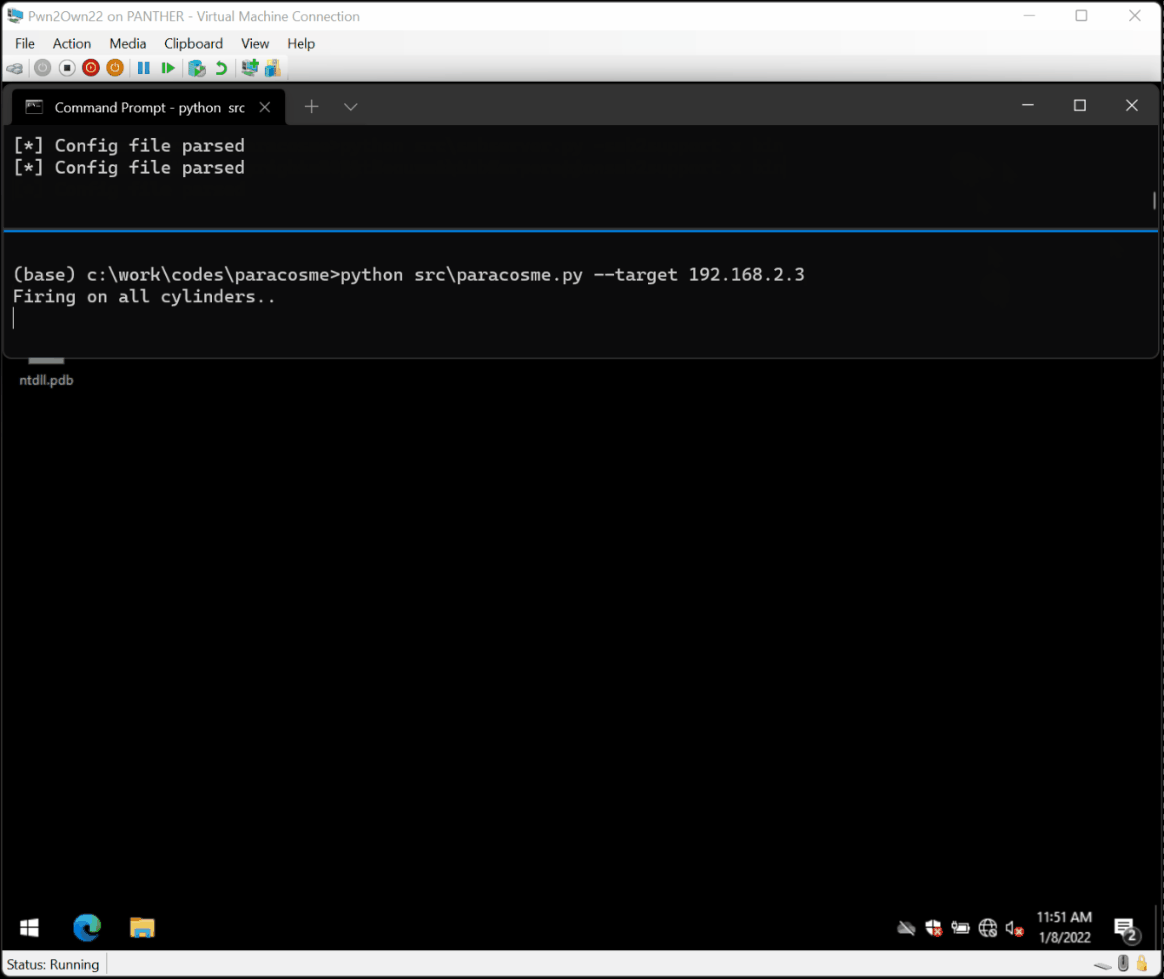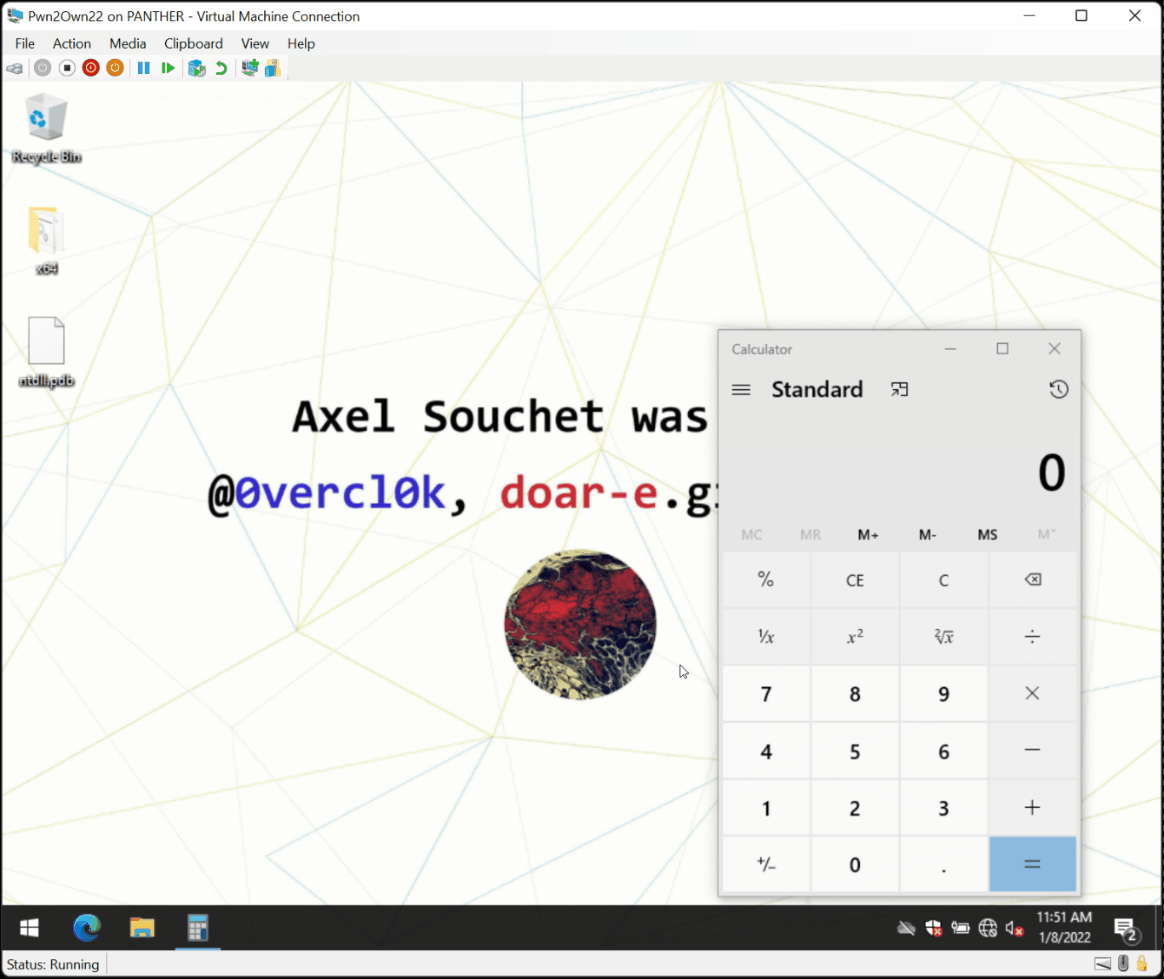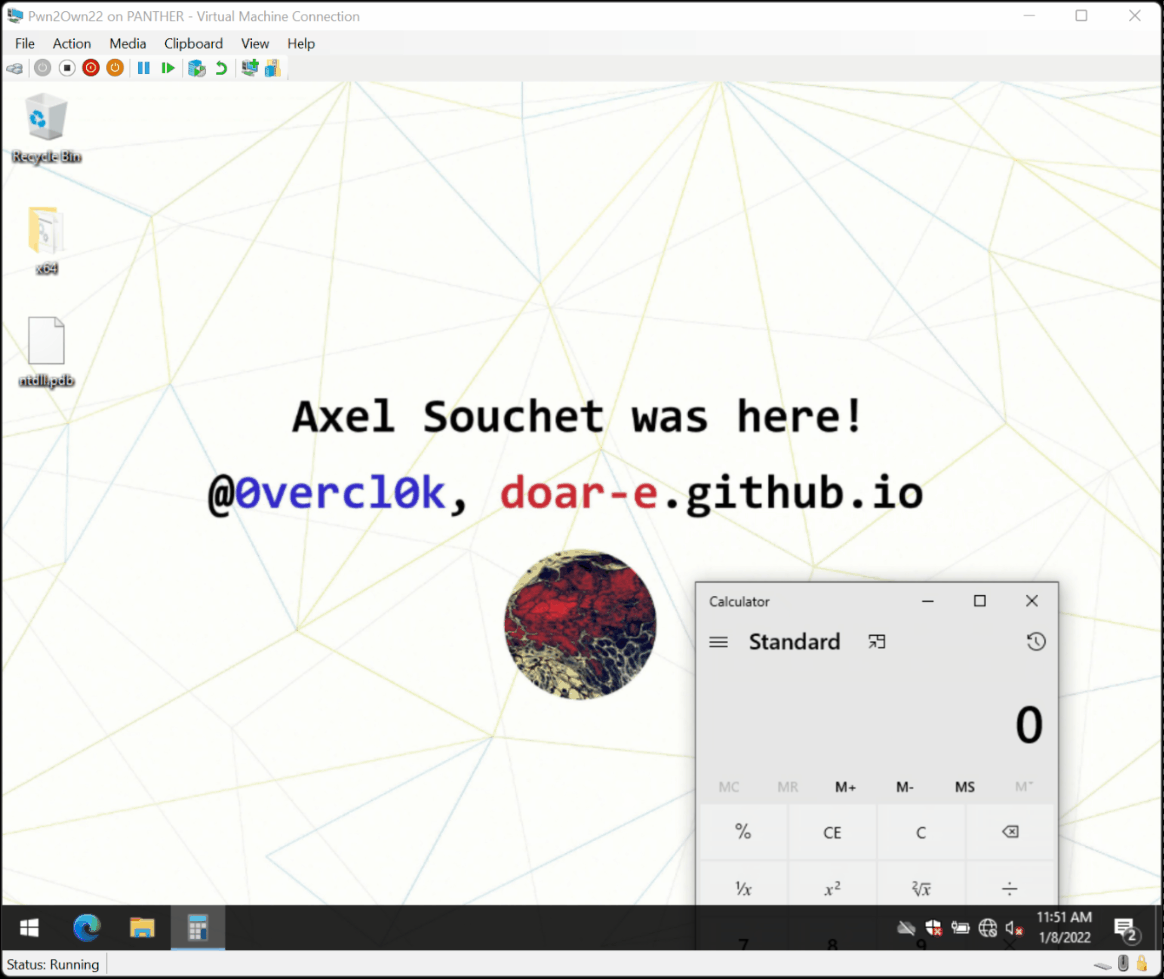
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
