CVE-2021-41579-LCDS-LAquis-SCADA-4.3.1.1085-Arbitrary-File-Write

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability

CVE-2018-7843

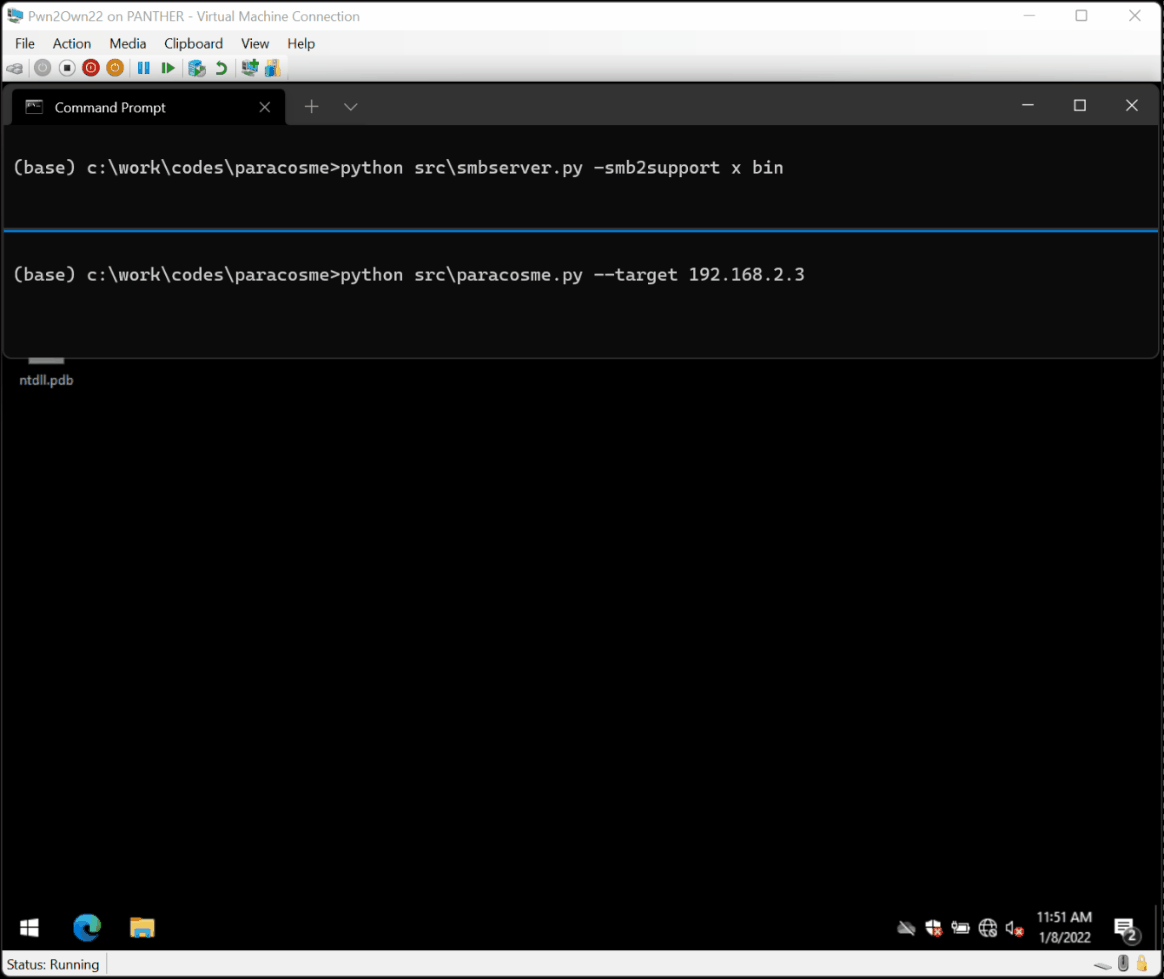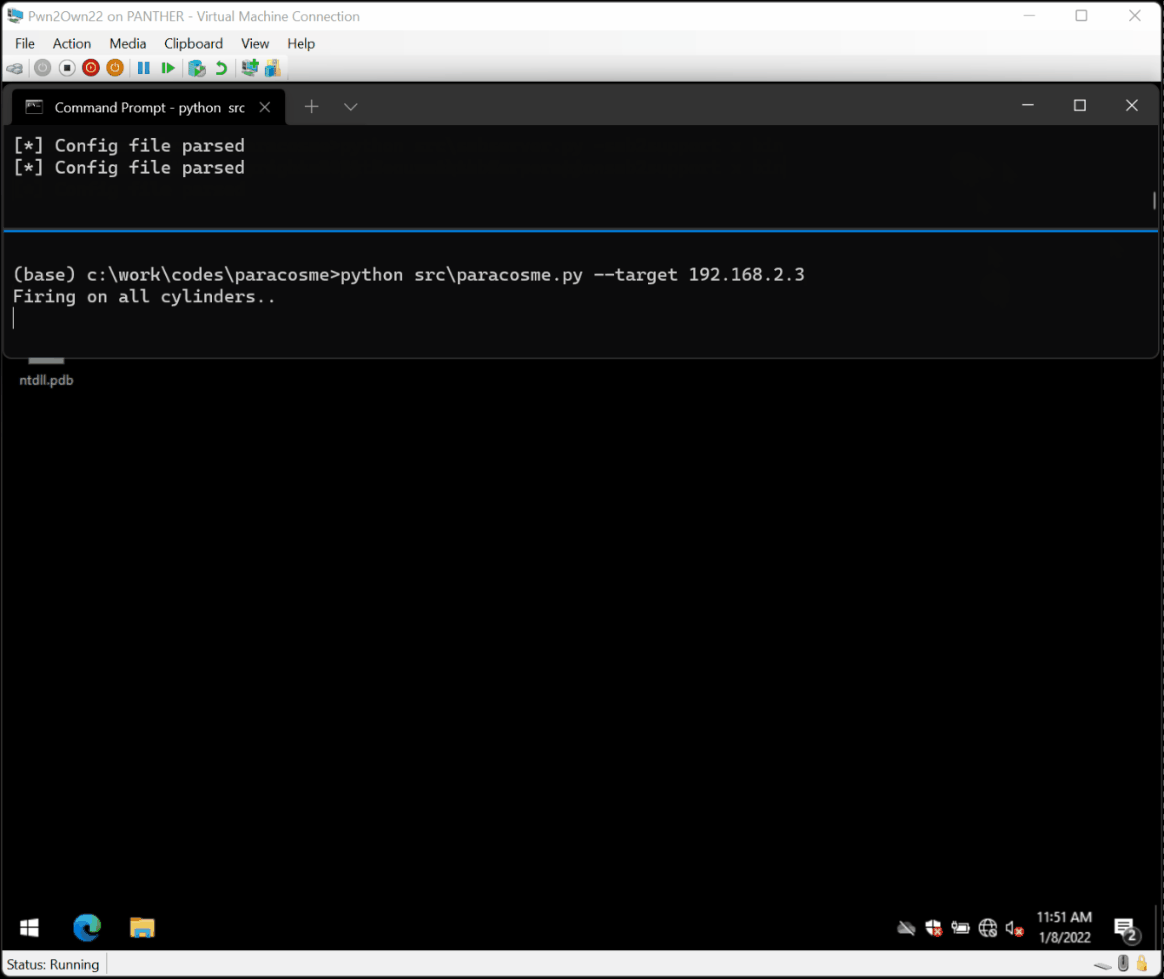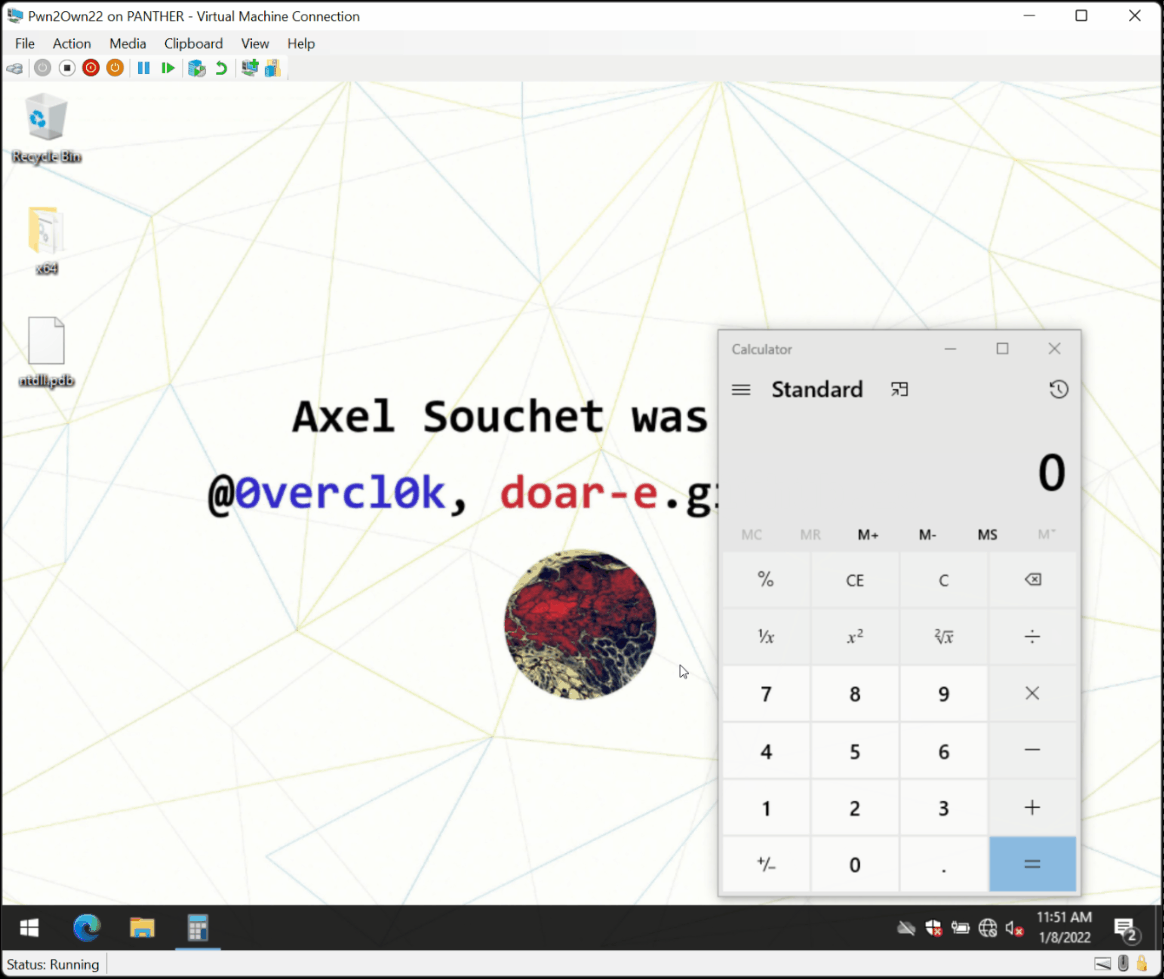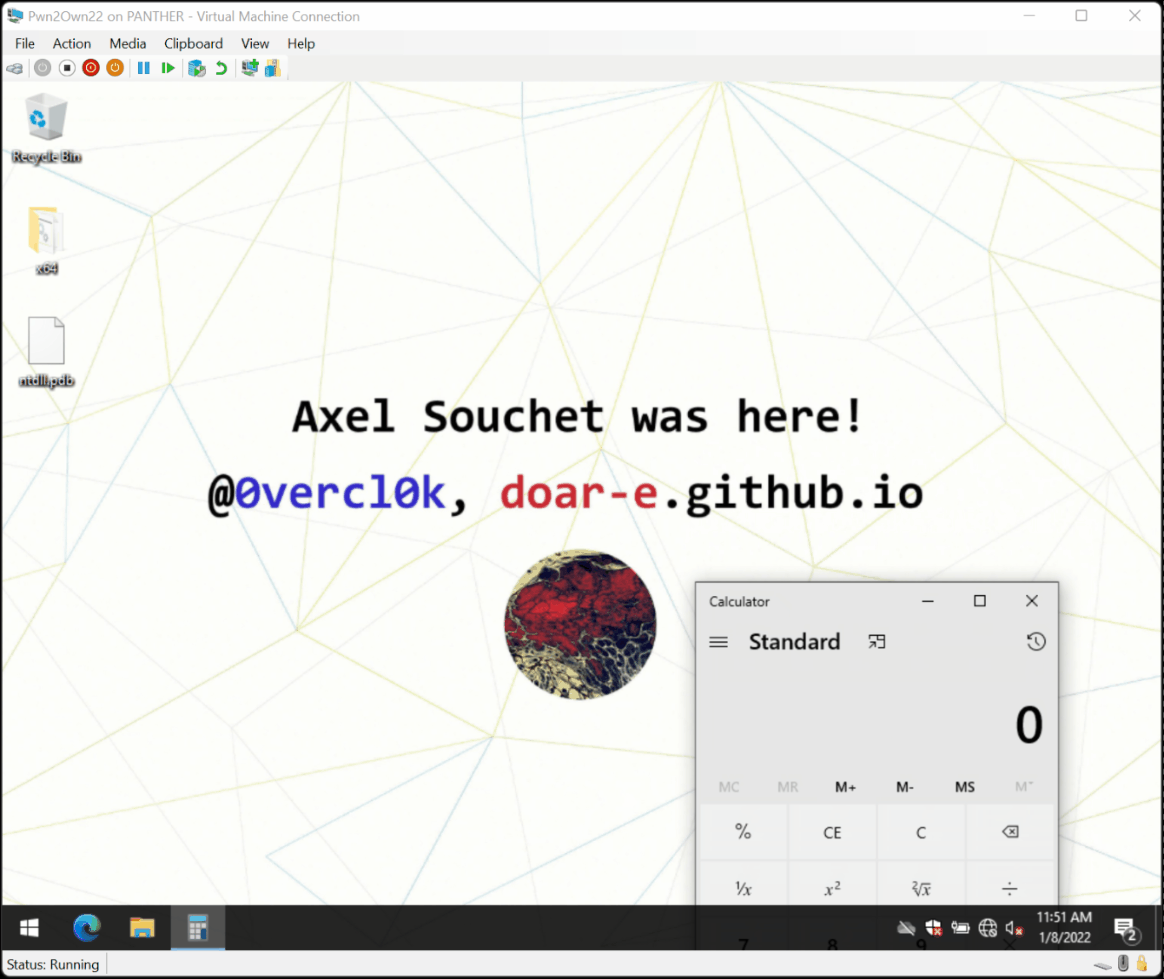
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…

Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…

Real world and CTFs exploiting web/binary POCs.

PoC for CVE-2018-12086 affecting various OPC UA stacks

Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…