
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
457 results
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
anti-botbinary-analysisdefensive-tools+4
333
14 days ago
Winstrument preview

Winstrument

GitHubnccgroup/winstrument

Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…

binary-analysisdynamic-code-analysisreverse-engineering+1
686 years ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
9.1k3 months ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
CVE-2023-28252 preview

CVE-2023-28252

GitHubfortra/cve-2023-28252

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
binary-exploitationdebuggersexploitation+4
1843 years ago
KasperMeow preview

KasperMeow

GitHubmein-0/kaspermeow

Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
binary-analysisexploitationreverse-engineering+1
1429 days ago
deobf-Arxan-Deob-C preview

deobf-Arxan-Deob-C

GitHubgmh5225/deobf-arxan-deob-c

Simple C program to quickly deobfuscate windows executables protected with Arxan.
binary-analysisdefensive-toolsmalware-analysis+1
153 years ago
idenLib preview

idenLib

GitHubsecrary/idenlib

idenLib - Library Function Identification [This project is not maintained anymore]
binary-analysisdebuggersmalware-analysis+2
3957 years ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

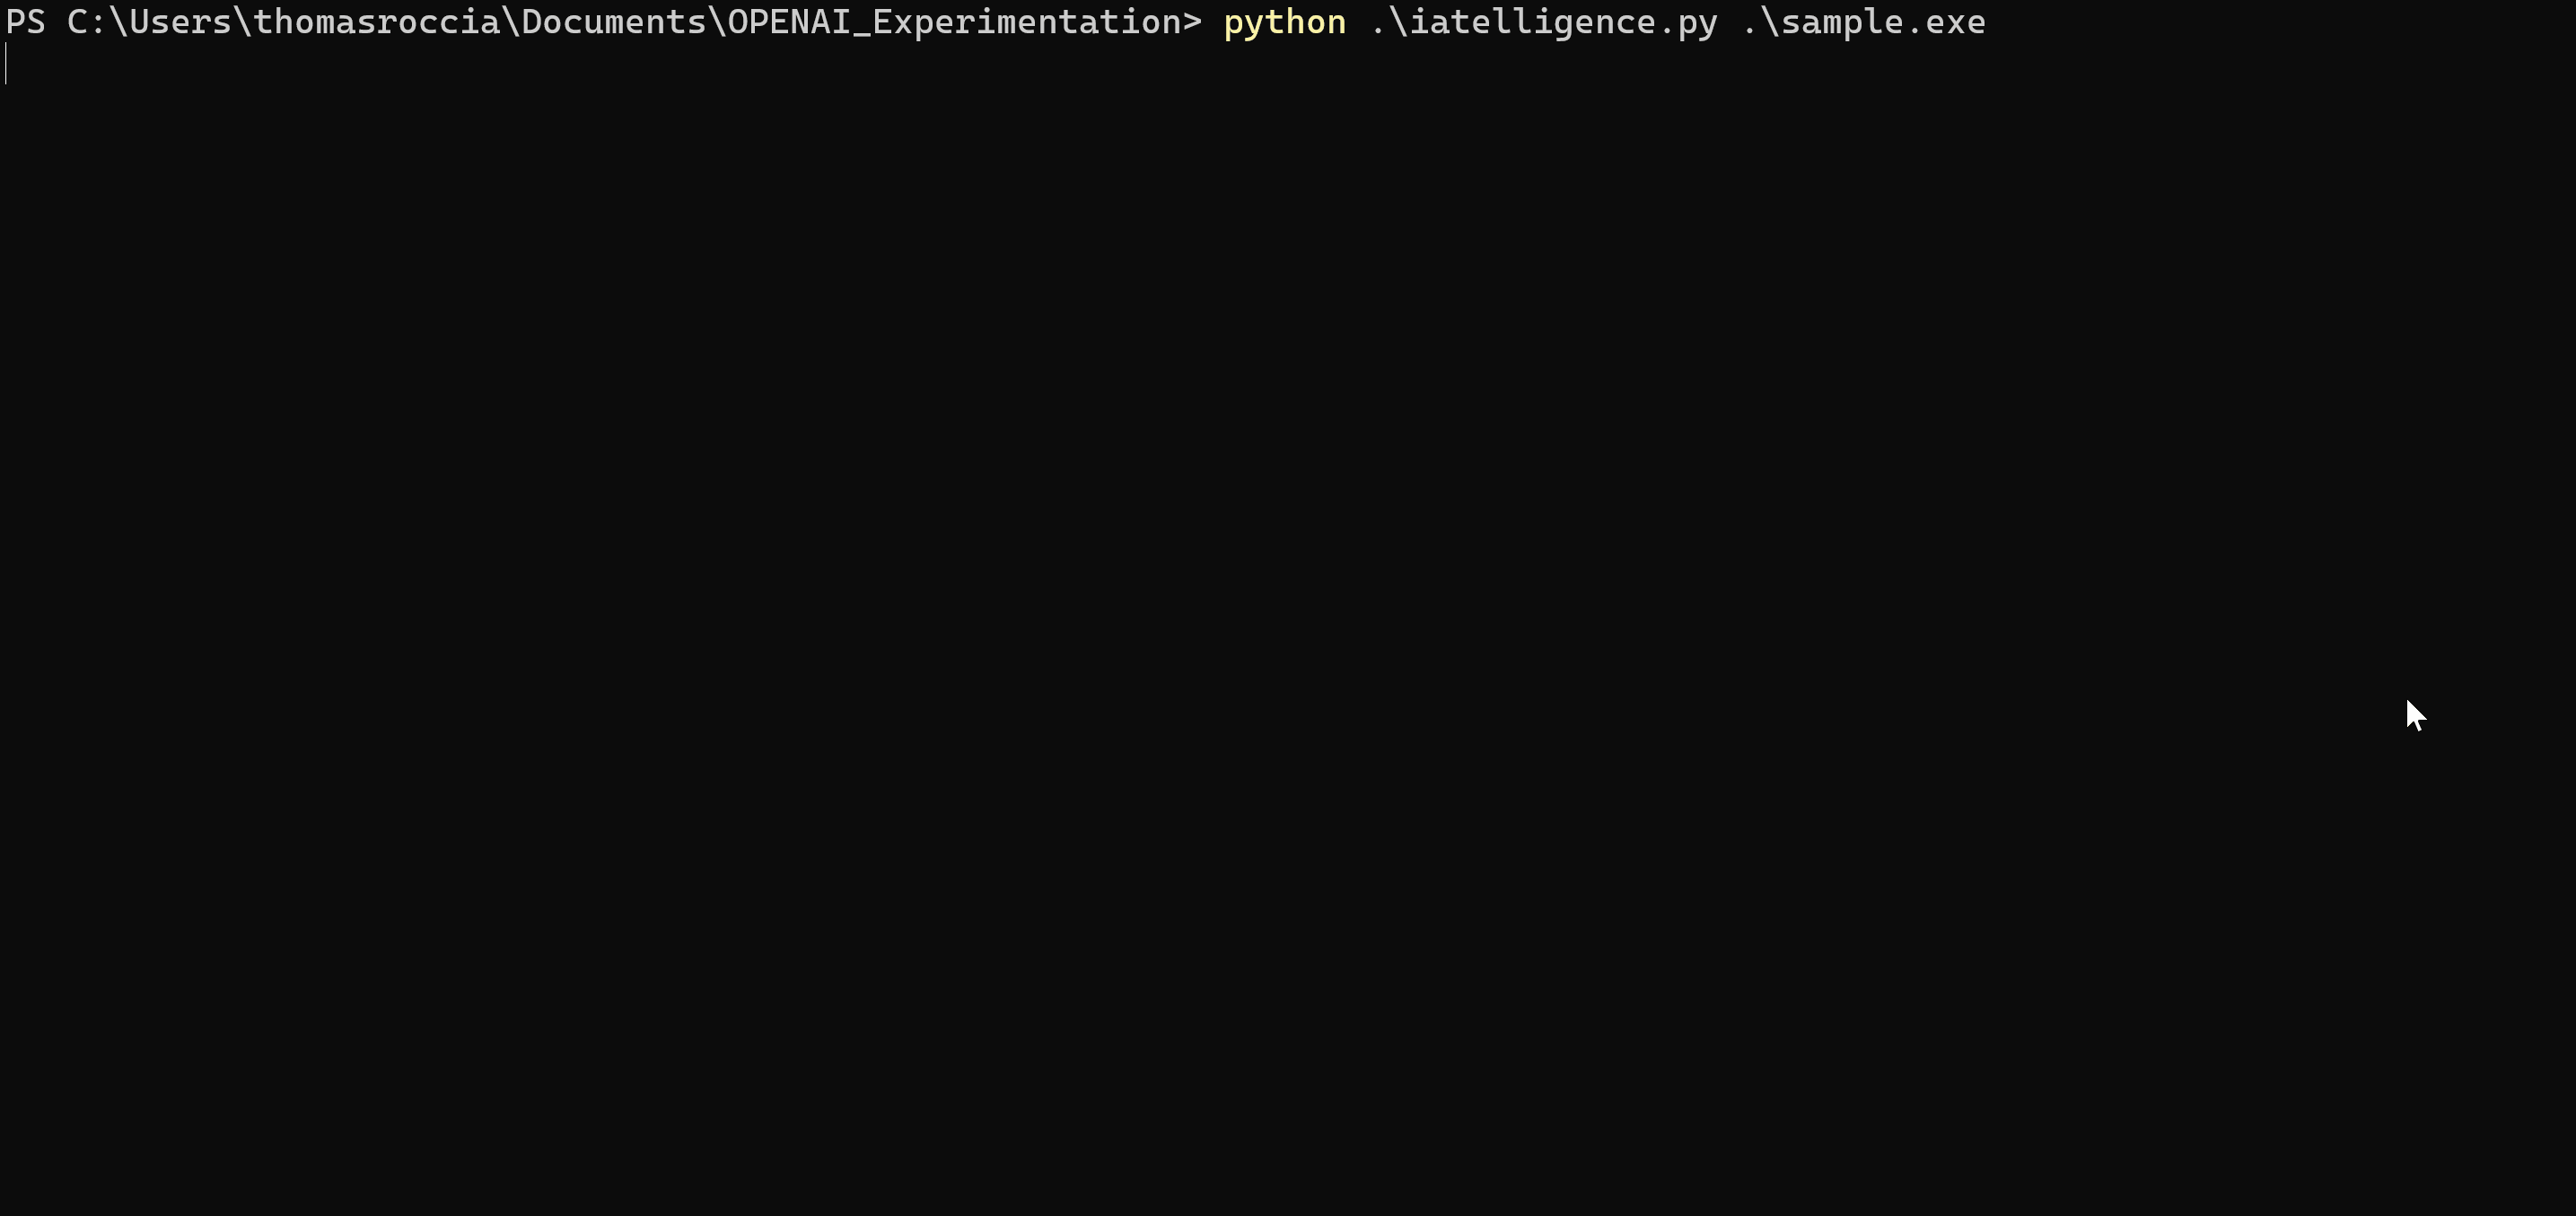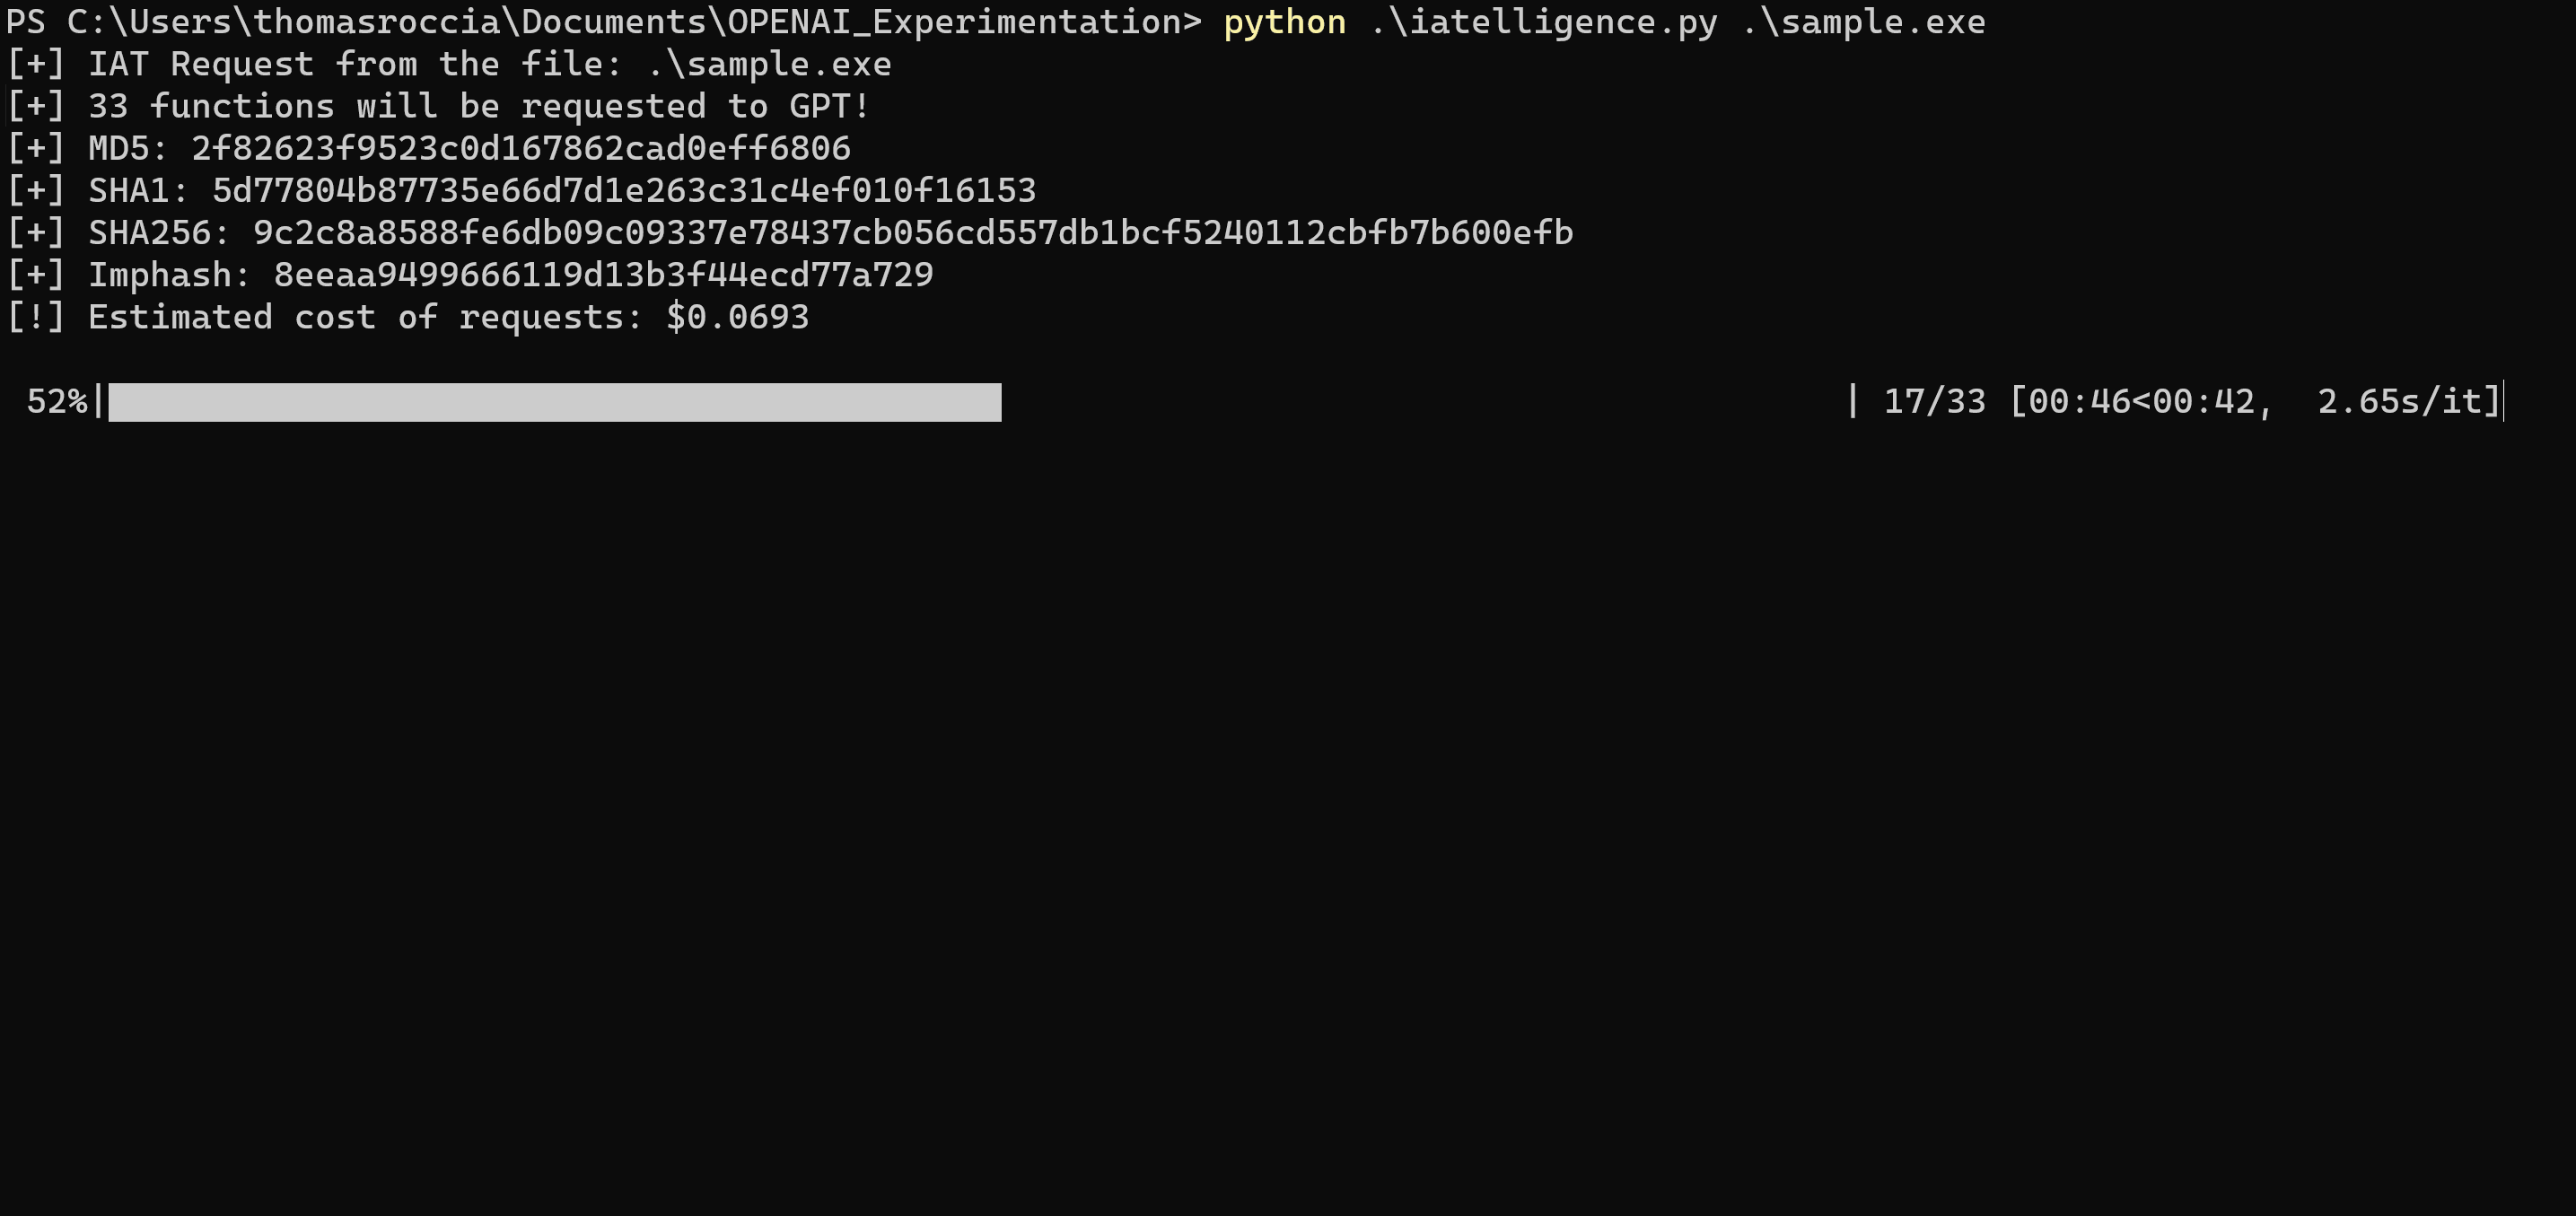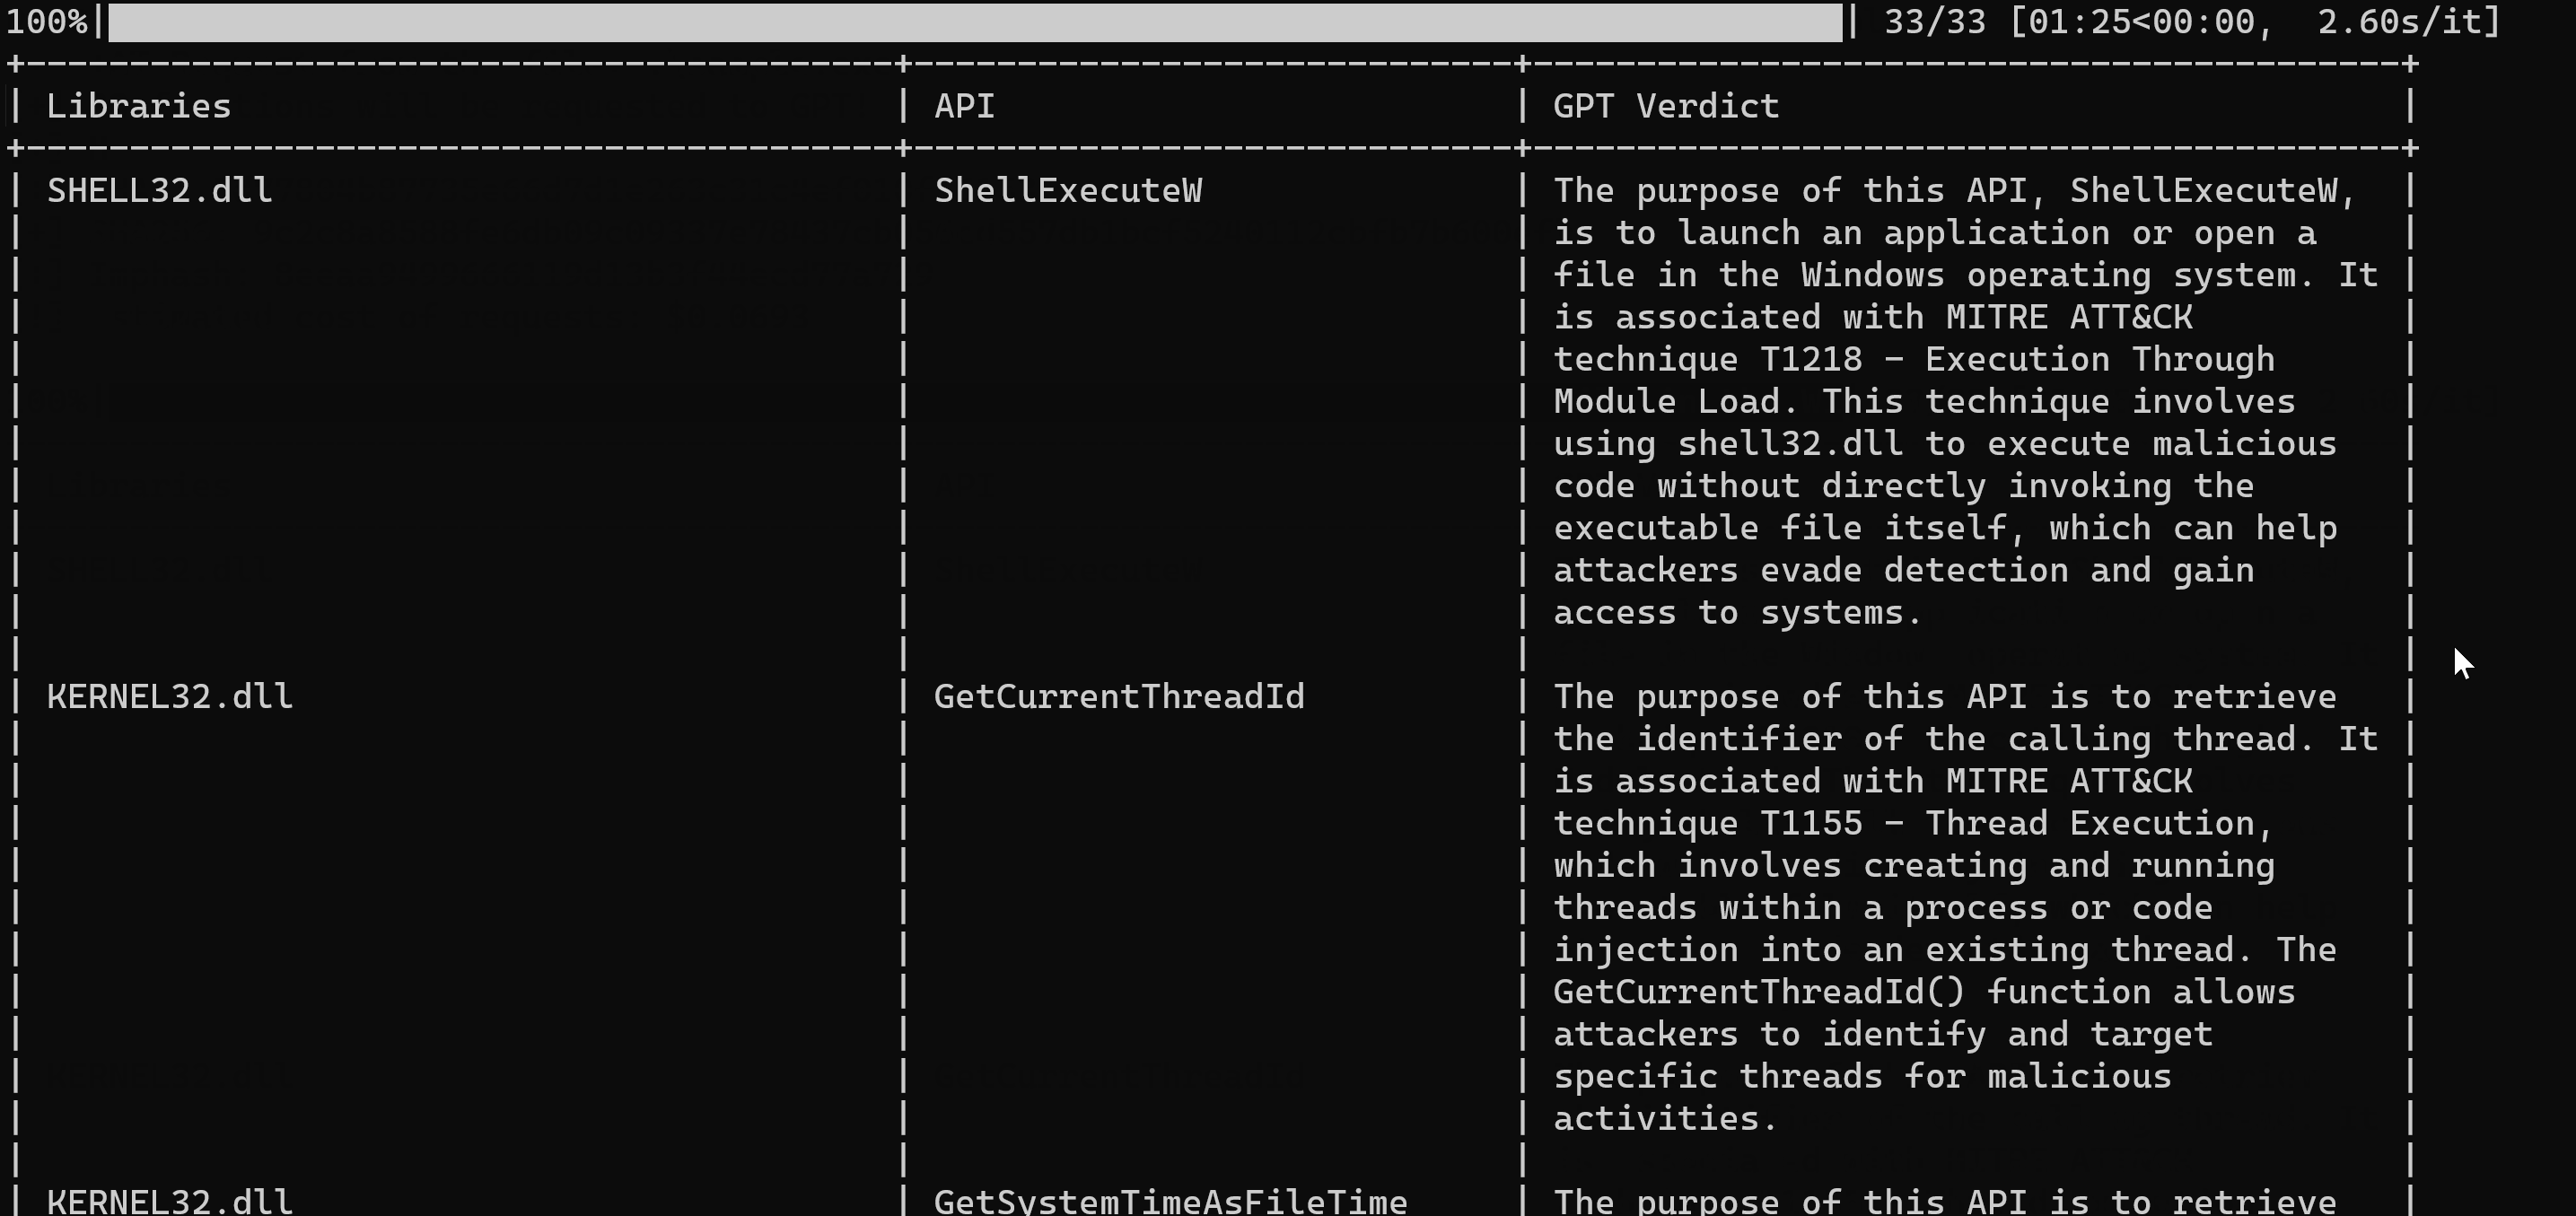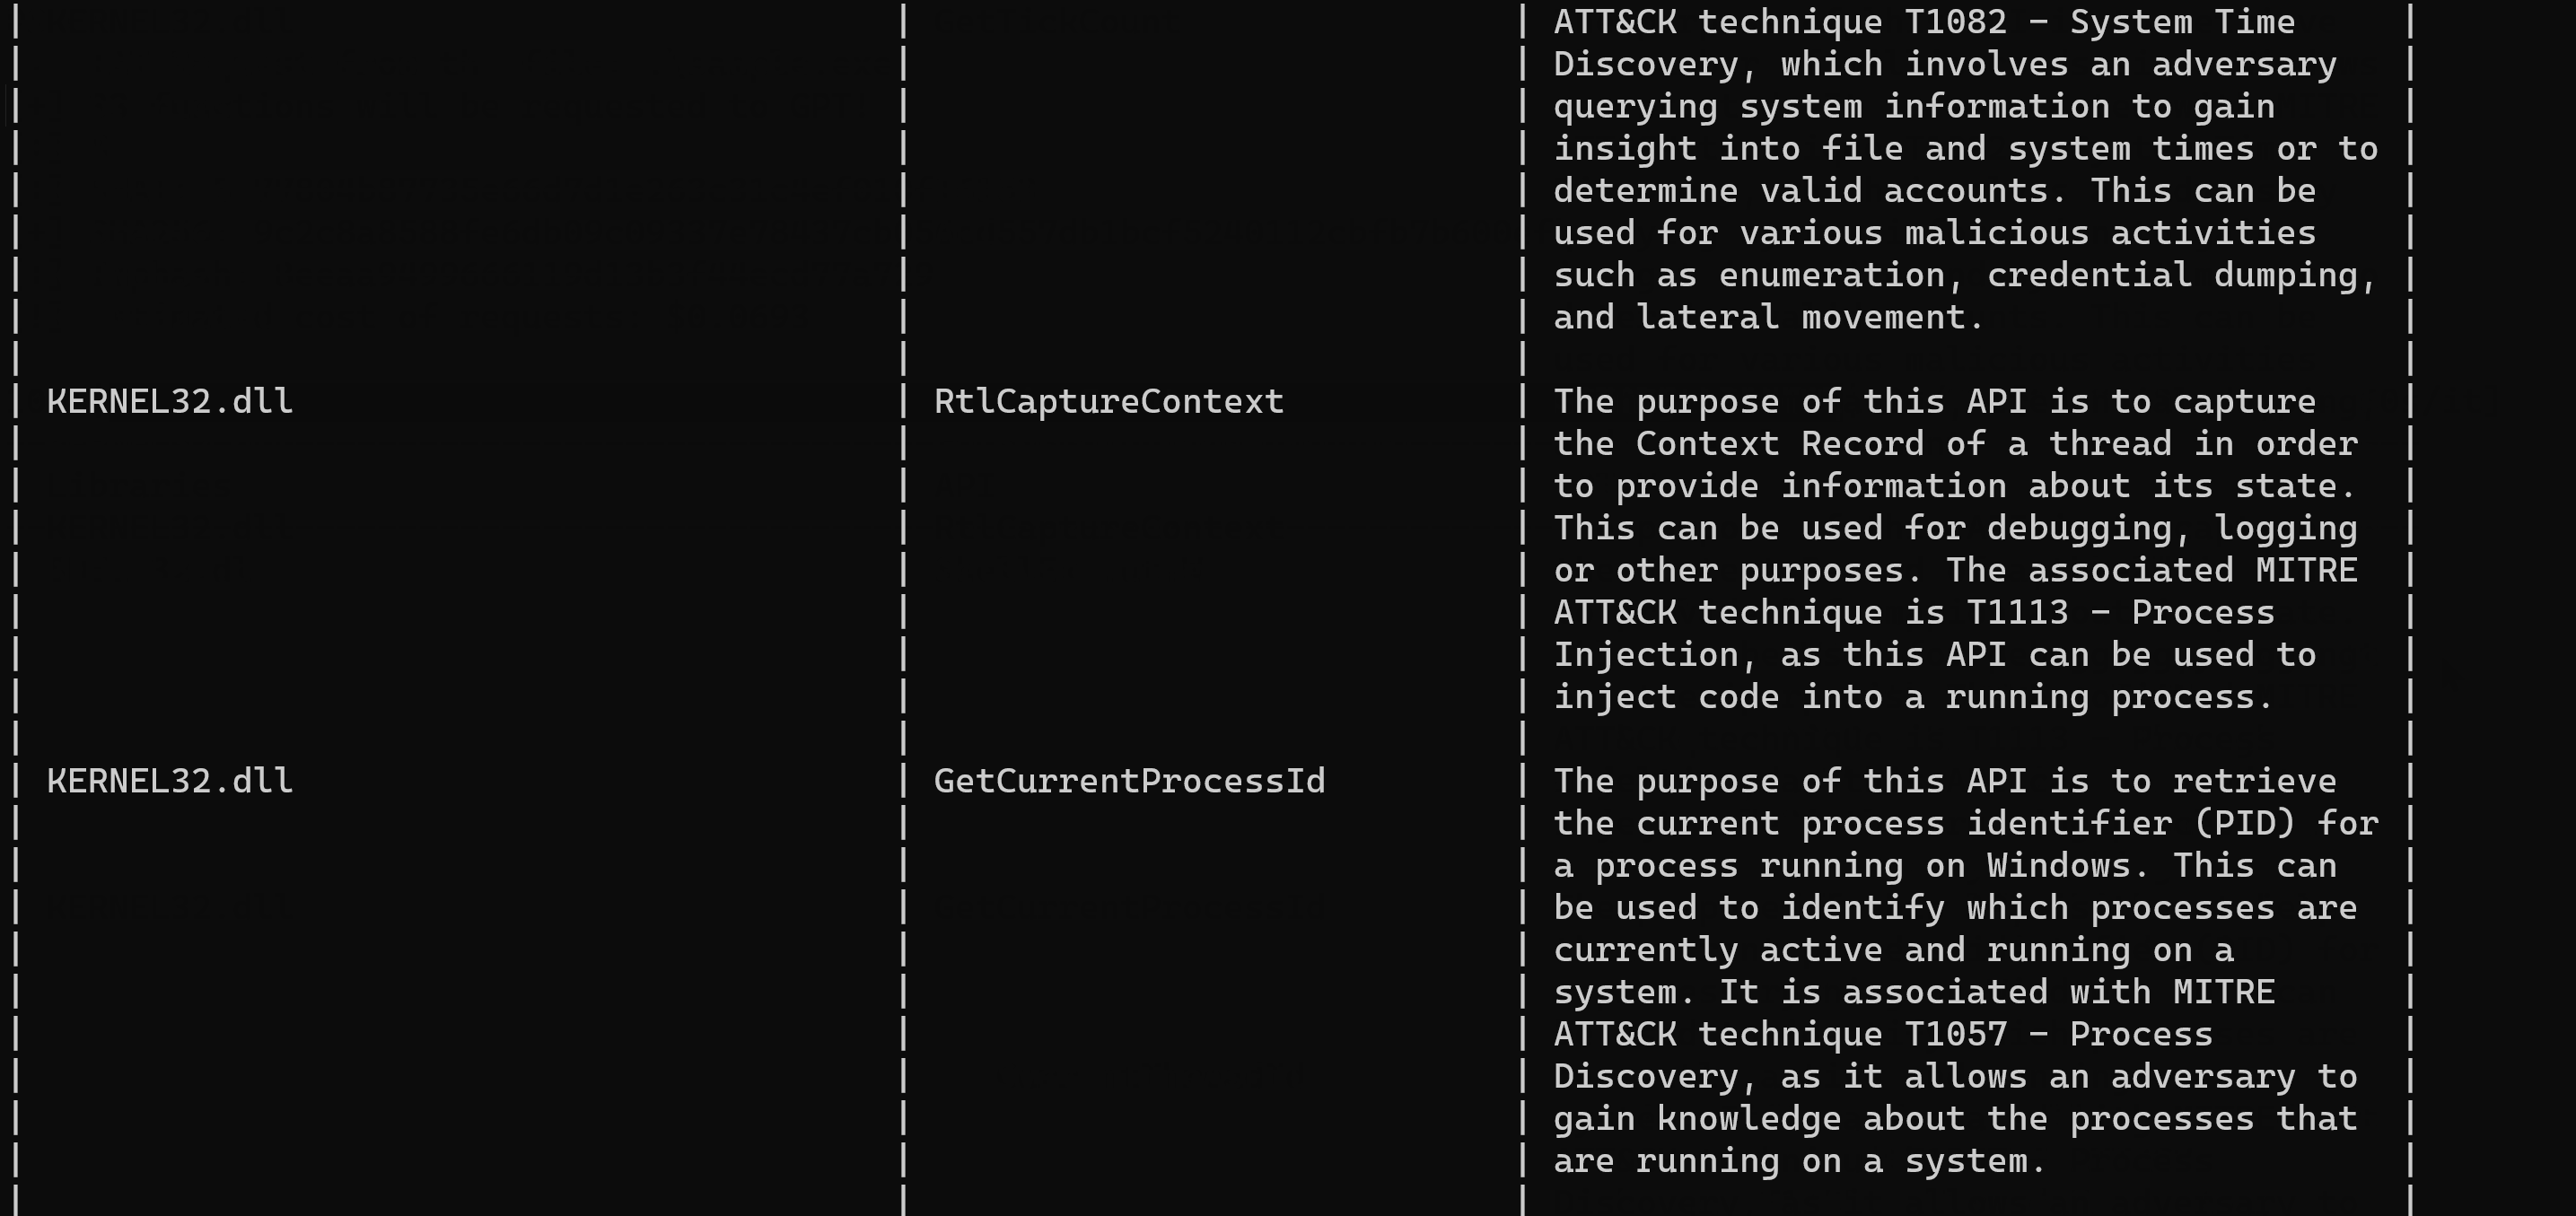
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
3863 years ago
CVE-2026-9789 preview

CVE-2026-9789

GitHubugvxb/cve-2026-9789

A critical local privilege escalation vulnerability has been discovered in Acer NitroSense software (PSAdminAgent.exe). The vulnerability allows any…

binary-analysiseducationexploitation+3
4 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k2 days ago
p-invoke.net preview

p-invoke.net

GitHubricardojoserf/p-invoke.net

Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
malware-analysisreverse-engineeringutilities-frameworks
241 year ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
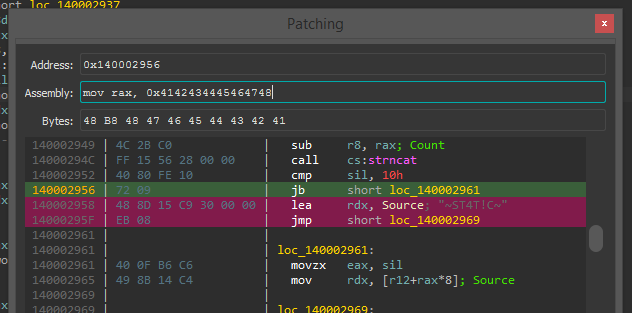
patching preview

patching

GitHubgaasedelen/patching

An Interactive Binary Patching Plugin for IDA Pro

binary-analysisbinary-exploitationdebuggers+8
1.3k1 year ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
binary-exploitationexploitationmalware-analysis+3
3252 years ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k17 days ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
1269 months ago
pecli preview

pecli

GitHubte-k/pecli

CLI tool to analyze PE files

binary-analysismalware-analysisreverse-engineering+1
902 years ago
Previous12…26Next