
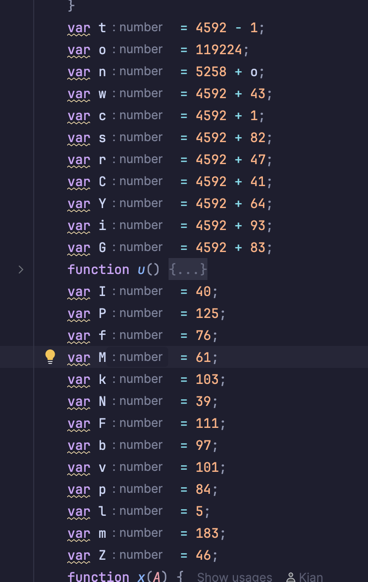
datadome-vm
 xkiian/datadome-vm
Reverse engineering the new Datadome VM 🔥
anti-botbinary-analysiscaptcha-bypass+3
xkiian/datadome-vmReverse engineering the new Datadome VM 🔥
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 mrexodia/dumpulator
An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…
 cert-polska/malduck
🦆 Malduck is your ducky companion in malware analysis journeys
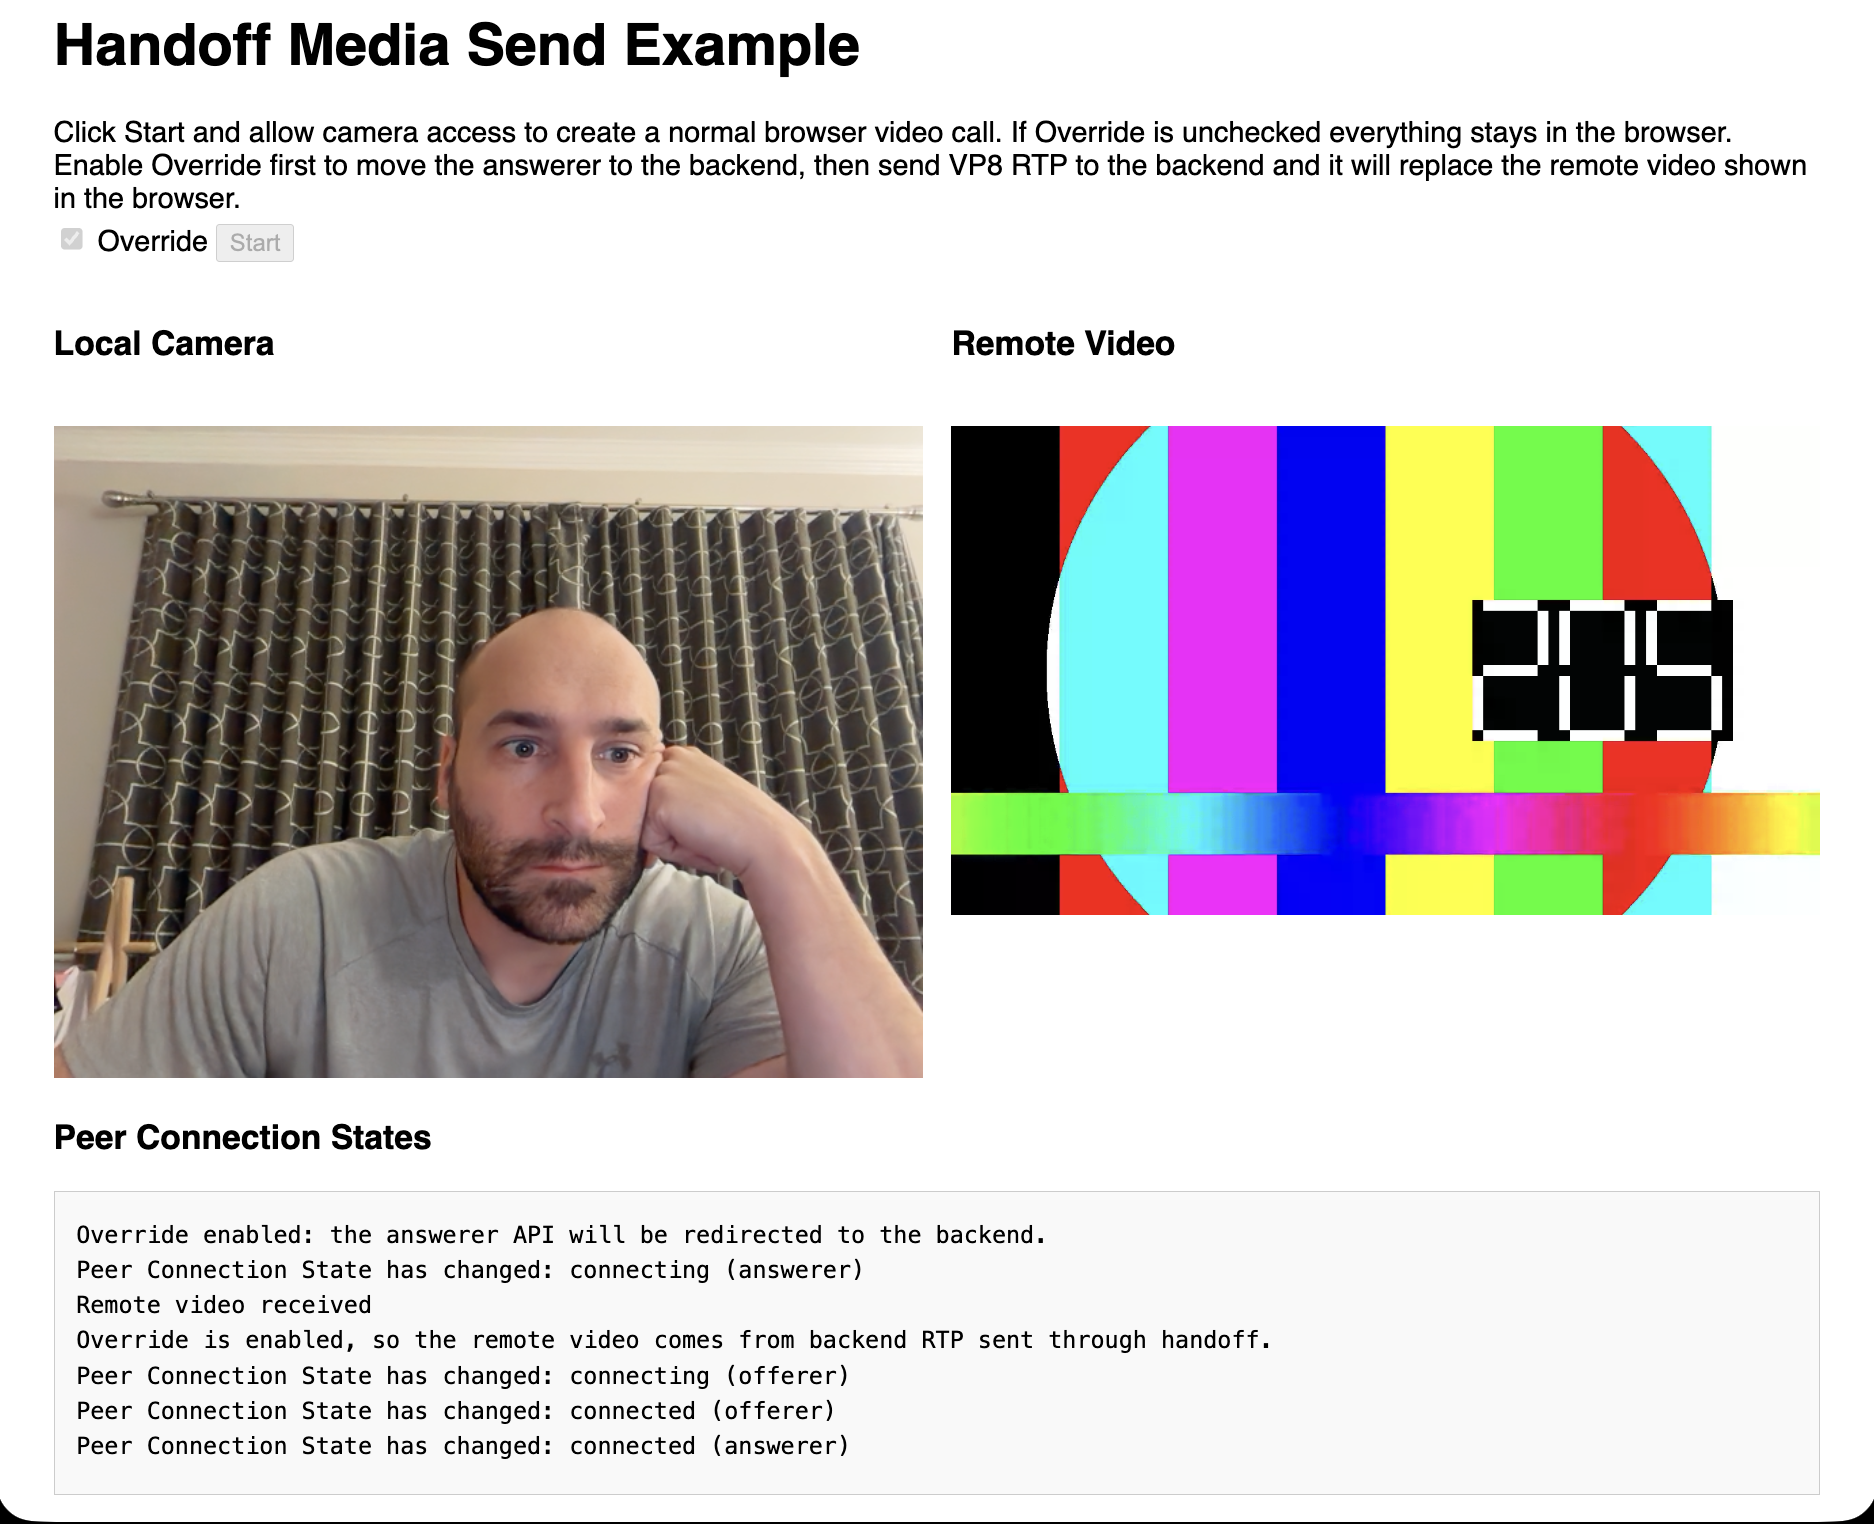 pion/handoff
Start WebRTC in the browser—run it somewhere else
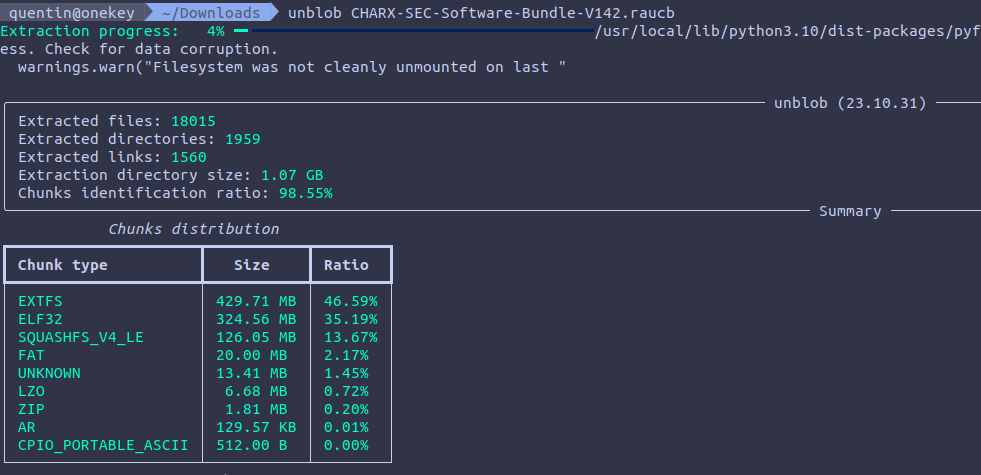 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 jprx/cve-2024-54507
Proof-of-concept exploit for CVE-2024-54507, an integer type confusion vulnerability in XNU kernel, with technical writeup and exploitation details.
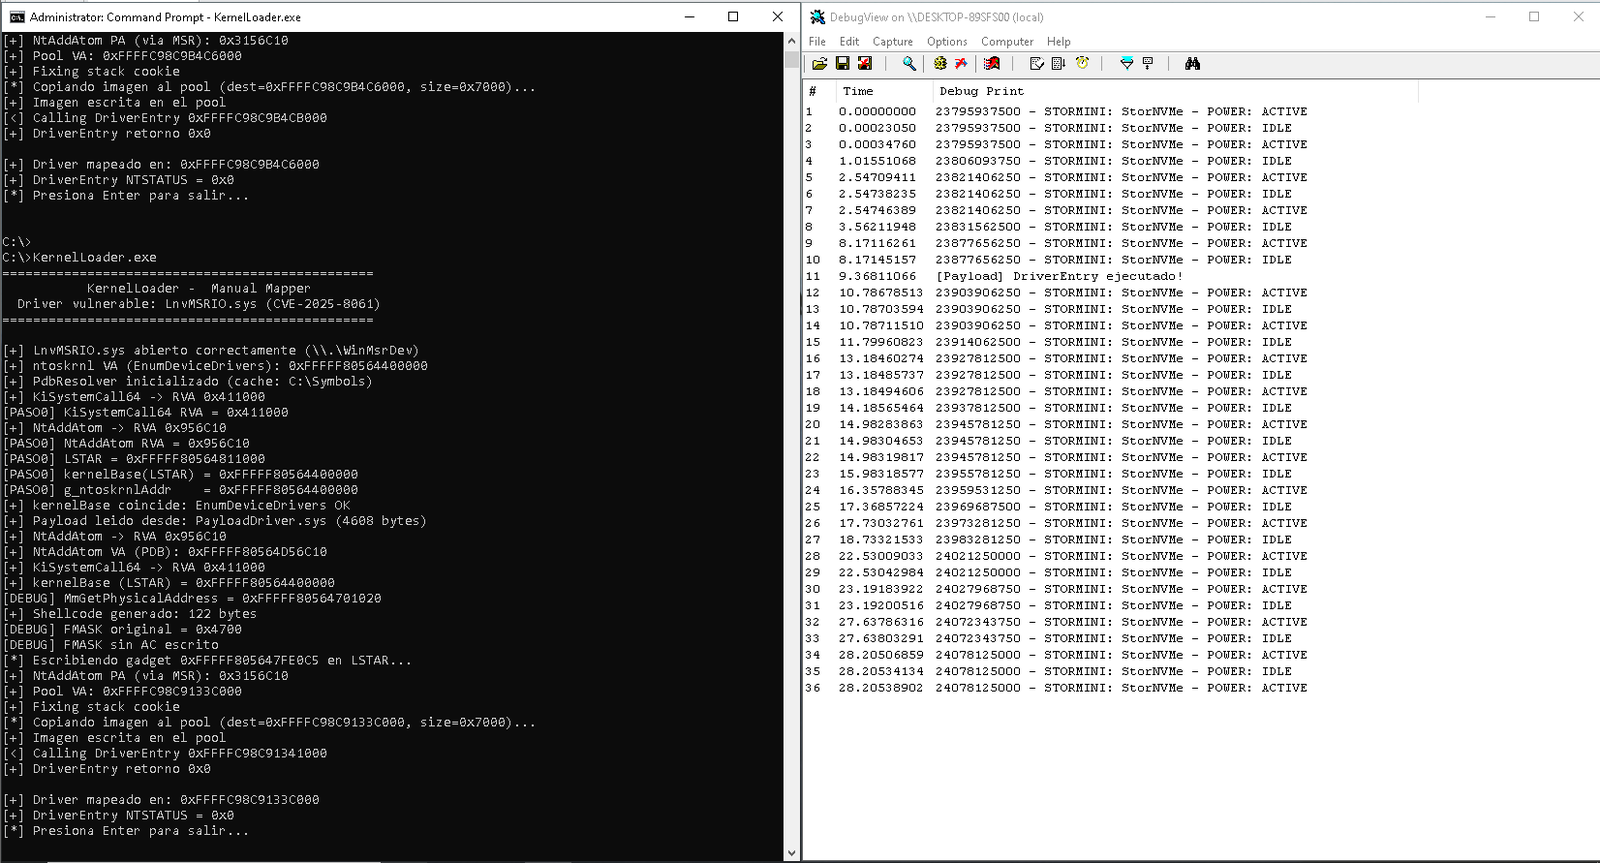 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 sandi-go/cve-2018-12798
Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.
 a0rtega/pafish
Pafish is a testing tool that uses different techniques to detect virtual machines and malware analysis environments in the same way that malware…
 vxunderground/malwaresourcecode
Collection of malware source code for a variety of platforms in an array of different programming languages.
 cea-sec/miasm
Reverse engineering framework in Python
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.