
windows-x86-shellcode-poc
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
binary-exploitationeducationpayload-development+3
8
nataliadiak/windows-x86-shellcode-pocWindows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 zodiacon/quickasm
Simple x86/x64 Assembler/Disassembler/Emulator
 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 nccgroup/binja_arch_ref
A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
 andreiverse/shlol
do common hacking tasks with a simple menu
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
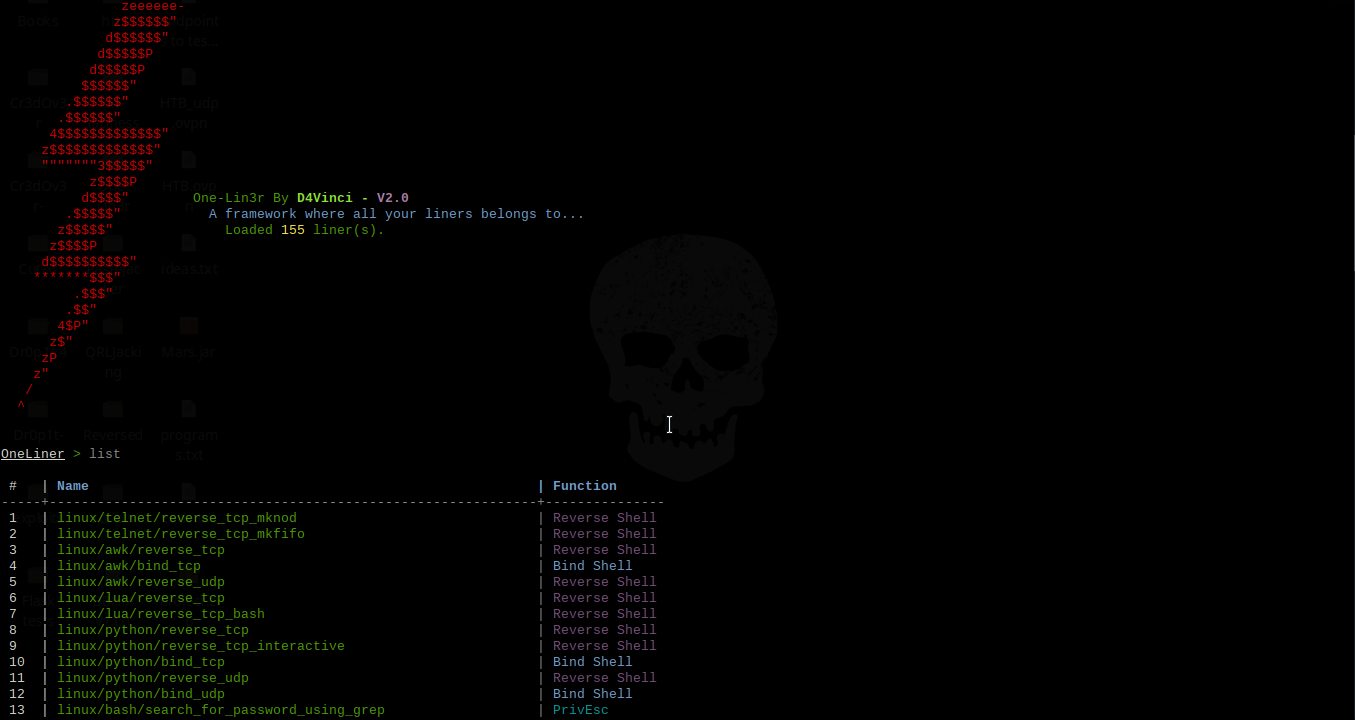 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 lunixbochs/patchkit
binary patching from Python