
mwcfg
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
c3rb3ru5d3d53c/mwcfgA Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
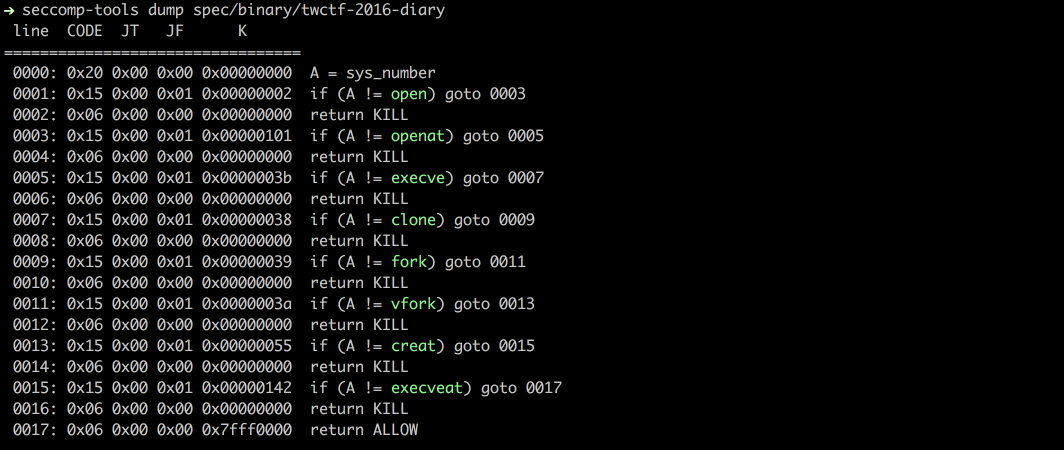 david942j/seccomp-tools
Provide powerful tools for seccomp analysis
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
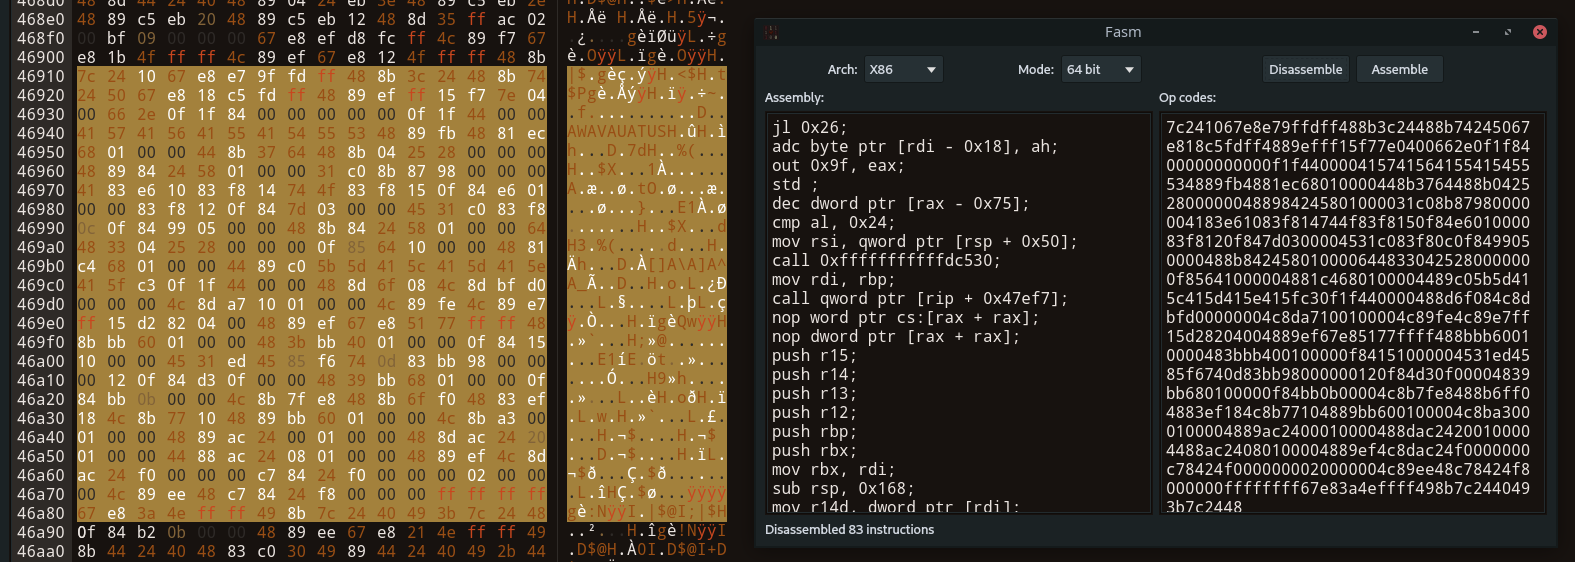 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
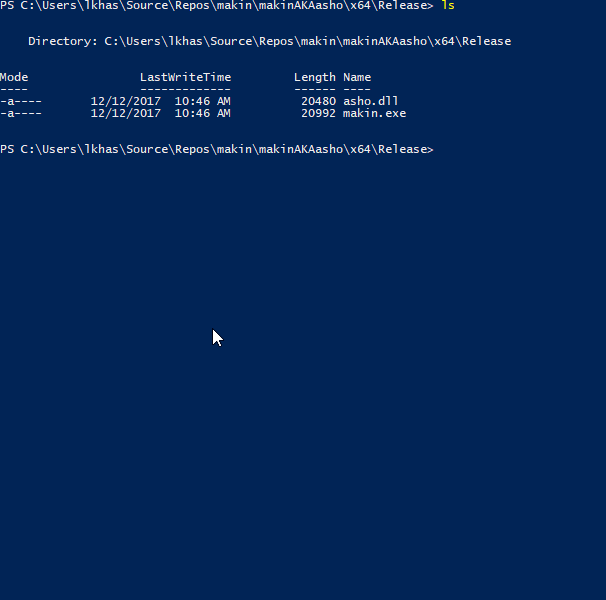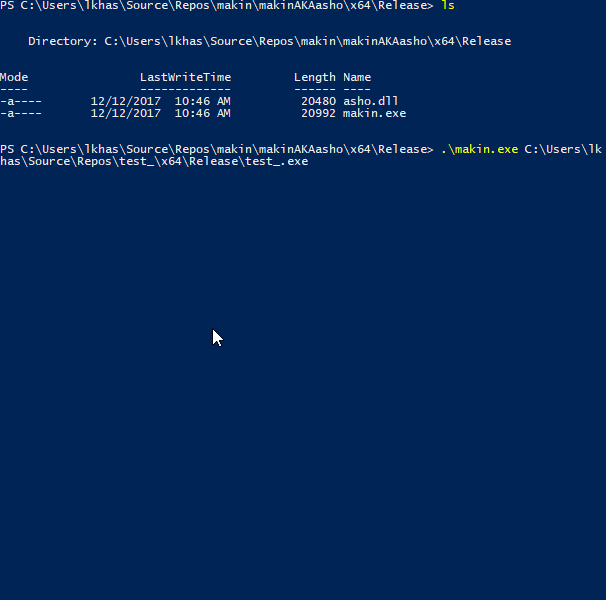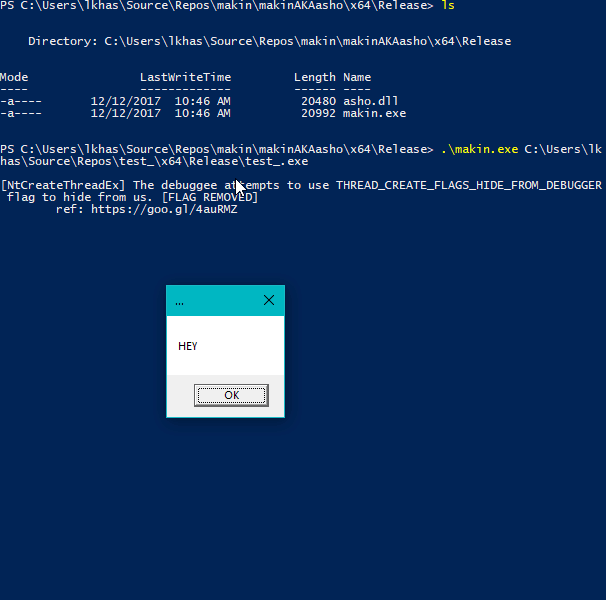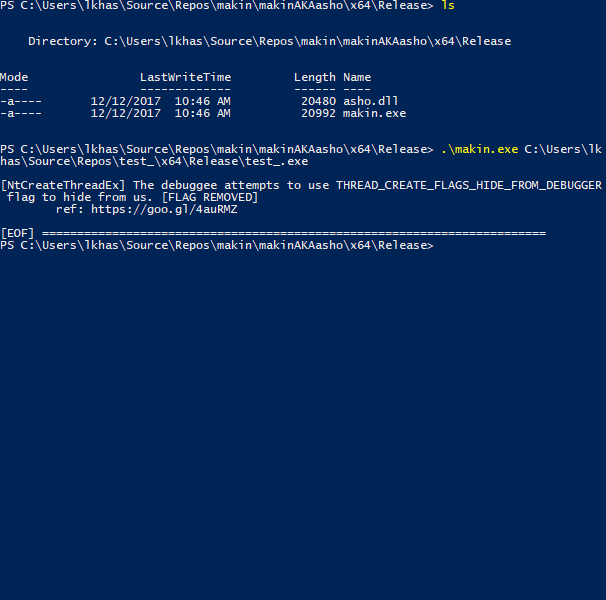 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 uofw/uofw
The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
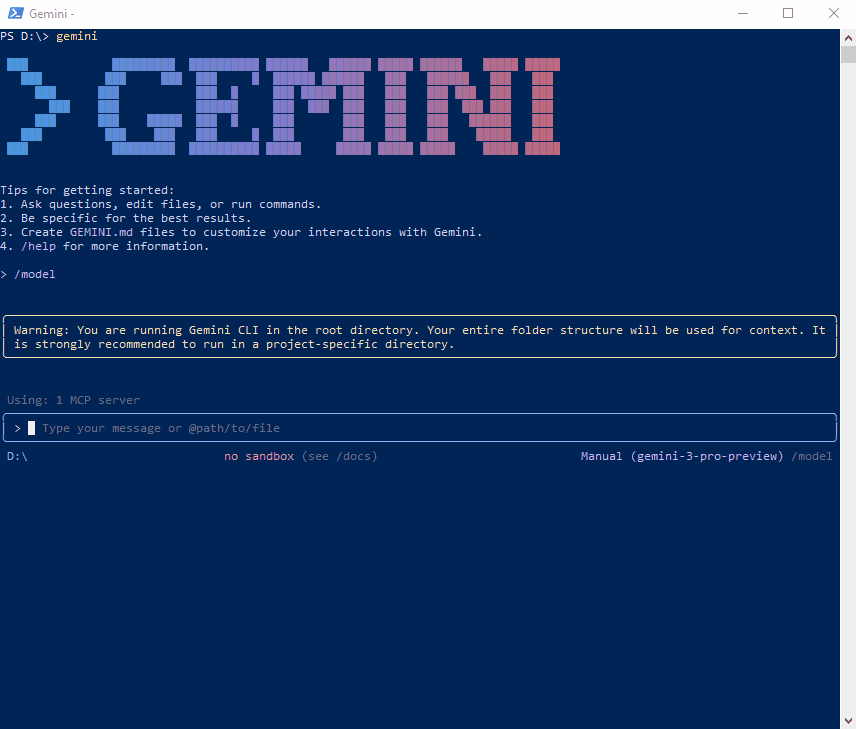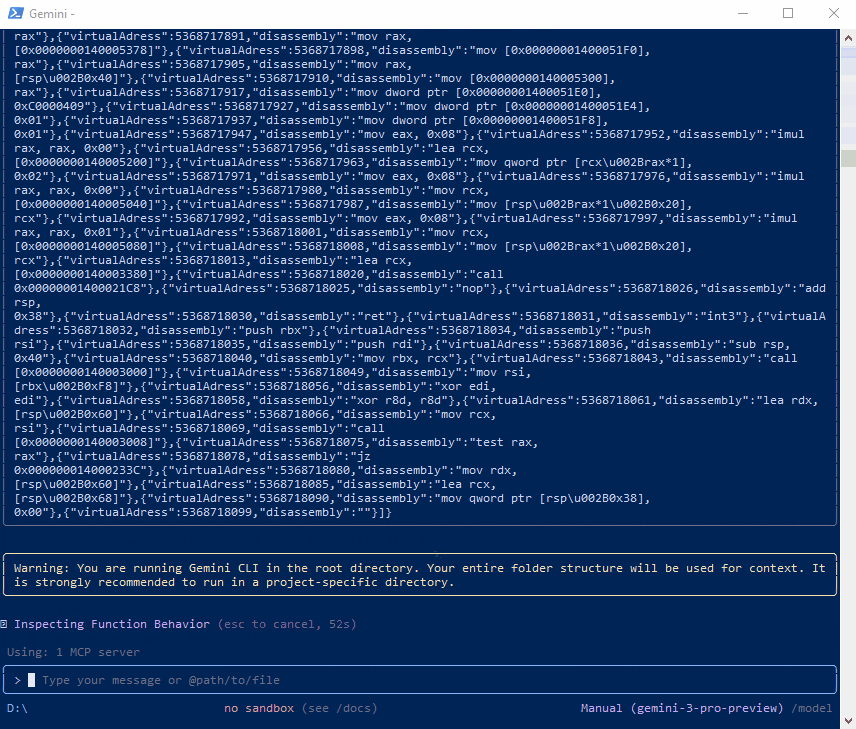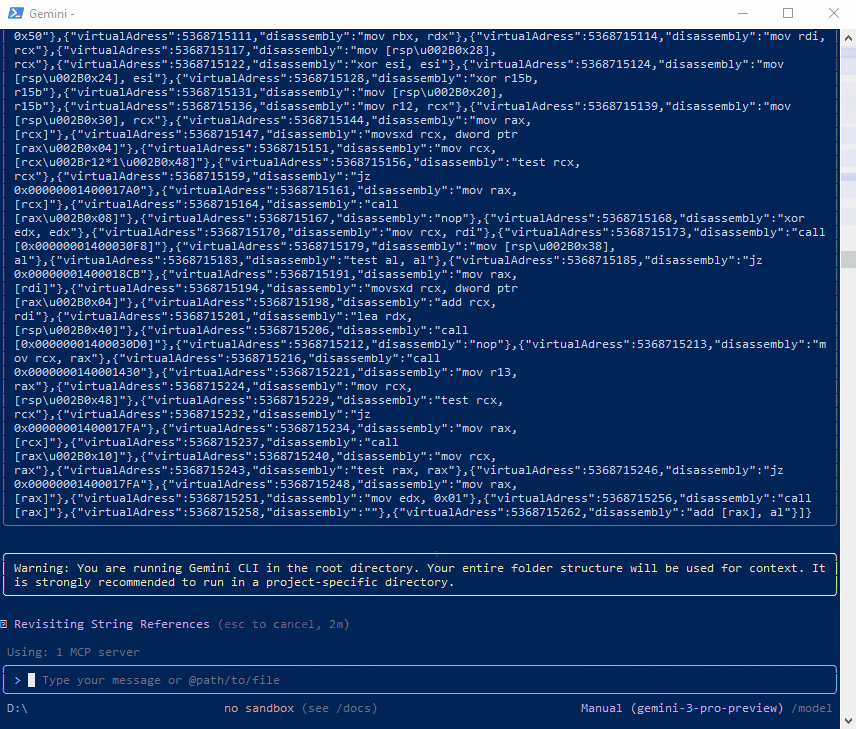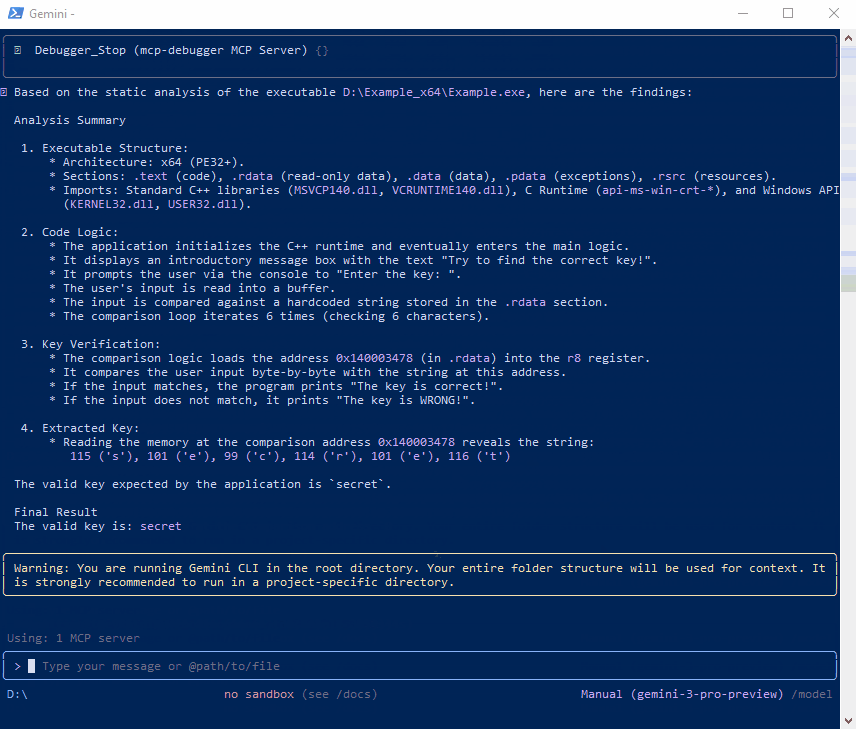 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
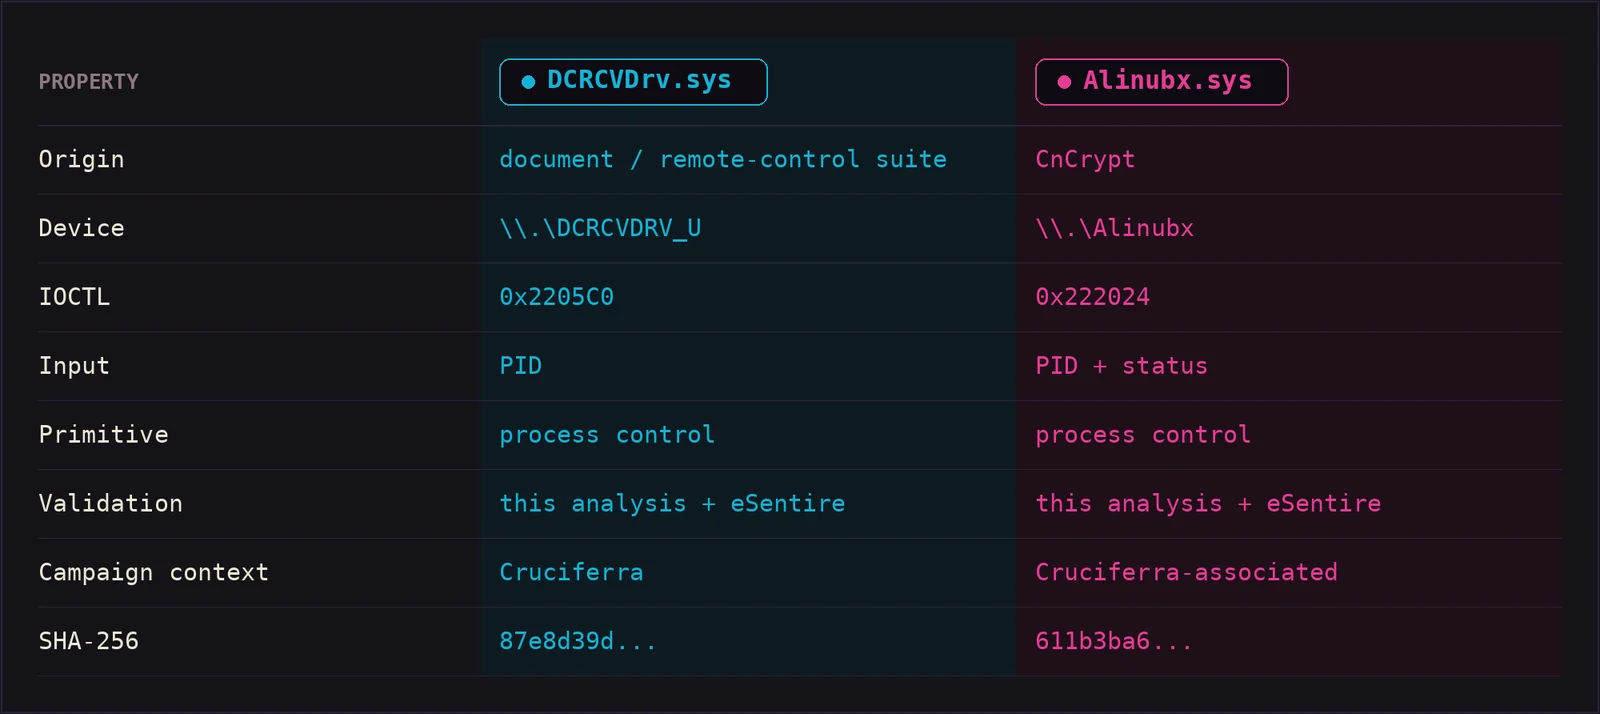 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]