
python-haystack
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
binary-analysisdigital-forensicsforensics+2
95
trolldbois/python-haystackProcess heap analysis framework - Windows/Linux - record type inference and forensics
 equifox/ksdumper
Dumping processes using the power of kernel space !
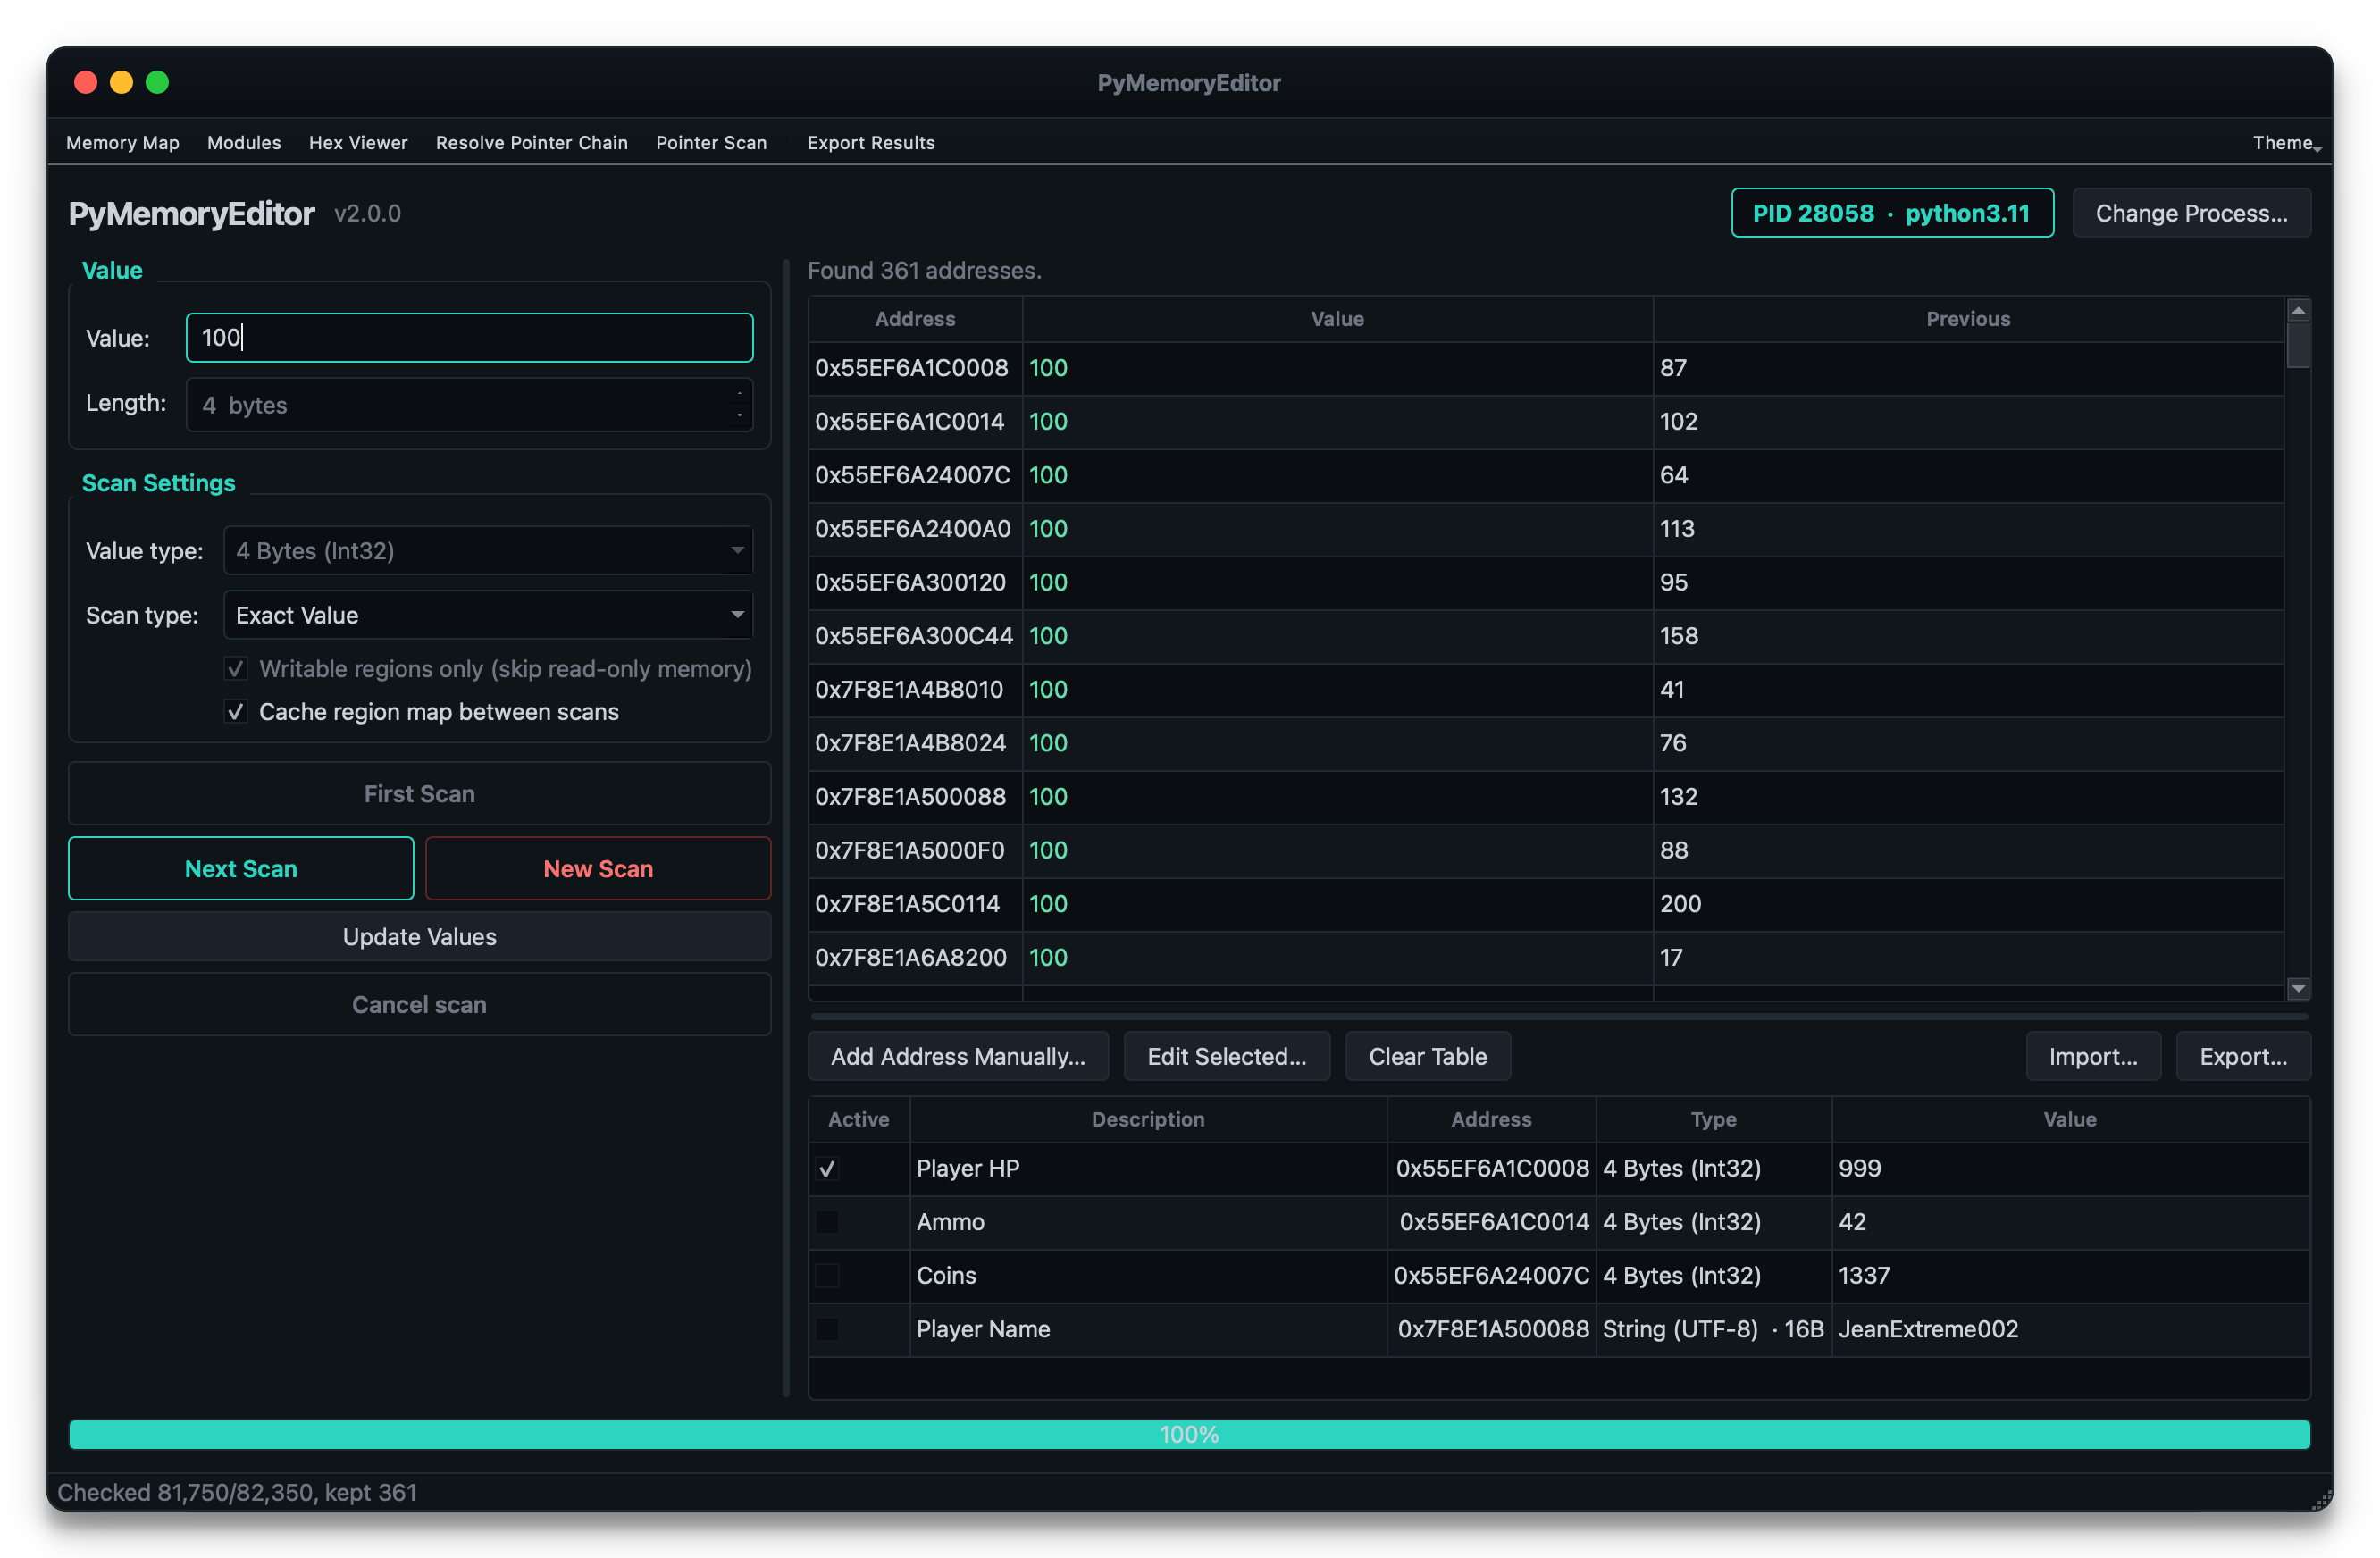 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
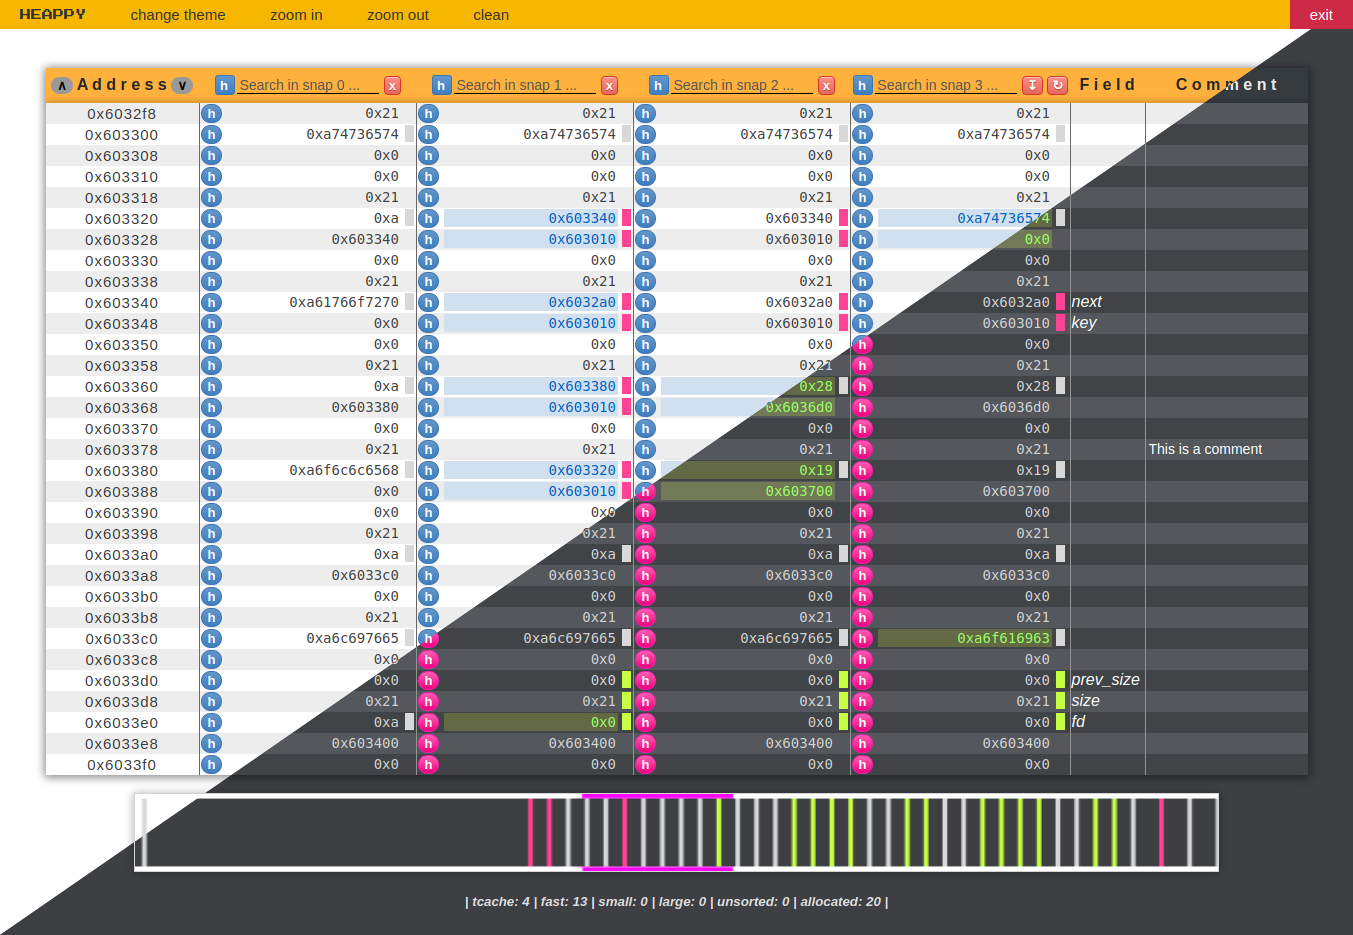 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 paddycahil/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 nozominetworks/upx-recovery-tool
Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
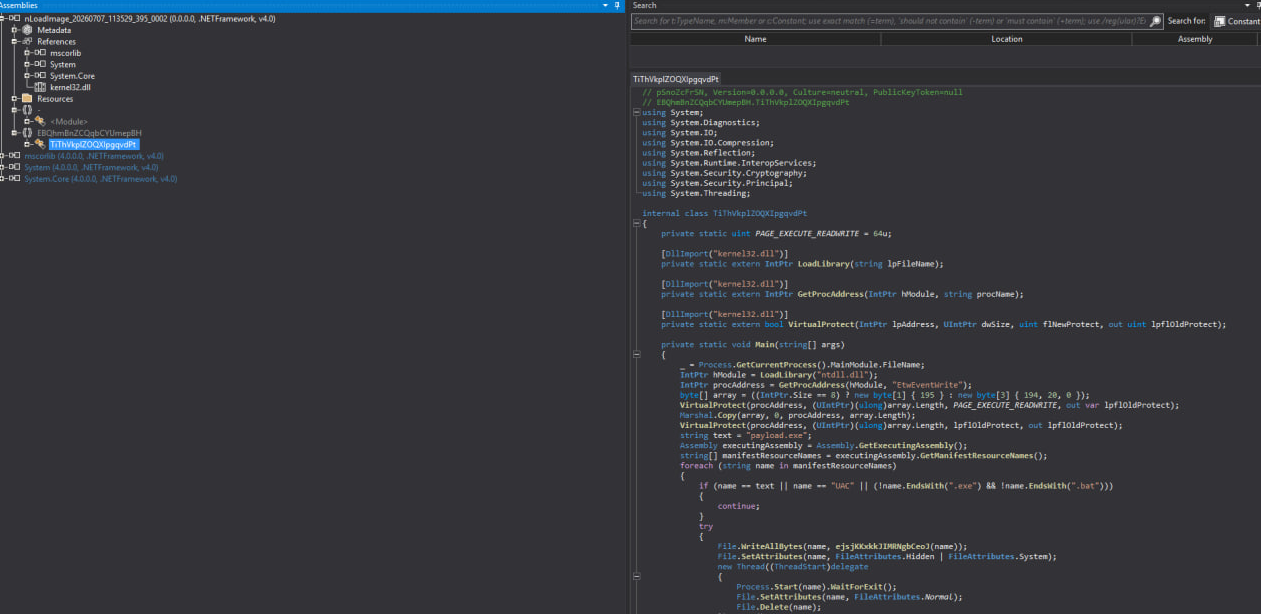 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…