super-tart-vphone-writeup

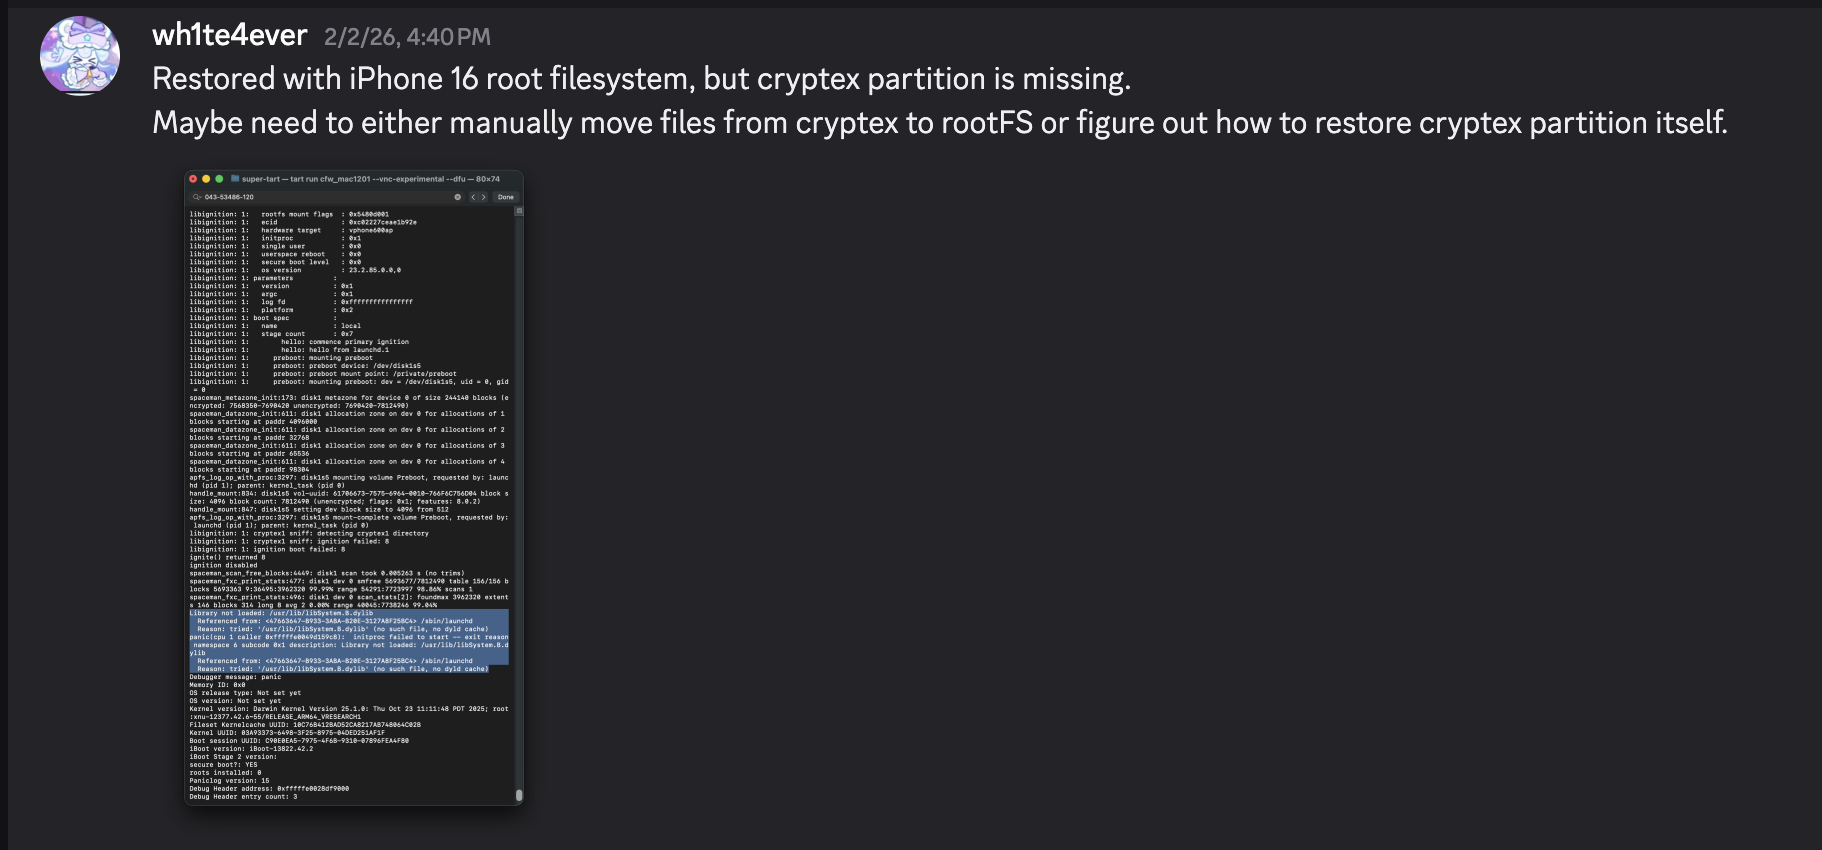
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…

Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…

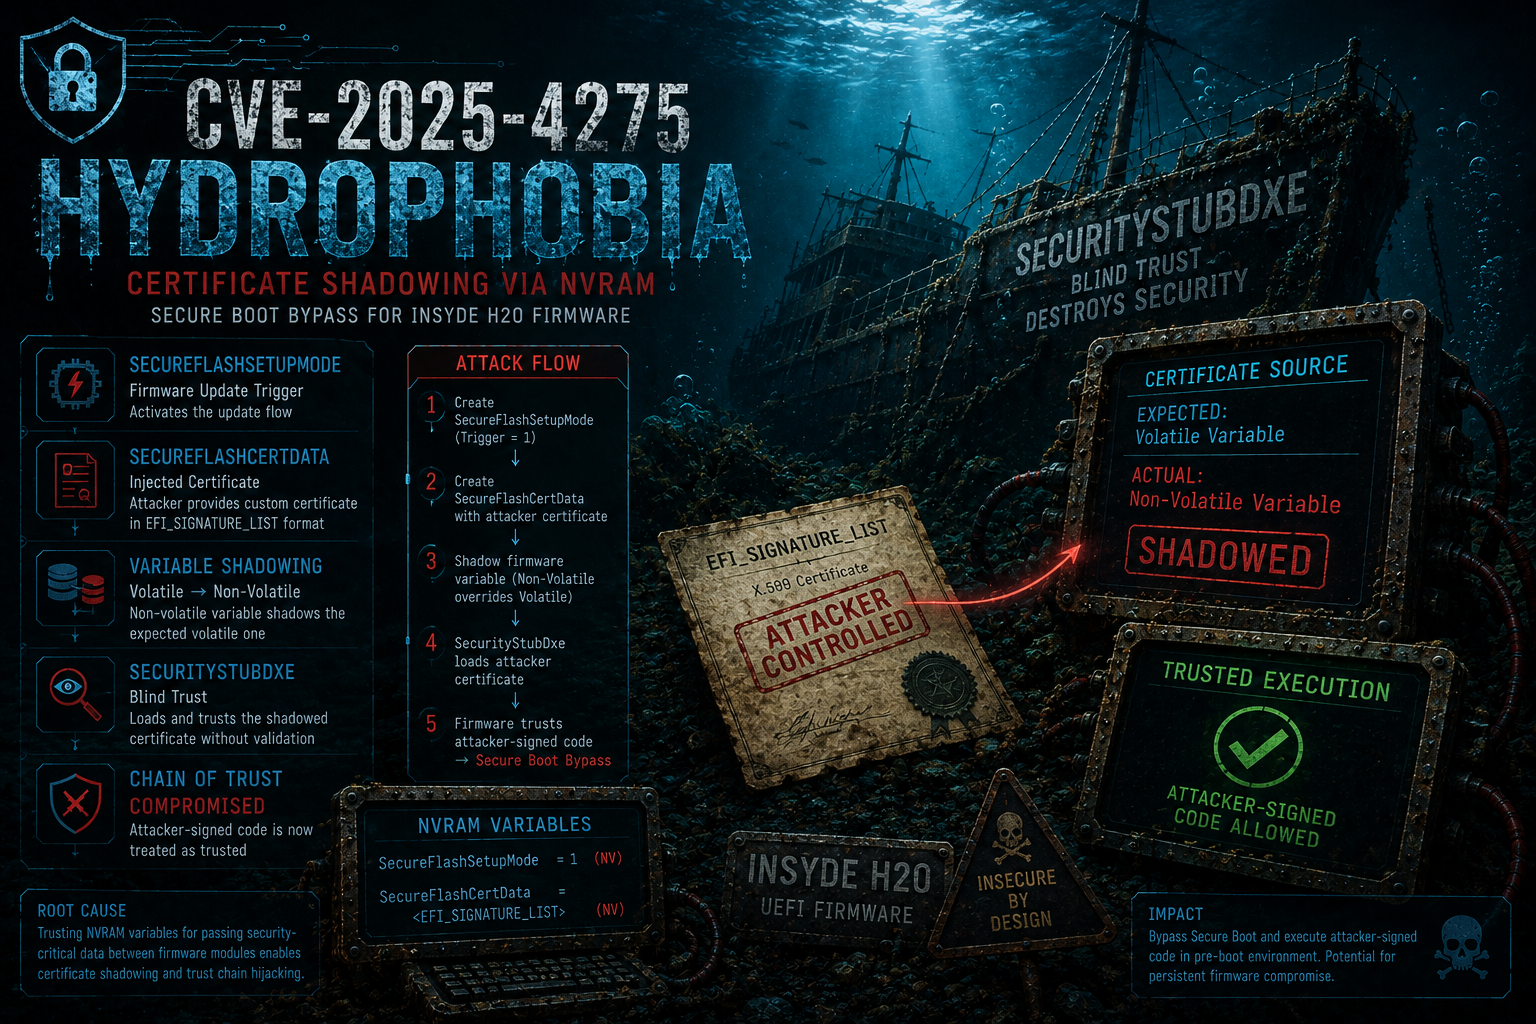
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…

Simplifies D-Link DCS-932L firmware emulation with pre-patched components and includes a Proof-of-Concept exploit for CVE-2024-37606."

Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…

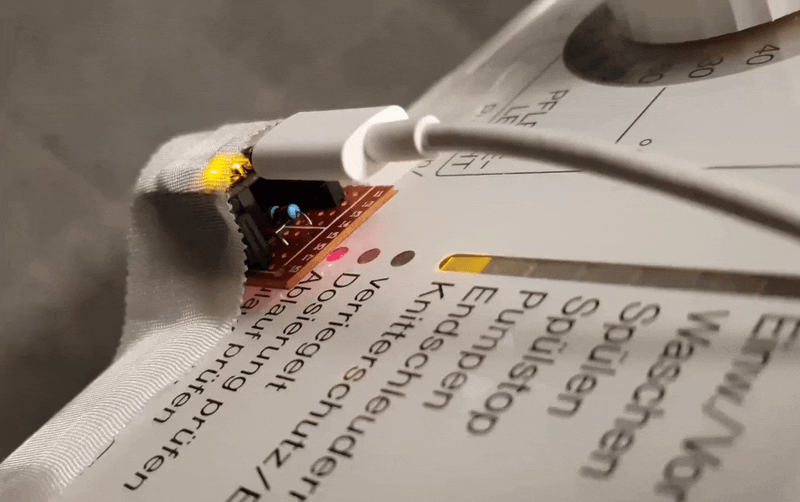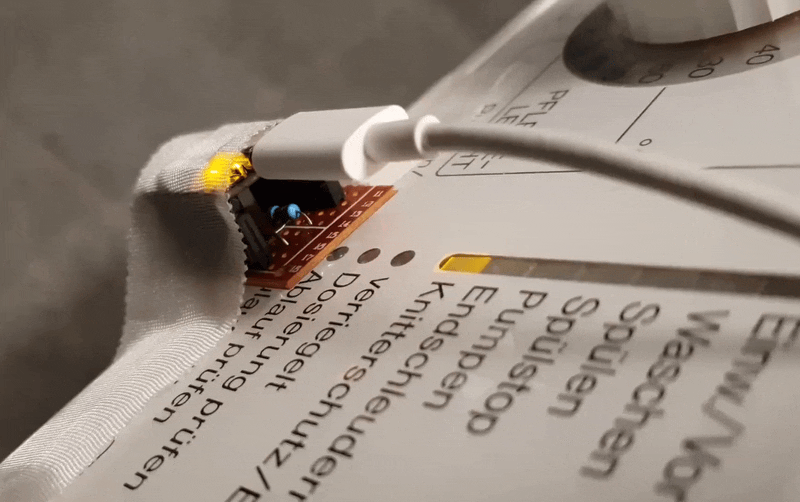
Open hardware and software tools for communicating with Miele appliances via their optical diagnostic interface

A tool for UEFI firmware reverse engineering

Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…

LLDB MCP Integration + other helpful commands

A reverse engineering framework written in Python.

Snapshot-based coverage-guided windows kernel fuzzer

Proof of concept exploit of Windows Update Orchestrator Service Elevation of Privilege Vulnerability

GNU IFUNC is the real culprit behind CVE-2024-3094

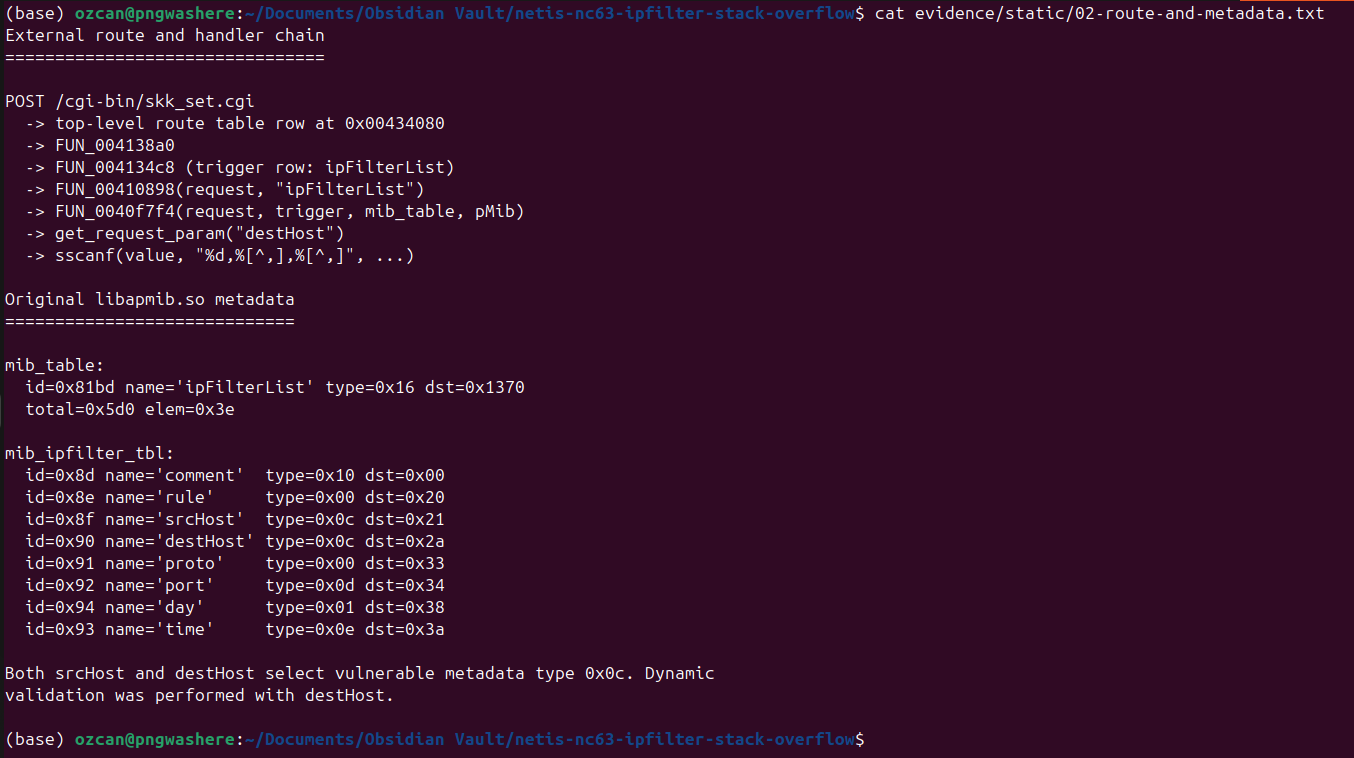
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler

Apple Silicon device emulator.

The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more

Extract files from any kind of container formats

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…