

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
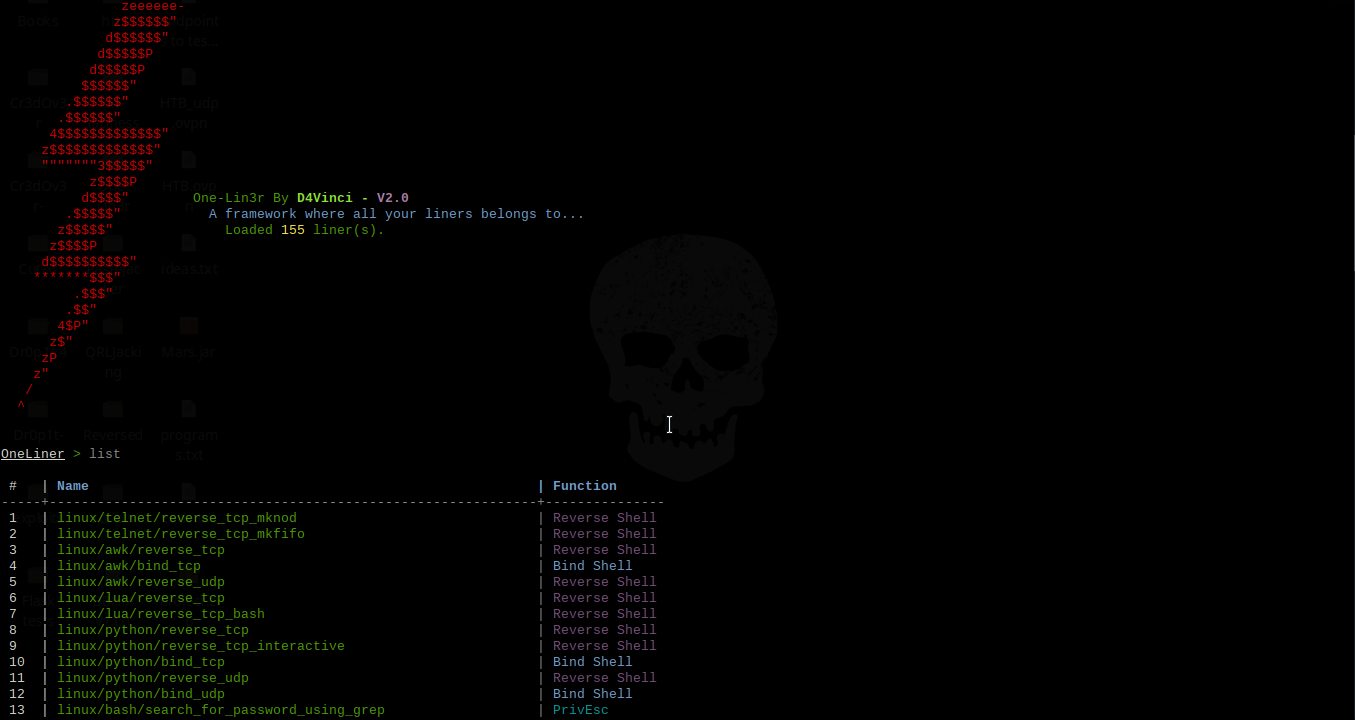 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 cpkt9762/ida-cli
Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…
 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .