

cve-2026-64560-a16
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
android-securitybinary-exploitationexploitation+8
become-illusory/cve-2026-64560-a16CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 mercul1ninna/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
 donfanning/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
 janhalendk/react
A OSINT project that explores how to dump data from React
 andreiverse/shlol
do common hacking tasks with a simple menu
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 bytesizedmarius/rewerse-engineering
Rewe API reverse engineering in Go
 nccgroup/ghostrings
Ghidra scripts for recovering string definitions in Go binaries
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 zznop/sploit
Go package that aids in binary analysis and exploitation
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
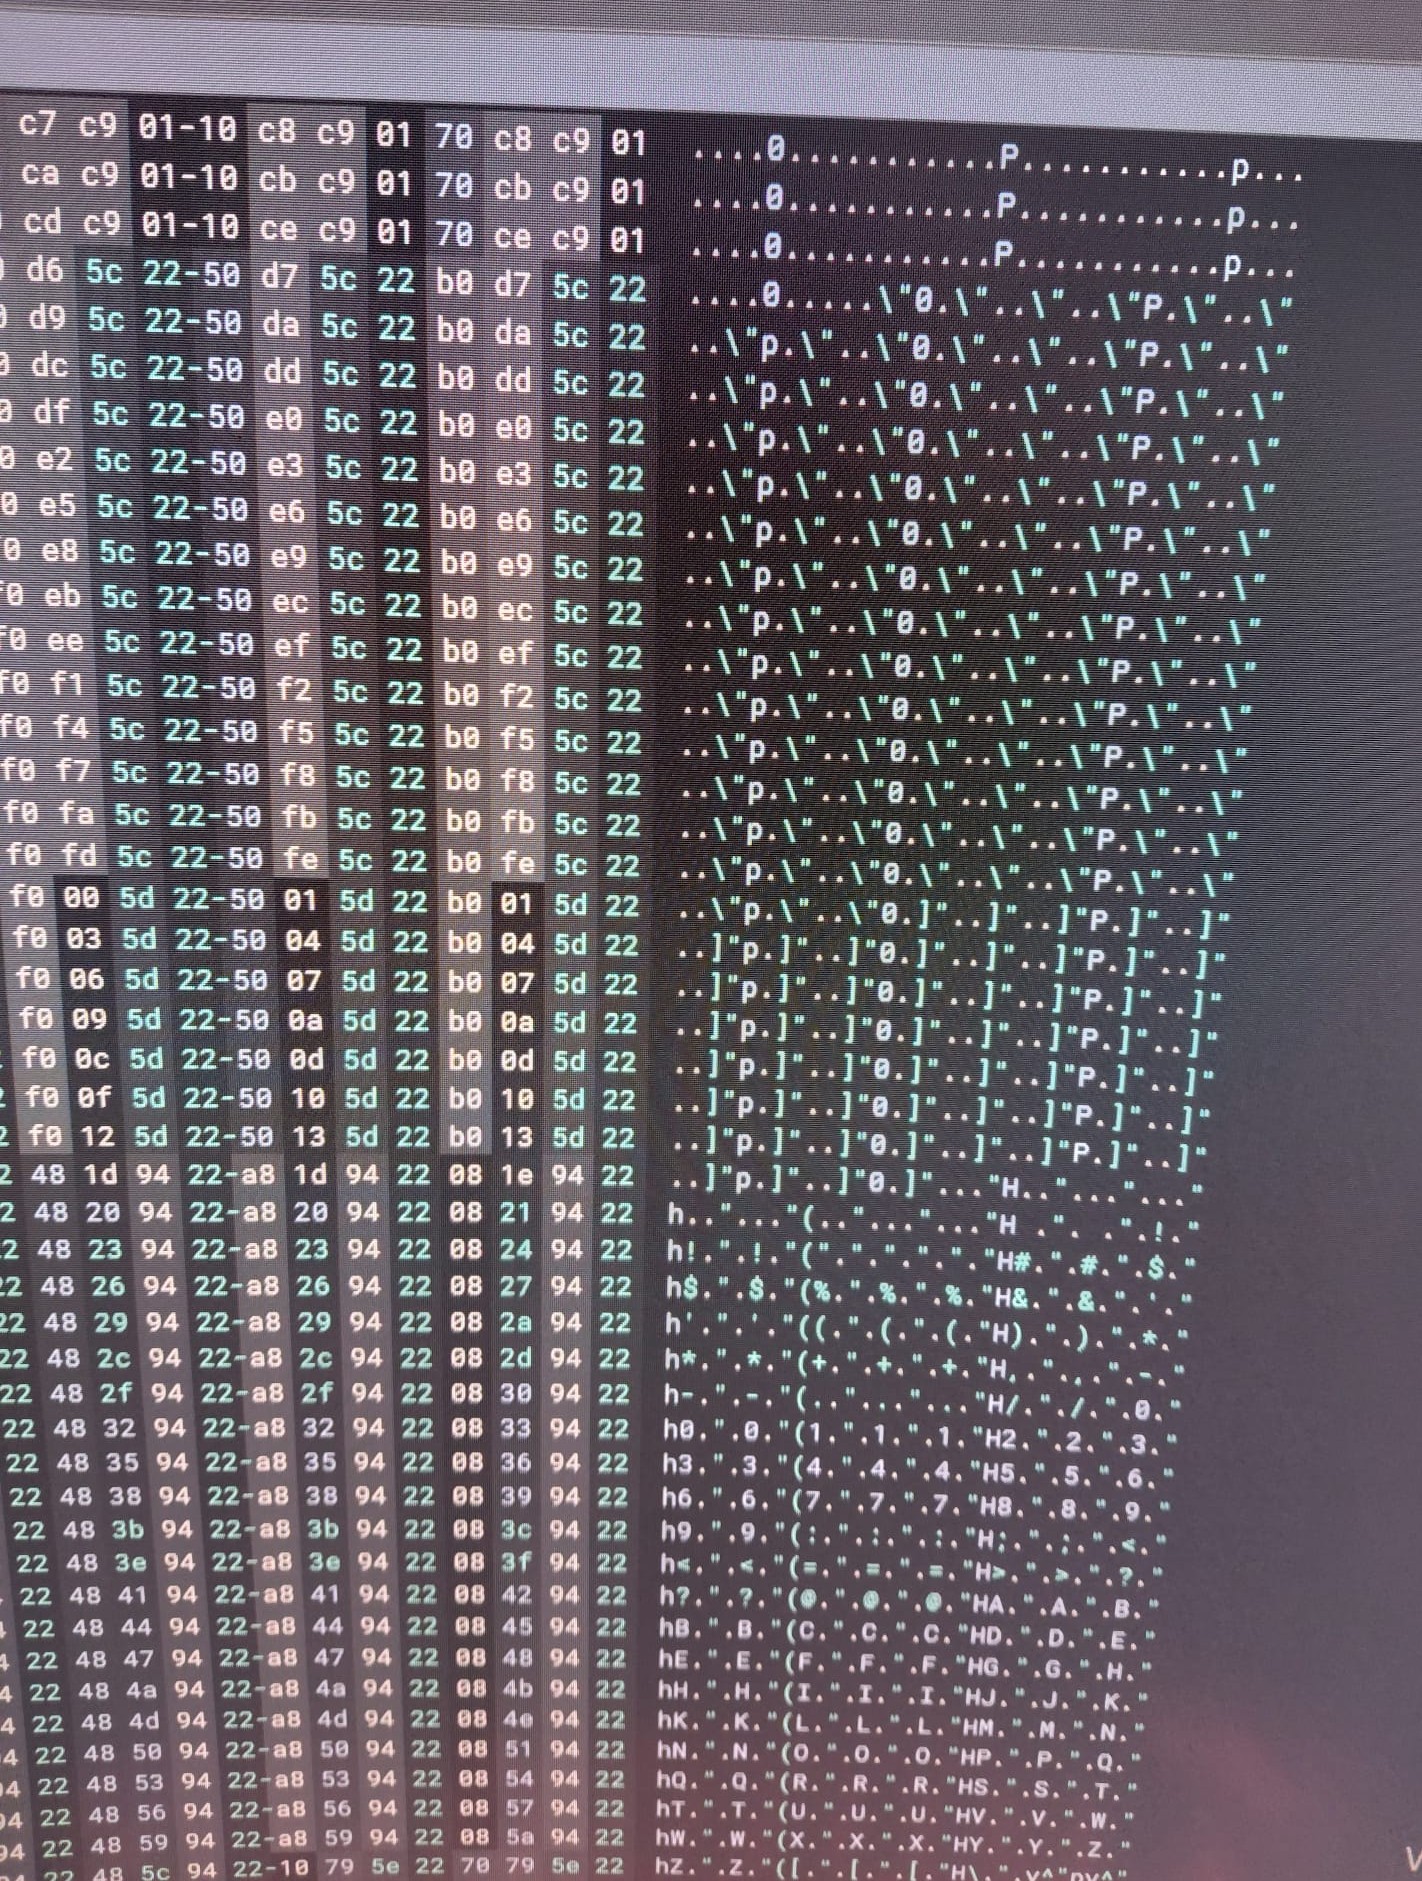 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.