

replica
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
binary-analysiscryptographymalware-analysis+2
315
reb311ion/replicaGhidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
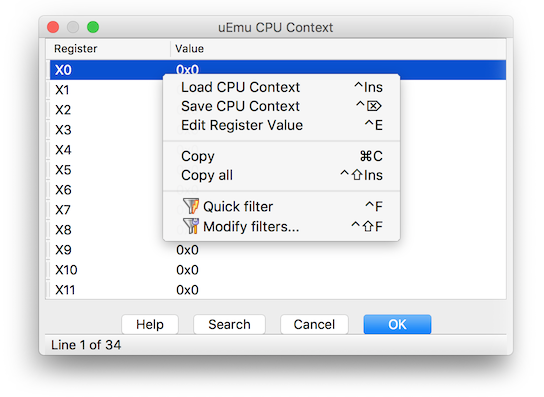 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
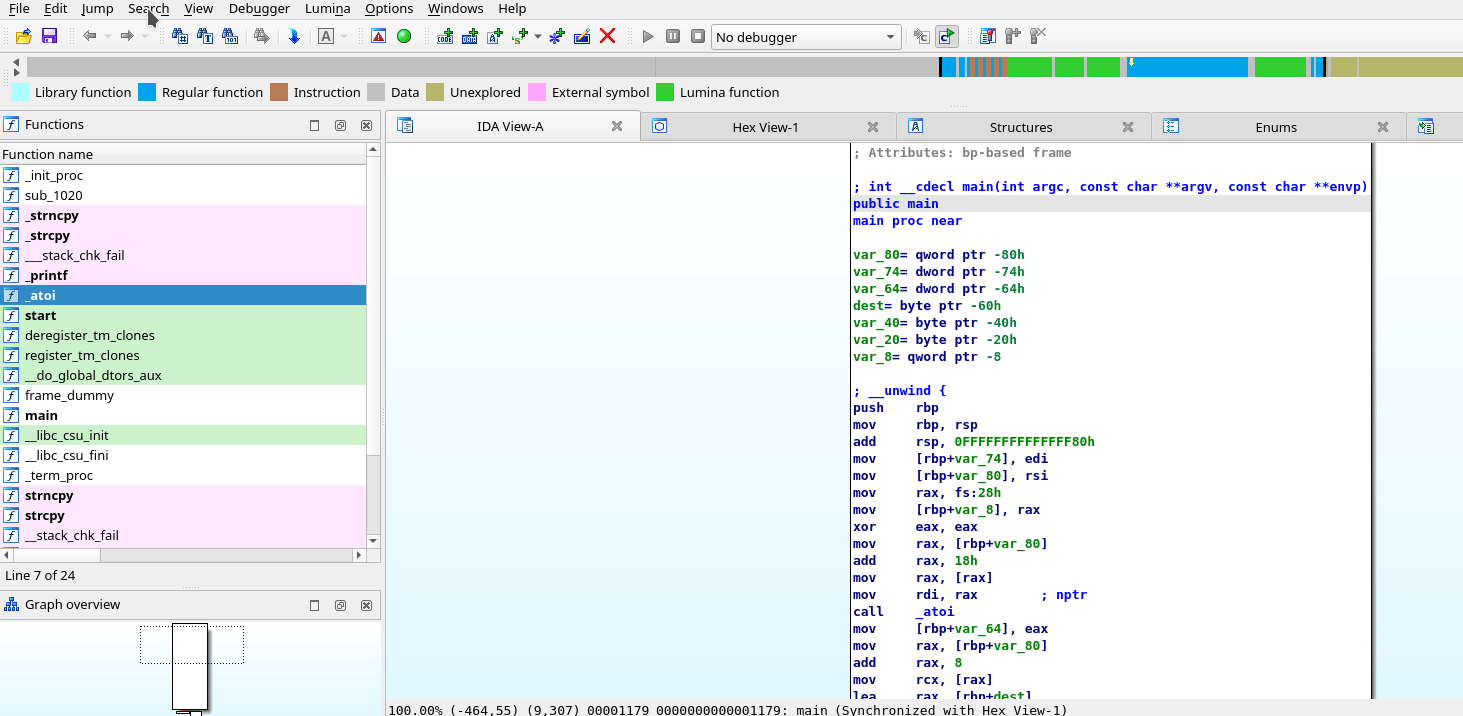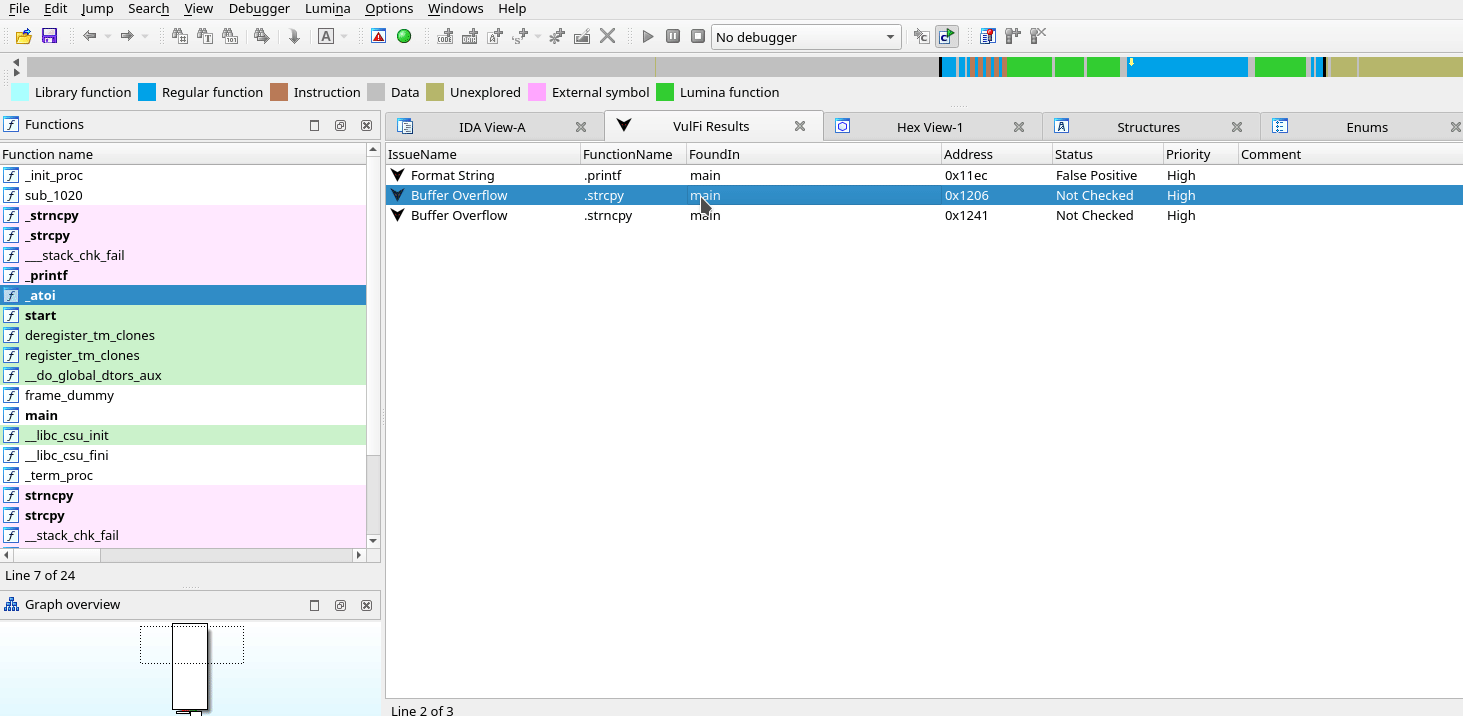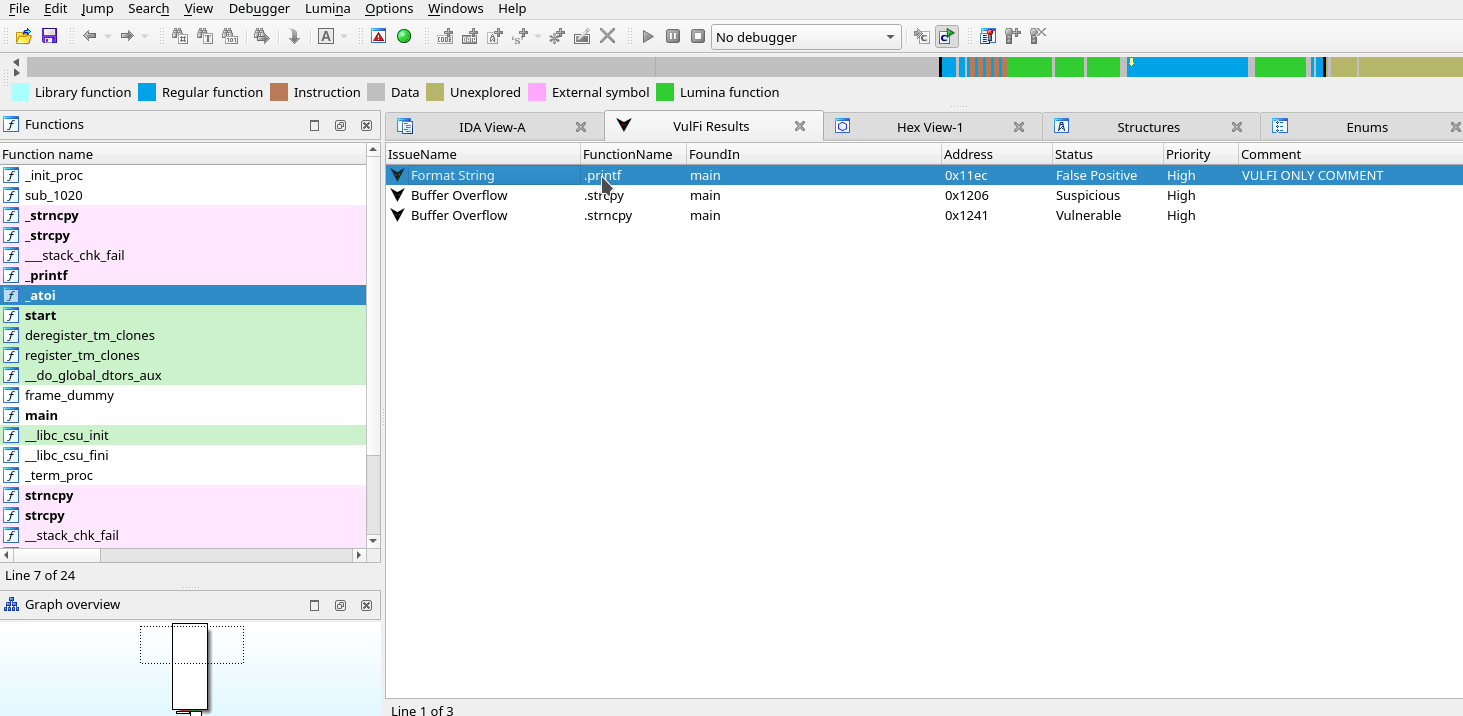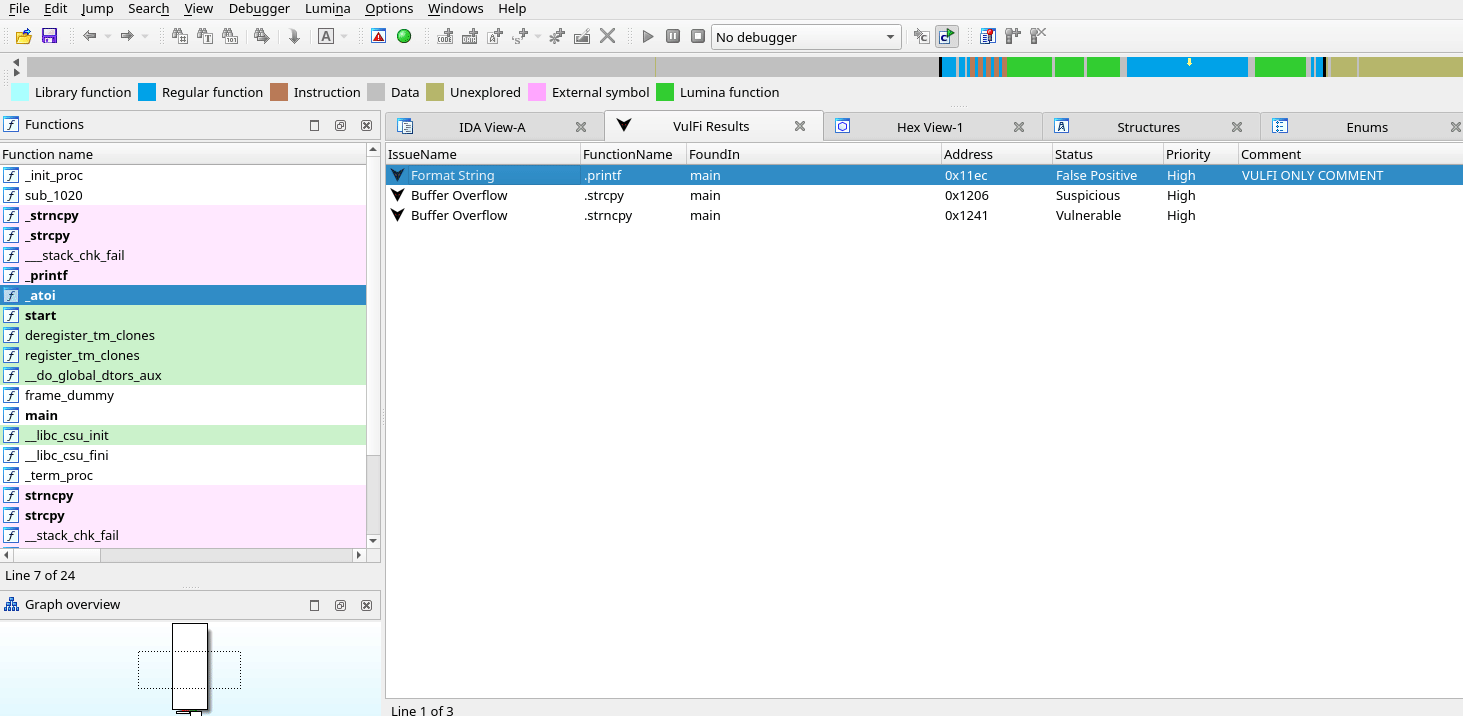 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
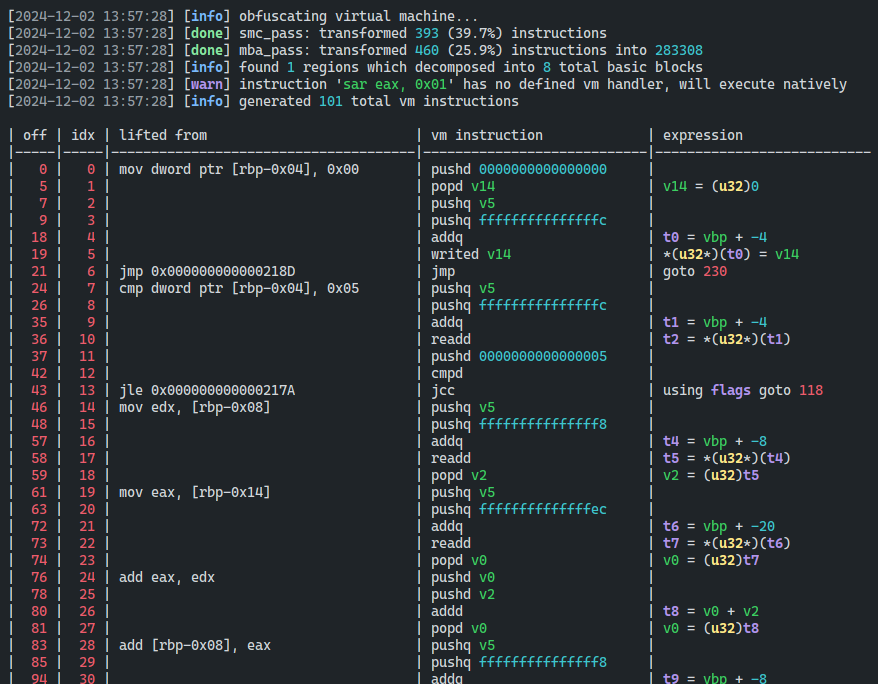 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 dr4k0nia/xorstringsnet
Easy XOR string encryption for NET based binaries
 knight0x07/onenoteanalyzer
A C# based tool for analysing malicious OneNote documents
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
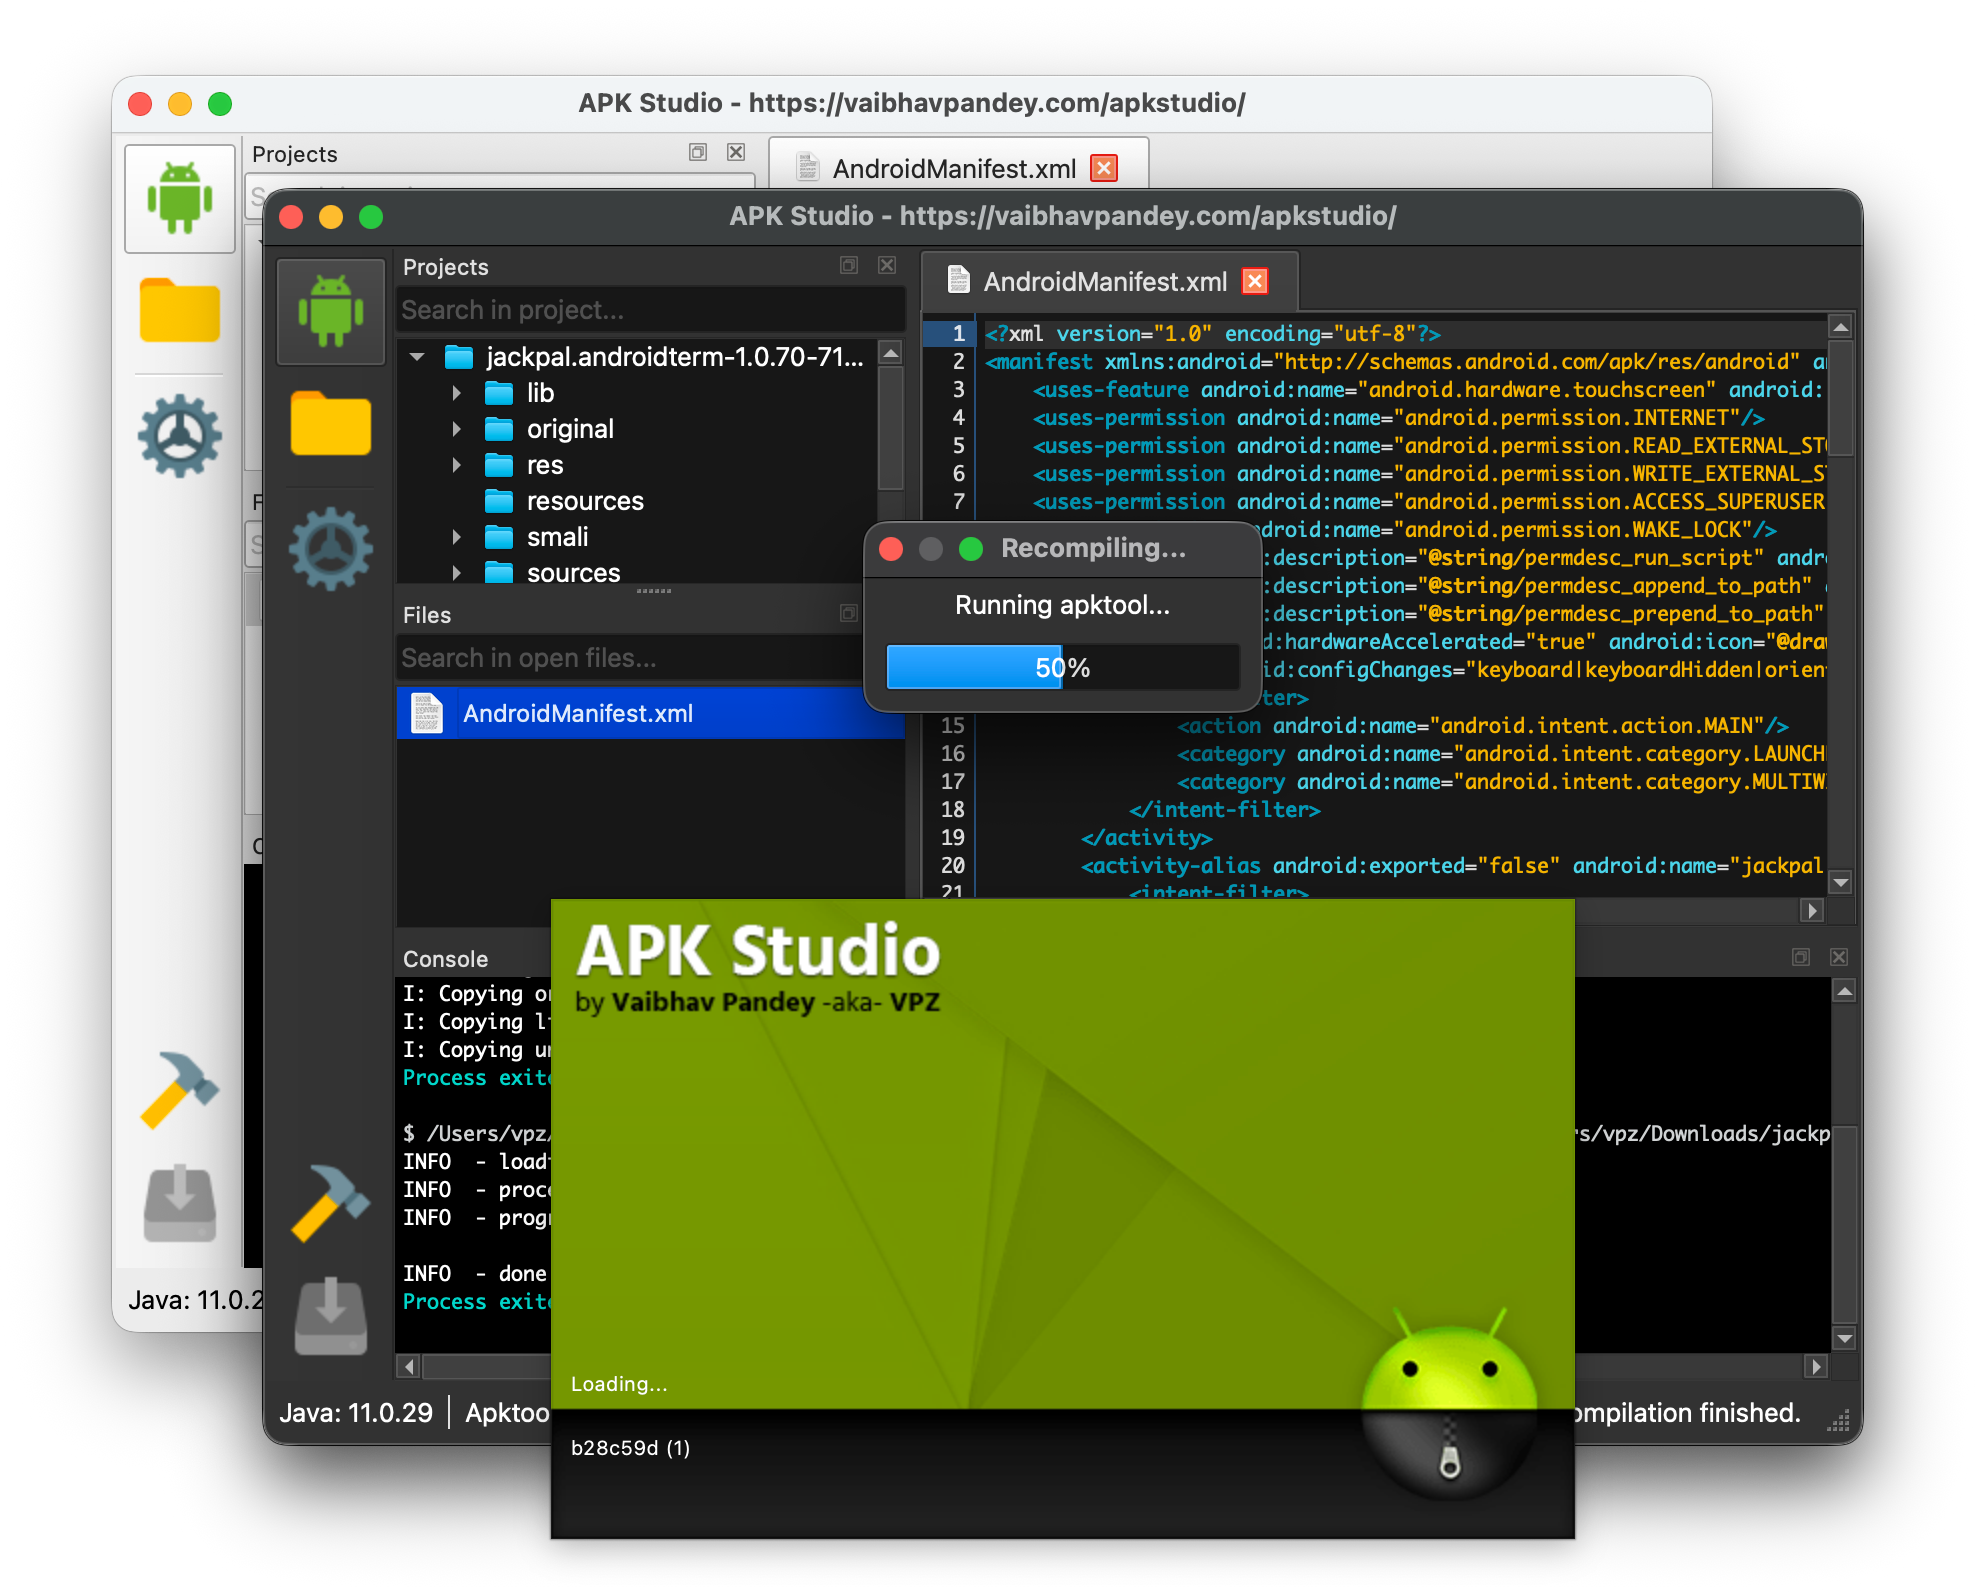 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)